
ftw
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
vulnerability-scannerswaf-bypassweb-security+2
142
coreruleset/ftwYAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 spiarh/webhook-cve-2022-0811
Simple webhook to block exploitation of CVE-2022-0811
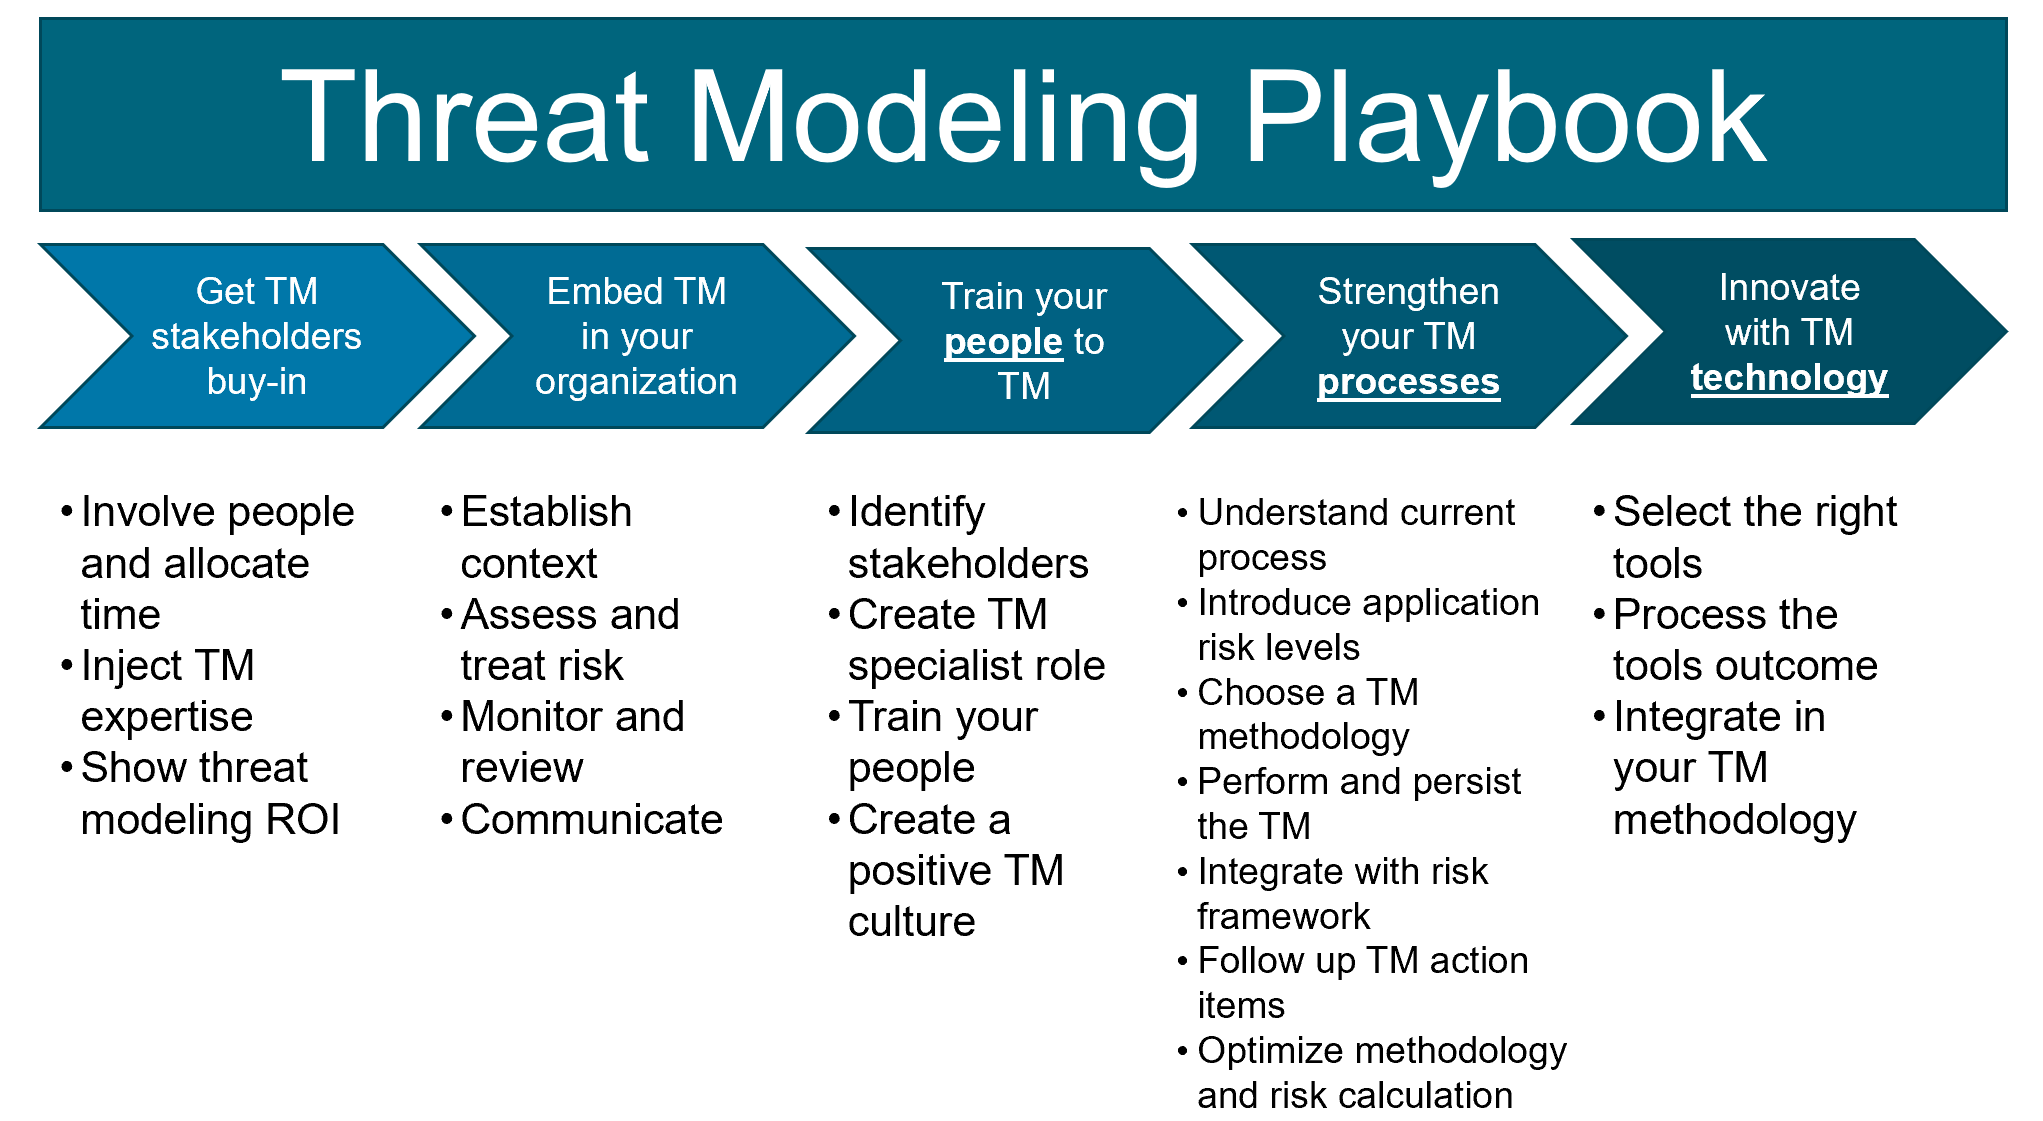 owasp/threat-modeling-playbook
Structured playbook for integrating threat modeling into product security, covering stakeholder buy-in, organizational embedding, training, process…
 poshbotio/poshbot
Powershell-based bot framework
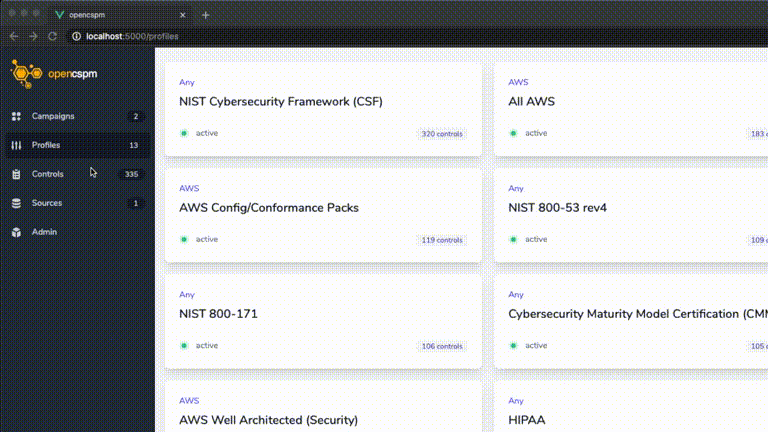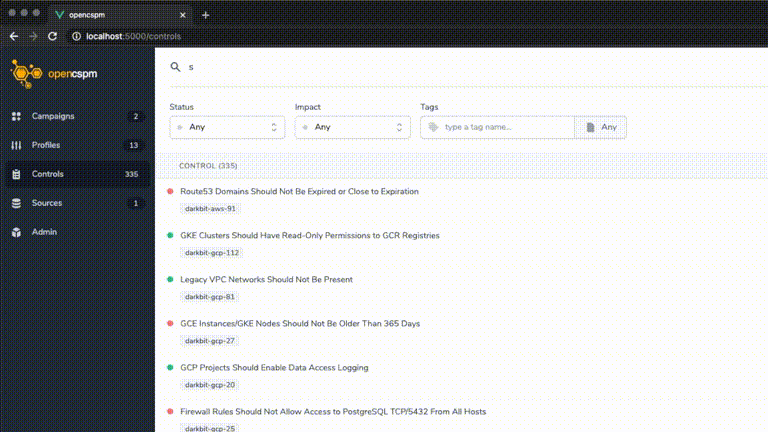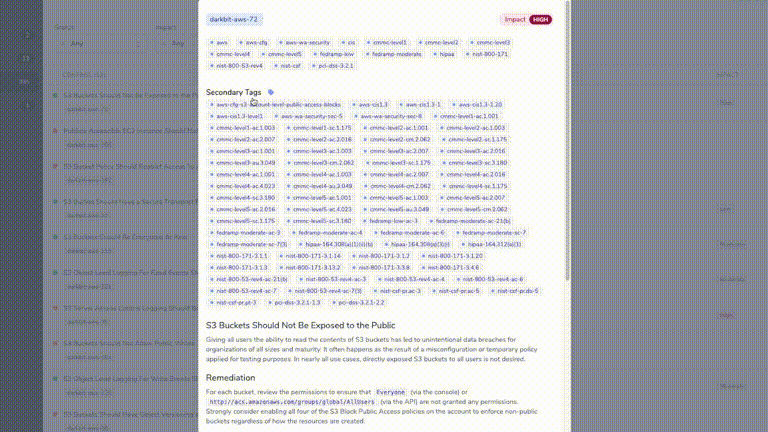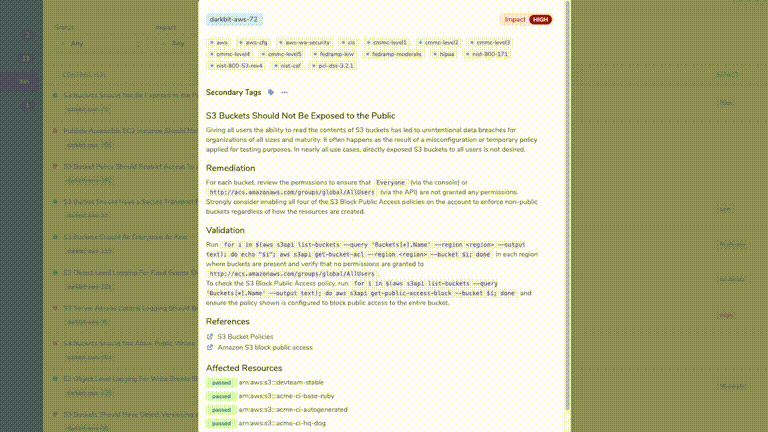 opencspm/opencspm
Open Cloud Security Posture Management Engine
 salesforce/vulnreport
Open-source pentesting management and automation platform by Salesforce Product Security
 novoda/gradle-static-analysis-plugin
Easy setup of static analysis tools for Android and Java projects.
 ziadsaleemi/polkit_cve-2021-4034
Ansible role to patch RHSB-2022-001 Polkit Privilege Escalation - (CVE-2021-4034)
 arnaudluti/ps-cve-2021-44228
Static detection of vulnerable log4j librairies on Windows servers, members of an AD domain.
 lhotari/pulsar-docker-images-patch-cve-2021-44228
Patch Pulsar Docker images with Log4J 2.17.1 update to mitigate Apache Log4J Security Vulnerabilities including Log4Shell
 open-aims/log4j
Patched Log4j 1.2.17 library with the vulnerable JMSAppender class removed to mitigate CVE-2021-4104, intended as a drop-in replacement for affected…
 lucab85/log4j-cve-2021-44228
Ansible playbook automating Red Hat's Log4j detector script to scan Linux hosts for CVE-2021-44228 (Log4Shell) vulnerability with GPG verification.
 dbzoo/log4j_scanner
Filesystem scanner for Log4Shell (CVE-2021-44228) and related CVEs. Detects vulnerable JAR files via hash matching and class presence. Runs…
 lucab85/ansible-role-log4shell
Ansible playbook to verify target Linux hosts using the official Red Hat Log4j detector script RHSB-2021-009 for Log4Shell (CVE-2021-44228).
 3pplus/loguccino
Scan and patch tool for CVE-2021-44228 and related log4j concerns.
 robocoder/rips-scanner
RIPS - A static source code analyser for vulnerabilities in PHP scripts
 thedevappsecguy/log4j-mitigation-cve-2021-44228--cve-2021-45046--cve-2021-45105--cve-2021-44832
Log4J CVE-2021-44228 : Mitigation Cheat Sheet
 dtact/divd-2021-00038--log4j-scanner
Recursive vulnerability scanner for Log4j CVEs in archives and Docker images. Detects JndiLookup.class and vulnerable versions via SHA256 hashes,…