

BLT
 owasp/blt
Monorepo of OWASP Bug Logging Tool projects: crowd-sourced vulnerability reporting, bug bounty workflows, CVE namespace, autopatching, and security…
curated-resourcesdevsecopseducation+7
11 day ago
owasp/bltMonorepo of OWASP Bug Logging Tool projects: crowd-sourced vulnerability reporting, bug bounty workflows, CVE namespace, autopatching, and security…
 m14r41/scan4secrets
Find credentials and secret with 170+ rules covering across source code, Web URL, and CI/CD, verifies them against vendor APIs, and generates SARIF,…
 0sec-labs/0
Open-source AI security harness. Includes a web UI for code analysis, pentesting, vulnerability research, reverse engineering, verification, and…
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 terra-nova83/cve-2026-0915-json-patch.-v2.0
Provides a security patch for CVE-2026-0915, adding strict JSON schema validation, input sanitization, and rate limiting to prevent injection and DoS…
 open-aims/log4j
Patched Log4j 1.2.17 library with the vulnerable JMSAppender class removed to mitigate CVE-2021-4104, intended as a drop-in replacement for affected…
 gouldnicholas/cve-2026-4660-poc
PoC for CVE-2026-4660: arbitrary file read via git checkout in hashicorp/go-getter
 ashizzz/cve-2026-22610
Scans Angular projects for XSS vulnerabilities in SVG elements and unsafe bindings, generating a vulnerability report with line numbers and…
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
 george0papasotiriou/cve-2026-22018-jenkins-pipeline-shared-library-code-execution-via-grab-
PoC for CVE-2026-22018, a critical Jenkins Pipeline Shared Library RCE via Groovy @Grab, demonstrating supply-chain code injection and mitigation…
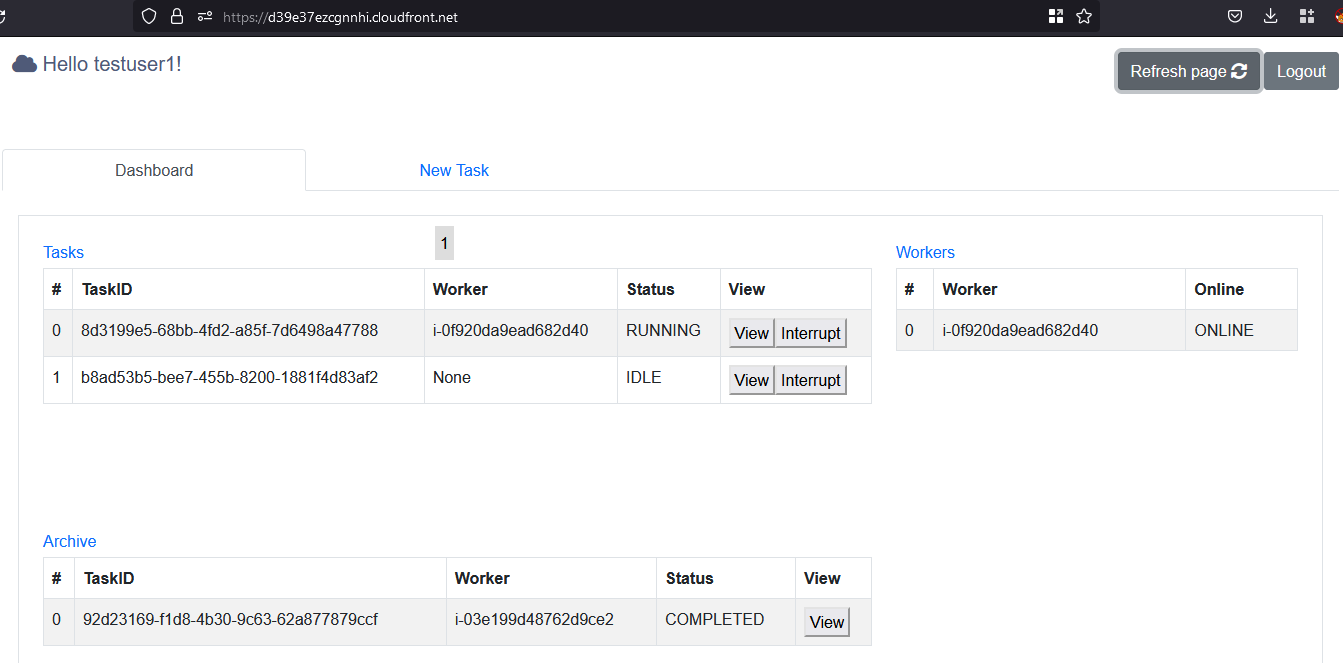 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
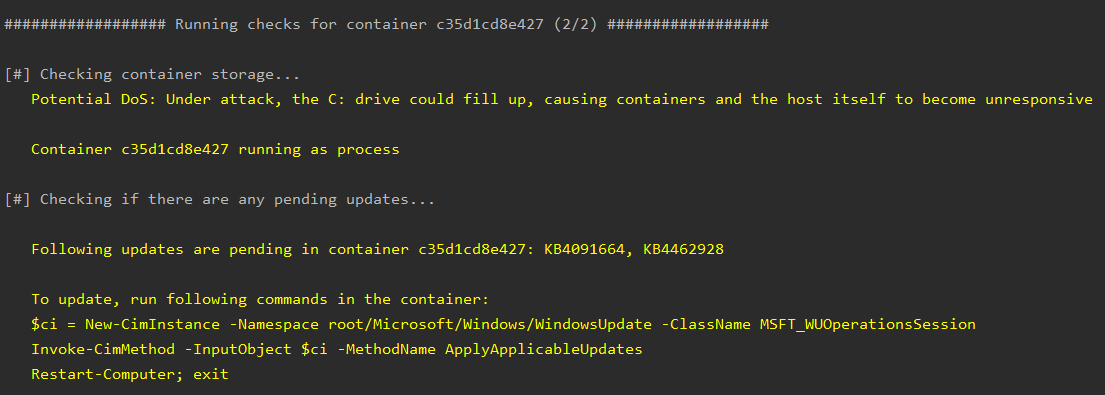 nccgroup/whalescan
Whalescan is a vulnerability scanner for Windows containers, which performs several benchmark checks, as well as checking for CVEs/vulnerable…
 aquasecurity/vex-repo-spec
VEX Repository Specification
 snyk/snyk-scan
Automated Snyk vulnerability scanning for dependencies and Docker images in Bitbucket Pipelines, with severity thresholds and monitoring options.
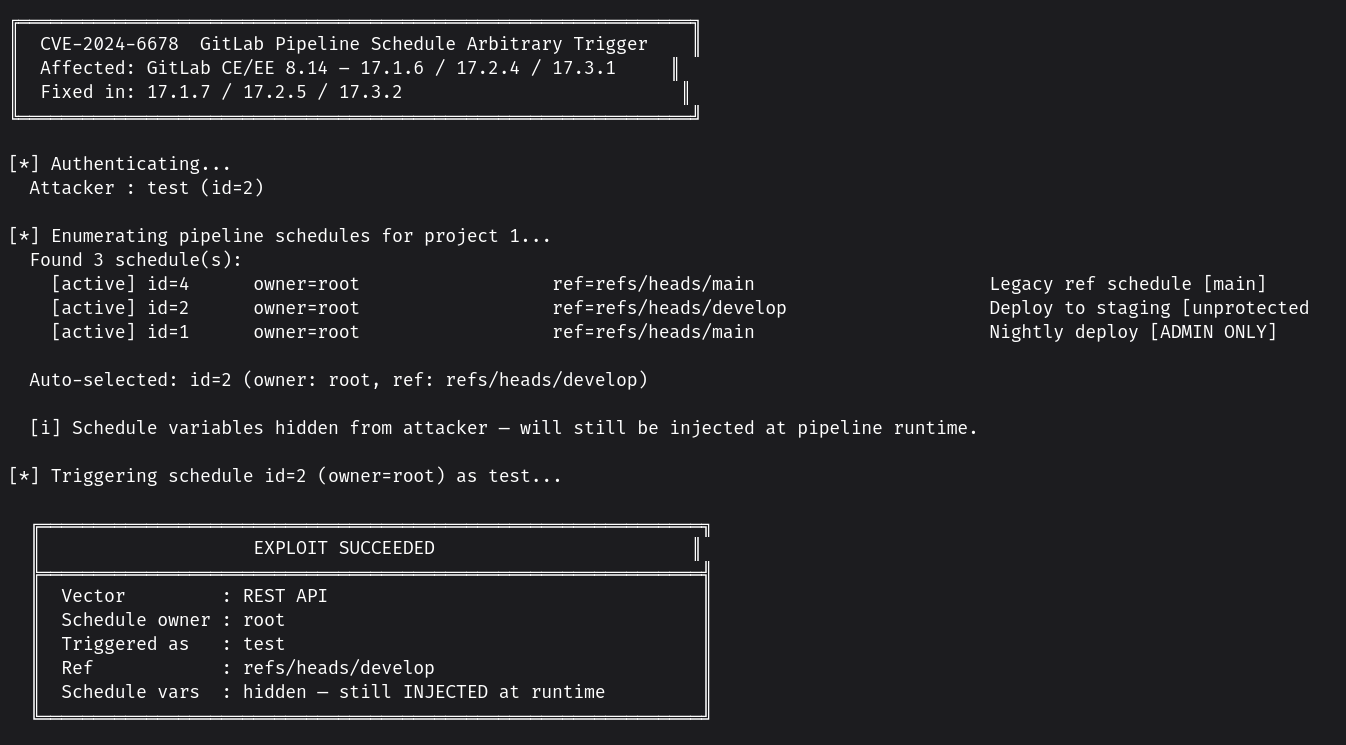
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 infobyte/faraday_plugins
Security tools report parsers for Faradaysec.com