 gmh5225/actions-secrets
Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
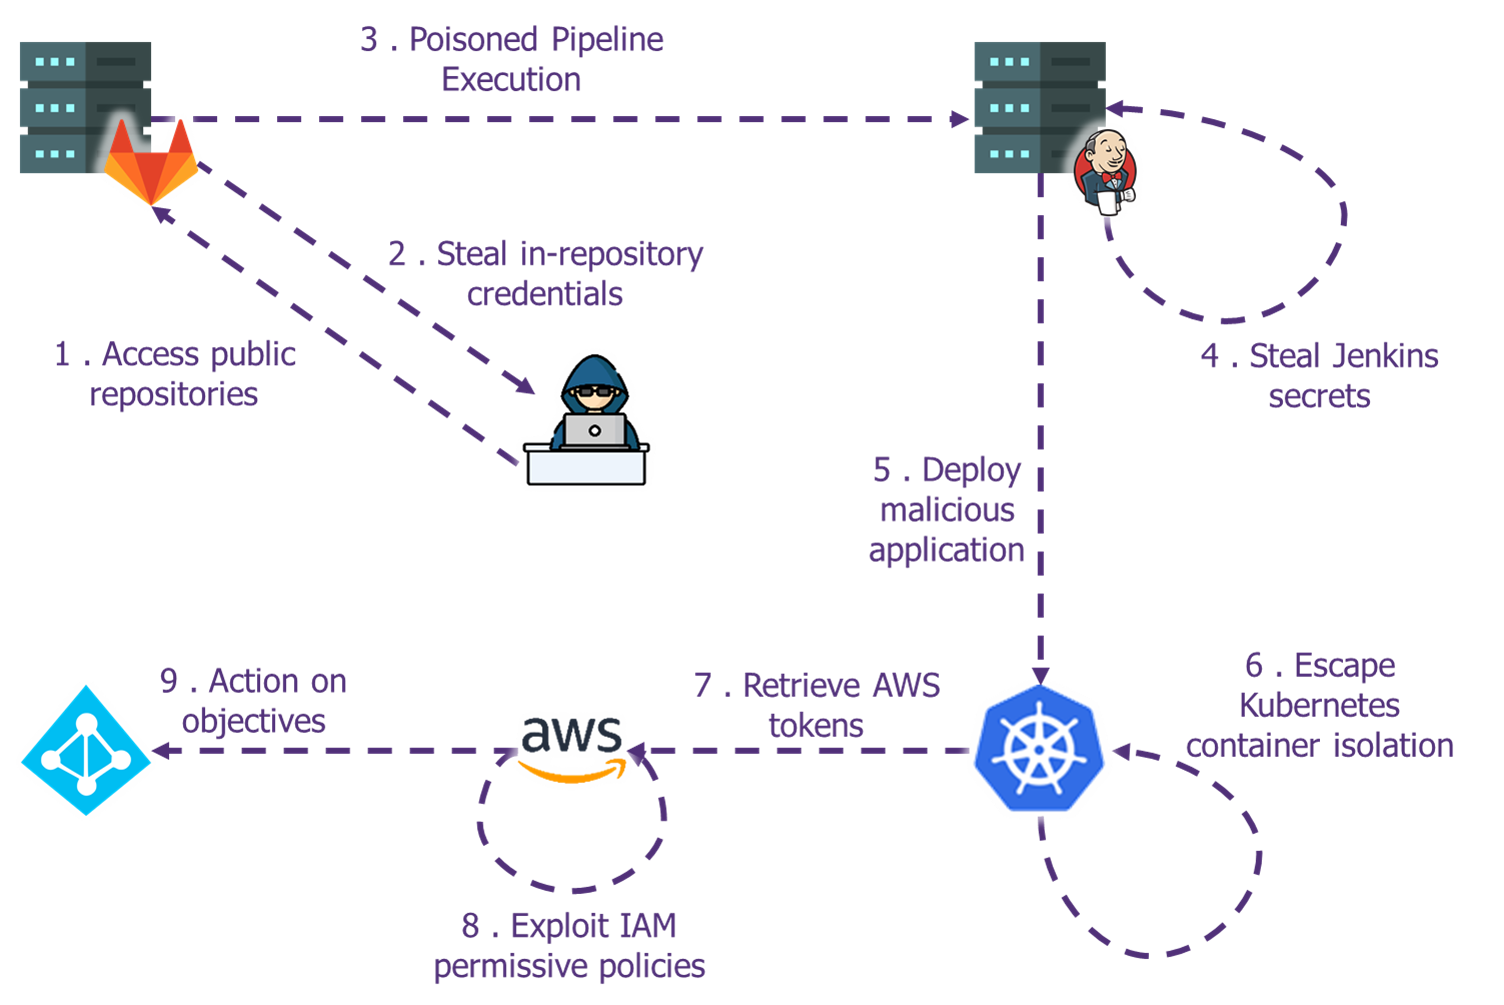 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
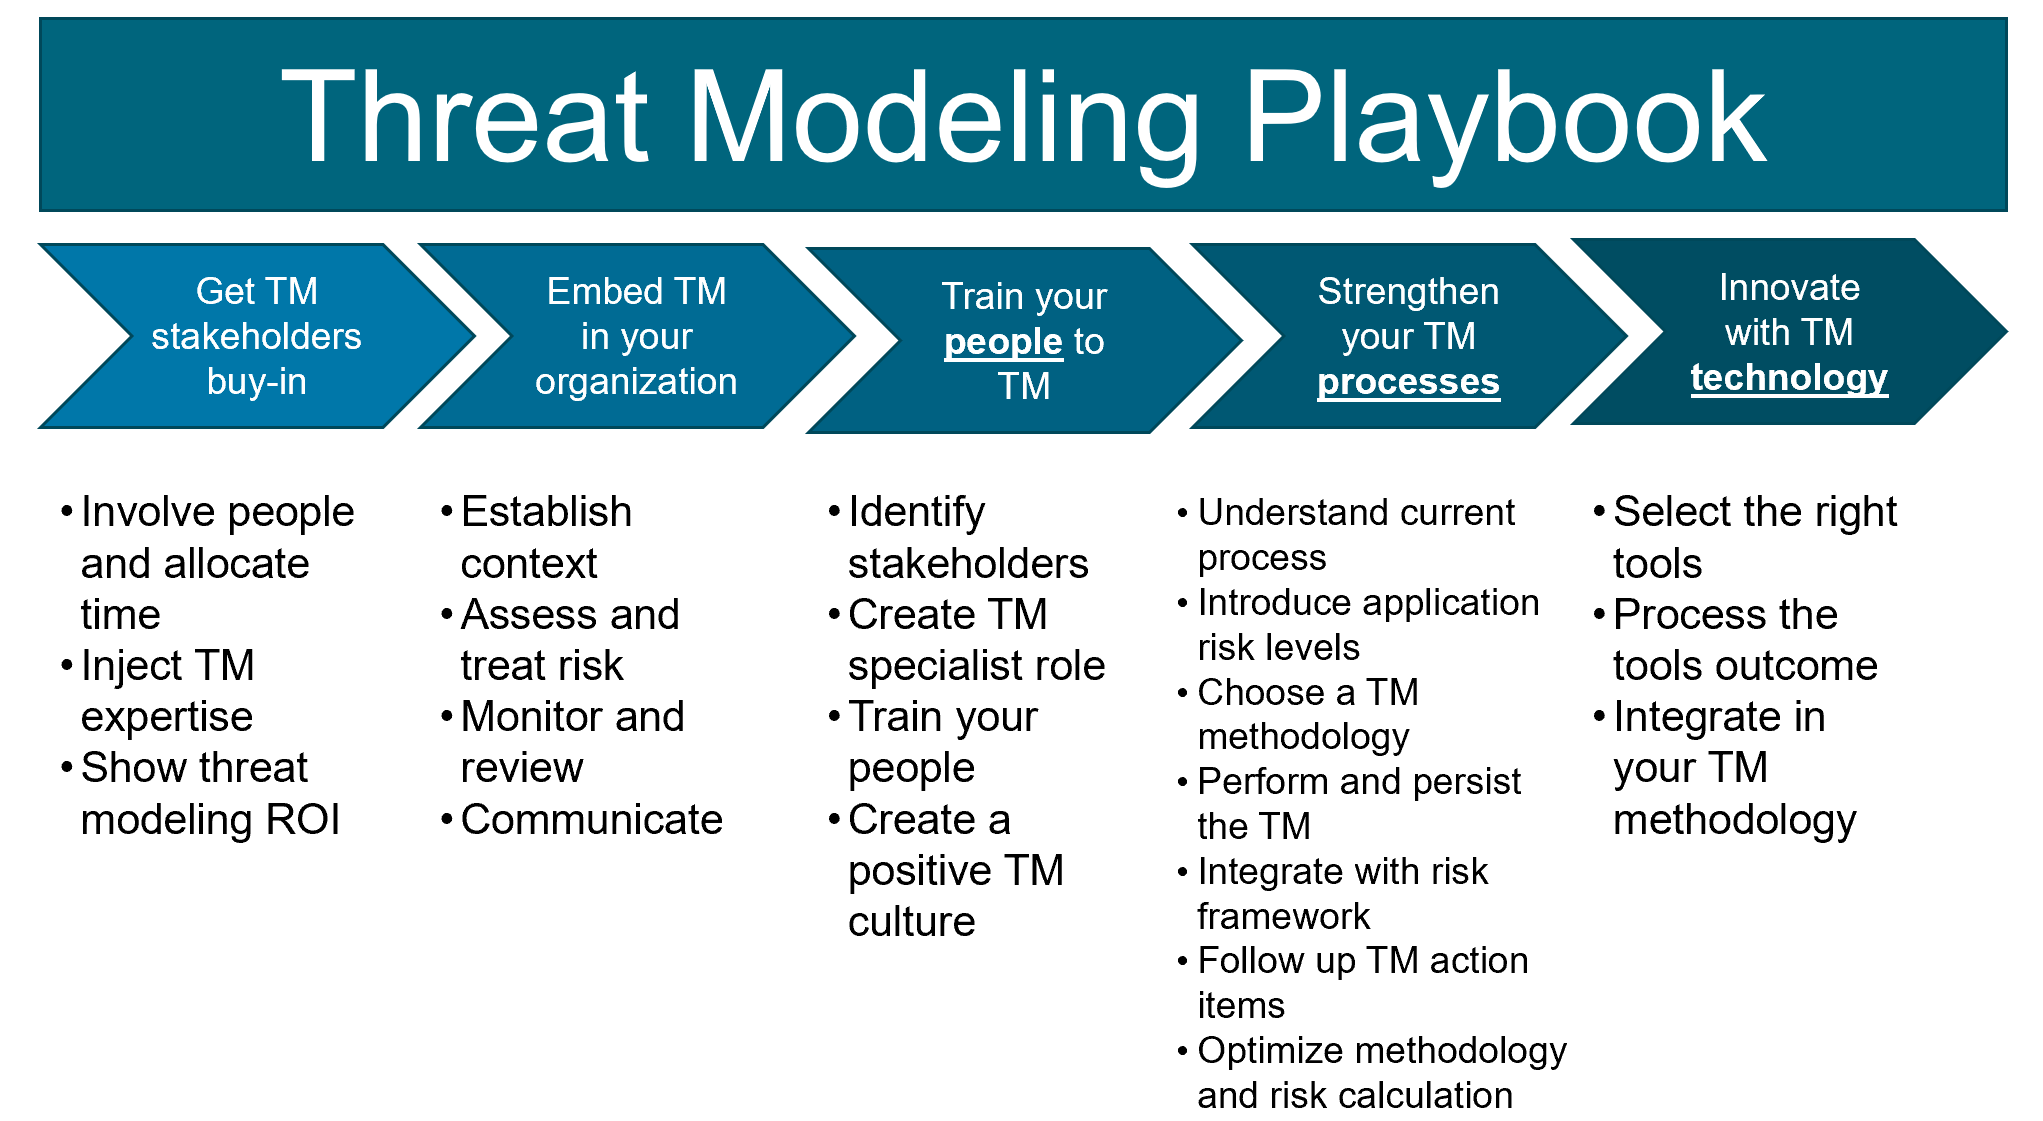 owasp/threat-modeling-playbook
Structured playbook for integrating threat modeling into product security, covering stakeholder buy-in, organizational embedding, training, process…
 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide
 kingofbugbounty/nuclearpond-ofjaaah
Nuclear Pond is a utility leveraging Nuclei to perform internet wide scans for the cost of a cup of coffee.
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 coinbase/salus
We would like to request that all contributors please clone a *fresh copy* of this repository since the September 21st maintenance.
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 google/osv.dev
Open source vulnerability DB and triage service.
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
 devopstoday11/tarian
Anti-Virus for K8s. Protect your Applications running on Kubernetes from malicious attacks with pre-registered source code, runtime processes…