

advisory-database
 github/advisory-database
Security vulnerability database inclusive of CVEs and GitHub originated security advisories from the world of open source software.
curated-resourcesdefensive-toolsdevsecops+5
2.5k
github/advisory-databaseSecurity vulnerability database inclusive of CVEs and GitHub originated security advisories from the world of open source software.
 tencentcloud/cubesandbox
Instant, Concurrent, Secure & Lightweight Sandbox for AI Agents.
 fazmin/cve-intel
Local security intelligence for CVE triage - 40 data sources and 41 tools, risk scores and an MCP server for AI agents, all in native Rust. Private…

 vpierre/ndaal_public_sbom_auditor
Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…
 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 dev-sec/puppet-os-hardening
This puppet module provides numerous security-related configurations, providing all-round base protection.
 ericmtzmtz/pwnproxy
An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.
 plutosecurity/mcpwnfluence
Information about CVE-2026-27825 & CVE-2026-27826 discovered by Pluto Security and a bash script for identifying vulnerable mcp-atlassian instances…
 nrnw/cve-2026-24061-gnu-inetutils-telnet-detector
A passive detection tool for identifying potential exposure to CVE-2026-24061 in GNU inetutils telnet installations
 fabacab/awesome-cybersecurity-blueteam
:computer:🛡️ A curated collection of awesome resources, tools, and other shiny things for cybersecurity blue teams.
 offseq/threat-finder
Runtime vulnerability scanner: finds CVEs in the services actually running on a host and ranks them by network exposure.
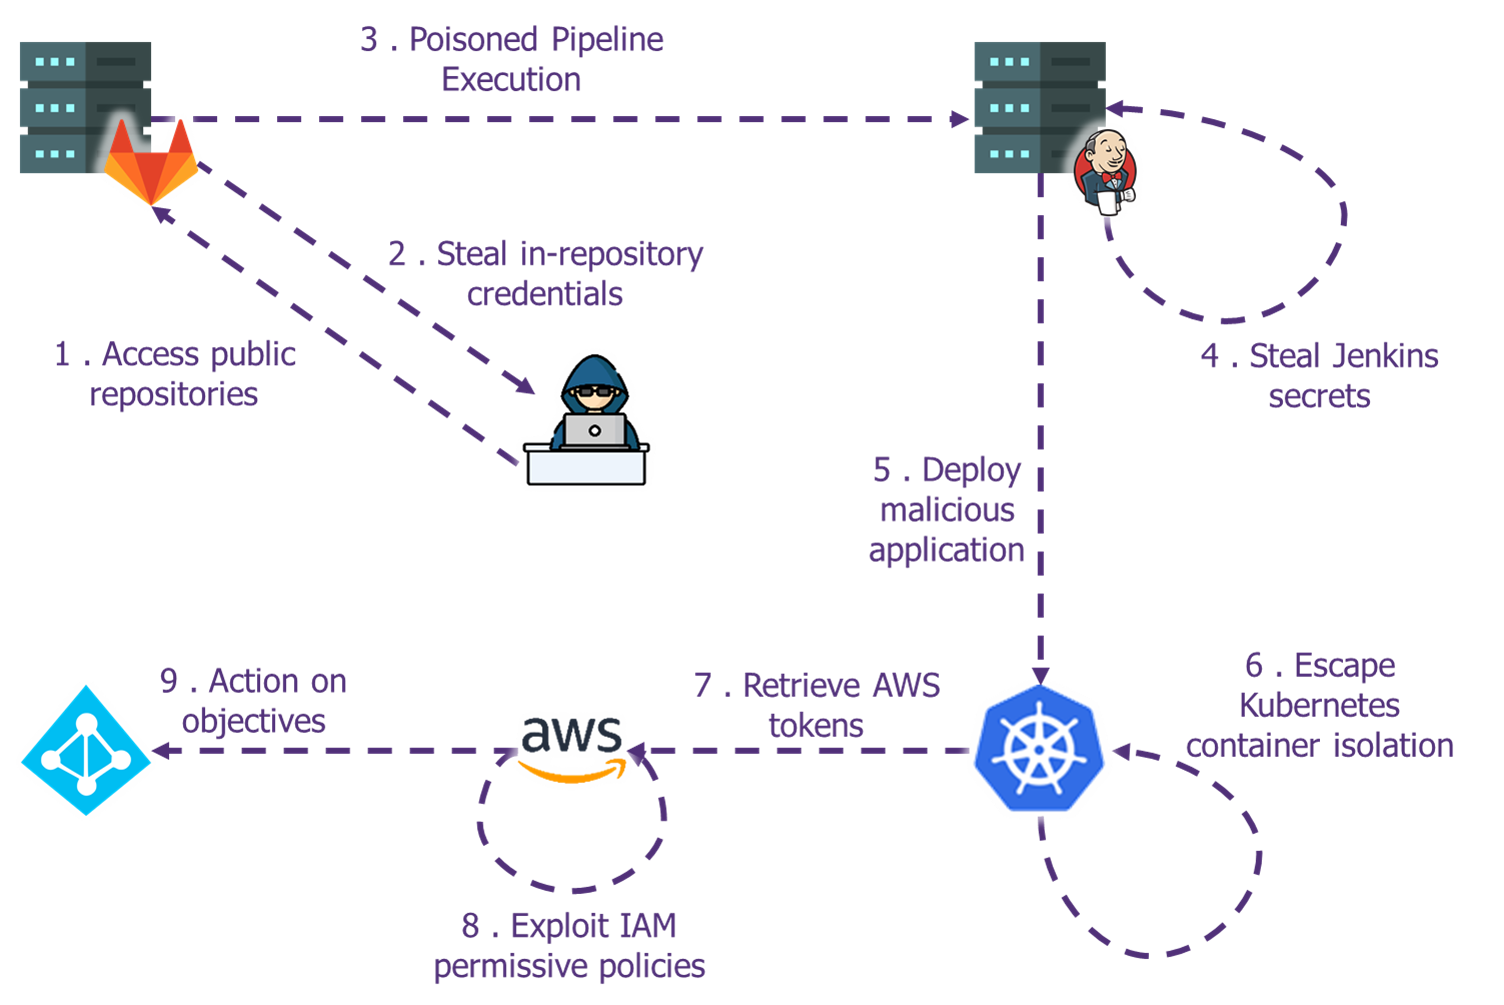 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
 dheeraj-jayaswal/cicd-goat-vapt-writeup
Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
 corelight/corelight-ansible-roles
Corelight-Ansible-Roles are a collection of Ansible Roles and playbooks that install, configure, run and manage a variety of Corelight, Suricata and…
 aquasecurity/vexhub
Aggregates Vulnerability Exploitability eXchange (VEX) documents from open-source projects. Organizes by PURL for automated security tool integration.
 aquasecurity/secfixes-tracker
Forked from https://gitlab.alpinelinux.org/kaniini/secfixes-tracker
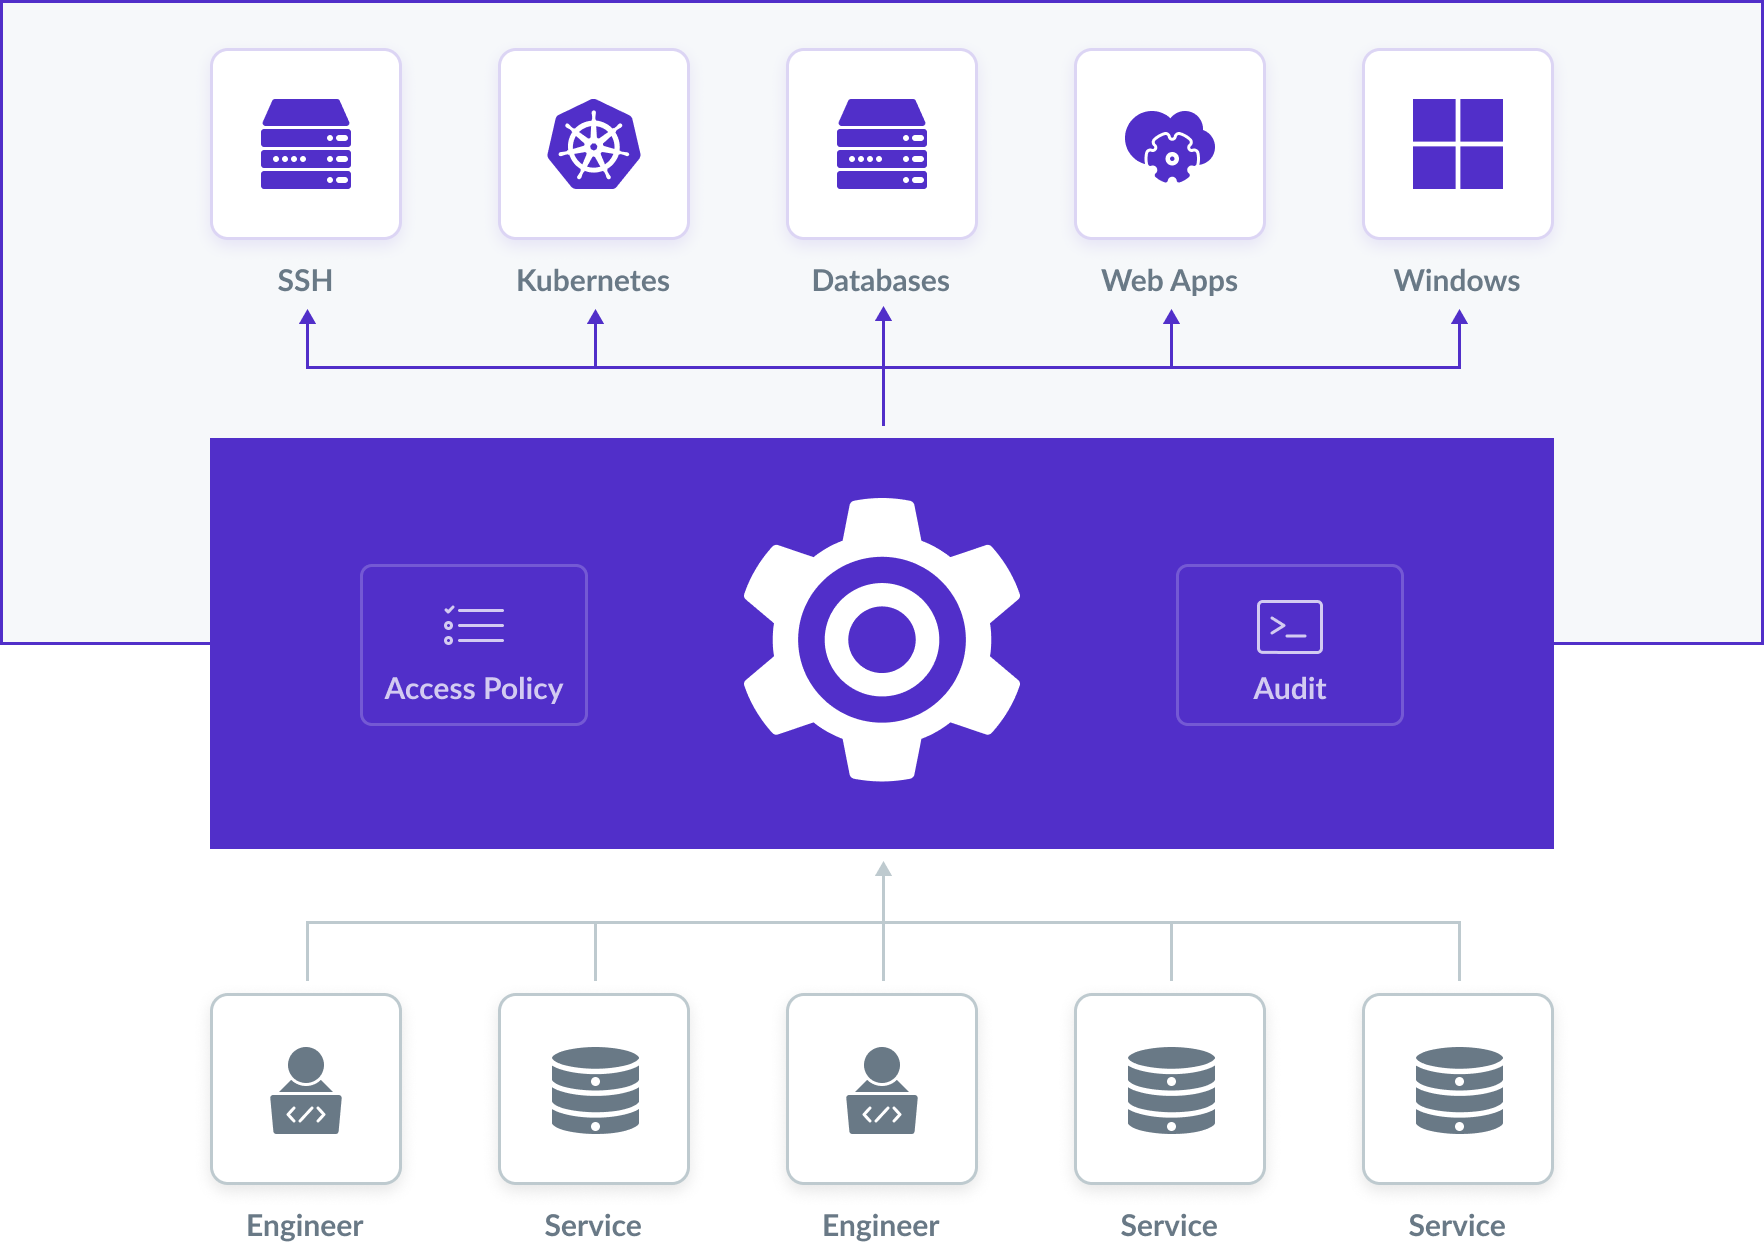 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.