self-hosted-ctf-platform

Self-hosted CTF: original web challenges + scoreboard, deployed with Docker Compose via GitLab CI and a GitOps agent. Flags derived from one CI…

Self-hosted CTF: original web challenges + scoreboard, deployed with Docker Compose via GitLab CI and a GitOps agent. Flags derived from one CI…

Scan Magento/Adobe Commerce installations via composer.lock — CVE matching via ValtersIT API

Scan Java projects via pom.xml or build.gradle — CVE matching for Maven/Gradle dependencies

Scan Ruby/Rails apps via Gemfile.lock — matches gems against ValtersIT CVE database

Dependency-free secrets scanner for source code and git history that detects leaked API keys, tokens, and private keys, with redacted output and a…

Realtime secret and configuration management tool

🔍 ScanCode detects licenses, copyrights, dependencies by "scanning code" ... to discover and inventory open source and third-party packages used in…

🐾 Authority, not credentials, for AI agents: policy-approved actions, delegation that can only narrow, instant revocation, tamper-evident audit.

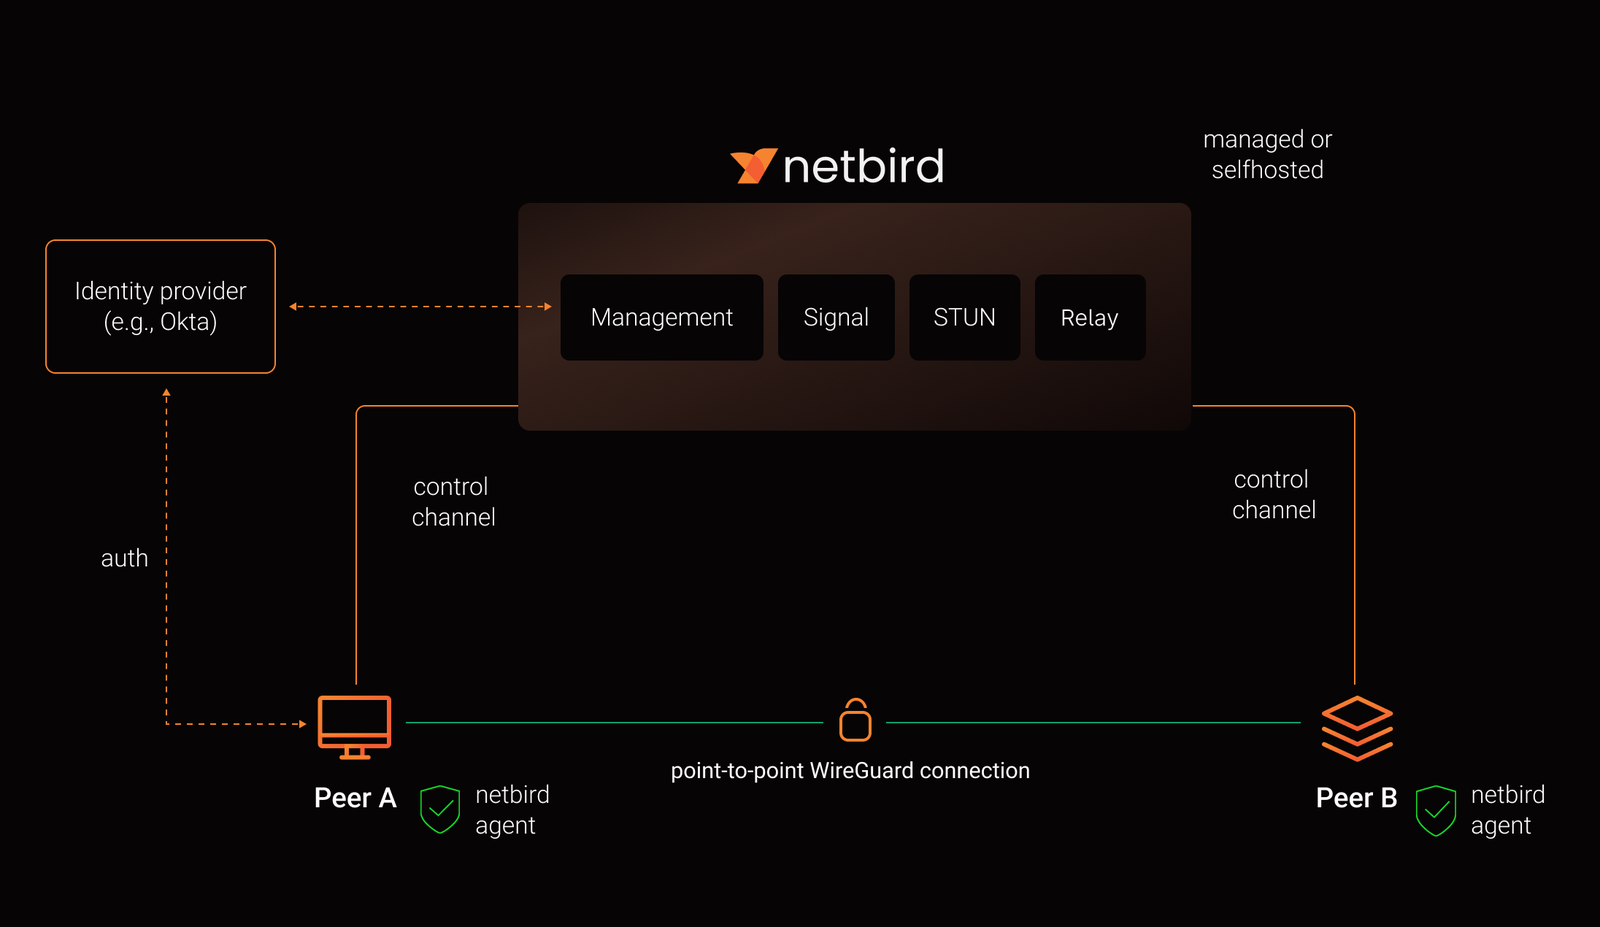
Identity-based Zero Trust networking platform that builds peer-to-peer WireGuard overlay networks with granular access policies, SSO/MFA, and…

High-performance open-source security scanner combining SAST, SCA, Secret Detection, and IaC analysis, built for developers and CI/CD pipelines,…

RuralShield — an AWS CDK research prototype for healthcare cloud security, with policy-bounded AI triage, human-approved response, audit logging, and…

CLI scanner that detects leaked API keys, tokens, and credentials in source trees and deployed web apps, with Supabase/Firebase misconfiguration…

Malware scanner for container images: daemonless, layer-aware, ClamAV and YARA

Offline educational model of CVE-2026-26189 (trivy-action envfile source injection)

Offline Next.js use-cache evidence checker for GHSA-673q-mjm6-r5xr. Next.js cache and typed-array evidence. Standalone Python; JSON/CSV/HTML reports;…

Offline security-report converter to SARIF 2.1.0 and NDJSON with schema validation and preserved evidence provenance. No scanning or uploads.

Closed-loop vulnerability remediation: detect -> reproduce exploit -> generate patch -> verify with a proof harness. Worked example: Langflow…

A vulnerable-by-design, secure-by-deployment NGINX pipeline centered around the aftermath of CVE-2026-42945 (NGINX Rift).