

sast-scan-action
 offensive360/sast-scan-action
GitHub Action: Offensive360 SAST scan with SARIF output for code scanning. 60+ languages. Free for open source.
api-security-testingcloud-securitycode-analysis+4
offensive360/sast-scan-actionGitHub Action: Offensive360 SAST scan with SARIF output for code scanning. 60+ languages. Free for open source.
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 ericmtzmtz/pwnproxy
An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
 taptap/cve-2025-59489
Automated scanner that detects Unity runtime injection vulnerability CVE-2025-59489 in Android APKs by extracting Unity version and checking against…
 arian-gogani/enforcement-coverage
Finds API routes carrying weaker authorization than their siblings. Recovered CVE-2026-45316 from source. Includes the negative results.
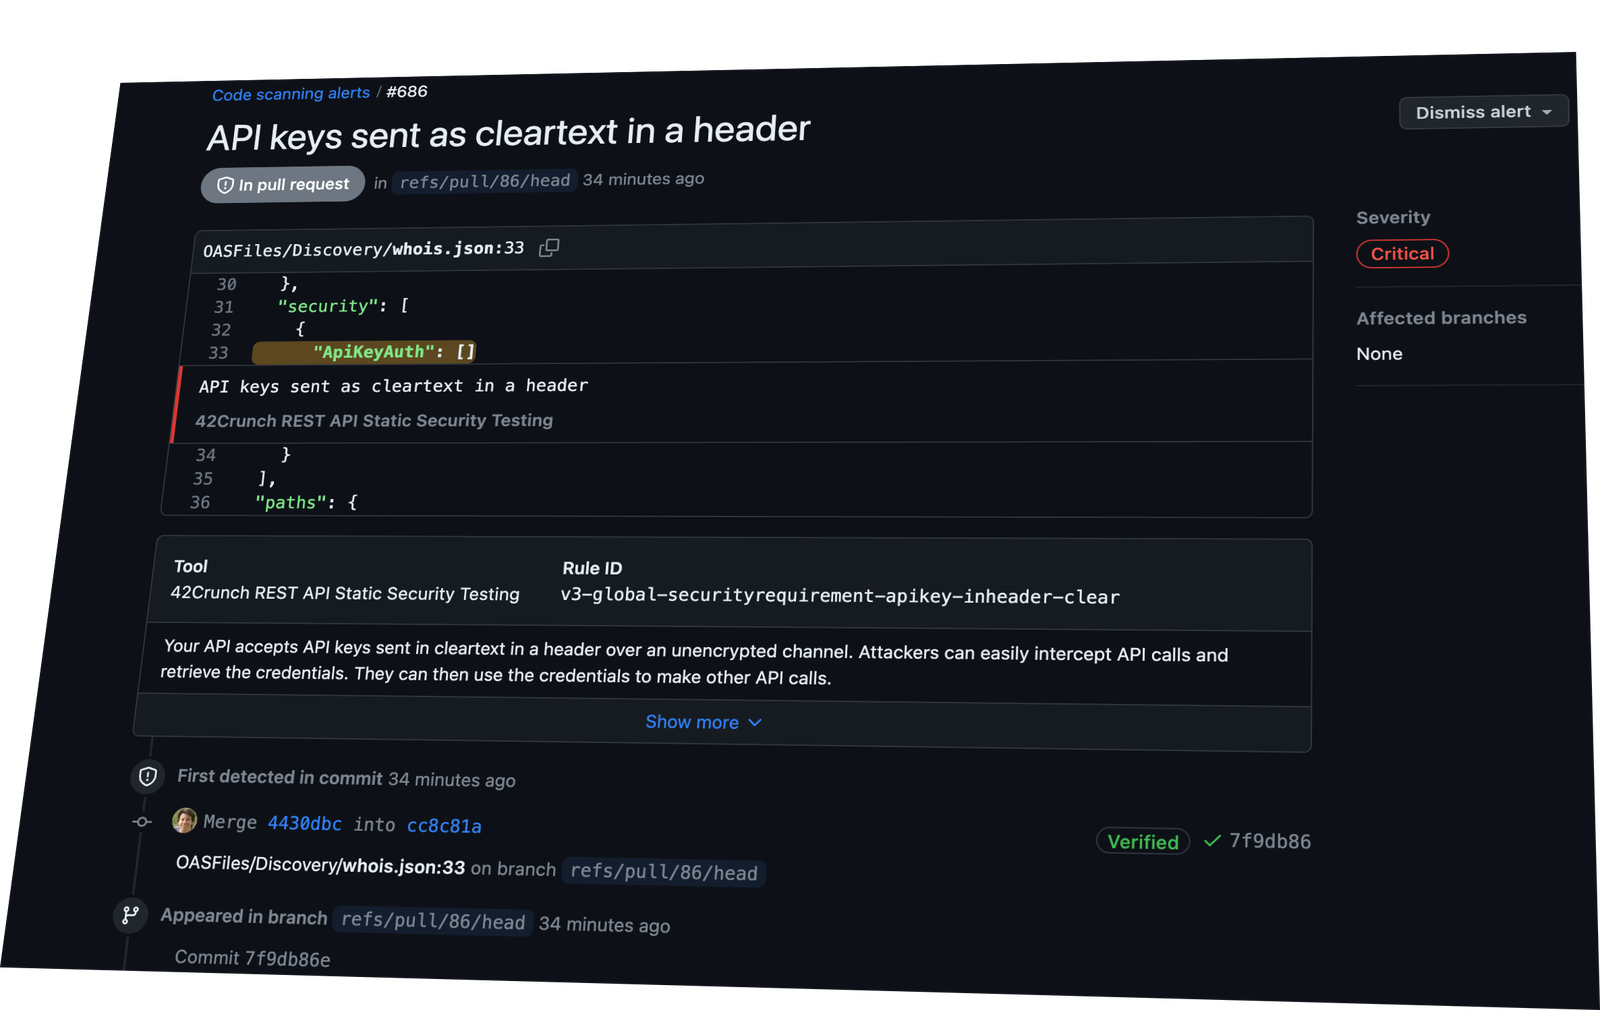 42crunch/api-security-audit-action
Automates static API security auditing of OpenAPI contracts in CI/CD, running 300+ checks for authentication, authorization, and data constraints,…
 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
 hahwul/smugglex
Rust-powered HTTP Request Smuggling Scanner.
 horizon3ai/h3-cli
CLI tool for the Horizon3.ai API
 pensarai/apex
AI-powered offensive security testing using autonomous agents, directly in your terminal.
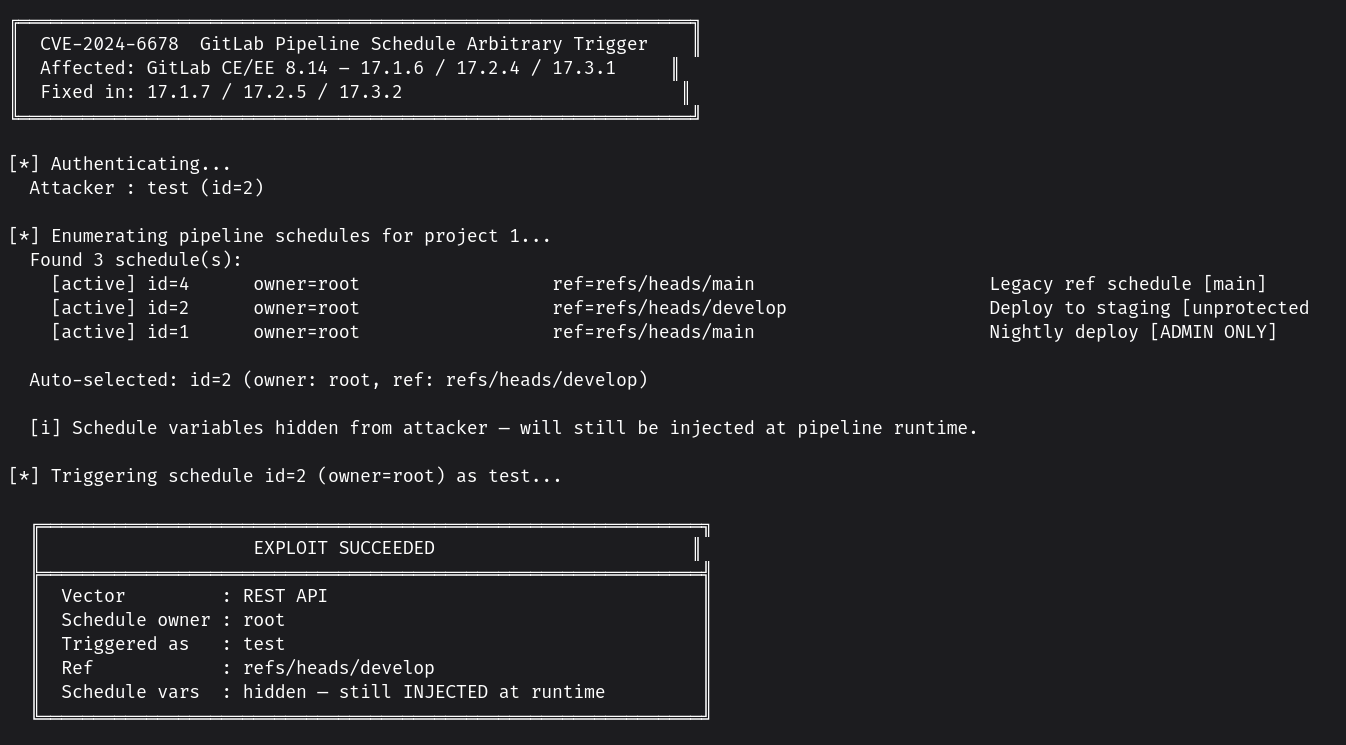
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 owasp/apicheck
Modular DevSecOps toolset for REST API security testing, designed for developers, sysadmins, and penetration testers to automate security checks…
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 owasp/agent-security-regression-harness
Executable security regression testing for agentic applications and MCP-integrated systems.
 infobyte/faraday_burp
Burp Extension for collaboration in Faraday
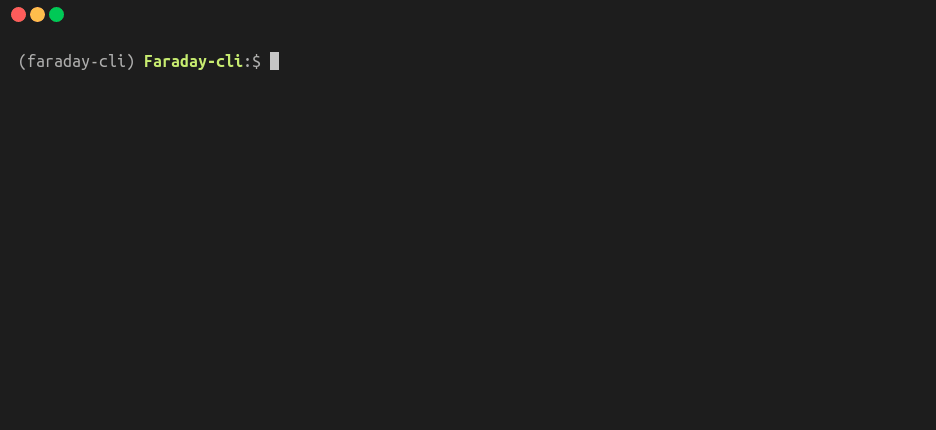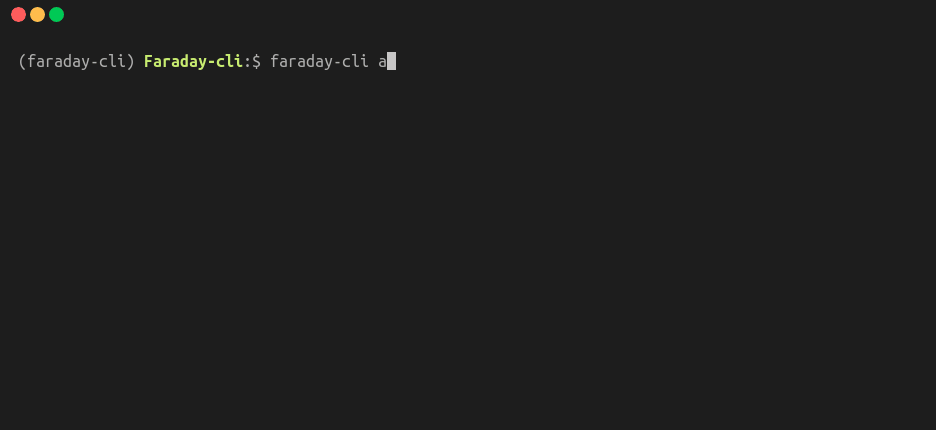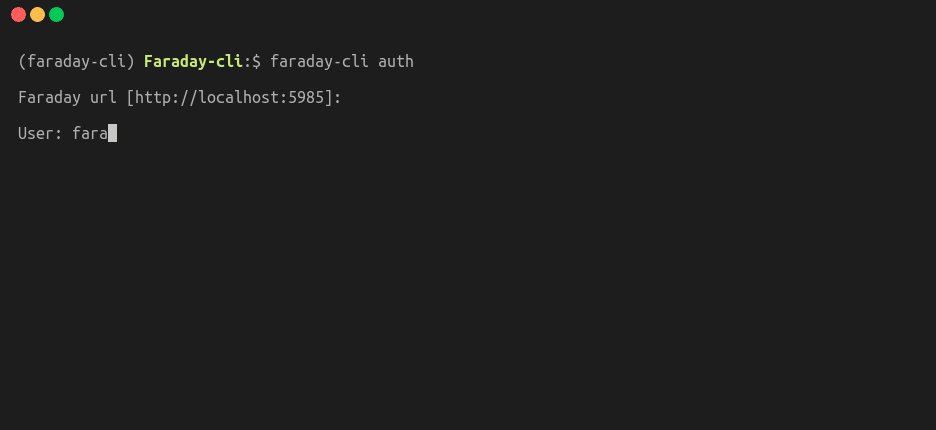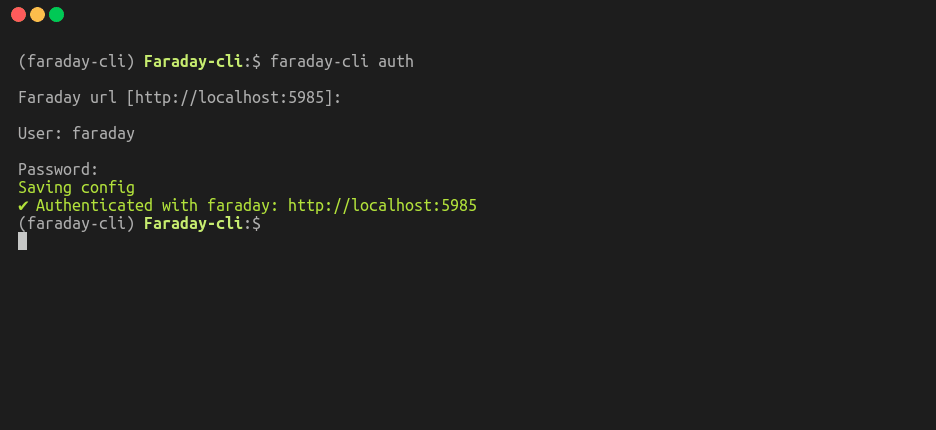 infobyte/faraday-cli
Faraday's Command Line Interface