
 pii-shield/pii-shield
Zero-code K8s sidecar for log sanitization. Detects secrets via Entropy Analysis, preserves JSON integrity, and redacts PII deterministically. 🛡️
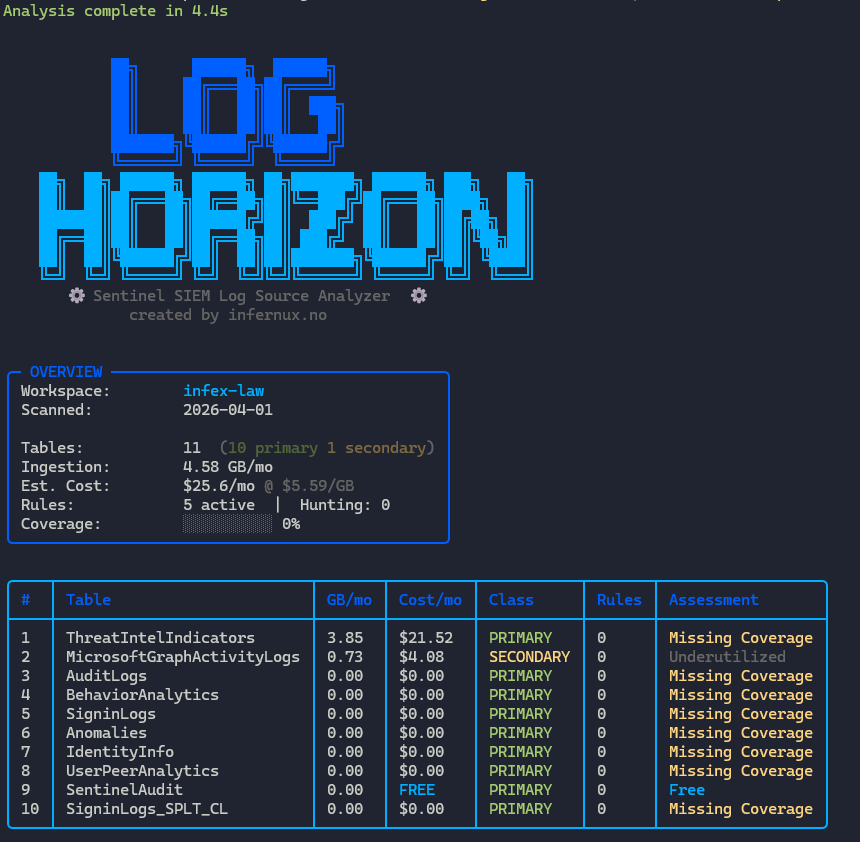 lnfernux/log-horizon
Microsoft Sentinel SIEM Log Source Analyzer
 siyad01/agentbox
Open-source sandboxed runtime for AI agents — gVisor/Docker isolation, credential vault, immutable audit log. Built after CVE-2026-25253.
 checkmarx/checkmarx-cve-2025-30066-detection-tool
Scans GitHub workflows and logs for indicators of CVE-2025-30066, detecting malicious actions and exposed secrets using Checkmarx 2ms integration.
 githubfoam/nxlog-ubuntu-githubactions
CI pipeline for building nxlog-ce on Ubuntu with CVE-2020-35488 vulnerability detection, enabling automated log collection and security auditing in…
 resery/cve-2019-17041
Proof-of-concept exploit for CVE-2019-17041, a buffer overflow in rsyslog's parser, demonstrating remote code execution.
 knqyf263/aqua-checksums
Monitors cryptographic integrity of container images, releases, and Git tags for supply chain security, verifying Sigstore cosign signatures with…