
advisory-database
 pypa/advisory-database
Community-owned database of security advisories for Python packages on PyPI, providing structured vulnerability data in OSV format for integration…
curated-resourcesdevsecopssupply-chain-security+2
372
pypa/advisory-databaseCommunity-owned database of security advisories for Python packages on PyPI, providing structured vulnerability data in OSV format for integration…
 sorami-consulting-au/ai-kubernetes-helm-chart-security
Evidence and data for the Sorami technical report on security defaults of 15 AI serving, vector database and MCP Helm charts on Kubernetes.
 gmh5225/actions-secrets
Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…
 node9-ai/node9-proxy
Access control for AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run,…
 pgbackrest/pgbackrest
Parallel backup and restore solution for PostgreSQL with encryption, delta restore, and multi-cloud object store support for enterprise disaster…
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 xiaoqimikko/netty-http-check
Offline Java tool that scans application jars to determine exposure to 14 Netty codec-http CVEs, identifying the exact patched version…
 baidu/openrasp
Runtime application self-protection engine that hooks into application servers to monitor and block malicious database queries, file operations, and…
 slowql/slowql
Next-generation SQL static analyzer written in Rust. 282+ rules. Zero false positives. Security, performance, reliability, cost, compliance, quality.…
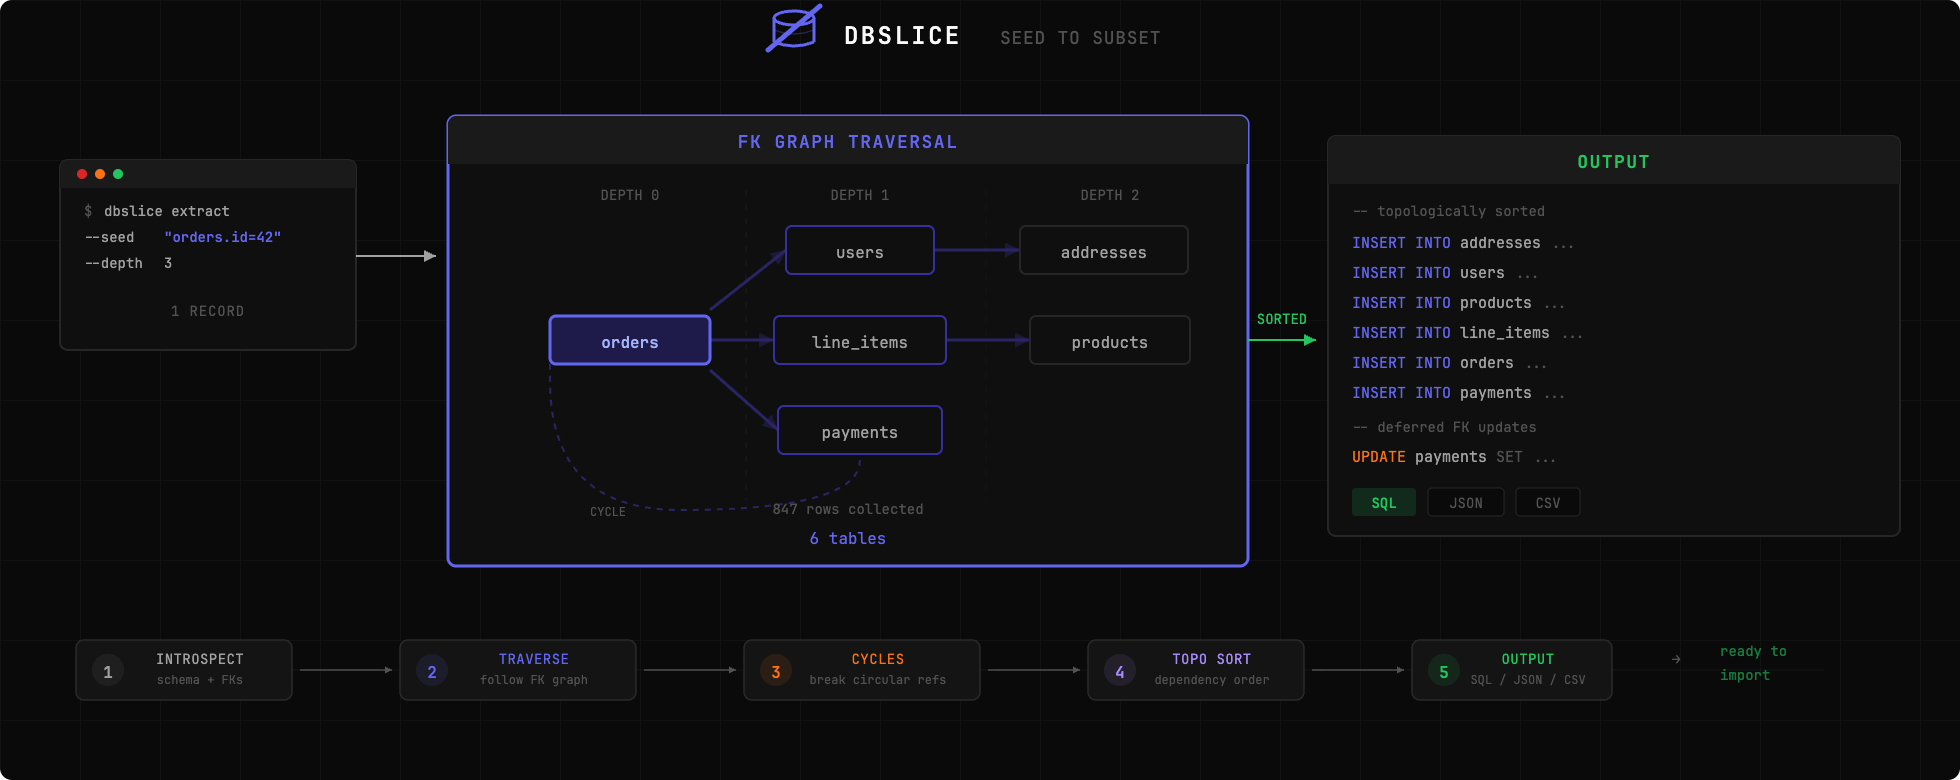 nabroleonx/dbslice
Extract a slice of your production database to reproduce bugs locally. Point dbslice at a record, it follows foreign keys and gives you a complete,…
 moisei-dev/go-dbmigrate
Go library and CLI for managing database schema migrations with support for PostgreSQL, MySQL, SQLite, and Cassandra, including up/down migration…
 farenhytee/database-sentinel
Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…
 cycodelabs/raven
Scans GitHub Actions CI/CD workflows for security vulnerabilities, indexes findings into a Neo4j graph database, and provides a query library for…
 pgedge/pgedge-anonymizer
An anonymizer tool for replacing PII and similar data in dev/test databases copied from production
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.