
ftw
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
devsecopspenetration-testingvulnerability-scanners+2
143
coreruleset/ftwYAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 ffffffff0x/f8x
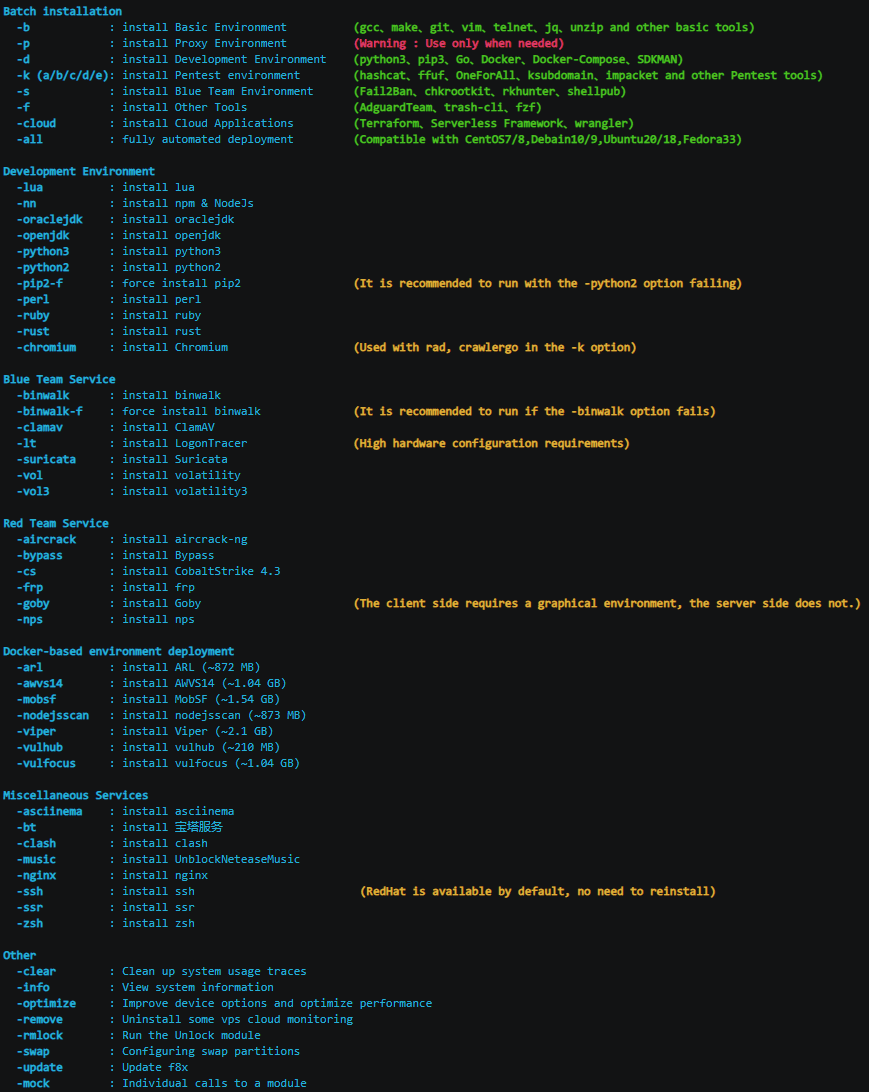
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
 nihal799/zttp
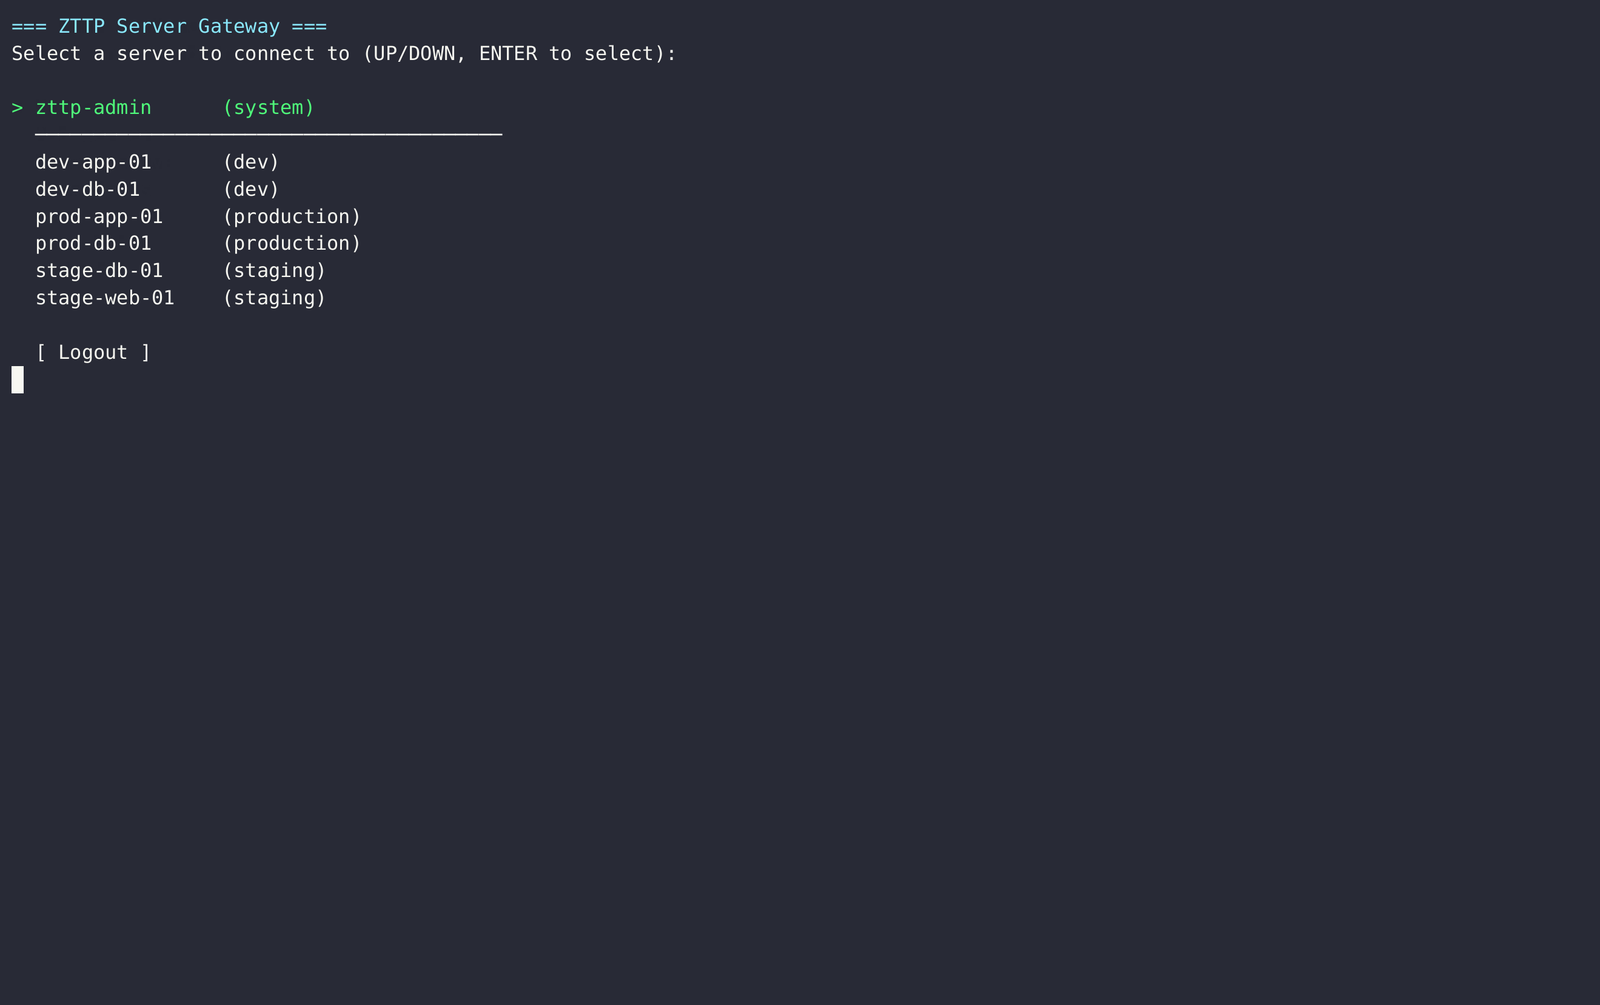
Zero-trust SSH bastion proxy with Vault-backed key management, RBAC policy enforcement, full session recording, and admin TUI for auditable access to…
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
 owasp/docksec
AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.
 godaddy/tartufo
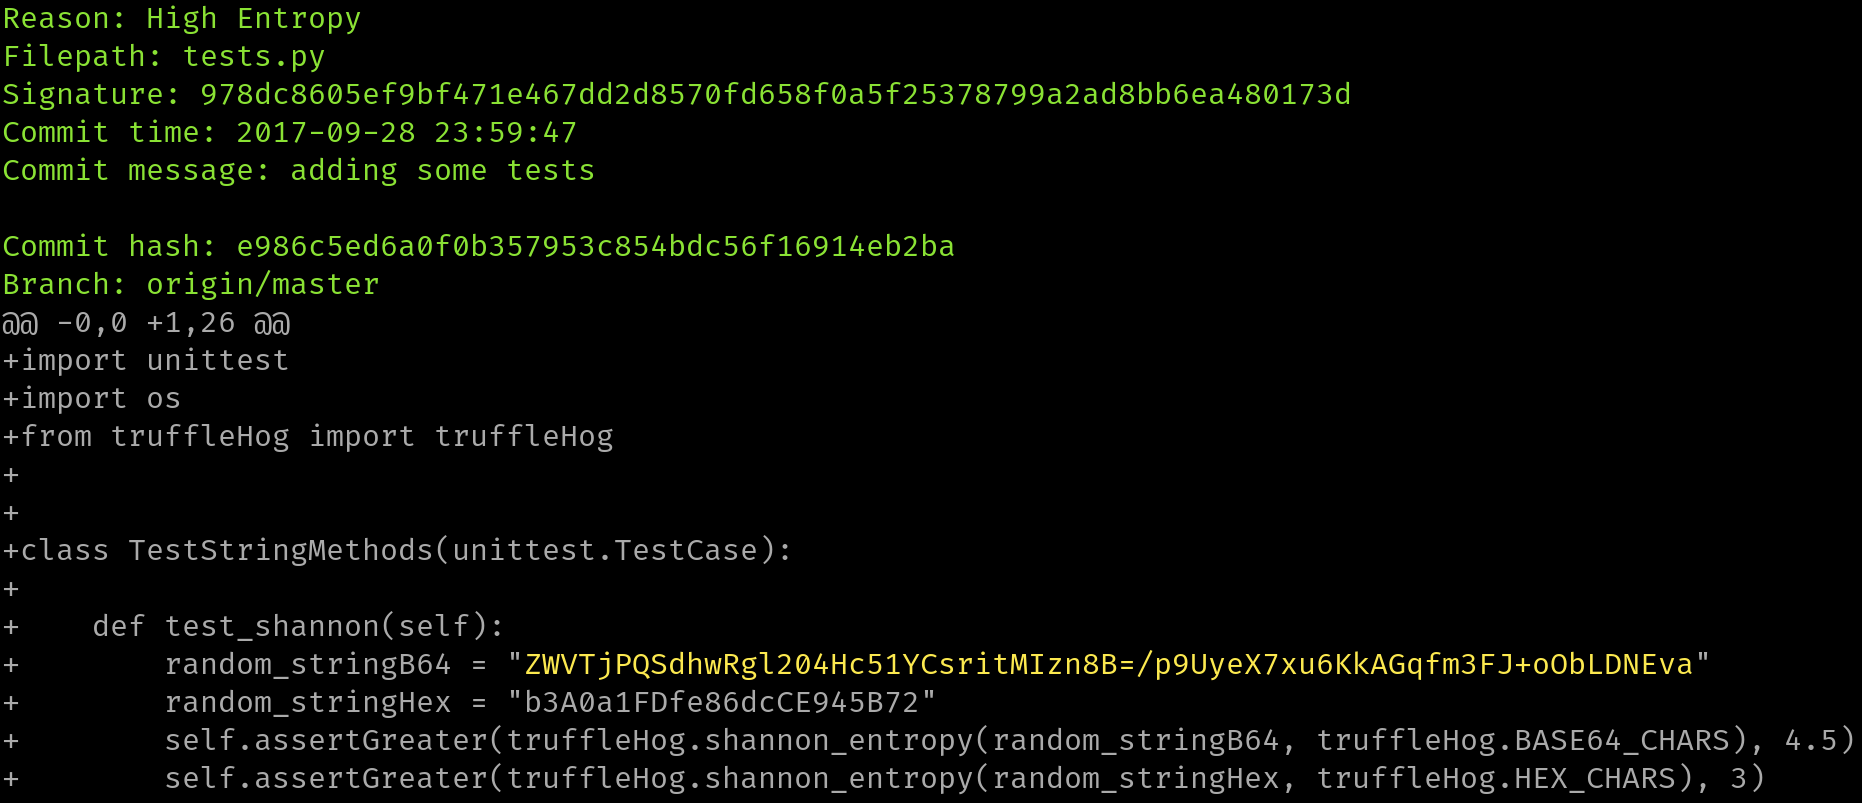
Searches through git repositories for high entropy strings and secrets, digging deep into commit history
 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency.
 swiftdevcollective/xcodeprojectsecurity
A macOS app to scan Xcode project files for possible security issues.
 threatspec/threatspec
threatspec - continuous threat modeling, through code
 ccfos/nightingale
Open-source alerting engine for time-series monitoring data. Connects to Prometheus, VictoriaMetrics, ElasticSearch, and other data sources. Supports…
 opnsense/core
OPNsense GUI, API and systems backend
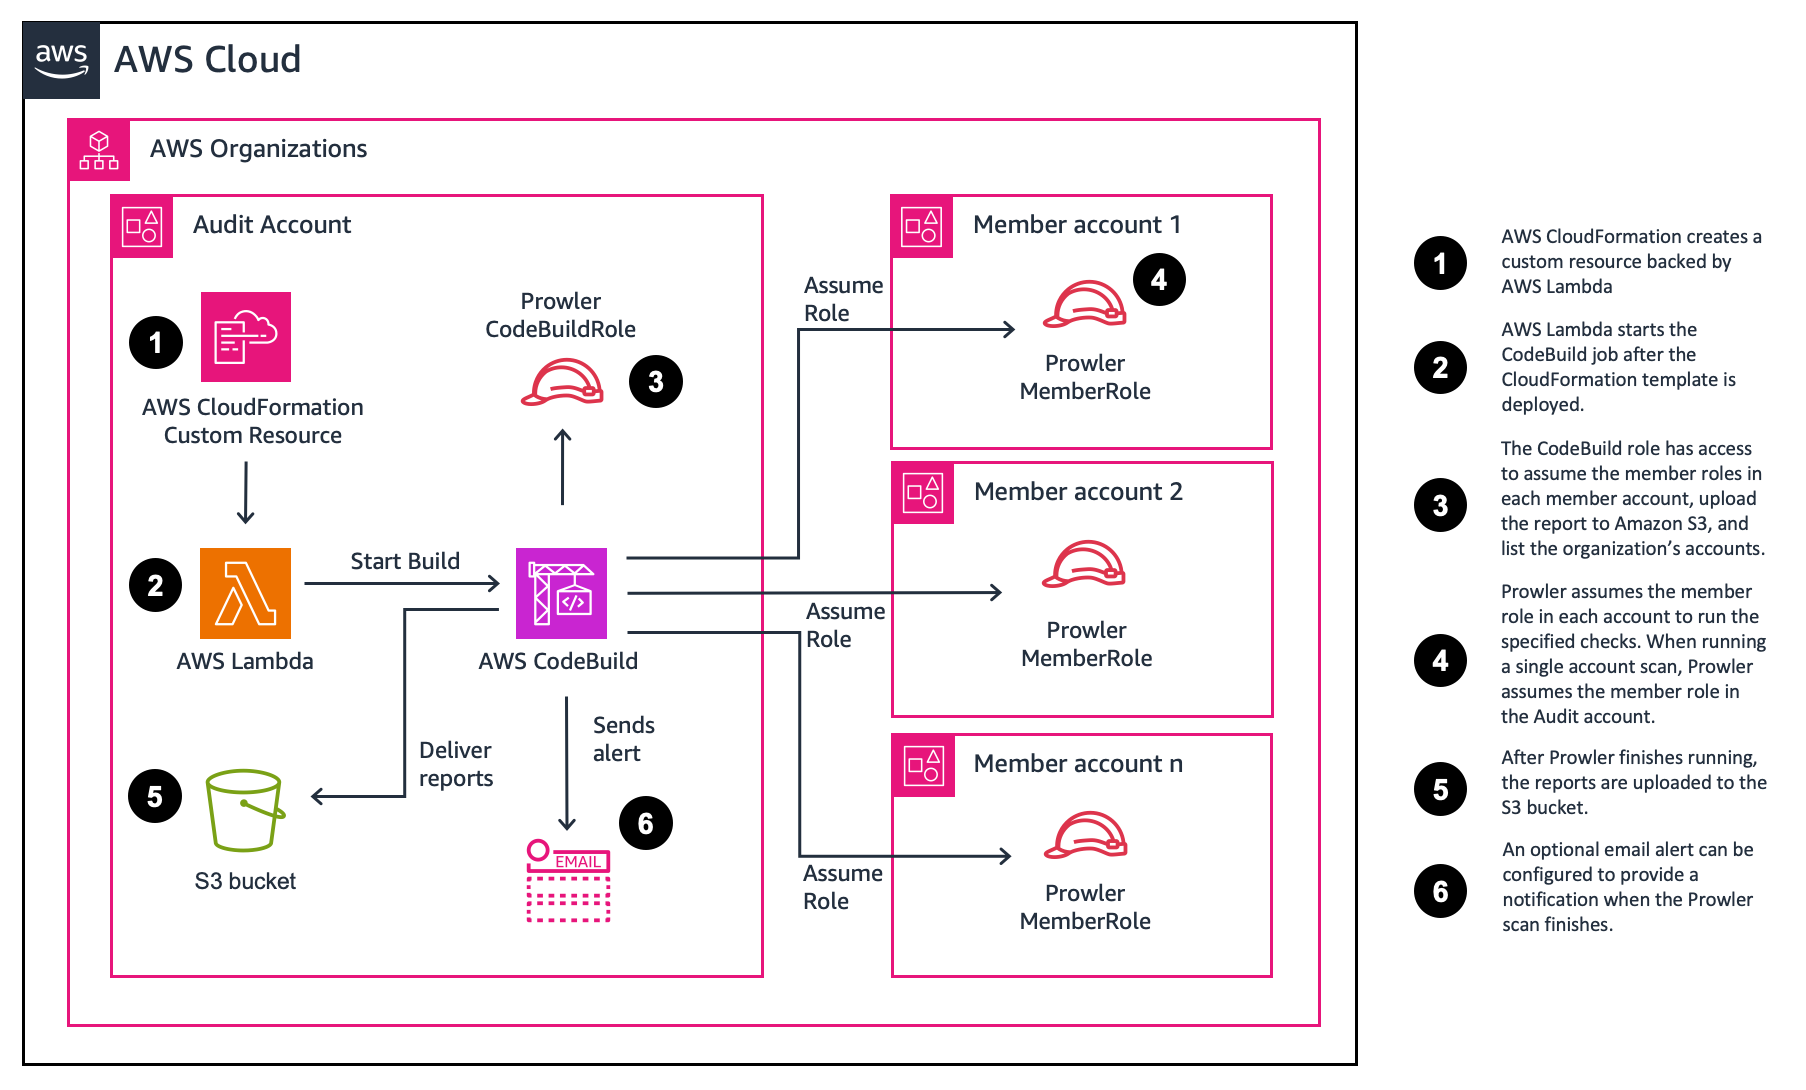 awslabs/aws-security-assessment-solution
An AWS tool to help you create a point in time assessment of your AWS account using Prowler.
 nestybox/sysbox
An open-source, next-generation "runc" that empowers rootless containers to run workloads such as Systemd, Docker, Kubernetes, just like VMs.
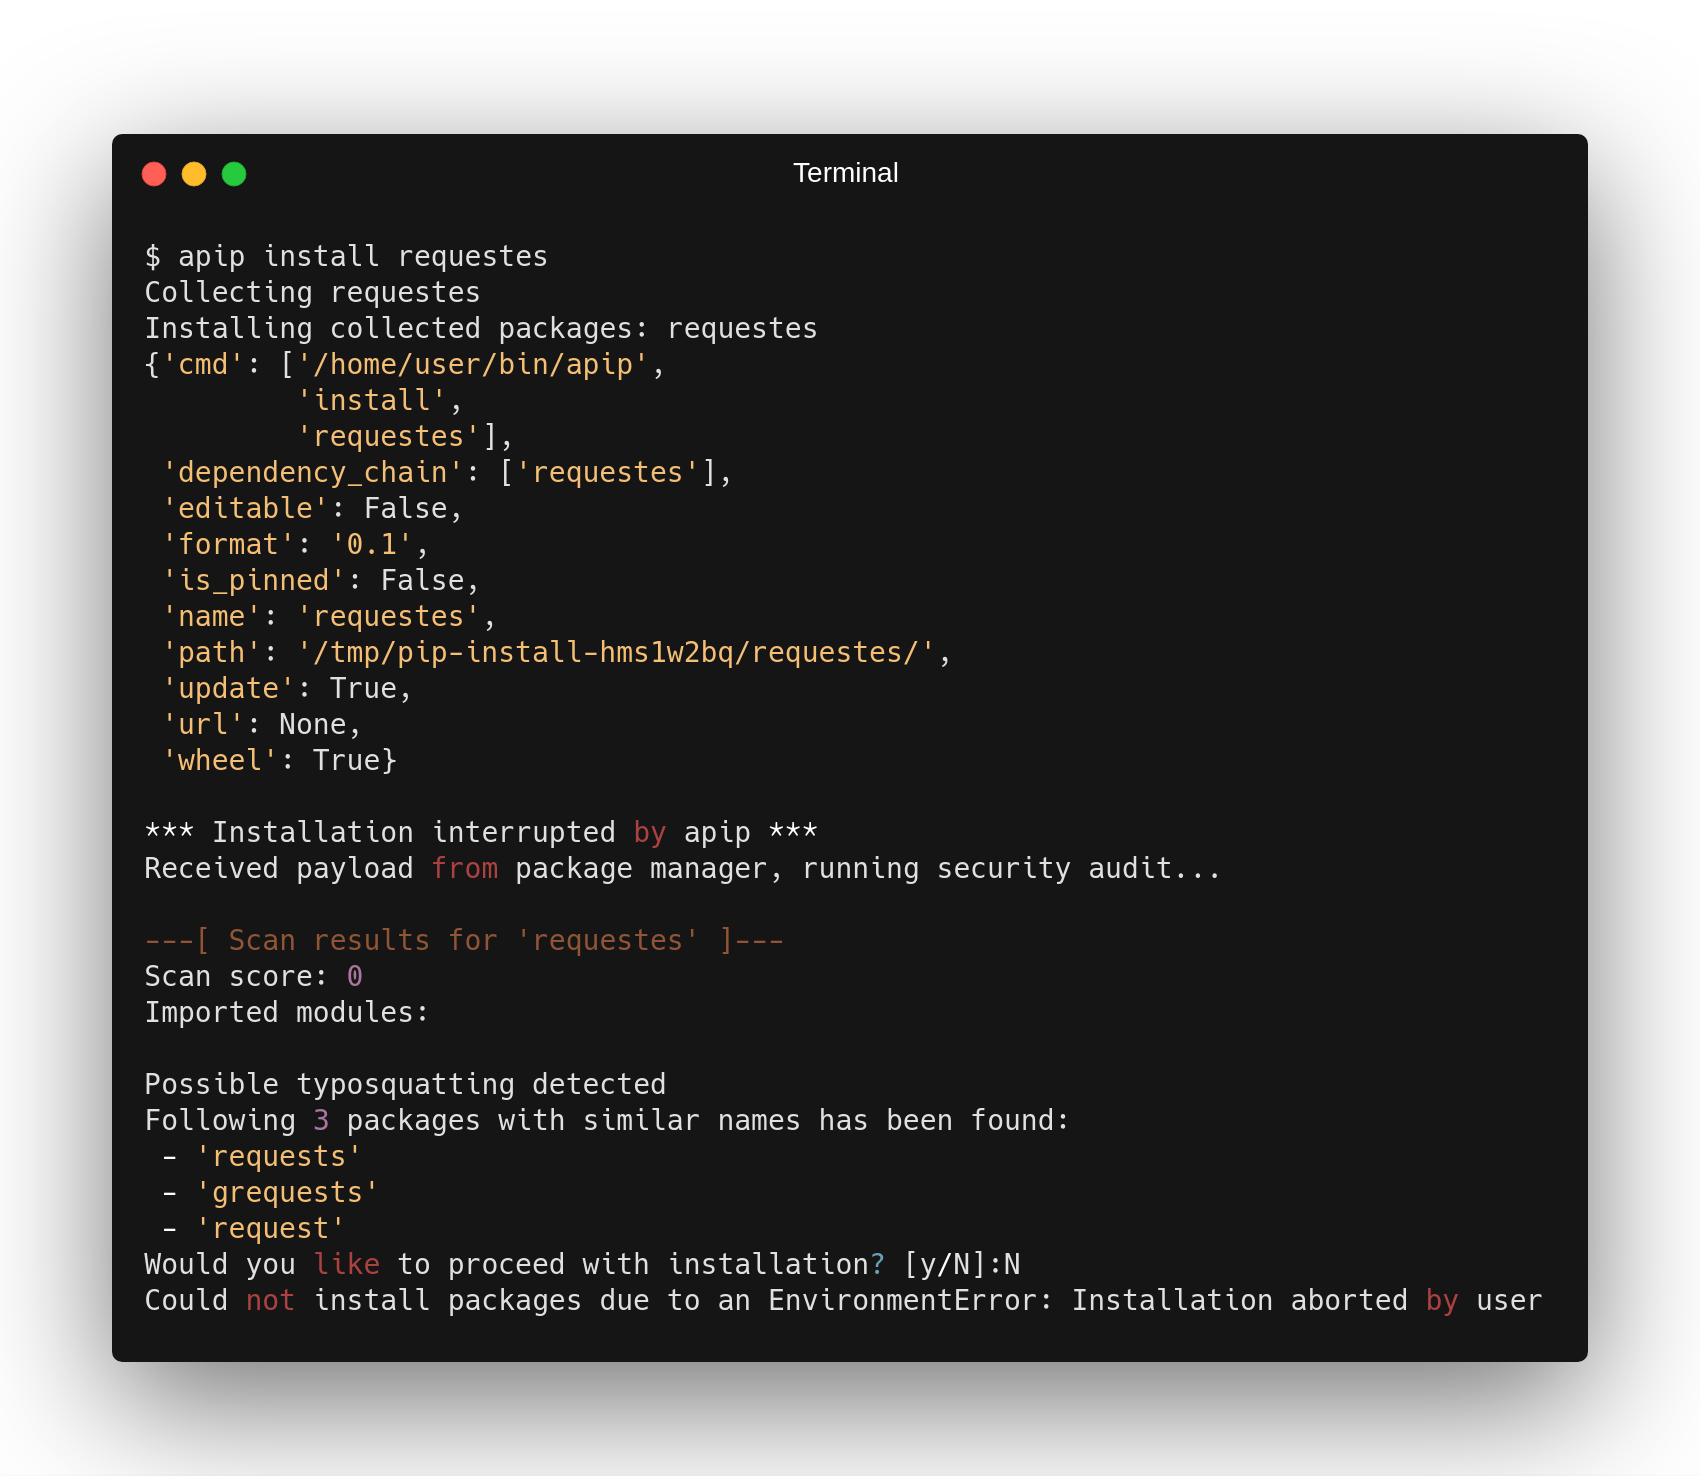 rootlug/aura
Project Aura: Security auditing and code introspection
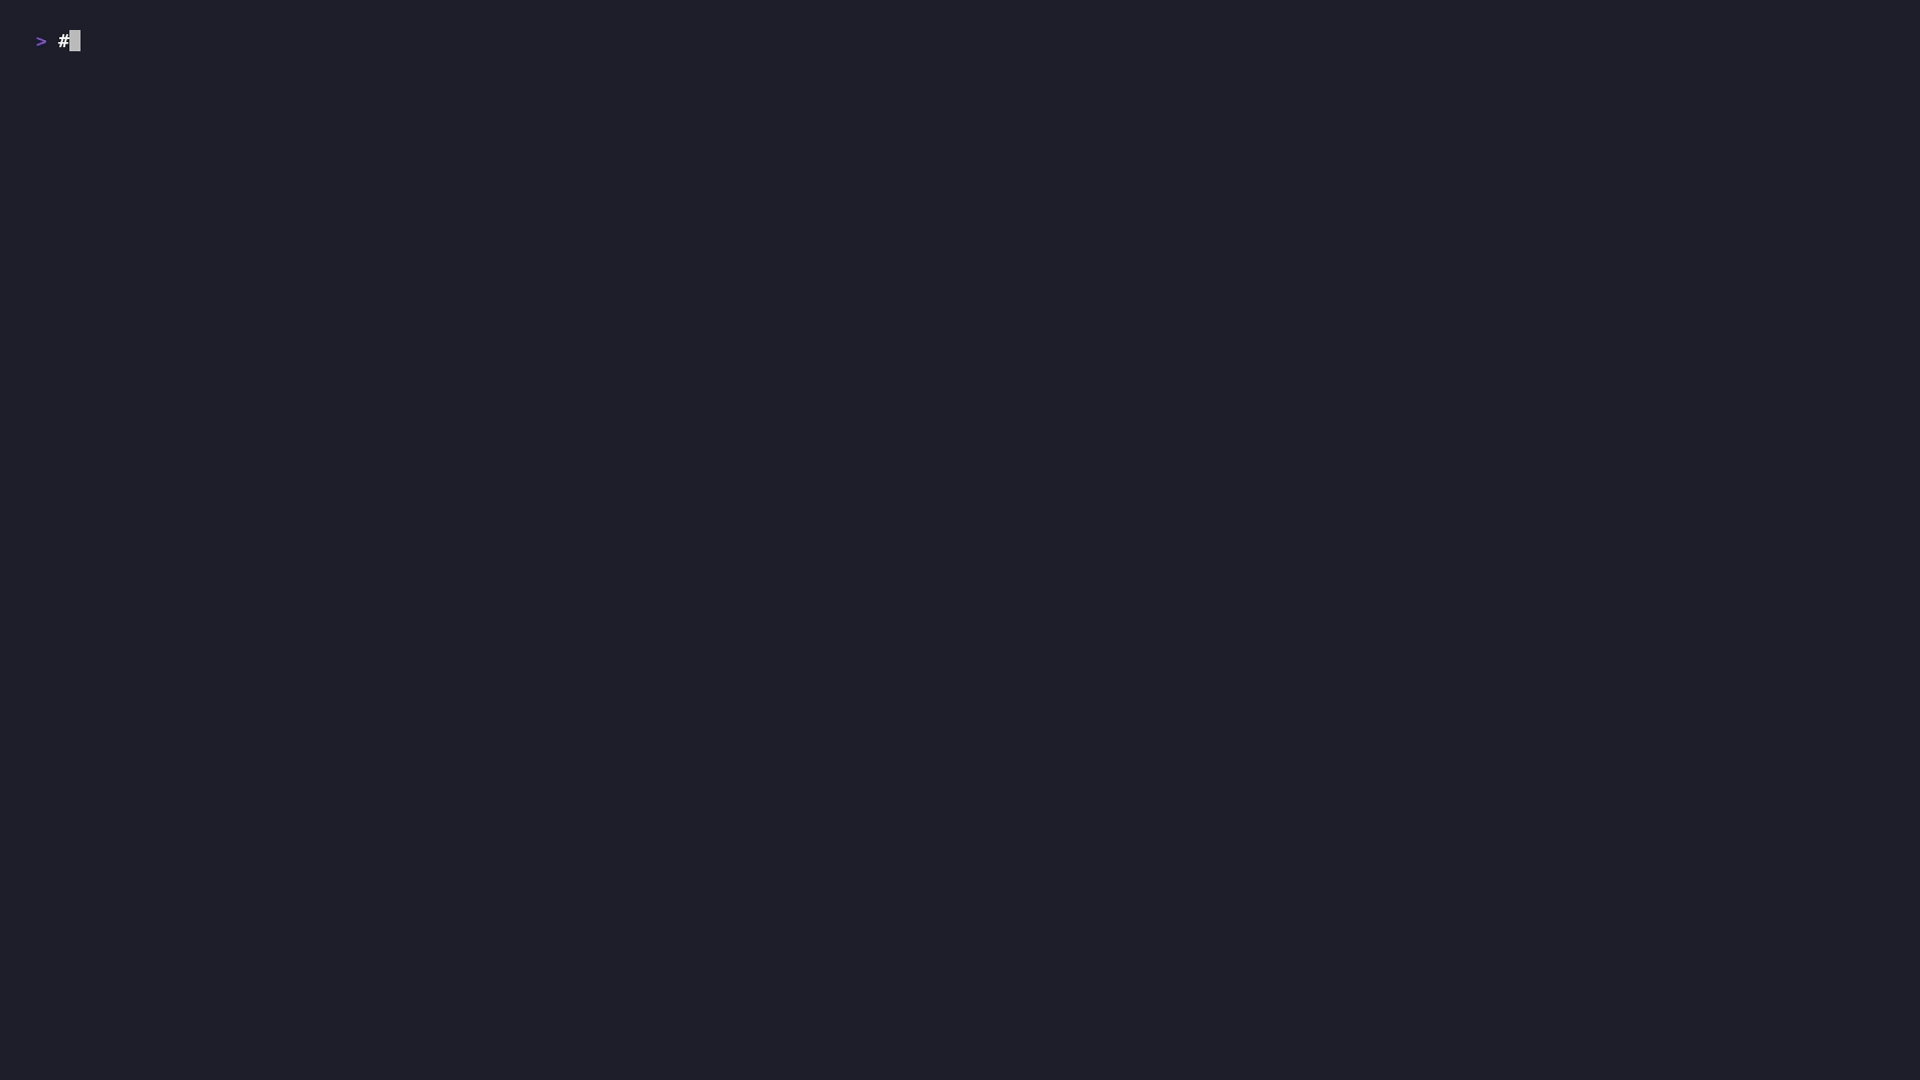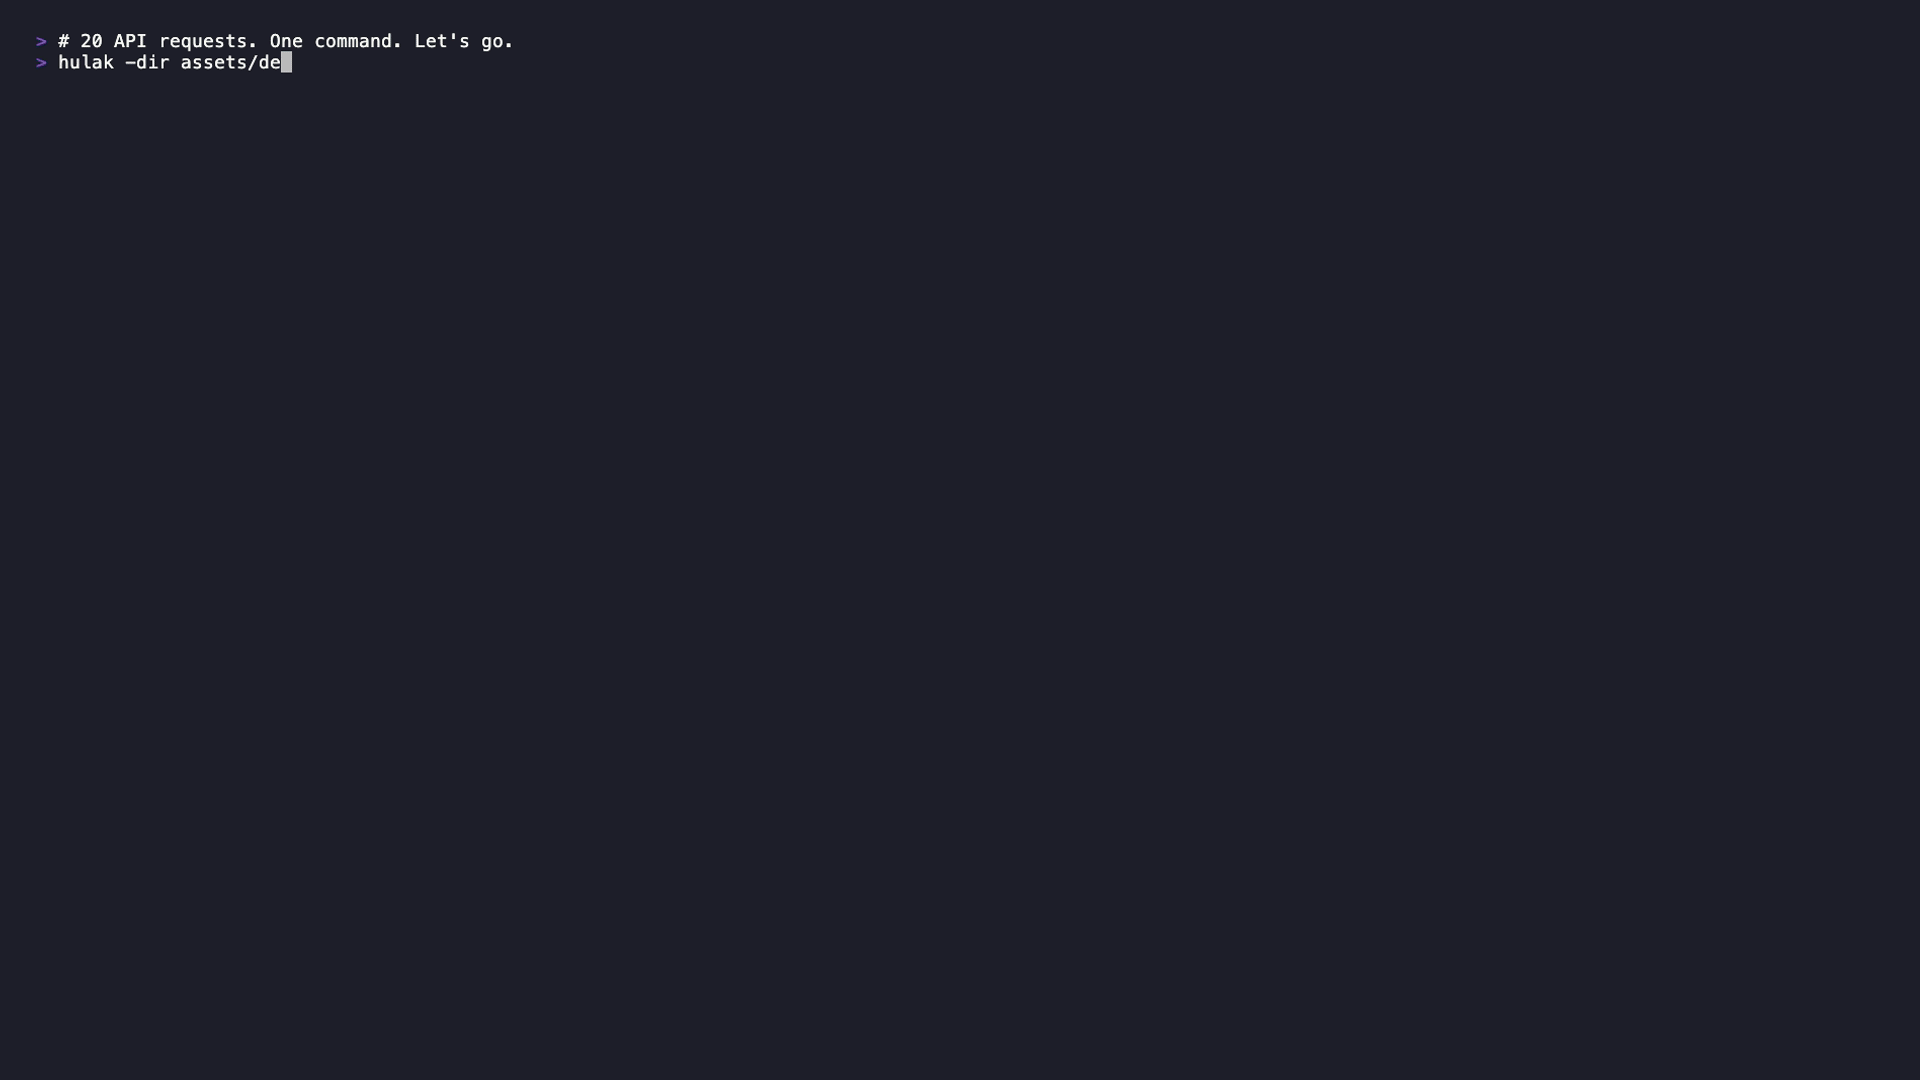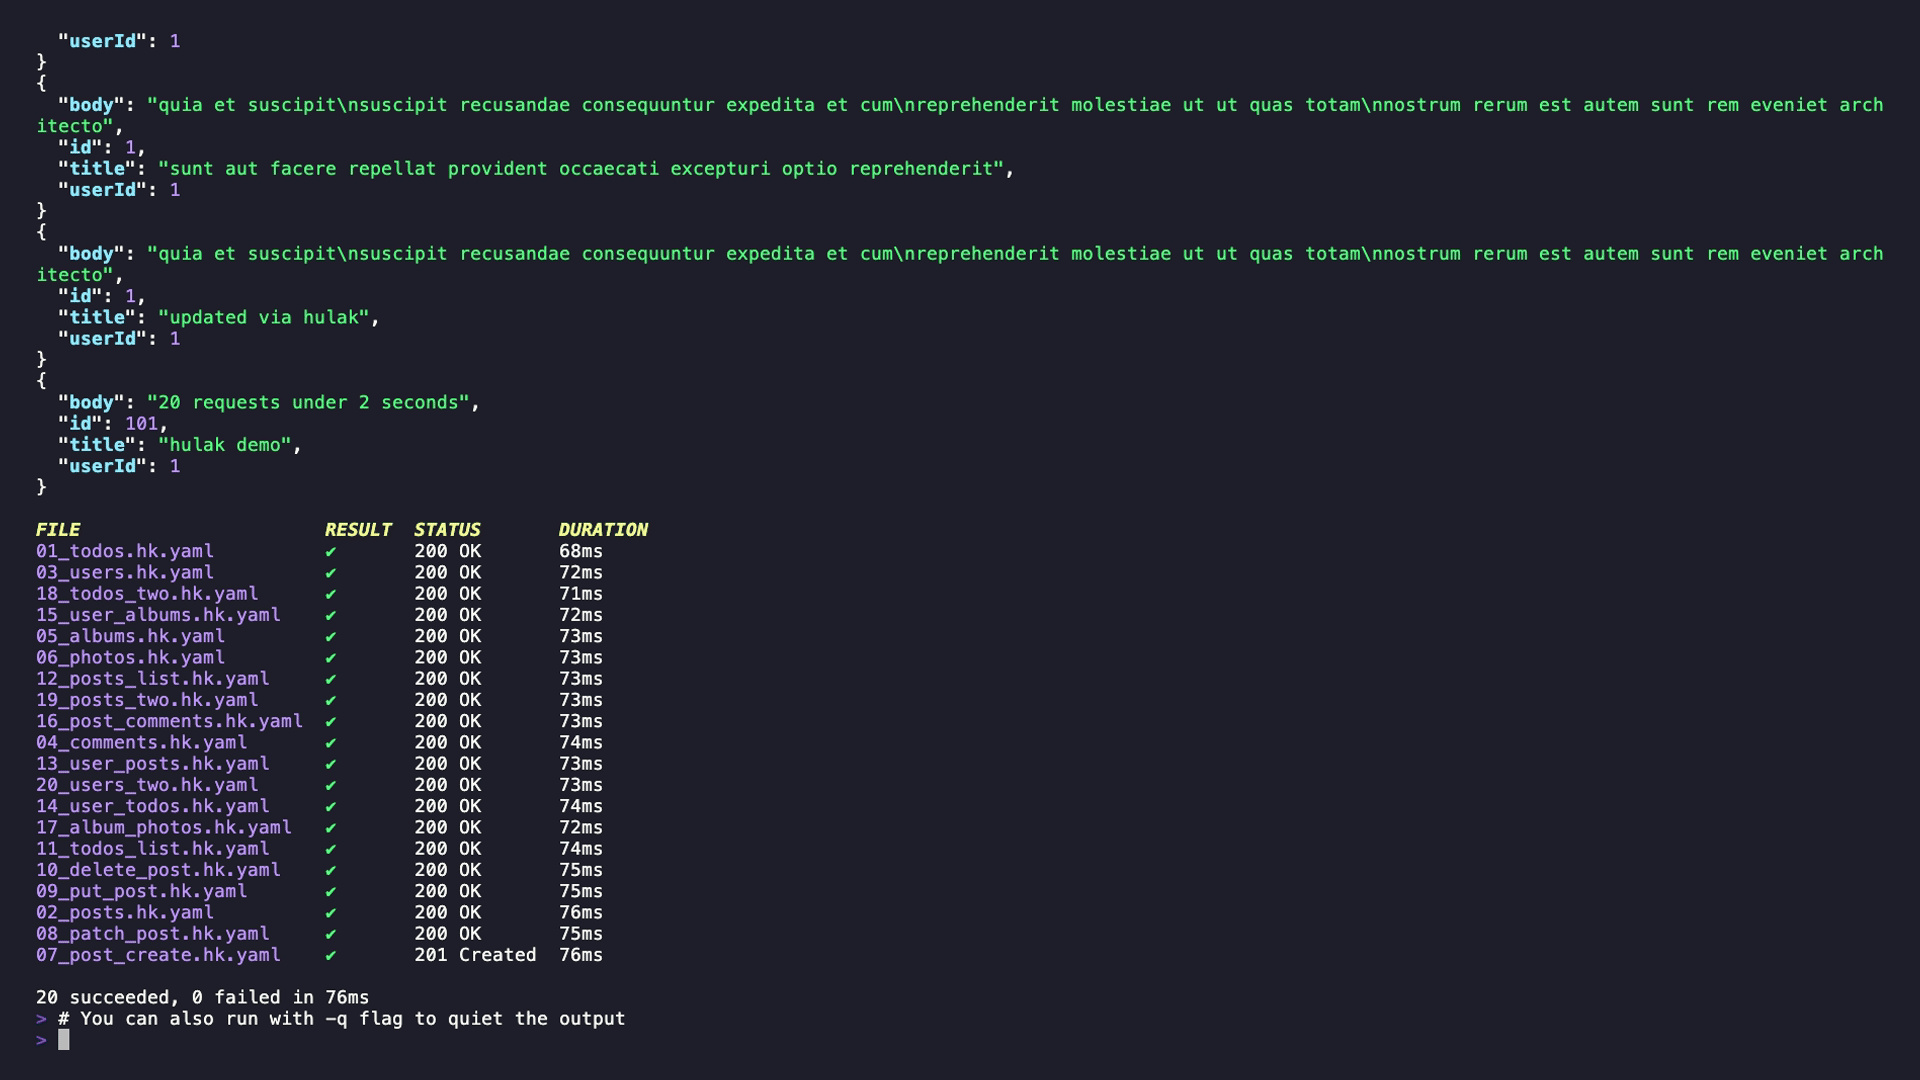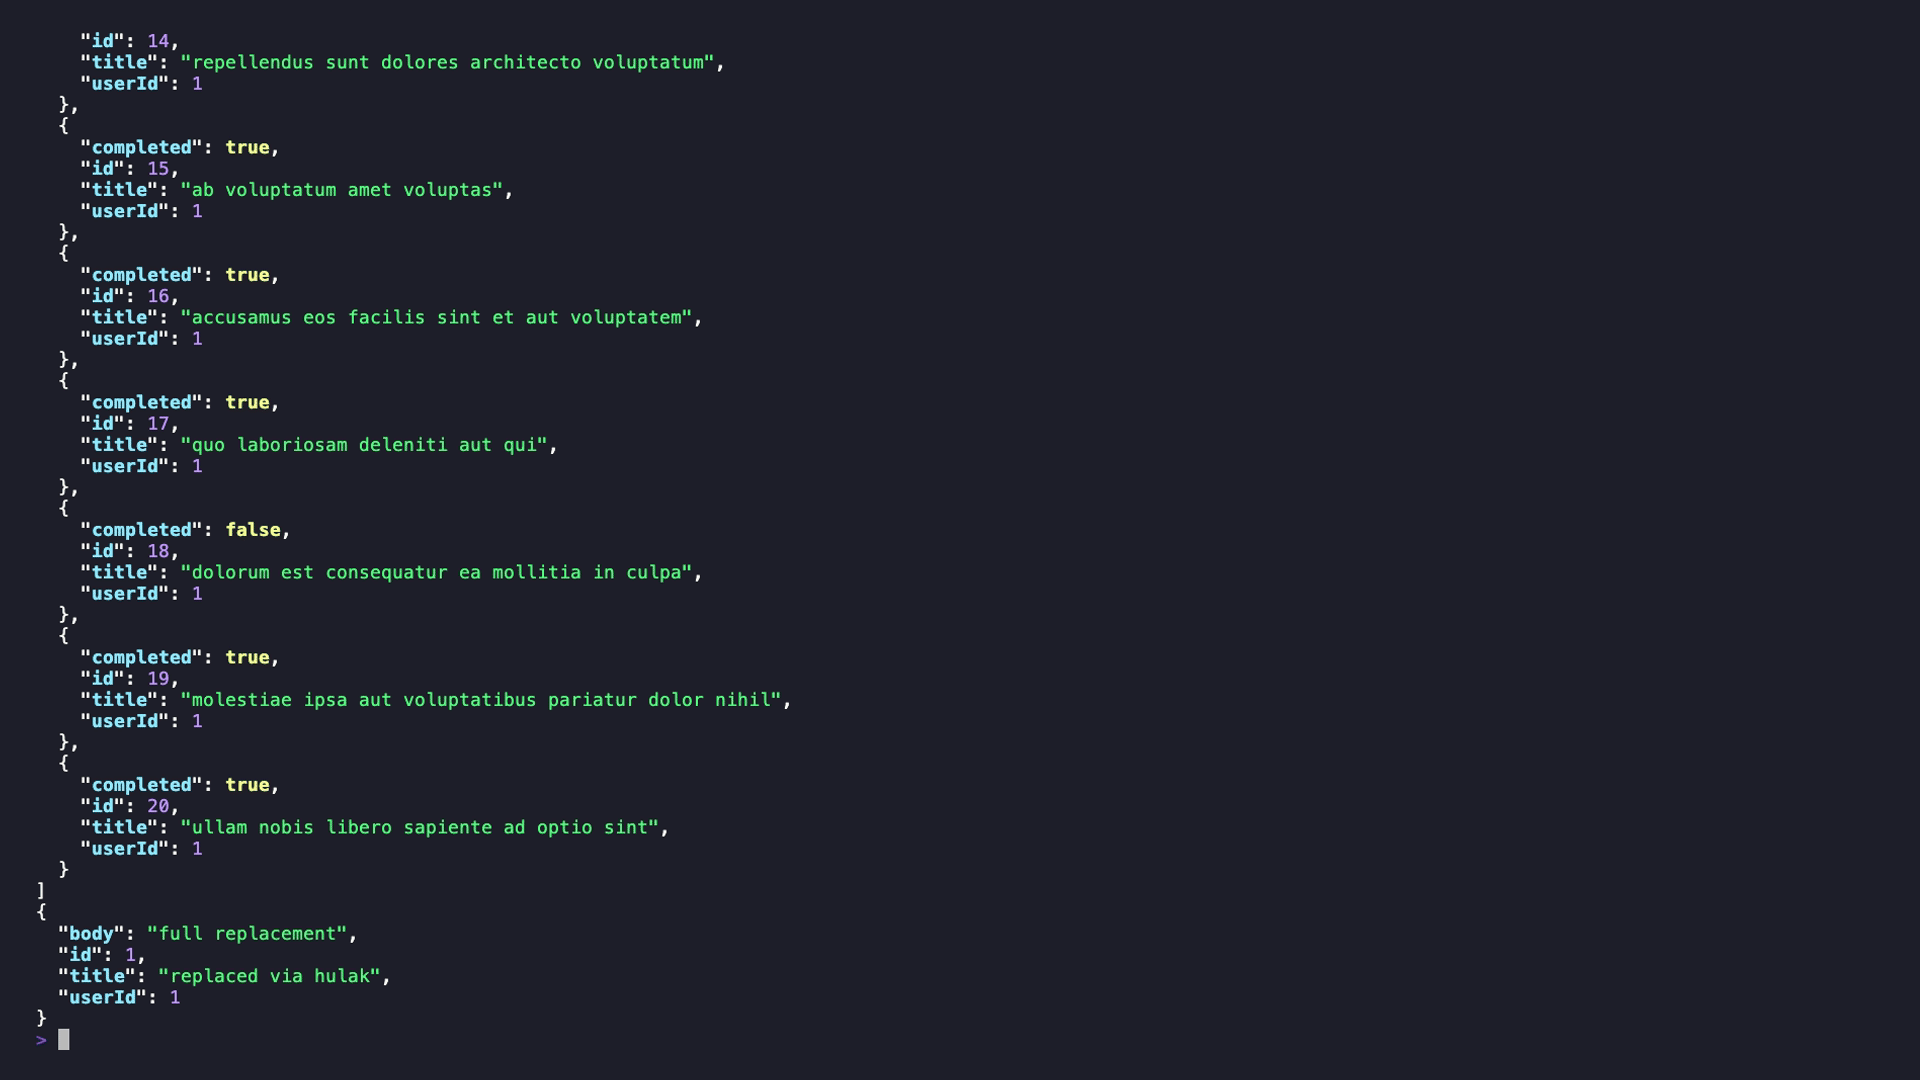 xaaha/hulak
Lightweight file-based CLI API client with age-encrypted secrets, first-class GraphQL support and MCP server for agentic workflow.
 poshbotio/poshbot
Powershell-based bot framework