Mobile-Security-Framework-MobSF

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…

This puppet module provides numerous security-related configurations, providing all-round base protection.

Automated scanner that detects Unity runtime injection vulnerability CVE-2025-59489 in Android APKs by extracting Unity version and checking against…

Web-based Source Code Vulnerability Scanner

Easy setup of static analysis tools for Android and Java projects.

Ansible Playbook for CVE-2023-36845(Juniper Networks Junos OS 远程代码执行漏洞)

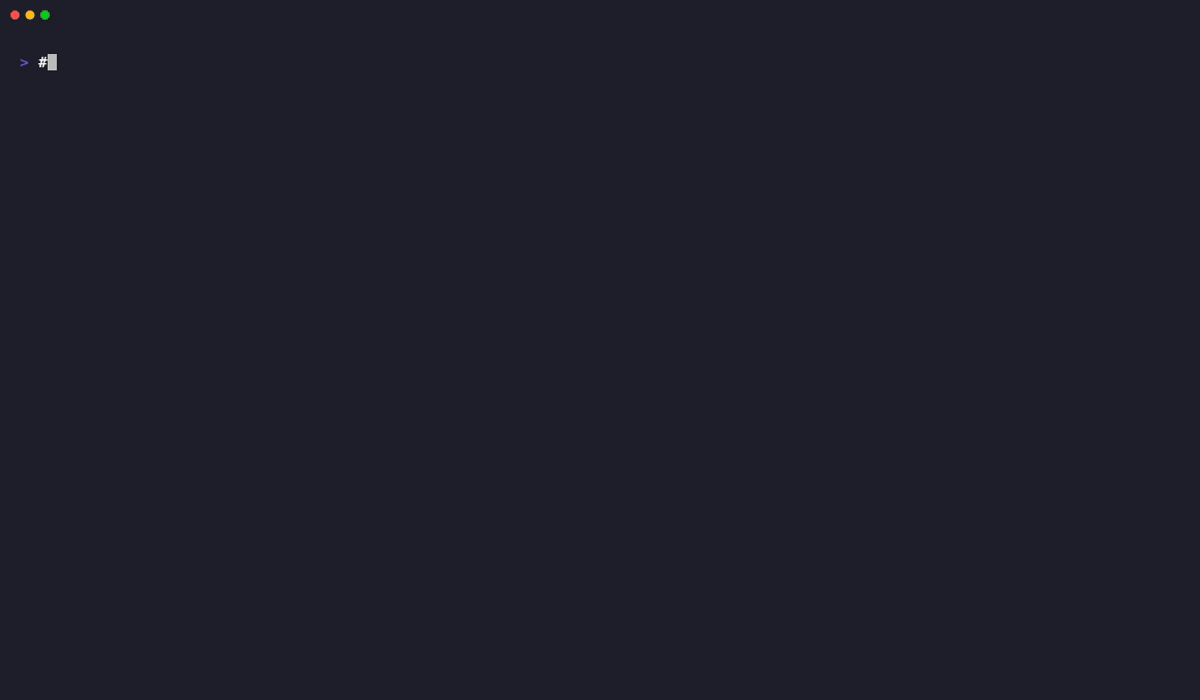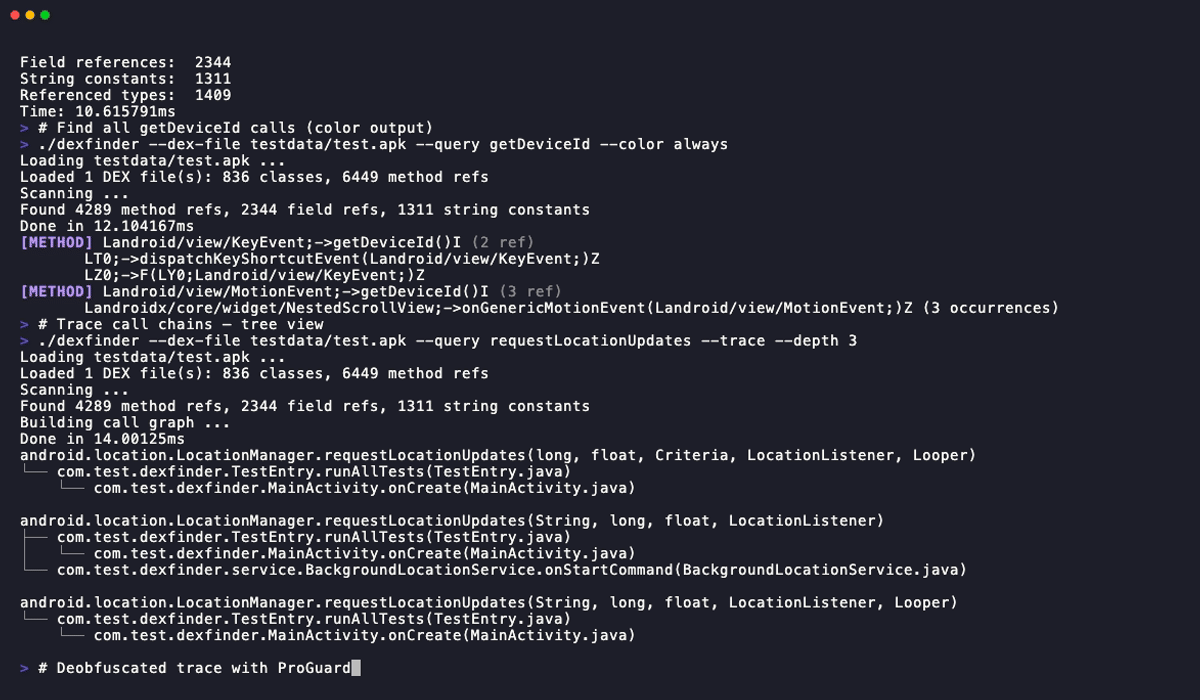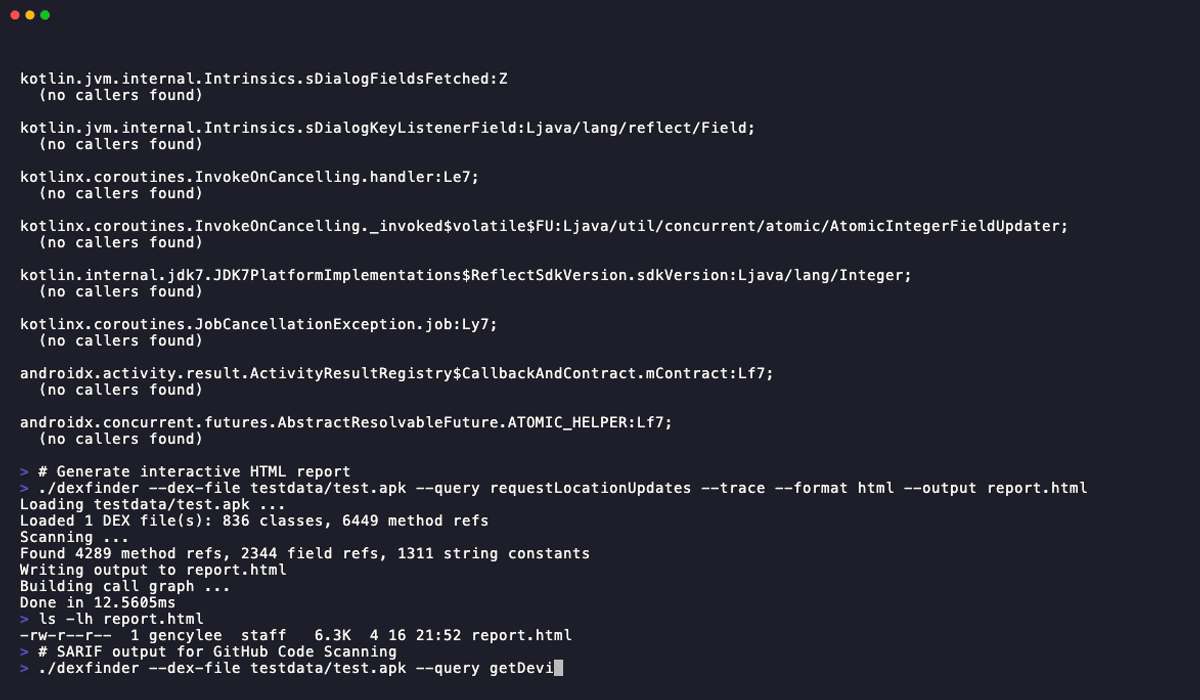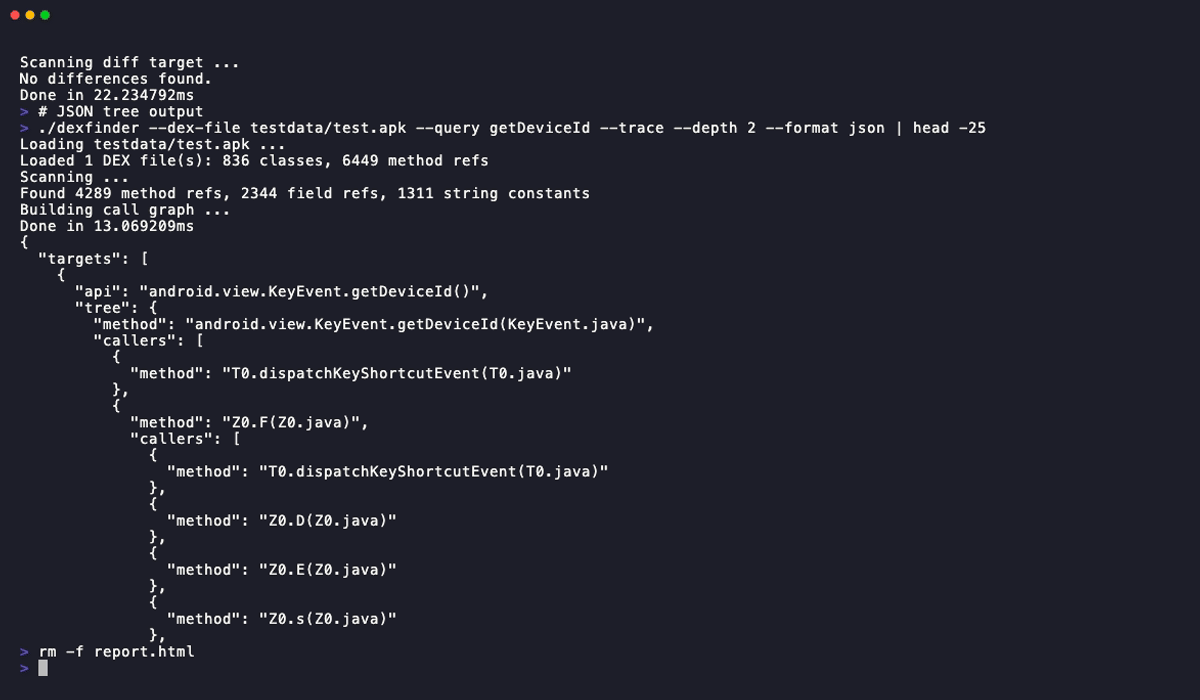
Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection

Read-only audit tooling for CVE-2026-0300 (PAN-OS User-ID Authentication Portal exposure)

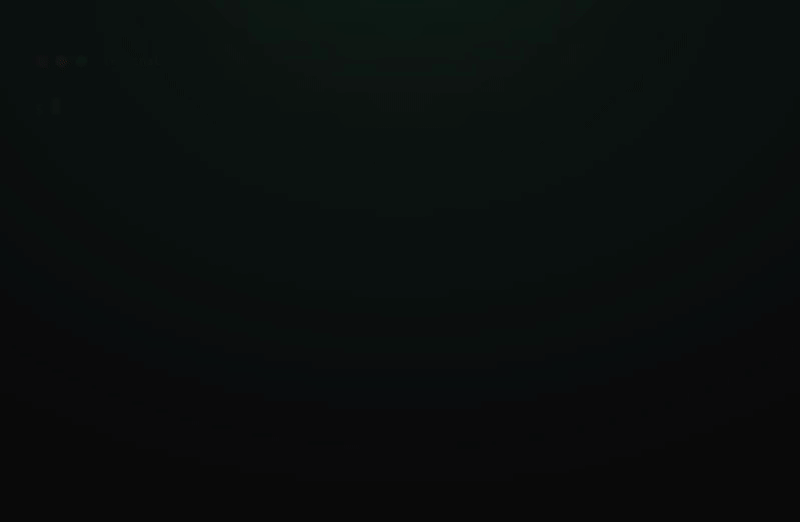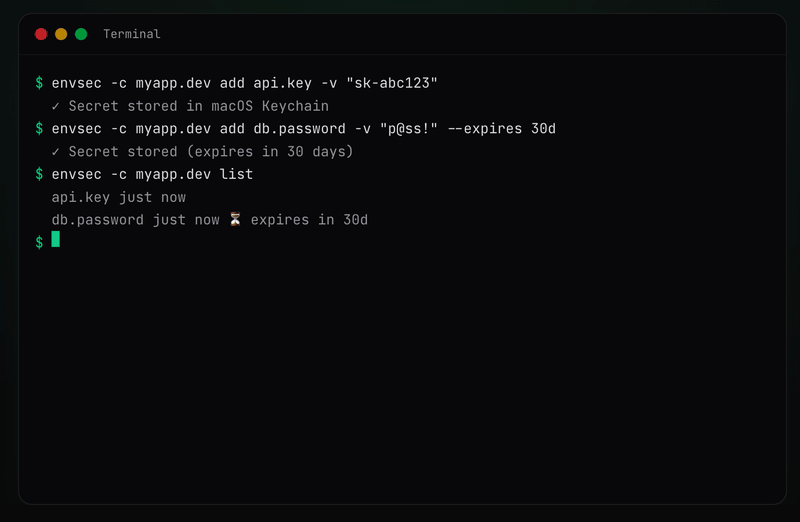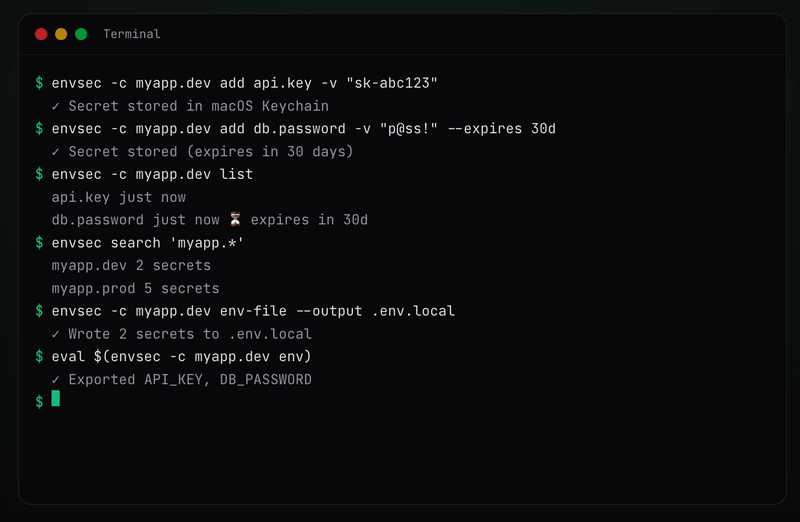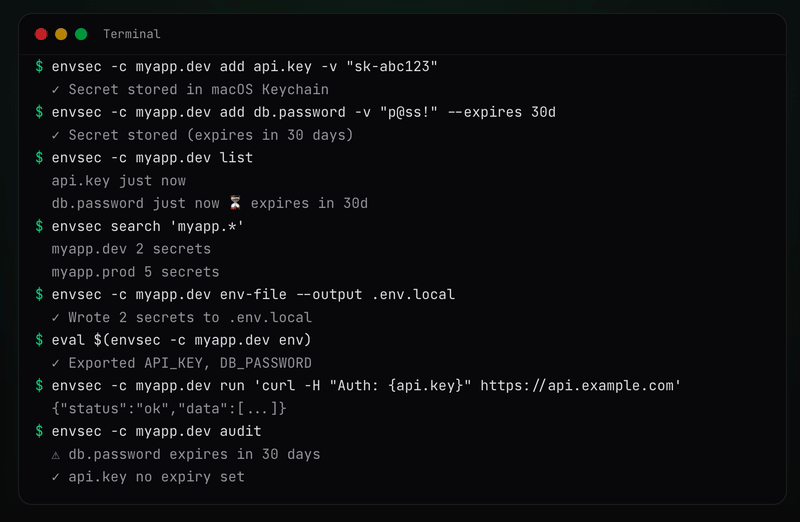
Secure CLI tool for managing environment secrets using native OS credential stores (macOS Keychain, Linux Secret Service, Windows Credential Manager)

Static code analysis plugin for Android project. (Checkstyle, PMD)

Git diff for SBOMs—compare CycloneDX, SPDX, and Syft documents, detect tampering, and gate CI.

This Ansible role provides numerous security-related ssh configurations, providing all-round base protection.

Patch: Command injection in GlobalProtect (Palo Alto PAN-OS)

Workaround for CVE-2025-52881: Fixes Docker/Podman breakage in Proxmox LXC containers caused by AppArmor incompatibility with runc 1.2.7+. Universal…

Android CVE-2024-0044, 43093, 23706 zafiyet analizi ve PoC lab ortamı

composer require delivery of Adobe's official APSB26-146 (CVE-2026-75650) fix for Mage-OS stores, via cweagans/composer-patches. Companion to…

Patch Manual para a correção das CVE-2025-26465-e-CVE-2025-26466, para sistemas sem update do OpenSSH