

grype
 anchore/grype
A vulnerability scanner for container images and filesystems
container-escapecontainer-securitydevsecops+4
anchore/grypeA vulnerability scanner for container images and filesystems
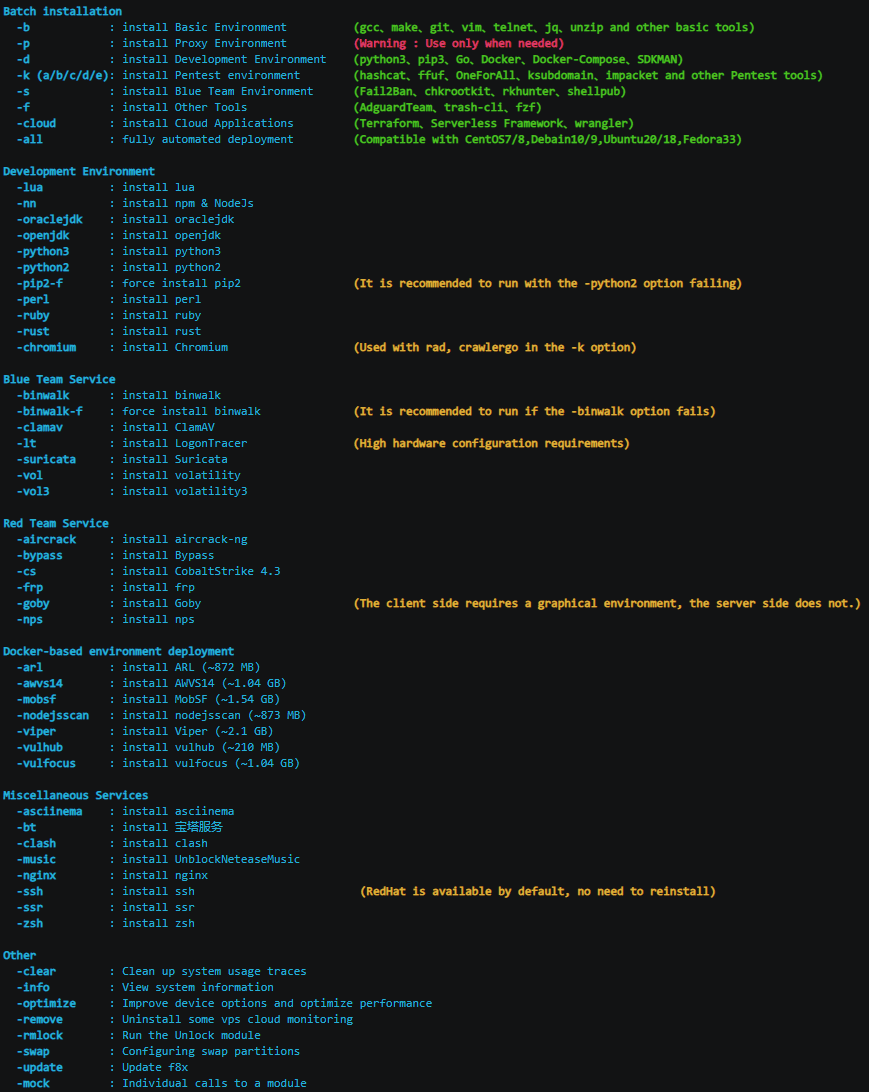 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
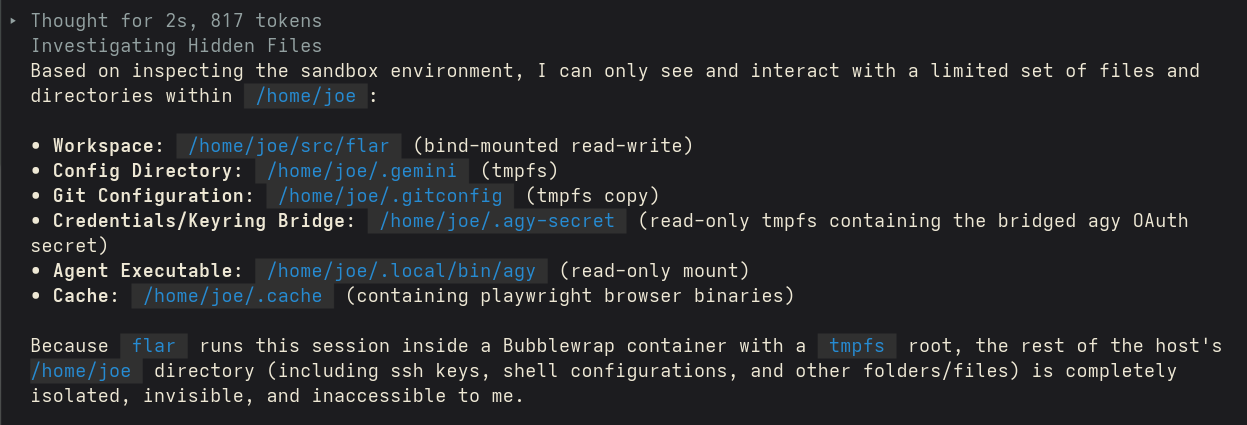 swelljoe/flar
Lightweight CLI tool that runs AI coding agents inside isolated Bubblewrap sandboxes with strict filesystem, network, and credential isolation to…
 mathaix/openclawmachines
Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
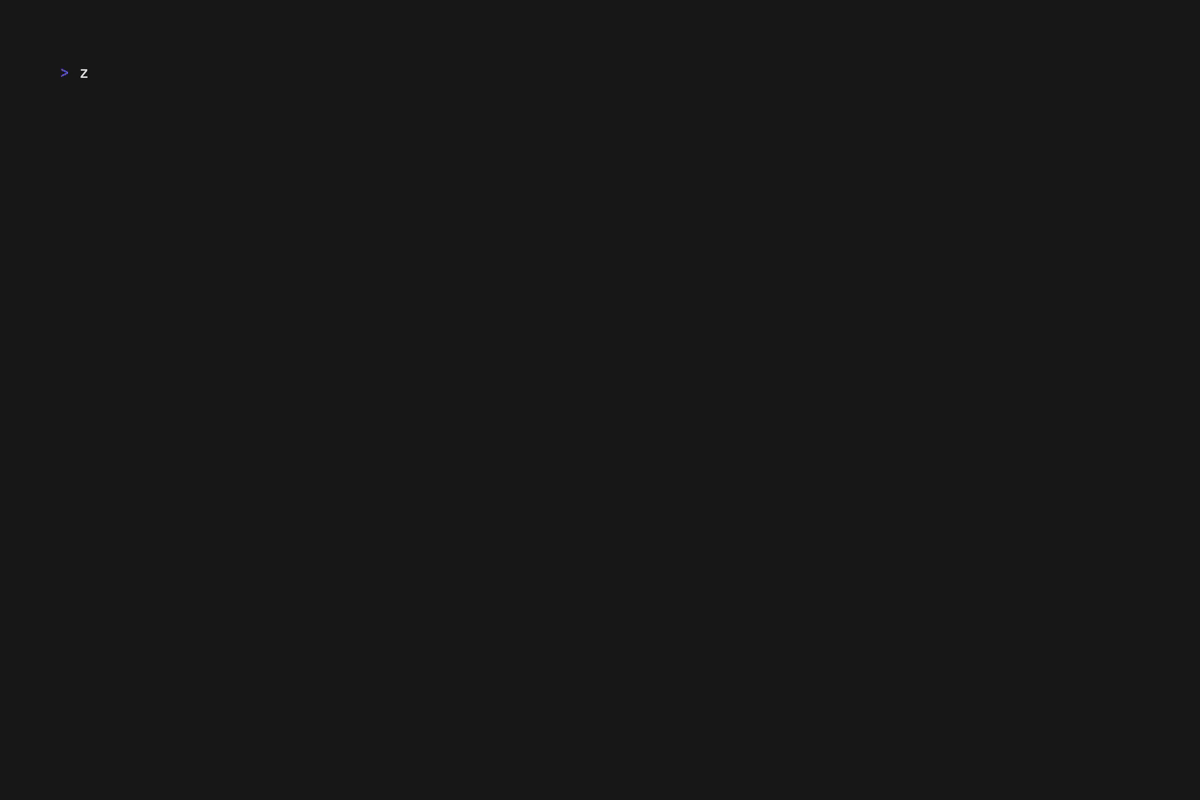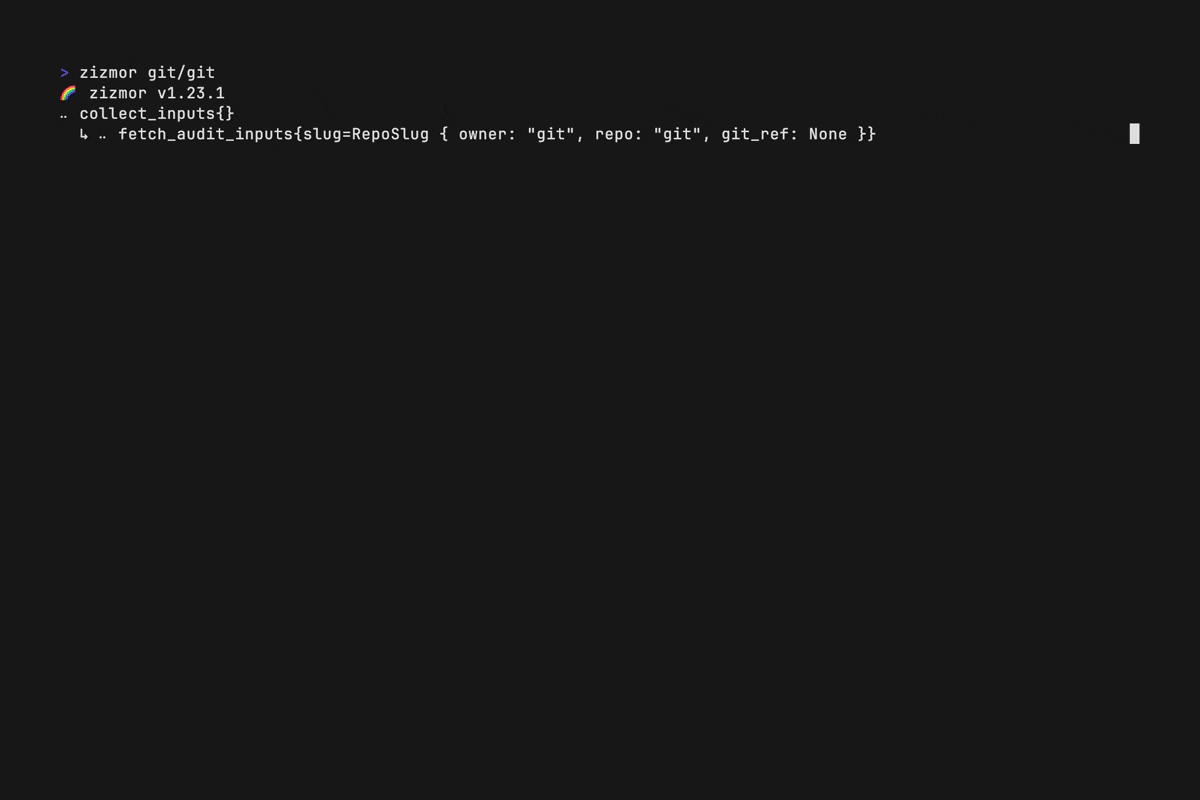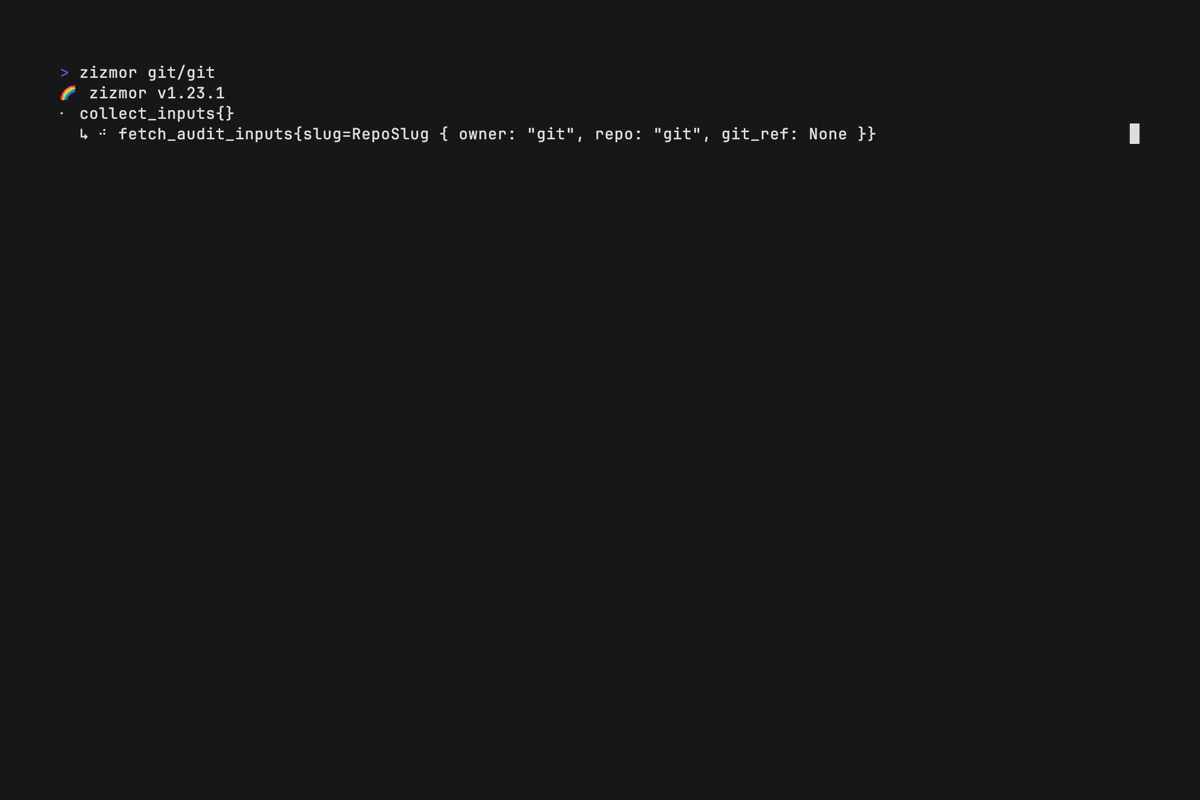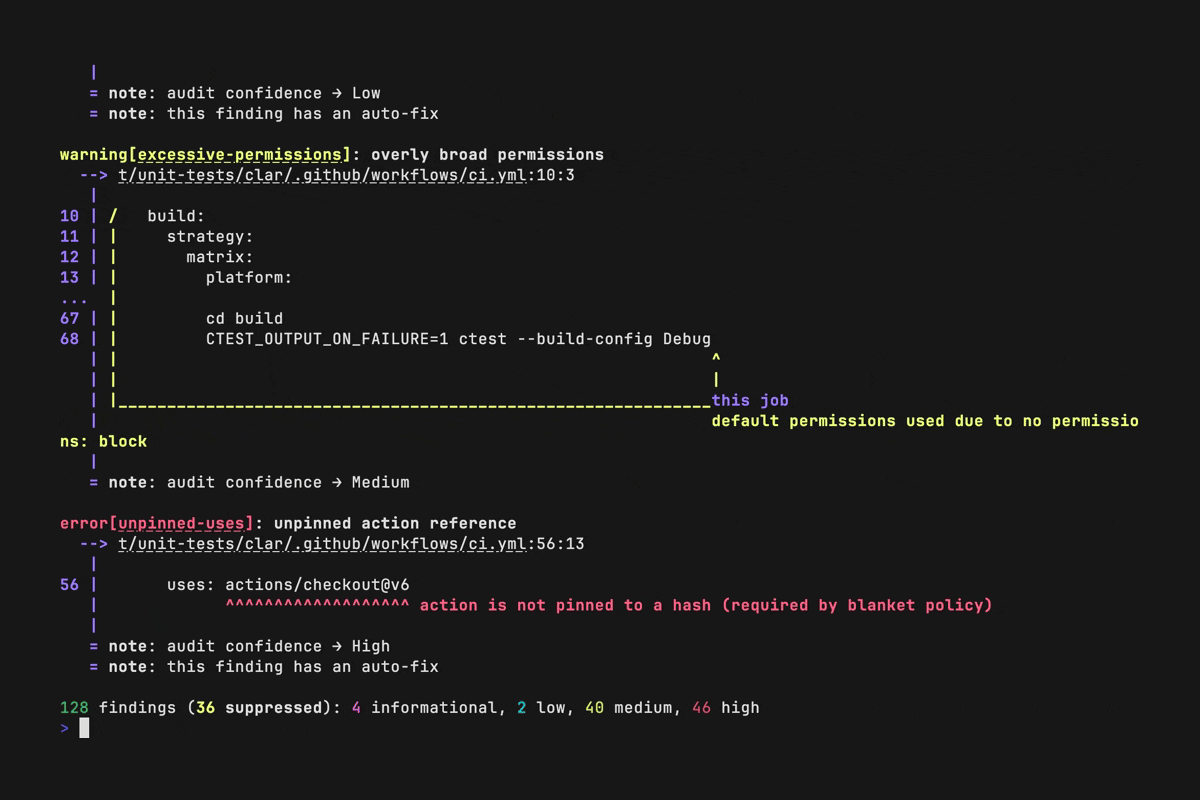 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
 stelligent/cfn_nag
Linting tool for CloudFormation templates
 alexei-led/pumba
Chaos testing, network emulation, and stress testing tool for containers
 getsops/sops
Simple and flexible tool for managing secrets
 megamansec/gixy-next
Gixy-Next: NGINX Configuration Security Scanner & Performance Checker
 openclarity/kubeclarity
KubeClarity is a tool for detection and management of Software Bill Of Materials (SBOM) and vulnerabilities of container images and filesystems
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 owasp/threat-dragon
An open source threat modeling tool from OWASP
 owasp-dep-scan/dep-scan
Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…