prowler
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…

CLI framework for deploying and managing serverless applications on AWS Lambda with YAML infrastructure, local development, and multi-language…

Autonomous agent framework with structured memory, safety hooks, and loop management. Built by the agent that runs on it.

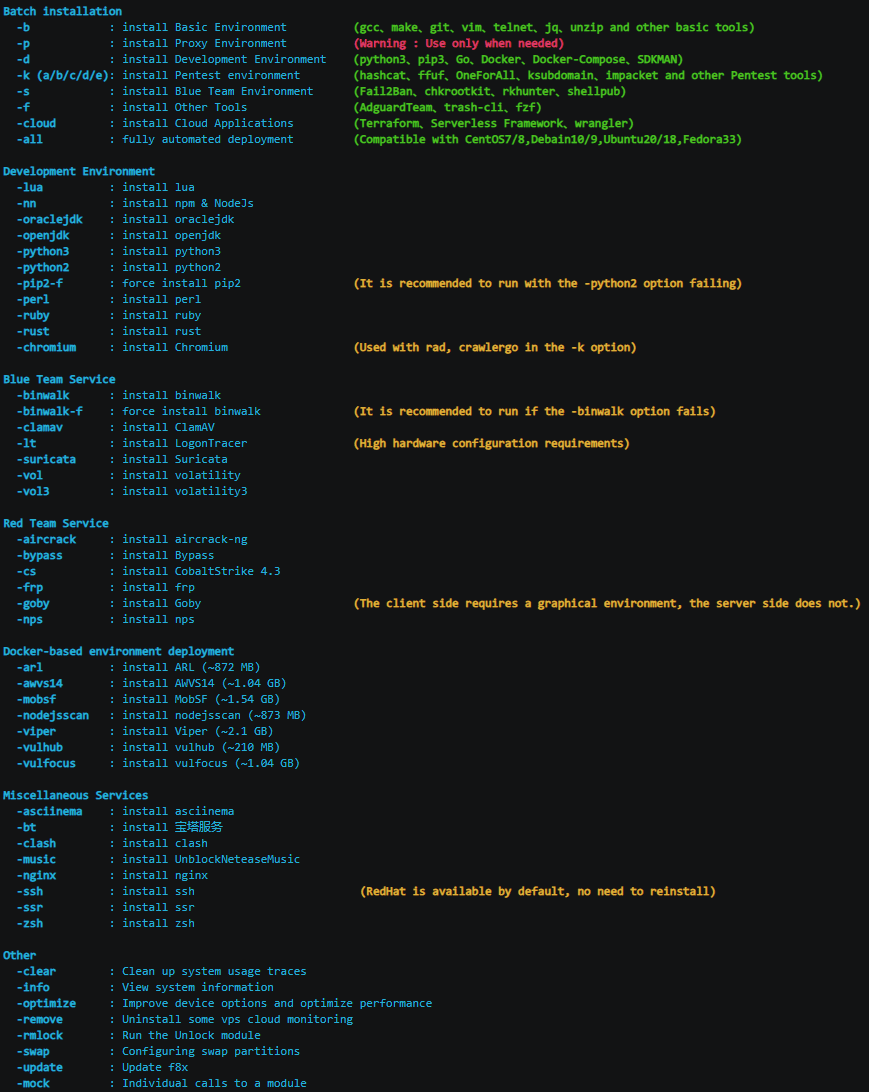
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool

Rules engine for cloud security, cost optimization, and governance, DSL in yaml for policies to query, filter, and take actions on resources

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Log4J Updater Bash Script to automate the framework update process on numerous machines and prevent the CVE-2021-44228

Complete Practical Study Plan to become a successful cybersecurity engineer based on roles like Pentest, AppSec, Cloud Security, DevSecOps and so…

Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…

Secure, private AI agent operating system with local encrypted storage, OAuth/SSO authentication, policy-based access control, and extensible…

Community-owned database of security advisories for Python packages on PyPI, providing structured vulnerability data in OSV format for integration…

Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives

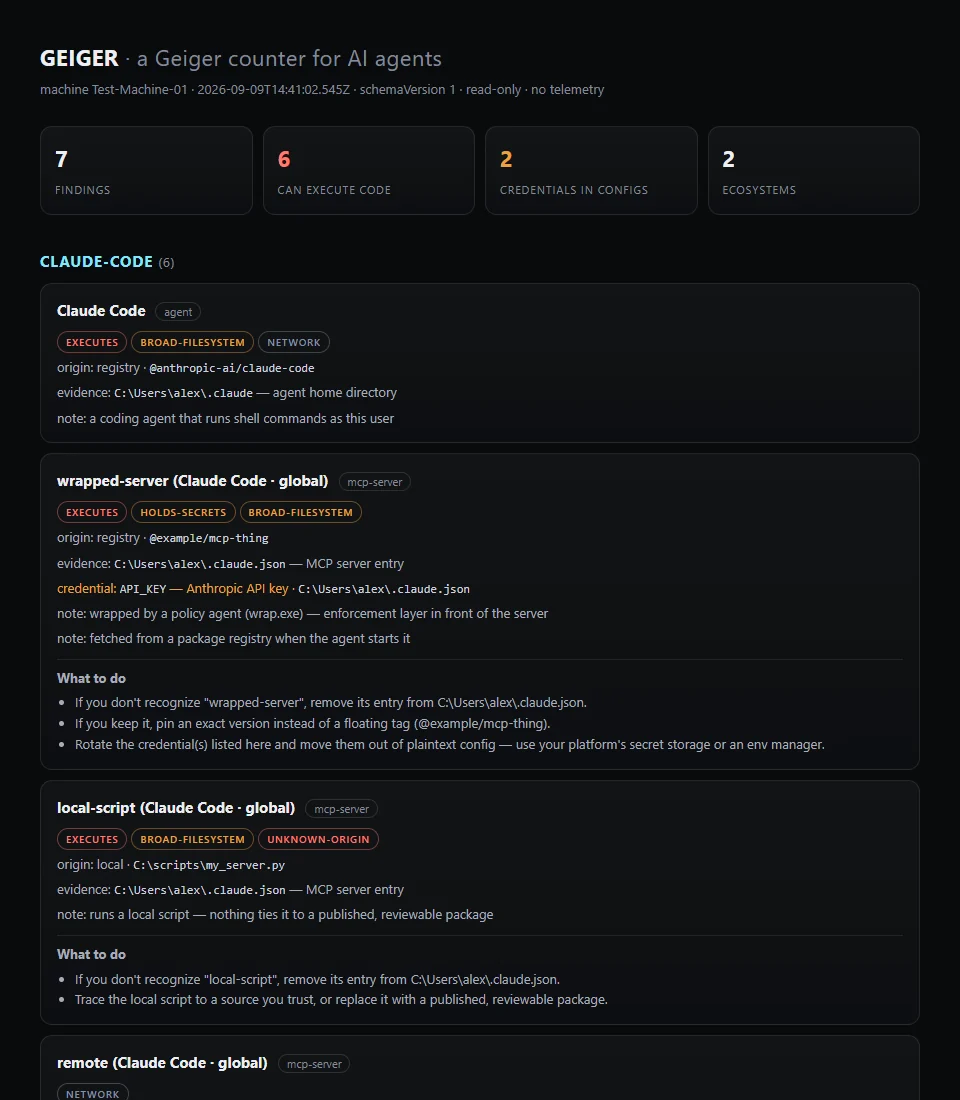
Read-only CLI that inventories AI agents, MCP servers, plugins, and extensions on a machine, reporting their capabilities and exposure with…

Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)

Certbot is EFF's tool to obtain certs from Let's Encrypt and (optionally) auto-enable HTTPS on your server. It can also act as a client for any…

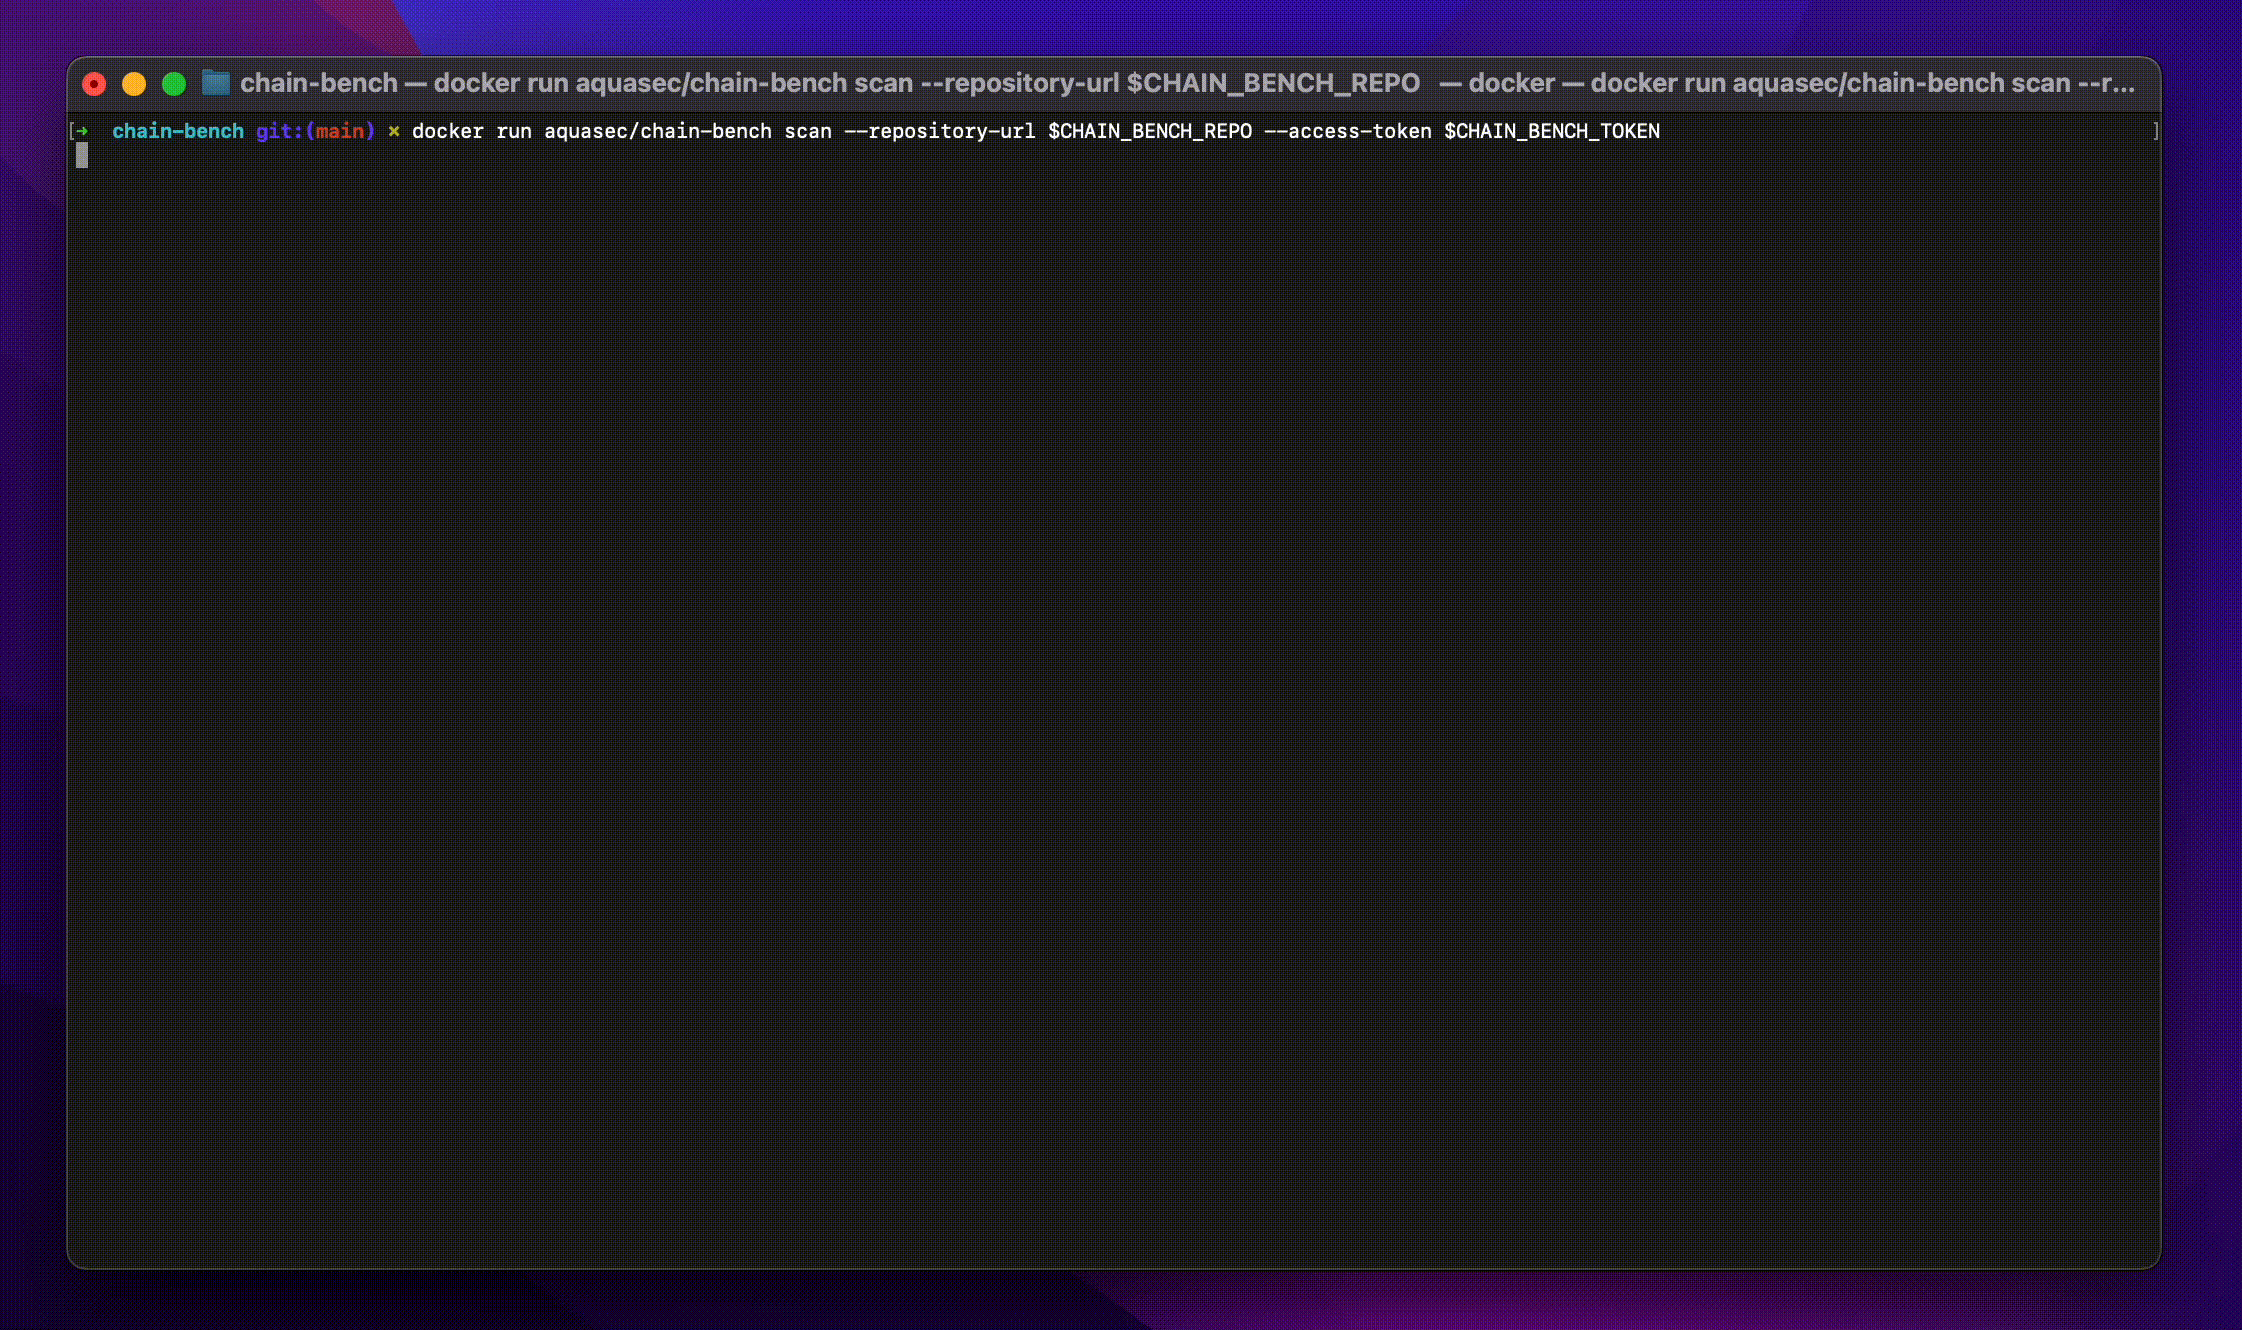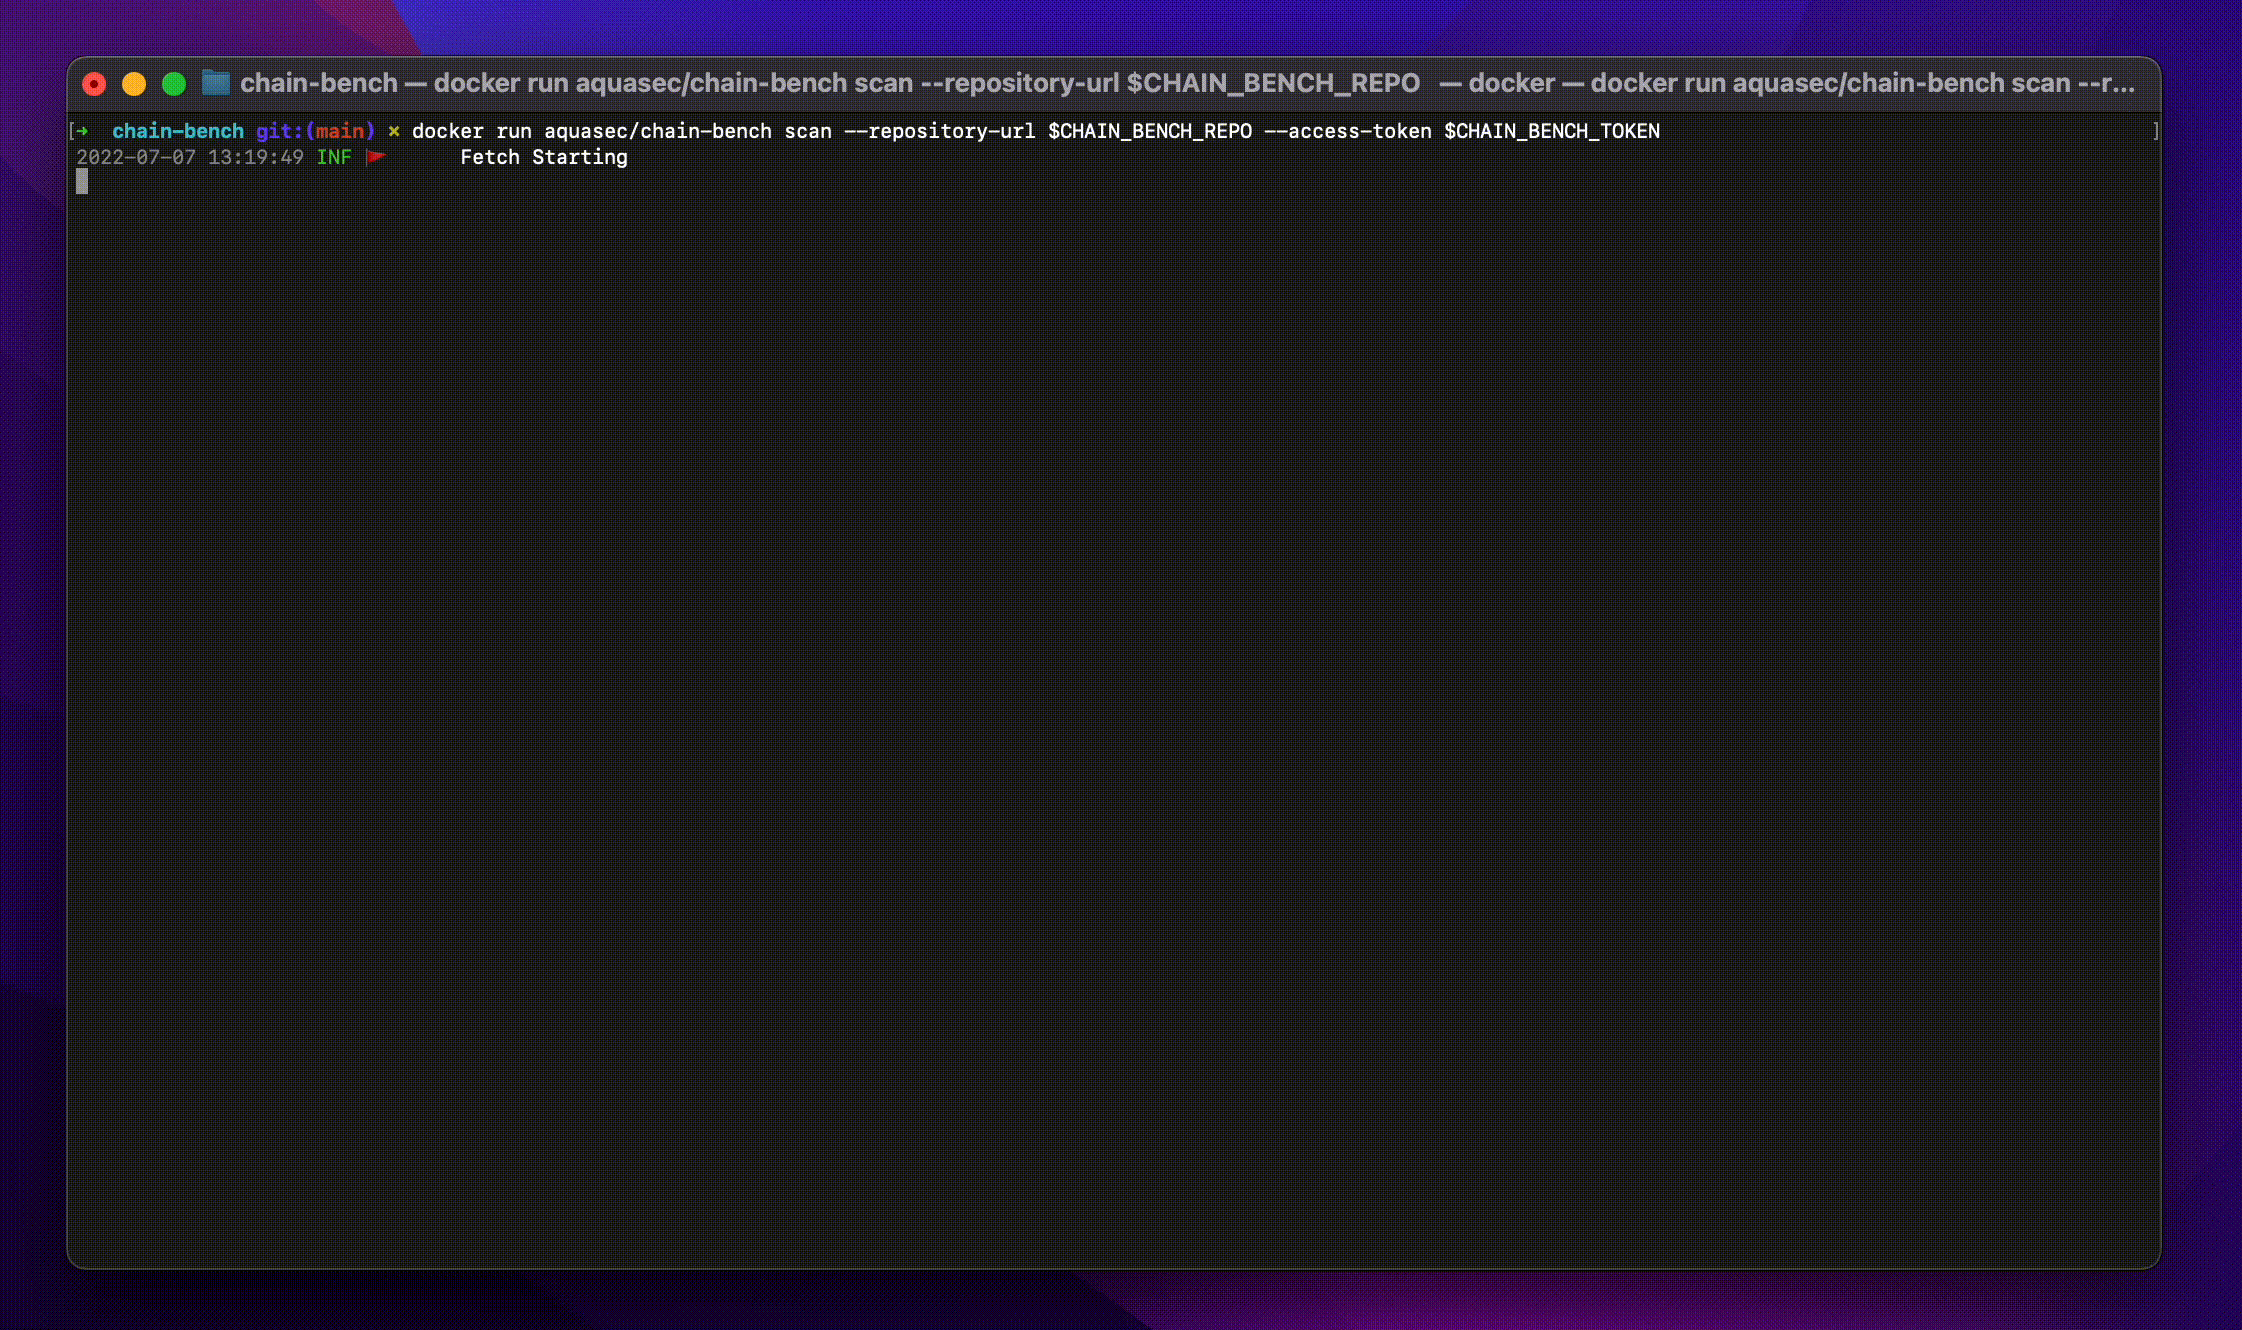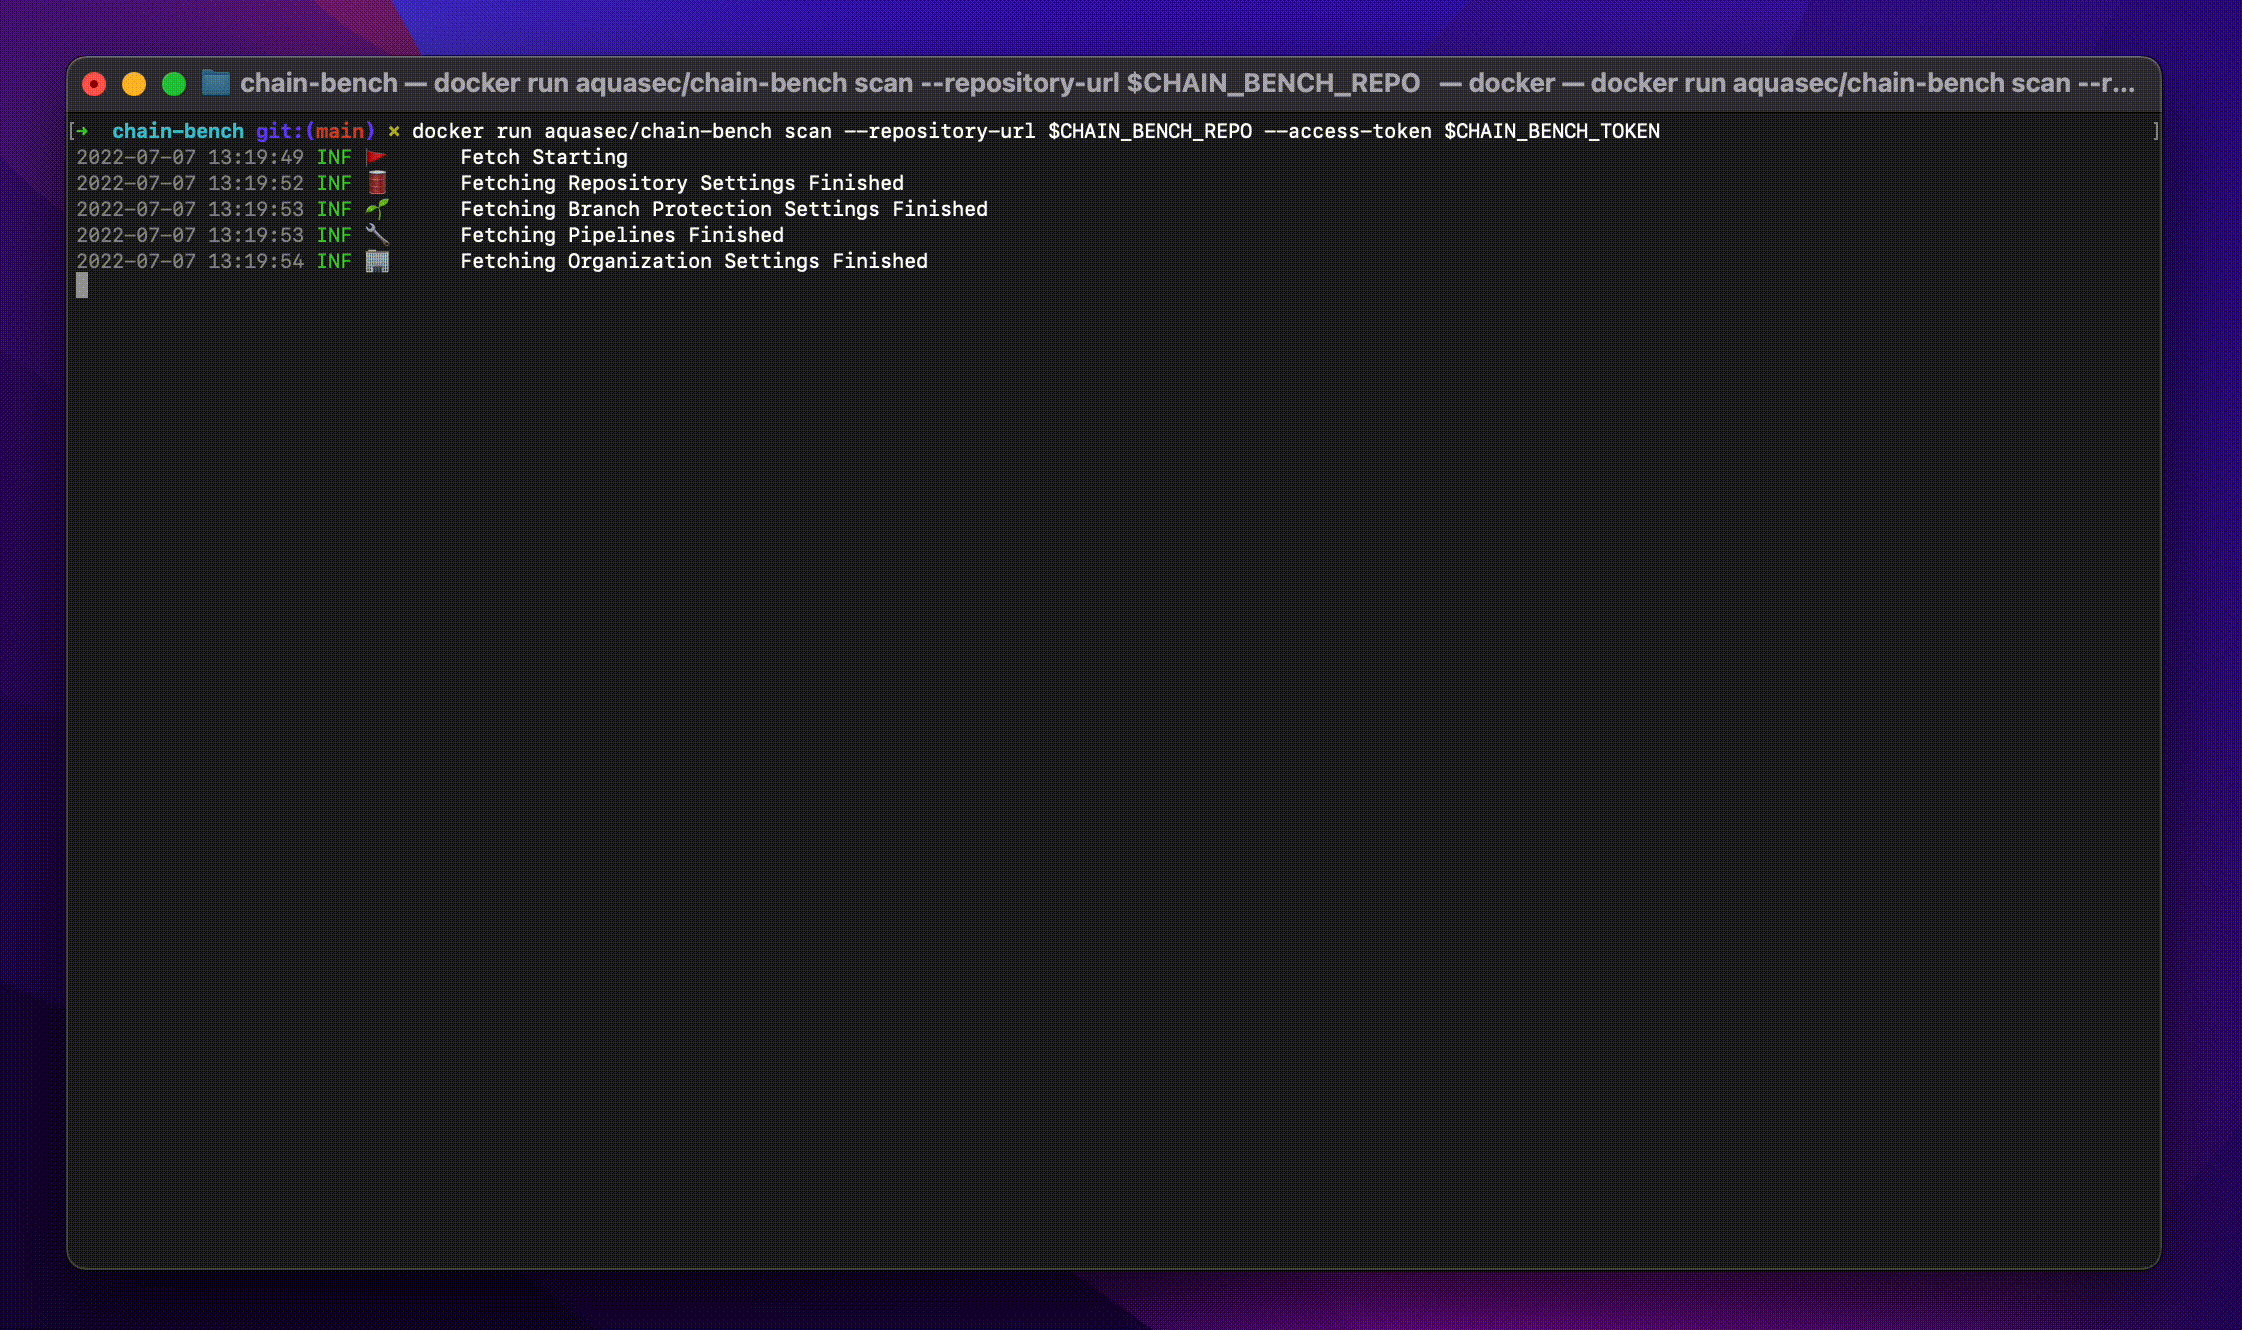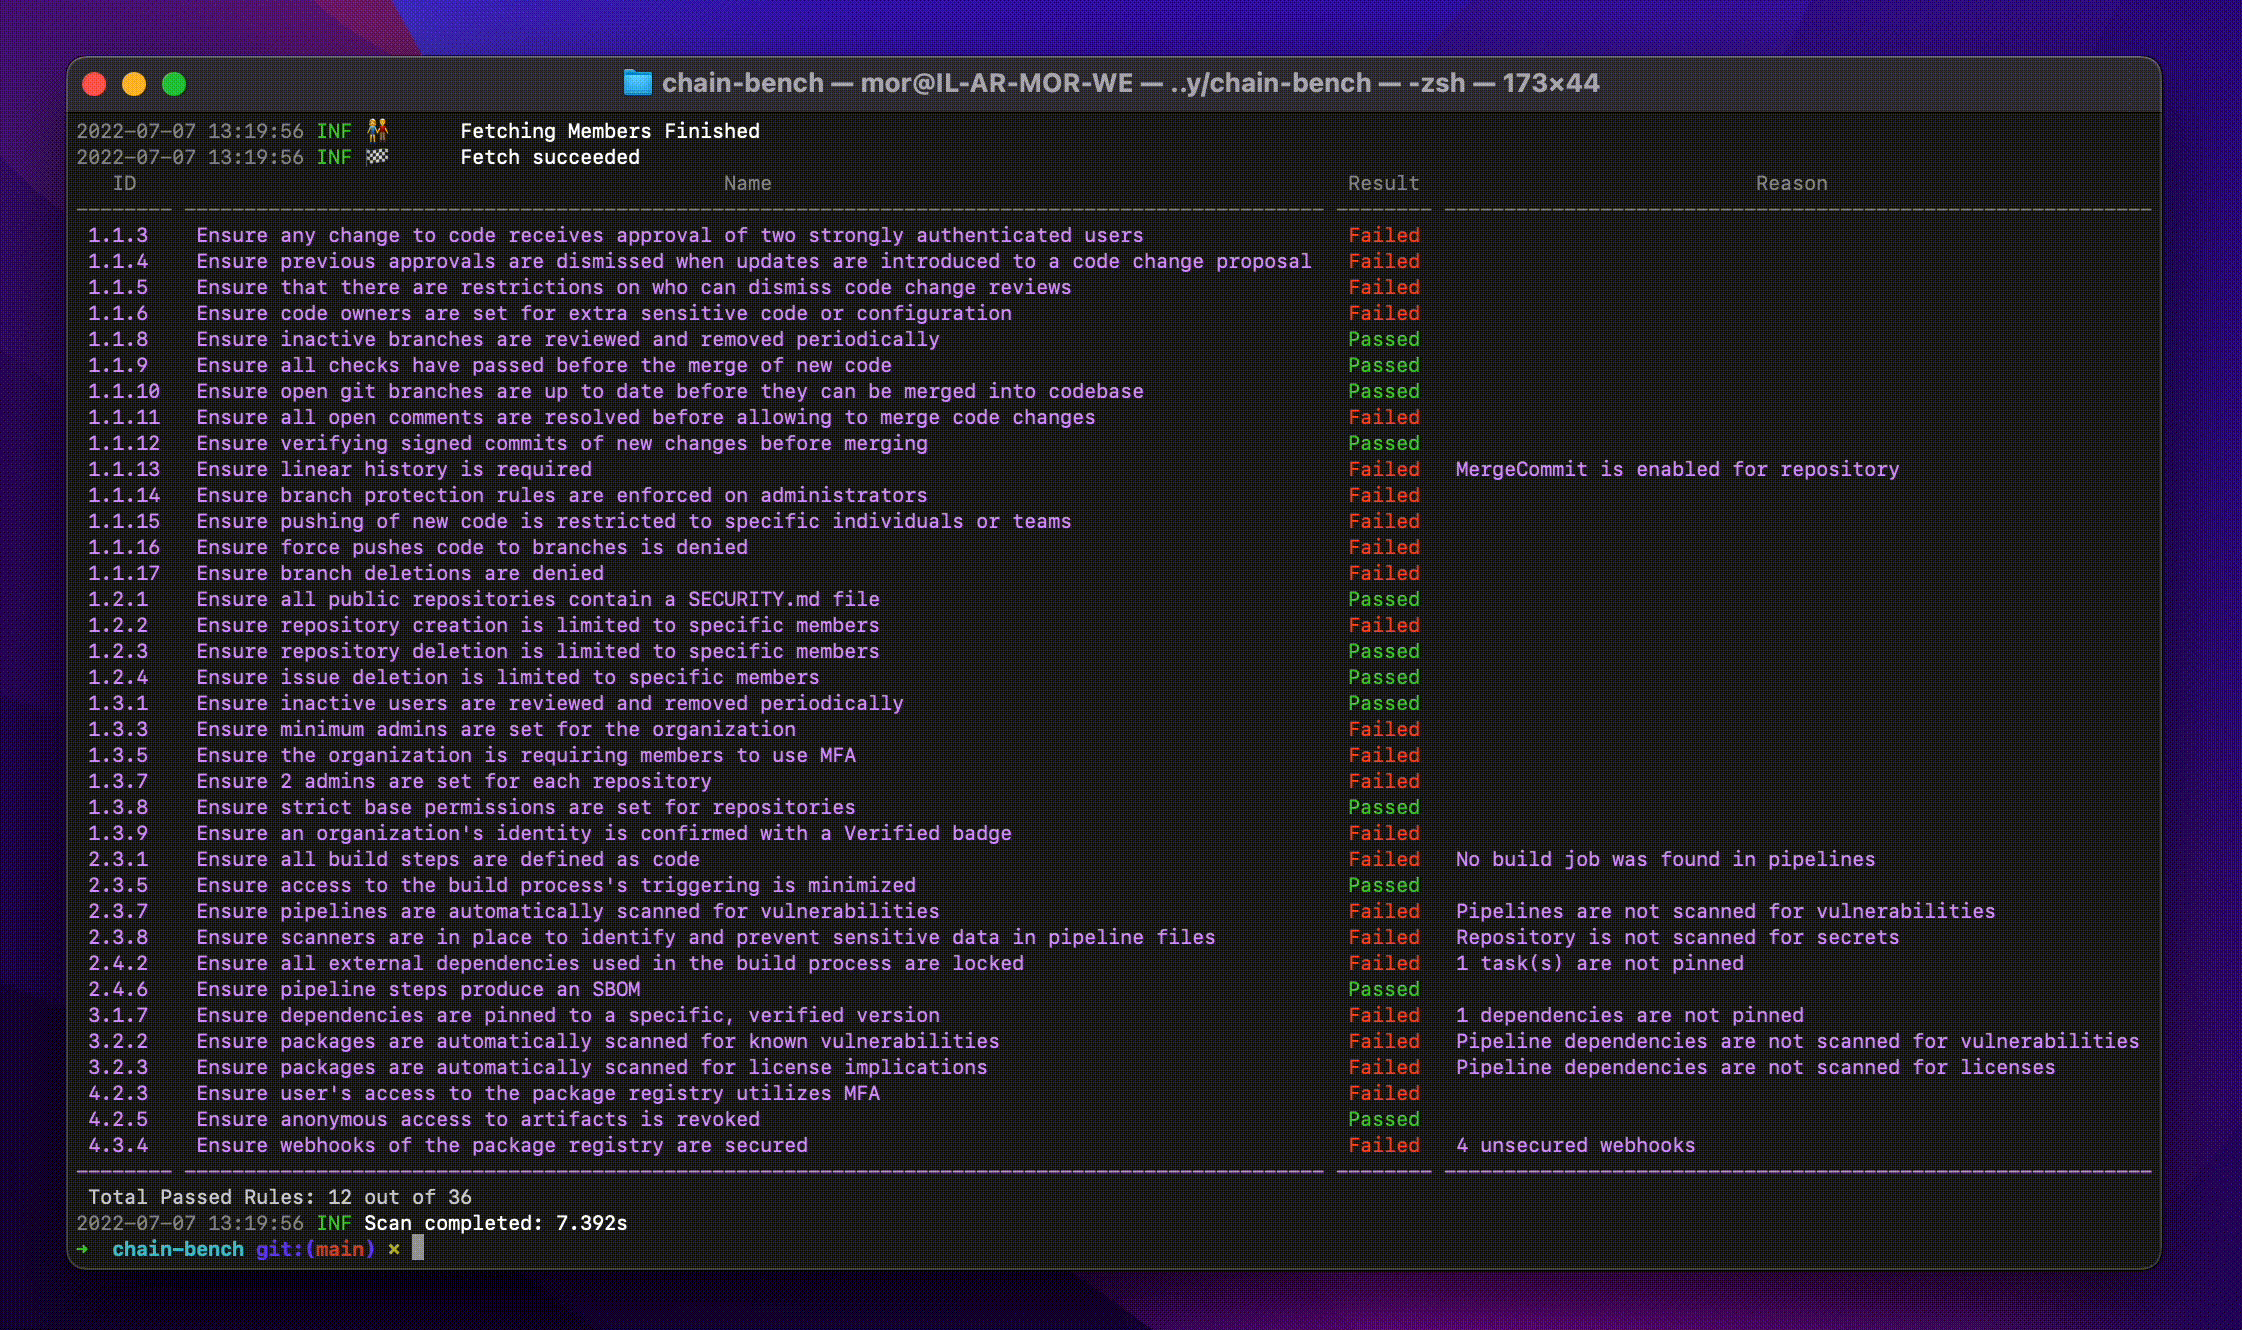
Audits software supply chain security compliance against the CIS benchmark, scanning SCM settings, branch protections, dependencies, and CI/CD…

Here is patch script to CVE-2026-31431 CopyFail