
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
81 results
OpenTAXII preview

OpenTAXII

GitHubeclecticiq/opentaxii

TAXII server implementation in Python from EclecticIQ
defensive-toolsioc-managementthreat-feeds-aggregators+1
2169 months ago
honeyLambda preview

honeyLambda

GitHub0x4d31/honeylambda

honeyλ - a simple, serverless application designed to create and monitor fake HTTP endpoints (i.e. URL honeytokens) automatically, on top of AWS…

cloud-securitydefensive-toolsincident-response+2
5257 years ago
NoArgs preview

NoArgs

GitHuboh-az/noargs

Windows API hooking tool that dynamically spoofs and conceals process arguments via Detours library and PEB manipulation, enabling stealthy process…

api-securitydefensive-toolsred-teaming
1512 years ago
adversary_emulation_library preview

adversary_emulation_library

GitHubcenter-for-threat-informed-defense/adversary_emulation_library

An open library of adversary emulation plans designed to empower organizations to test their defenses based on real-world TTPs.
curated-resourcesdata-exfiltrationdefensive-tools+5
2.2k1 year ago
packetsifterTool preview

packetsifterTool

GitHubpacketsifter/packetsiftertool

PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…

defensive-toolsdigital-forensicsforensics+5
935 years ago
cloudrasp-log4j2 preview

cloudrasp-log4j2

GitHubboundaryx/cloudrasp-log4j2

一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.
defensive-toolsexploit-frameworksvulnerability-analysis+1
1244 years ago
CVE-2022-30190 preview

CVE-2022-30190

GitHubcyberdashy/cve-2022-30190

PowerShell script to mitigate CVE-2022-30190 by updating a registry DWORD key, designed for deployment via RMM tools like ConnectWise Automate.
configuration-auditingdefensive-toolsmisconfiguration+2
4 years ago
CVE-2021-34527-PrintNightmare-Workaround preview

CVE-2021-34527-PrintNightmare-Workaround

GitHubgeekbrett/cve-2021-34527-printnightmare-workaround

This simple PowerShell script is in response to the "PrintNightmare" vulnerability. This was designed to give a end user the ability to stop and…
defensive-toolsexploitationgeneral-purpose-utilities+2
5 years ago
BlackLotus preview

BlackLotus

GitHubldpreload/blacklotus

BlackLotus UEFI Windows Bootkit

command-and-controldefensive-toolsexploitation+8
2.2k2 years ago
Python-Honeypot preview

Python-Honeypot

GitHubowasp/python-honeypot

OWASP Honeypot, Automated Deception Framework.
api-securitycontainer-securitydefensive-tools+4
4842 years ago
grove preview

grove

GitHubhashicorp-forge/grove

A Software as a Service (SaaS) log collection framework.
api-securitycloud-securitydefensive-tools+3
18719 days ago
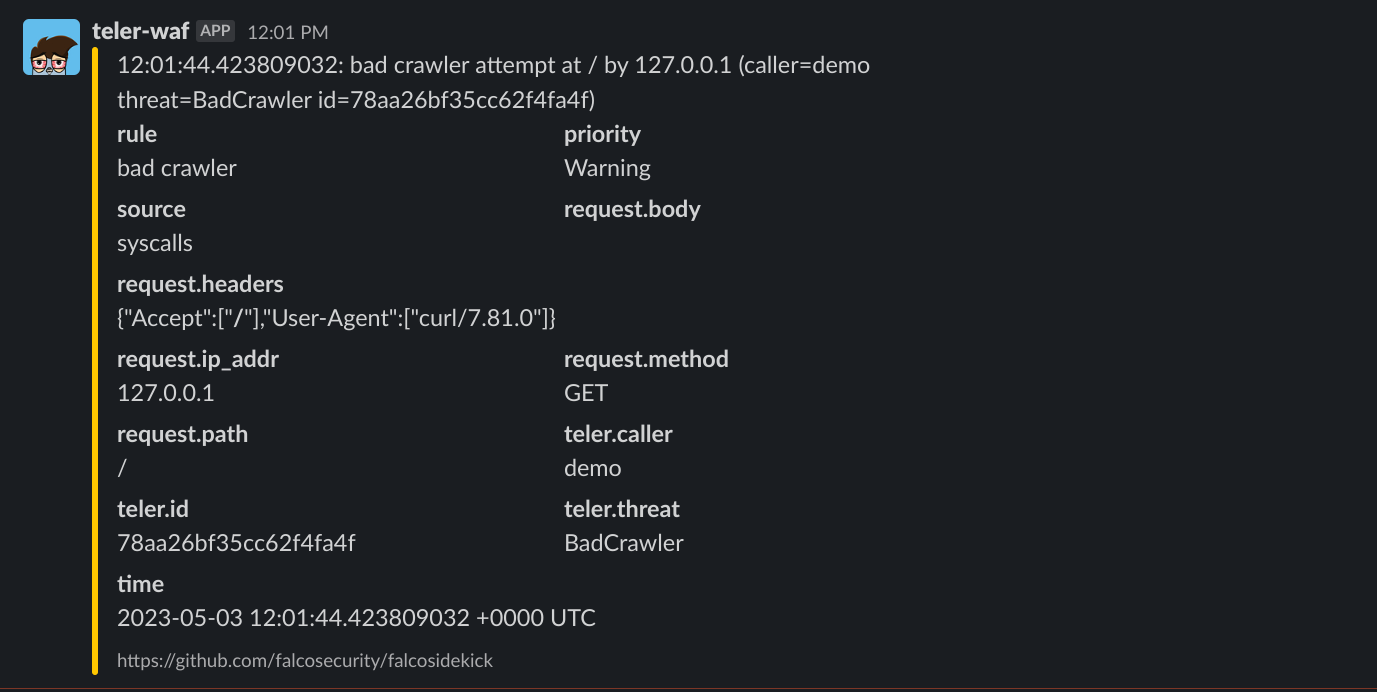
teler-waf preview

teler-waf

GitHubteler-sh/teler-waf

teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…
api-securitydefensive-toolsids-ips-evasion+5
4081 year ago
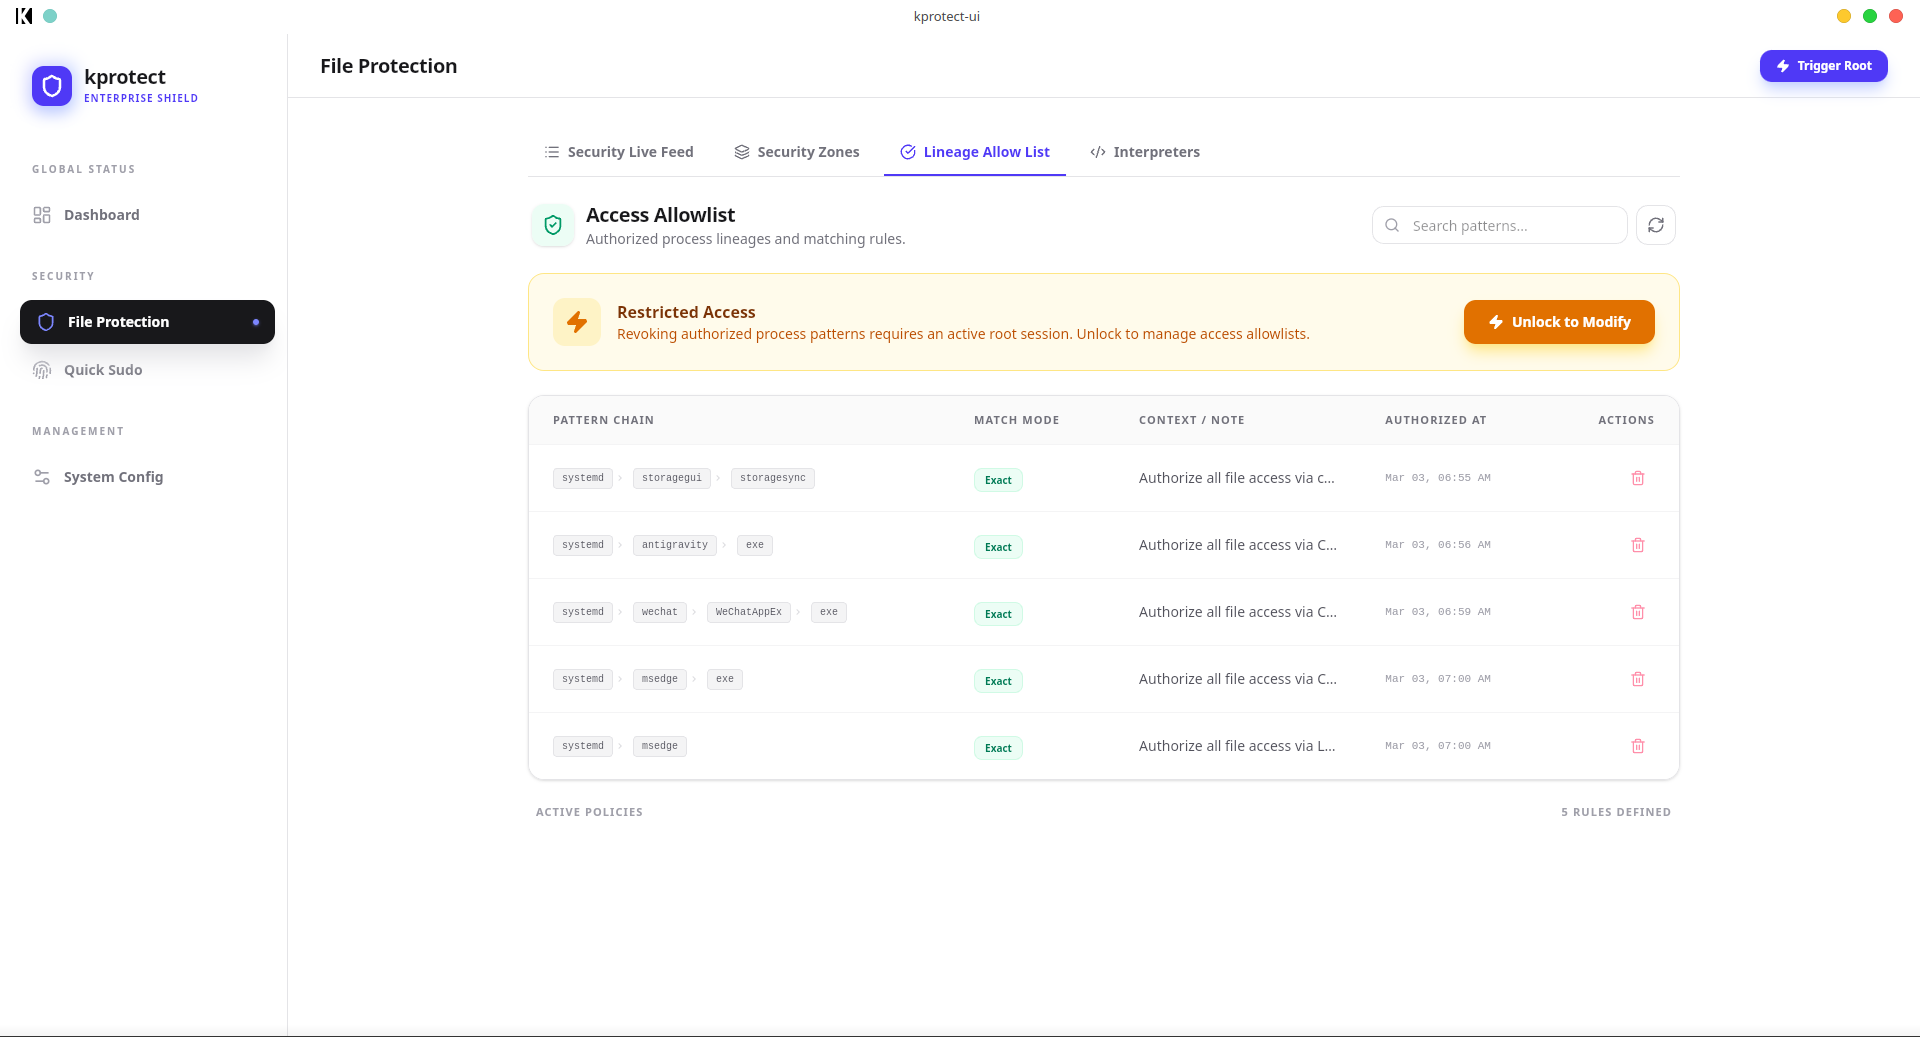
kprotect preview

kprotect

GitHubkhoinp1012/kprotect

Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…

authentication-authorizationcloud-securitydefensive-tools+4
367 months ago
CanoP preview

CanoP

GitHubopenbreach/canop

Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
ai-securitycode-analysisdefensive-tools+7
422 days ago
Disable-IPv6-CVE-2024-38063-Fix preview

Disable-IPv6-CVE-2024-38063-Fix

GitHubalmogopp/disable-ipv6-cve-2024-38063-fix

A PowerShell script to temporarily mitigate the CVE-2024-38063 vulnerability by disabling IPv6 on Windows systems. This workaround modifies the…
defensive-toolsgeneral-purpose-utilitiesmisconfiguration+2
2 years ago
GoDefender preview
Archived

GoDefender

GitHubkiexitdispatcher/godefender

Anti Virtulization, Anti Debugging, AntiVM, Anti Virtual Machine, Anti Debug, Anti Sandboxie, Anti Sandbox, VM Detect package. Windows ONLY.

anti-botbinary-analysisdefensive-tools+3
8569 months ago
sec-gemini preview

sec-gemini

GitHubgoogle/sec-gemini

Sec-Gemini is a cutting-edge AI model designed to enhance cybersecurity capabilities and empower defenders in the ongoing battle against cyber…
ai-securitydefensive-toolsmachine-learning
66118 days ago
SharpEDRChecker preview

SharpEDRChecker

GitHubpwndexter/sharpedrchecker

C# tool that enumerates running processes, loaded DLLs, installed services, and drivers to detect the presence of AV, EDR, and logging products,…

defensive-toolsinformation-gatheringpenetration-testing+2
7597 months ago
Previous12345Next