

Dejavu
 bhdresh/dejavu
DejaVU - Open Source Deception Framework
cloud-securitydefensive-toolsids-ips-evasion+7
bhdresh/dejavuDejaVU - Open Source Deception Framework
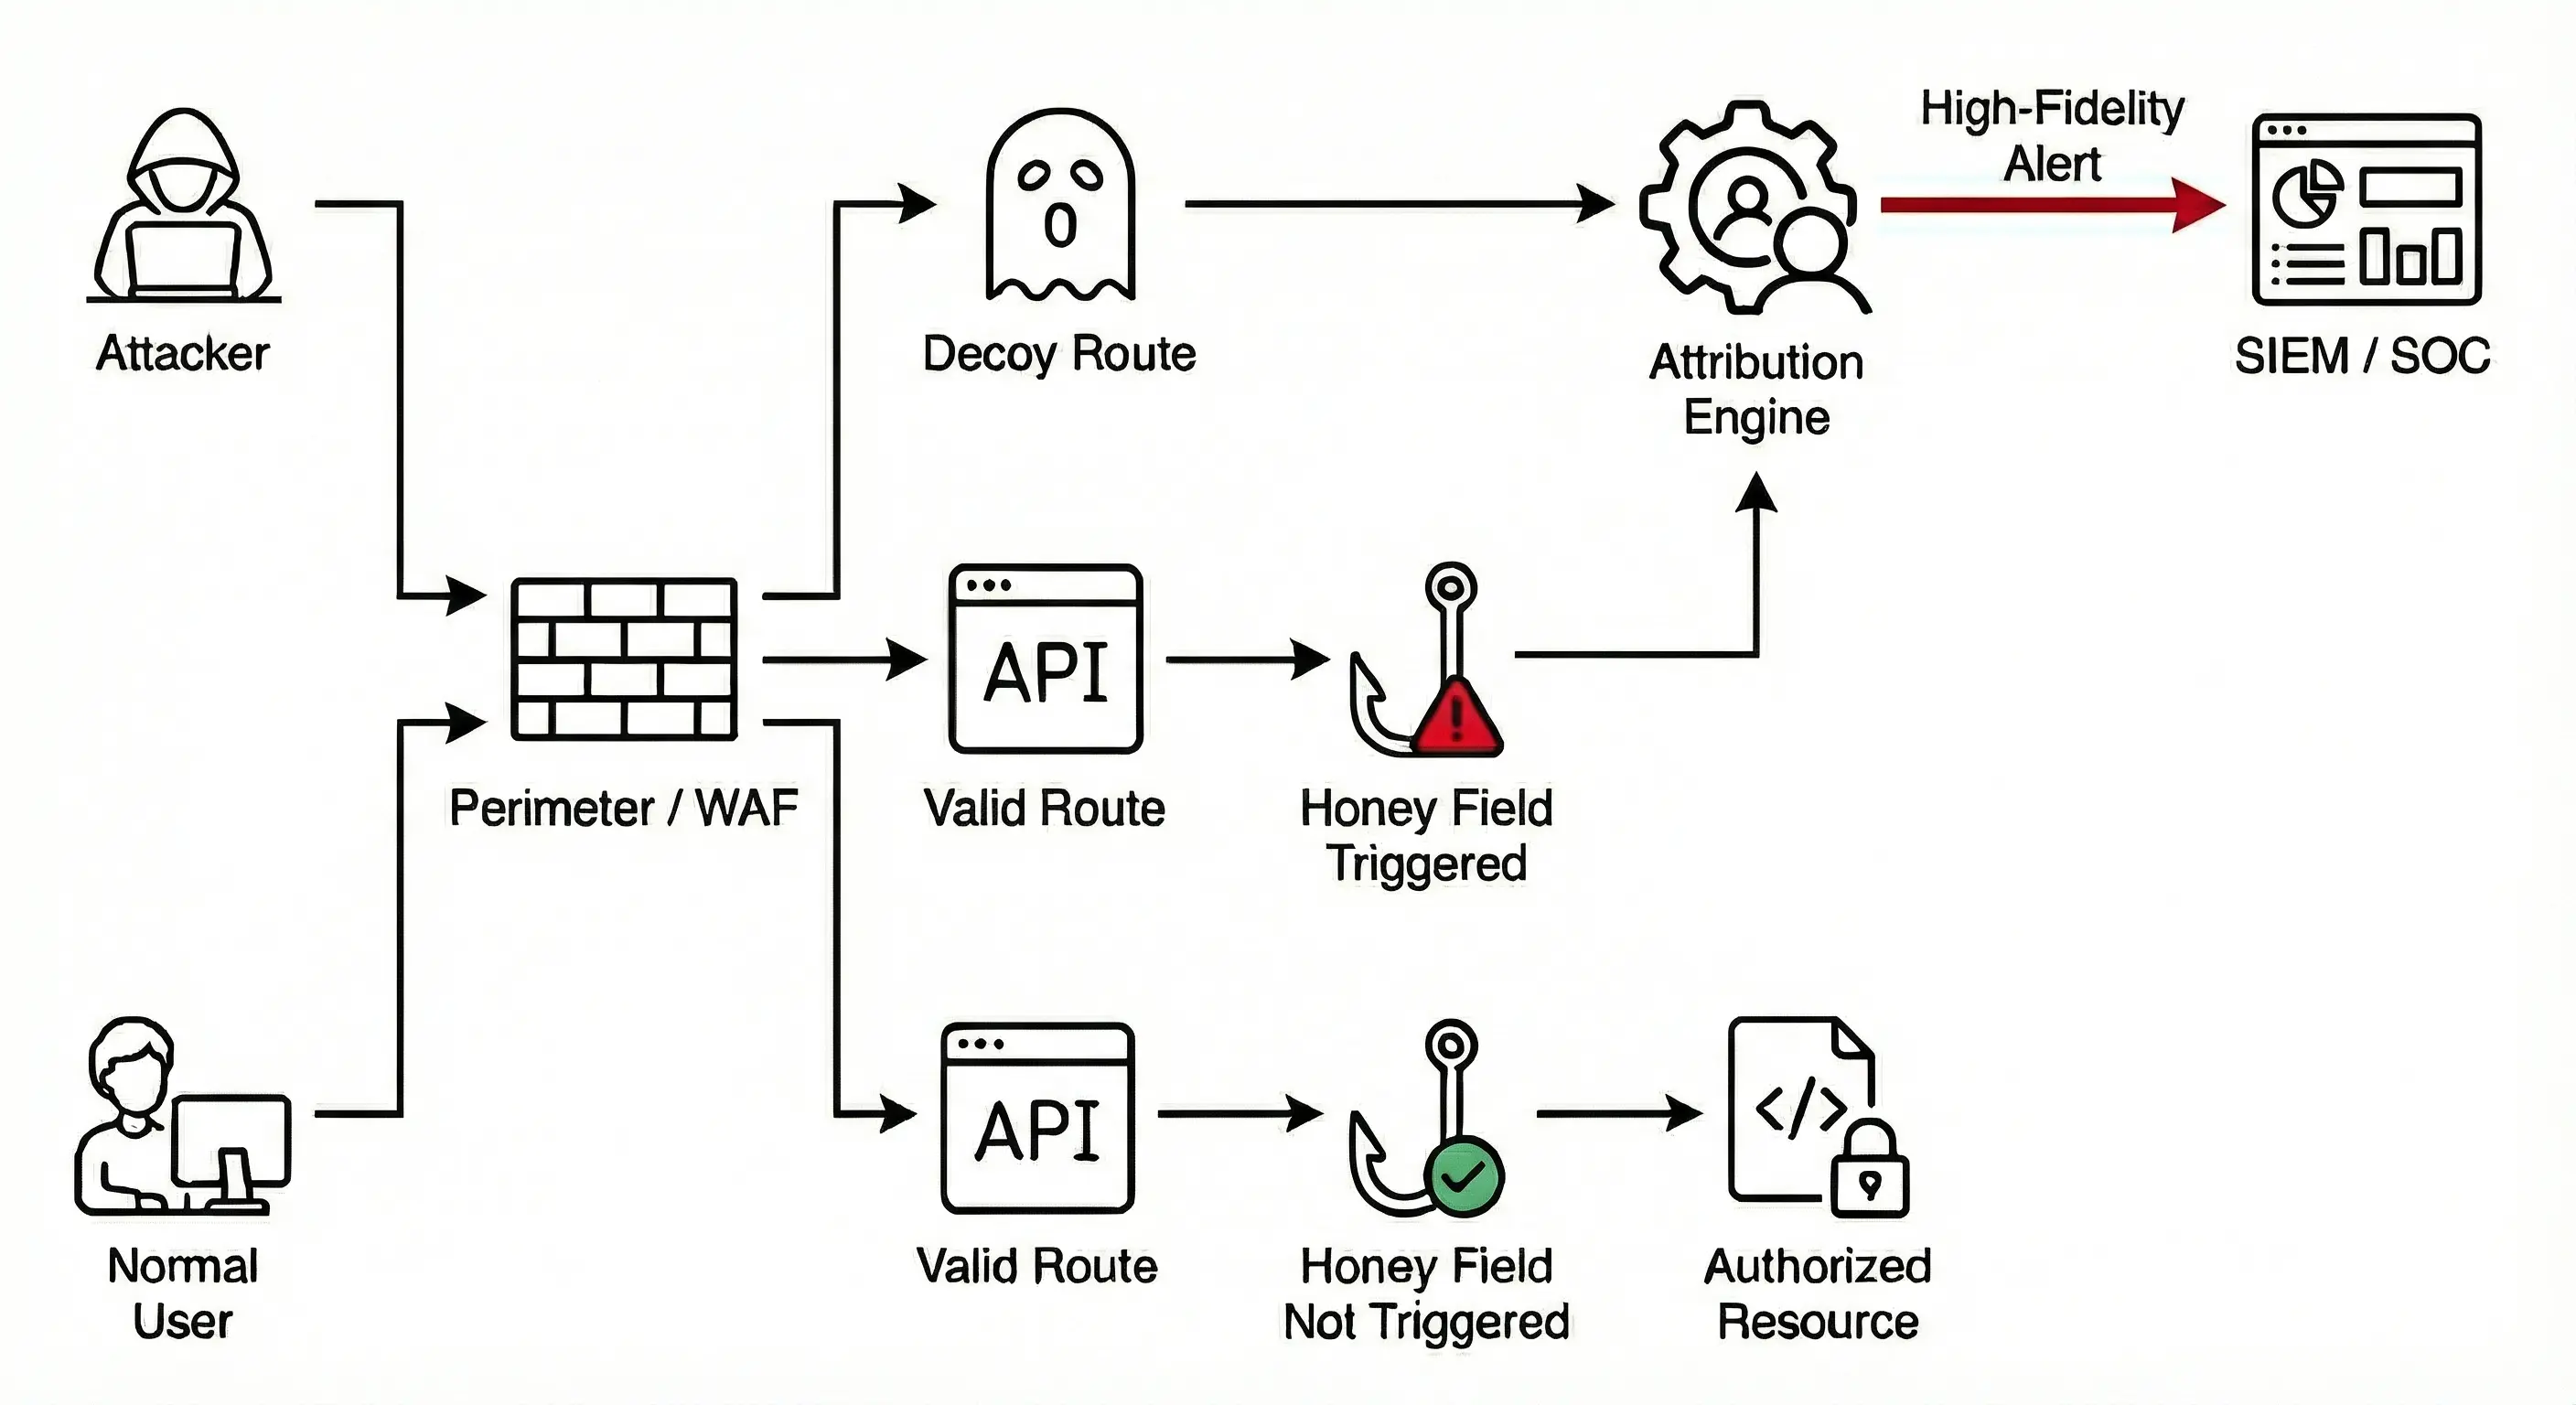 trappsec-dev/trappsec
Open-source framework for embedding realistic decoy routes and honey fields into APIs to detect attackers probing business logic, converting…
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
 patrowl/patrowlhears
PatrowlHears - Vulnerability Intelligence Center / Exploits
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
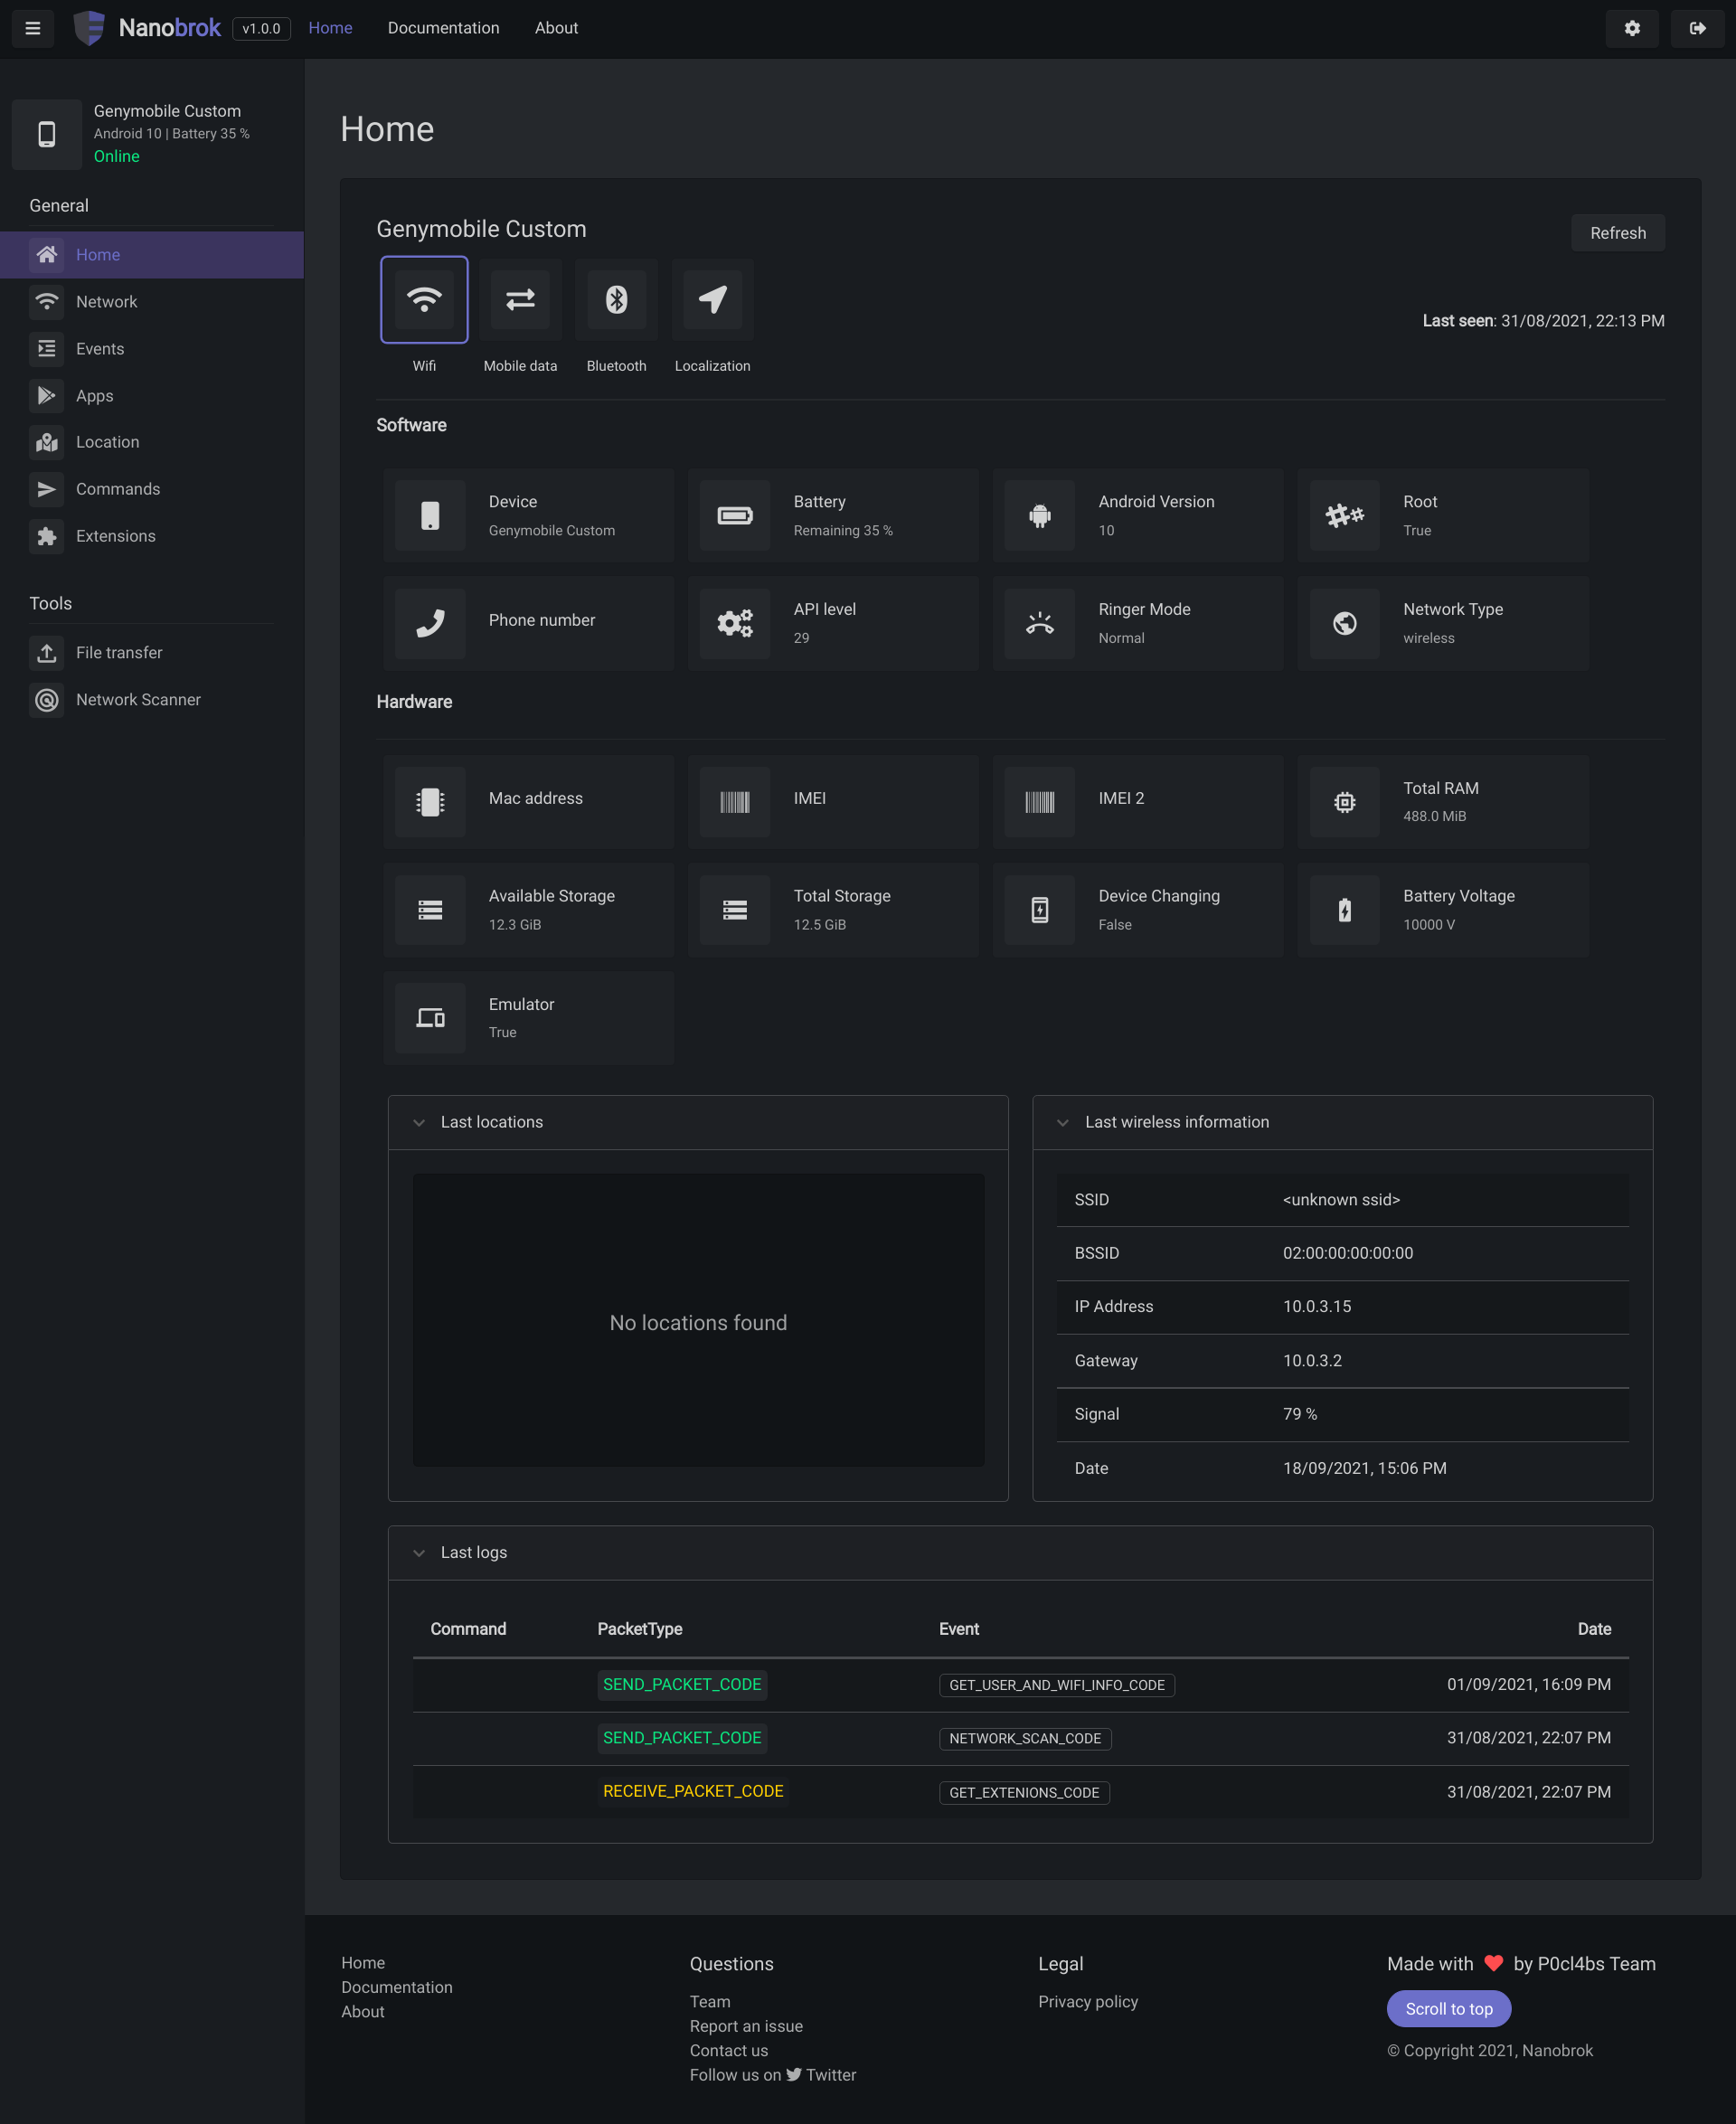 p0cl4bs/nanobrok
Web Service write in Python for control and protect your android device remotely.
 viralmaniar/ddwpasterecon
DDWPasteRecon tool will help you identify code leak, sensitive files, plaintext passwords, password hashes. It also allow member of SOC & Blue Team…
 princeaikinsbaidoo/cve-2022-24637
Defensive notes on CVE-2022-24637 in Open Web Analytics before 1.7.4, covering unauthenticated information disclosure, privilege escalation impact,…
 nxploited/cve-2026-91097-cve-2026-91106
HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)
 taisa456/network-security-snort
Snort 3 IDS → IPS lab on Kali. Custom detection rules + iptables enforcement against ICMP recon, Nmap SYN scans, Hydra FTP brute force, and vsftpd…
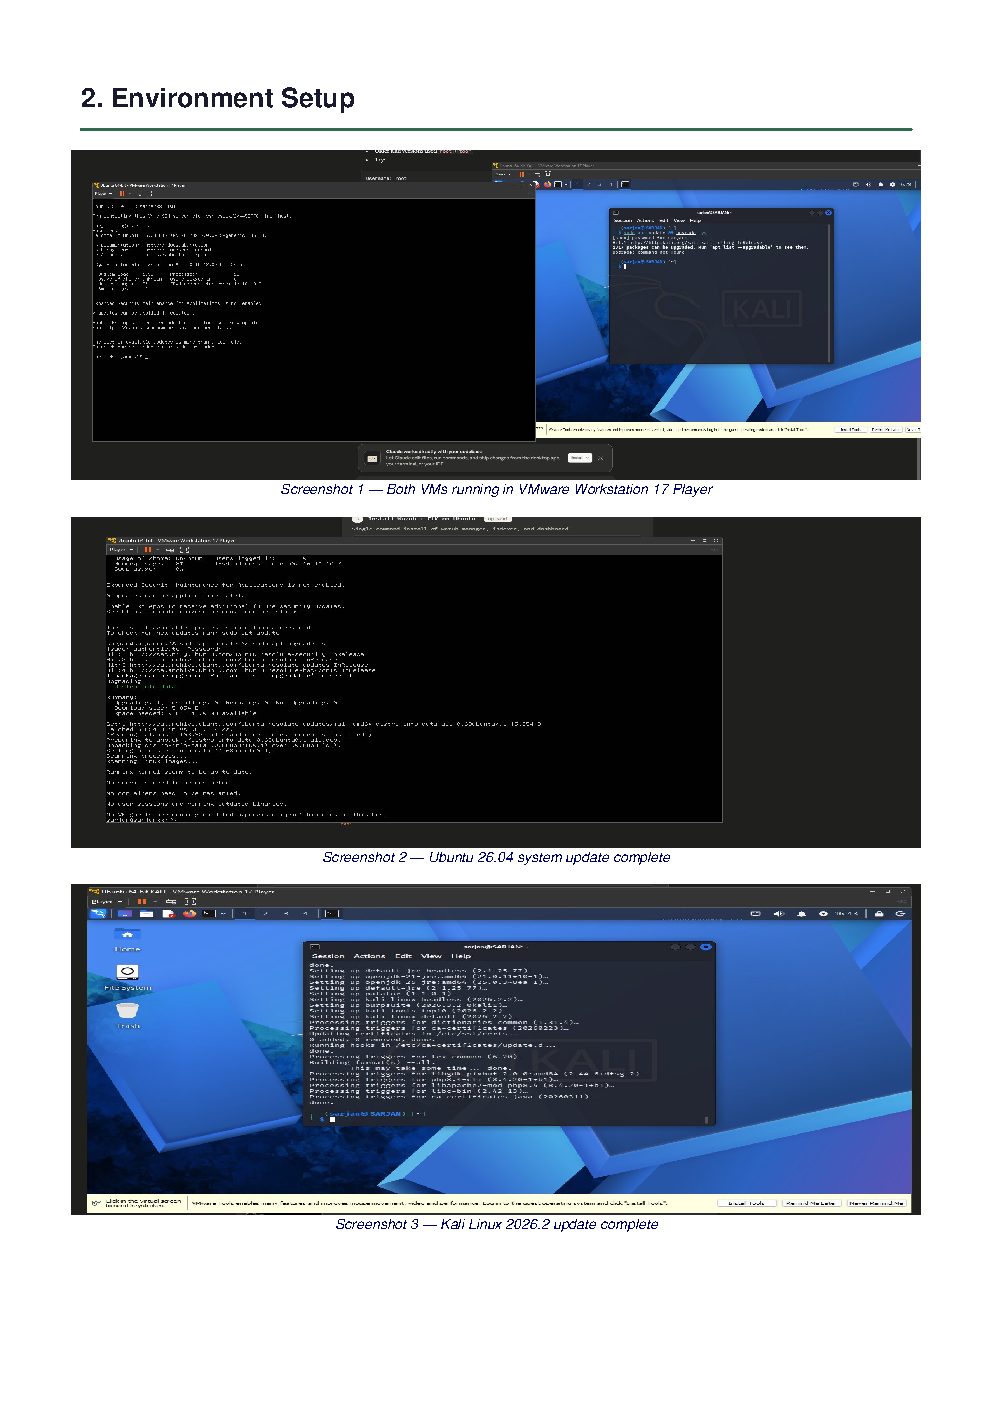 sarjanpatel22/siem-threat-detection-lab
Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…
 mcastens/alycon-threat-landscape
Training-free anomaly detection framework using Shannon Entropy, Fisher Information, and Wasserstein Distance to map system states into geometrically…
 specterops/bloodhound
Six Degrees of Domain Admin
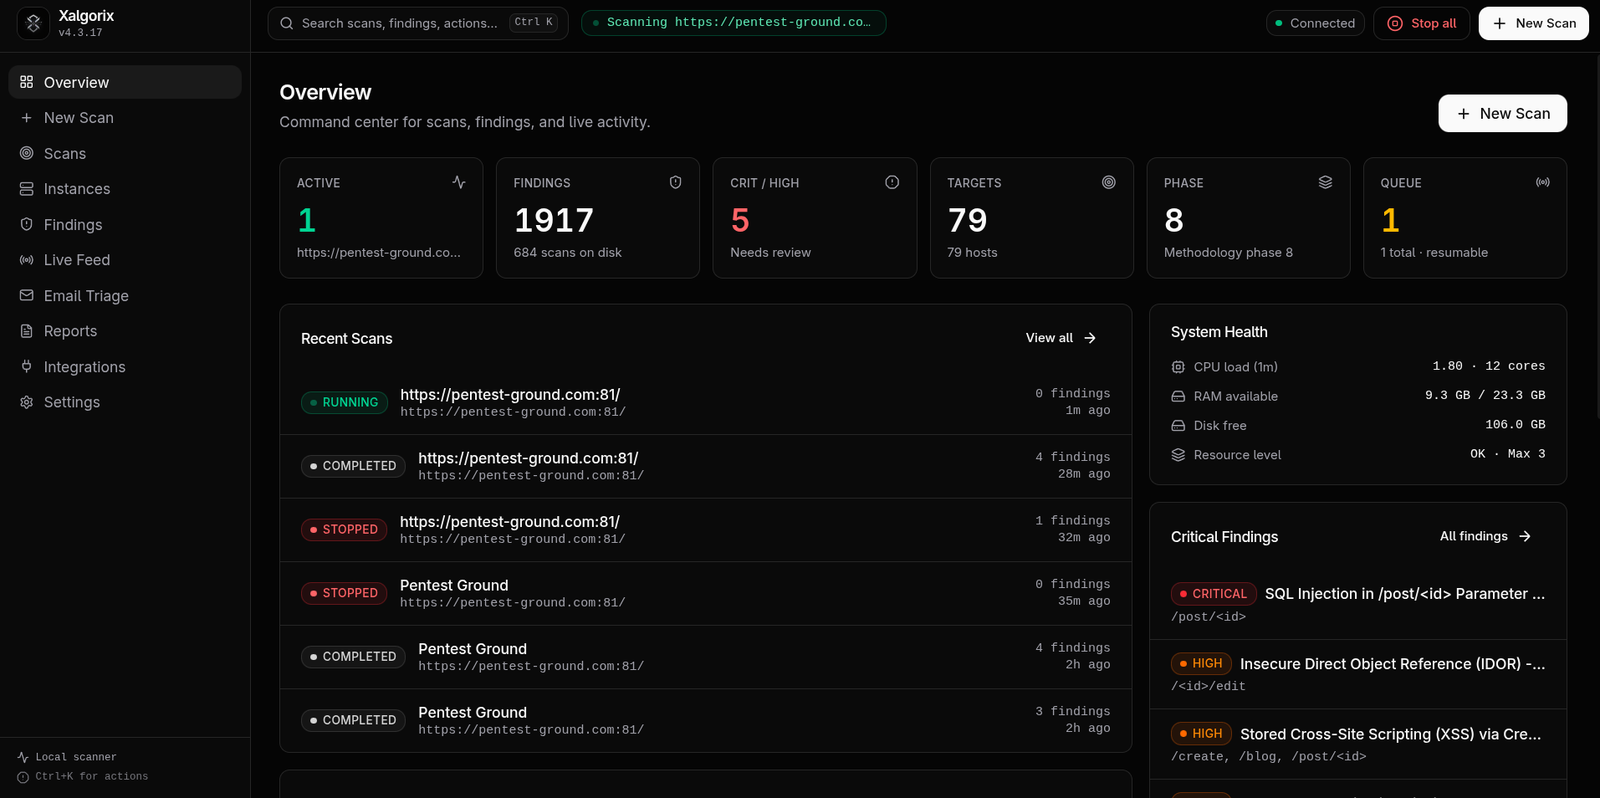 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.