
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
43 results
minisign preview

minisign

GitHubjedisct1/minisign

A dead simple tool to sign files and verify digital signatures.

cryptographydefensive-toolsencryption-decryption-tools+1
2.8k
26 days ago
r77-rootkit preview

r77-rootkit

GitHubbytecode77/r77-rootkit

Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
command-and-controldefensive-toolsids-ips-evasion+6
2.2k2 months ago
IPBan preview

IPBan

GitHubdigitalruby/ipban

Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…
defensive-toolsintrusion-detectionlog-analysis+1
2.2k2 months ago
SigFlip preview

SigFlip

GitHubmed0x2e/sigflip

SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.

binary-analysiscode-analysisdefensive-tools+5
1.3k3 years ago
Intel-Linux-Processor-Microcode-Data-Files preview

Intel-Linux-Processor-Microcode-Data-Files

GitHubintel/intel-linux-processor-microcode-data-files

Official Intel microcode data files for updating processor firmware to mitigate security vulnerabilities and address functional issues on Linux…
defensive-toolsembedded-systems-securityfirmware-analysis+2
8201 month ago
Malcolm preview

Malcolm

GitHubidaholab/malcolm

Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
defensive-toolsdigital-forensicsforensics+8
48227 days ago
CobaltStrikeScan preview

CobaltStrikeScan

GitHubapr4h/cobaltstrikescan

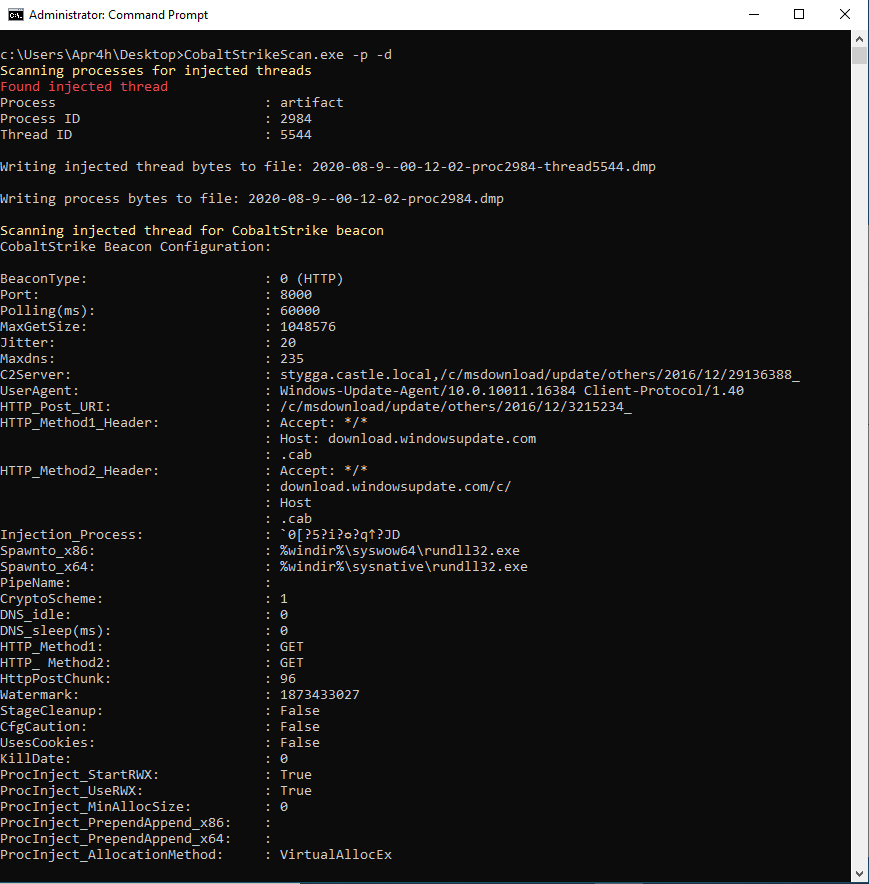
Scan files or process memory for CobaltStrike beacons and parse their configuration
defensive-toolsdigital-forensicsforensics+4
9175 years ago
LazySign preview

LazySign

GitHubjfmaes/lazysign

Create fake certs for binaries using windows binaries and the power of bat files
binary-analysisdefensive-toolsimpersonation-tools+6
5692 years ago
sage preview

sage

GitHubgendigitalinc/sage

Lightweight Agent Detection & Response (ADR) layer for AI agents — guards commands, files, and web requests. Part of Gen Agent Trust Hub.
ai-securitycode-analysisdefensive-tools+6
3105 days ago
ransomware-simulator preview

ransomware-simulator

GitHubnextronsystems/ransomware-simulator

Safe ransomware simulation tool for testing antivirus detection. Simulates macro staging, volume shadow copy deletion, document encryption, and note…
defensive-toolseducationmalware-analysis+2
4844 years ago
RansomLord preview

RansomLord

GitHubmalvuln/ransomlord

RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
binary-exploitationdefensive-toolsexploitation+4
5151 year ago
packetsifterTool preview

packetsifterTool

GitHubpacketsifter/packetsiftertool

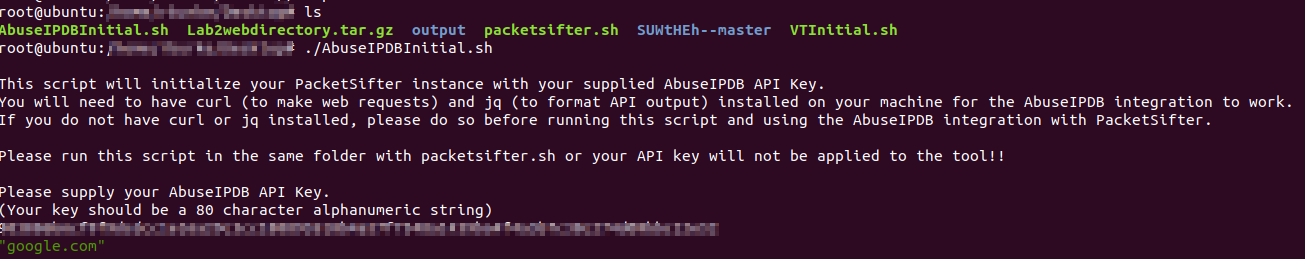
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
defensive-toolsdigital-forensicsforensics+5
935 years ago
SharePointDumper preview

SharePointDumper

GitHubzh54321/sharepointdumper

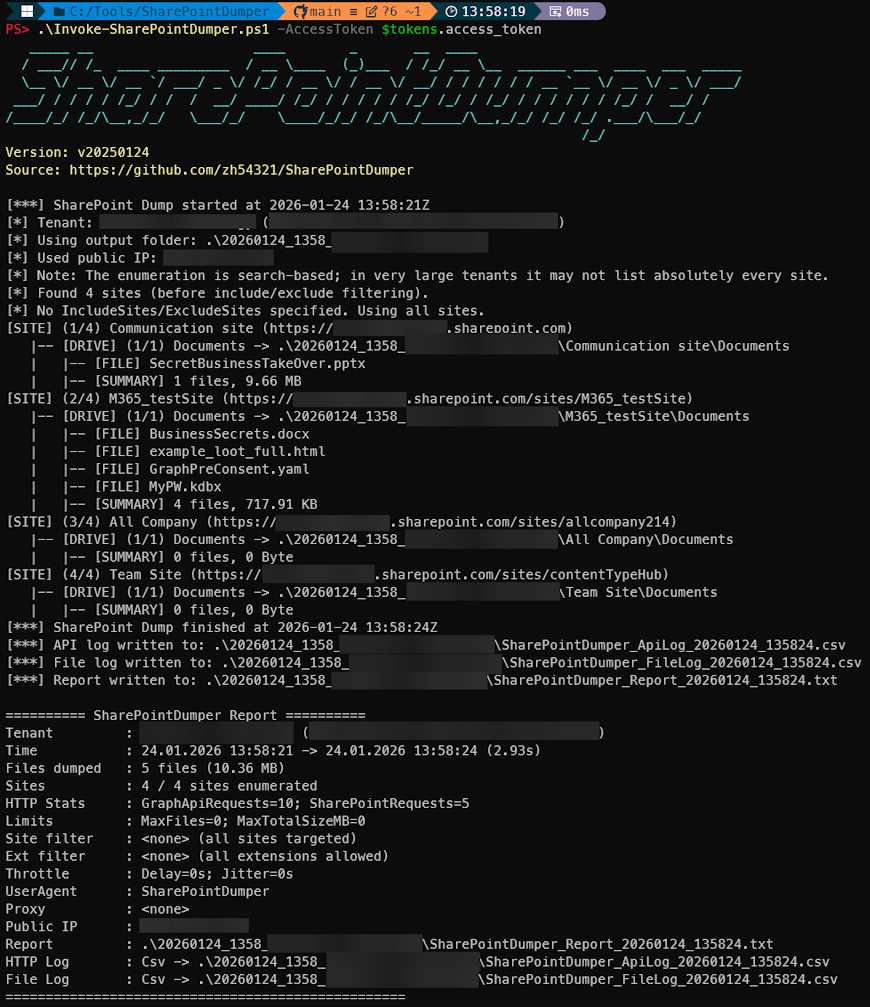
PowerShell SharePoint extraction + auditing tool for red/blue/purple teams. Enumerates all SharePoint sites/drives a user can access via Microsoft…
authenticationcloud-securitydata-exfiltration+7
1917 months ago
YARA_Rules preview

YARA_Rules

GitHubmalgamy/yara_rules

Curated signature-rule collection for detecting and classifying malicious files via pattern matching, with CLI instructions for scanning files and…
curated-resourcesdefensive-toolsincident-response+3
653 years ago
PhantomFS preview

PhantomFS

GitHuballoysecuregroup/phantomfs

Windows honeypot using ProjFS to project decoy files that trigger Event Log and desktop alerts when accessed, with SMB remote session logging for…
defensive-toolsincident-responseintrusion-detection
711 month ago
CheckPlz preview

CheckPlz

GitHubblacksnufkin/checkplz

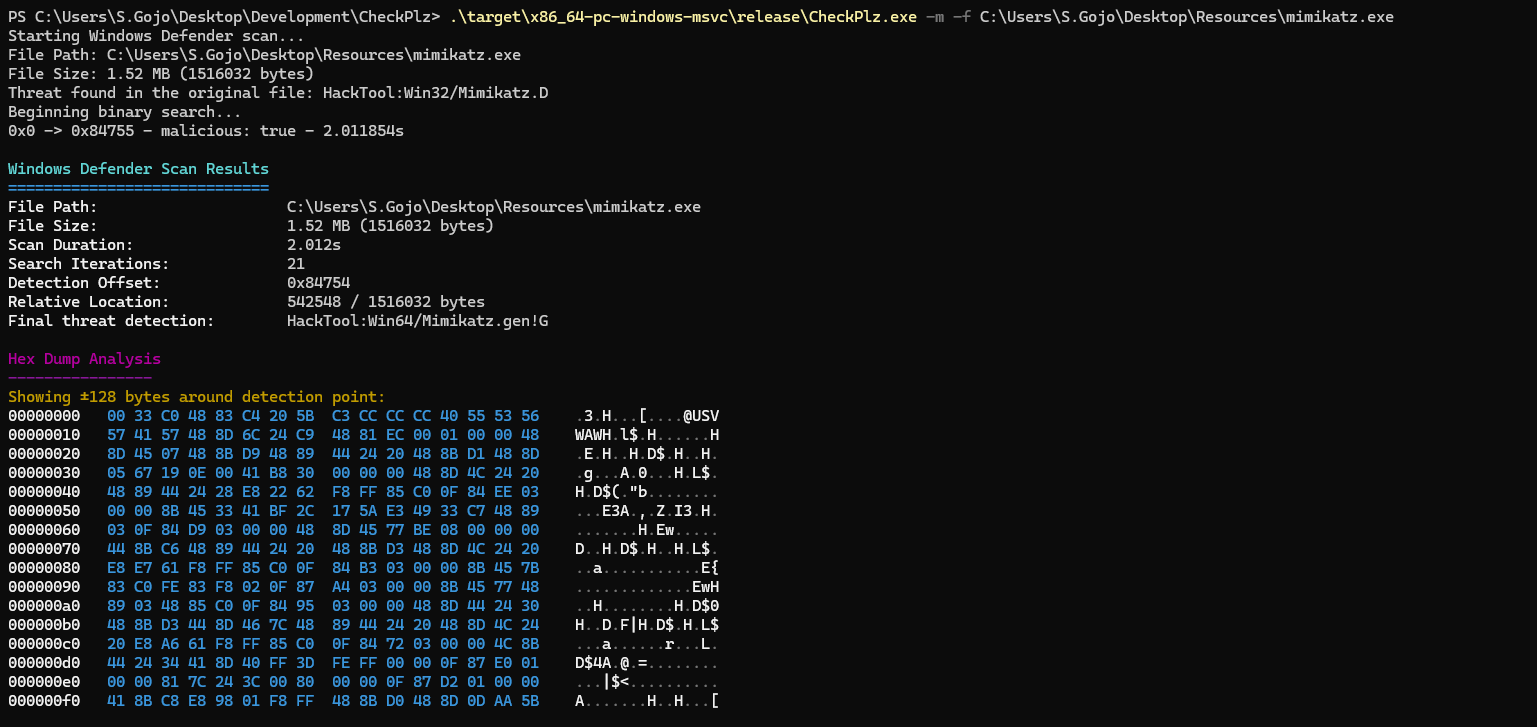
Scan files for potential threats while leveraging AMSI (Antimalware Scan Interface) and Windows Defender. By isolating malicious content.

binary-analysisdefensive-toolsdynamic-analysis-sandboxing+3
491 year ago
DDWPasteRecon preview

DDWPasteRecon

GitHubviralmaniar/ddwpasterecon

DDWPasteRecon tool will help you identify code leak, sensitive files, plaintext passwords, password hashes. It also allow member of SOC & Blue Team…
data-exfiltrationdefensive-toolsincident-response+4
464 years ago
cart preview

cart

GitHubcybercentrecanada/cart

Python implementation of the CaRT library for (un)inerting files.

cryptographydefensive-toolsdigital-forensics+2
551 year ago
Previous123Next