

dfir-orc
 dfir-orc/dfir-orc
Forensics artefact collection tool for systems running Microsoft Windows
defensive-toolsdigital-forensicsforensics+2
dfir-orc/dfir-orcForensics artefact collection tool for systems running Microsoft Windows
 jakehildreth/locksmith
A small tool built to find and fix common misconfigurations in Active Directory Certificate Services.
 prey/prey-android-client
Android client for Prey: reliable device tracking and security tool
 we5ter/flerken
A Solution For Cross-Platform Obfuscated Commands Detection presented on CIS2019 China. 动静态Bash/CMD/PowerShell命令混淆检测框架 - CIS 2019大会
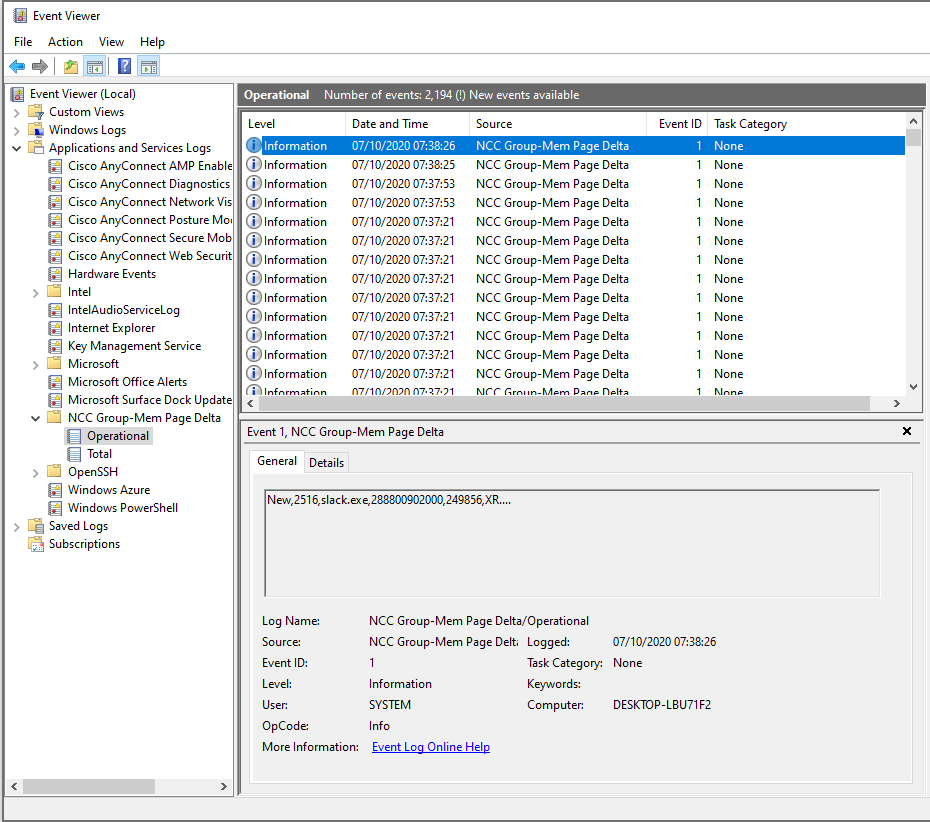 nccgroup/windowsmempagedelta
A Microsoft Windows service to provide telemetry on Windows executable memory page changes to facilitate threat detection
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 emposha/php-shell-detector
Web Shell Detector – is a php script that helps you find and identify php/cgi(perl)/asp/aspx shells. Web Shell Detector has a “web shells” signature…
 fmd-foss/fmd-android
Find your device and control it remotely. Works over SMS, instant messengers, or FMD Server's web interface. A secure open source alternative to…
 otrf/set-auditrule
Useful access control entries (ACE) on system access control list (SACL) of securable objects to find potential adversarial activity
 packetsifter/packetsiftertool
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
 mubix/find-wsus
Helps defenders find their WSUS configurations in the wake of CVE-2025-59287
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 papermtn/slack-watchman
Slack enumeration and exposed secrets detection tool
 spyboy-productions/facad1ng
Open-source URL masking & analysis tool for security research, phishing awareness, and defensive testing. Demonstrates adversary techniques used to…
 malwaretech/edrception
A proof of concept for abusing exception handlers to hook and bypass user mode EDR hooks.

 communityhoneynetwork/chn-server
CommunityHoneyNetwork Server