

lockc
 lockc-project/lockc
Making containers more secure with eBPF and Linux Security Modules (LSM)
cloud-securitycontainer-securitydefensive-tools
lockc-project/lockcMaking containers more secure with eBPF and Linux Security Modules (LSM)
 graphenex/graphenex
Automated System Hardening Framework
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 activecm/passer
Passive service locator, a python sniffer that identifies servers, clients, names and much more
 swimlane/soc-faker
A python package for use in generating fake data for SOC and security automation.
 kunai-project/kunai
eBPF-based Linux security monitor and threat hunter providing chronologically ordered, container-aware events with on-host correlation for incident…
 fencesandbox/fence
Lightweight, container-free sandbox for running commands with network and filesystem restrictions
 thodoristsampouris/agentguard
Zero-trust sandbox for AI agents with kernel-level filesystem jail, transparent network proxy, and YAML-based policy engine to intercept and control…
 trailofbits/claude-code-devcontainer
Sandboxed devcontainer for running Claude Code in bypass mode safely. Built for security audits and untrusted code review.
 loresuso/psc
the ps utility, with an eBPF twist and container context
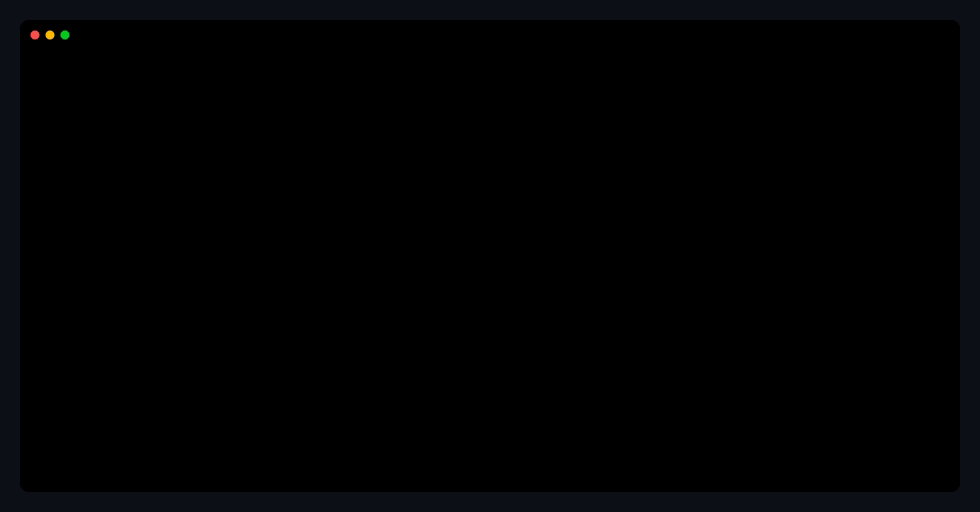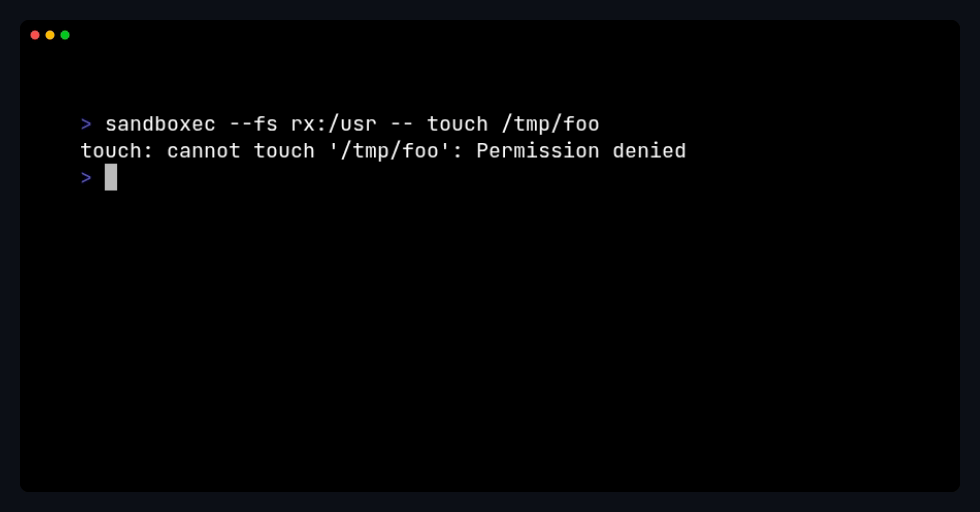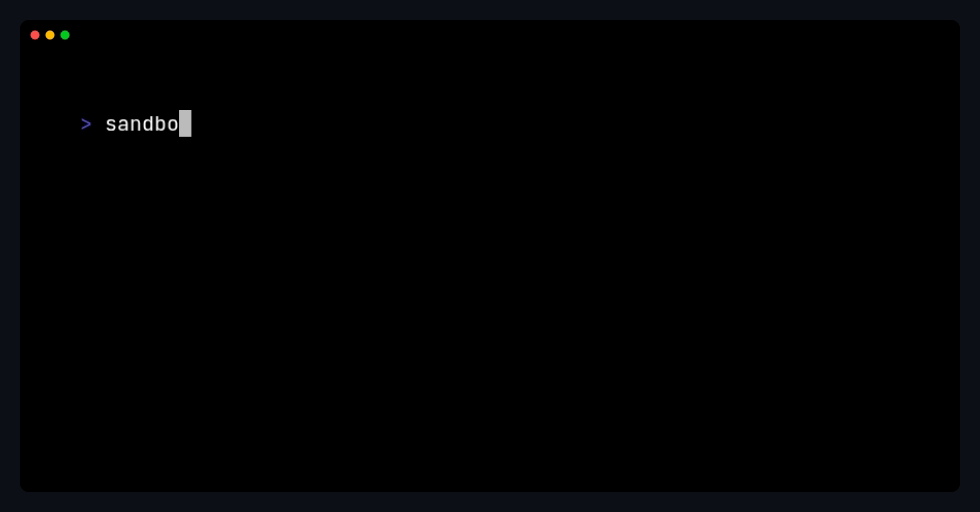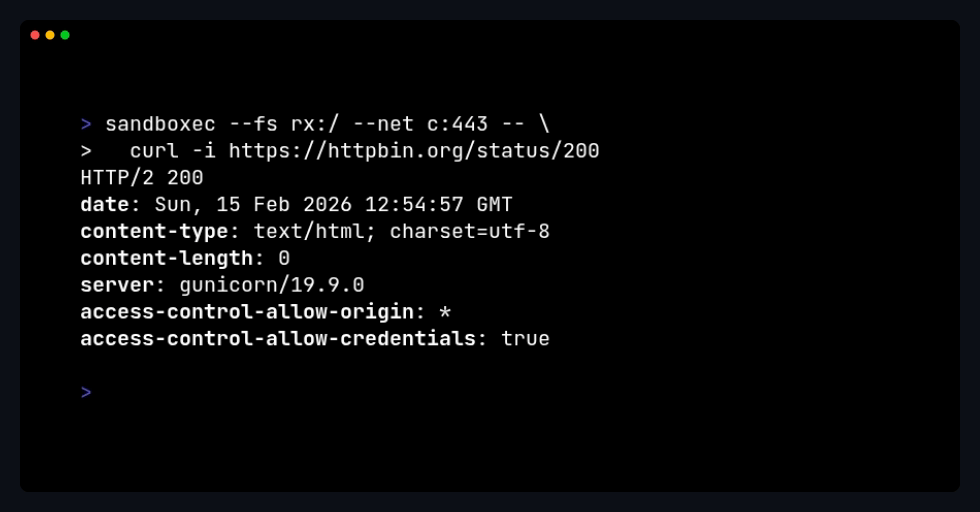 sandboxec/sandboxec
A lightweight command sandbox for Linux, secure-by-default, built on Landlock.
 grepular/foxcage
Run Firefox in a rootless Podman container with dropped capabilities, isolated networking, and ephemeral storage to contain sandbox escapes and…
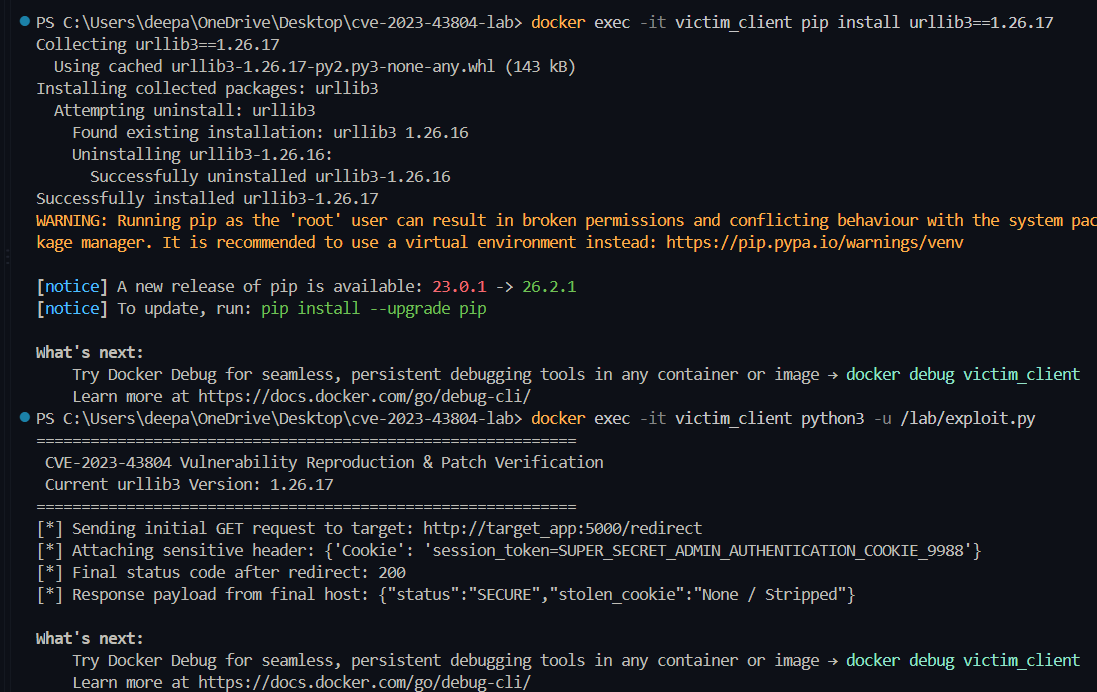 deepanshu-khurana/cve-2023-43804
Containerized three-tier lab reproducing CVE-2023-43804 urllib3 cookie leak via cross-origin redirects, with exploit script and patch verification.
 amulyakaushik/cve-2023-27163-lab
Docker-based lab reproducing CVE-2023-27163 SSRF in Request-Baskets, with exploitation verification, detection script, and network-isolation…
 knqyf263/aqua-checksums
Monitors cryptographic integrity of container images, releases, and Git tags for supply chain security, verifying Sigstore cosign signatures with…
 zsxen/cve-2025-1974
Windows 11-first educational lab for studying CVE-2025-1974 in ingress-nginx. Provides safe attack emulation and defense validation with local…
 secdev02/cyber-decoy
Experimental Decoy Broker
 wattocyber/detection-defense-library
Detection-engineering reference mapping Windows, cloud, container, identity, and ICS attack classes to Sigma rules, trust-boundary models, BYOVD…