ALYCON-Threat-Landscape

Training-free anomaly detection framework using Shannon Entropy, Fisher Information, and Wasserstein Distance to map system states into geometrically…

Training-free anomaly detection framework using Shannon Entropy, Fisher Information, and Wasserstein Distance to map system states into geometrically…

Splunk detection writeup for CVE-2026-54121 (CertiGhost): AD CS certificate chase abuse leading to full domain compromise. Lab-validated detection,…

Zeek package to detect Zerologon

AIEngine is a next generation interactive/programmable Python/Ruby/Java/Lua and Go NIDS (Network intrusion detection system).

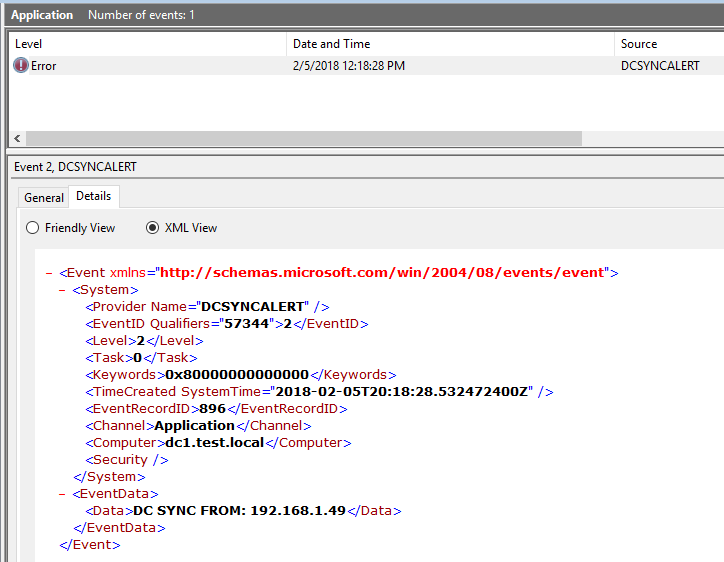
Monitors for DCSYNC and DCSHADOW attacks and create custom Windows Events for these events.

Dynamically generated Suricata rules from real-time threat feeds

CVE-2025-55182-scanner with 2 different method

Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.

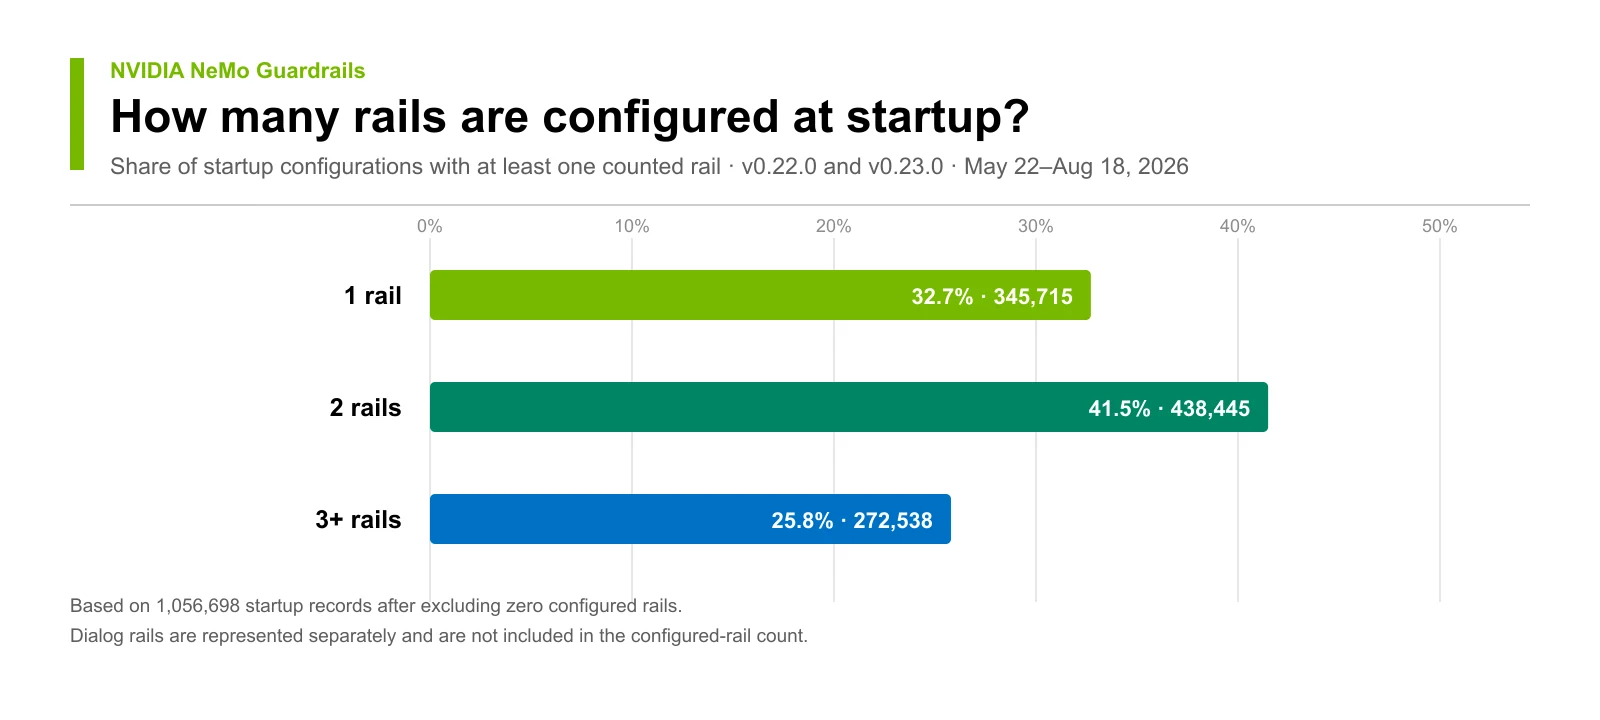
Programmable guardrails for LLM chat apps: enforce input/output rails, block jailbreaks and prompt injections, detect hallucination, and mask…

A repository of sysmon configuration modules

Tools for hunting for threats.

Docker configuration to quickly setup your own Canarytokens.

A smart gateway to stop cyber criminals - Sponsored by Falcon Guard

Advanced Phishing Protection: Suricata rulesets open and free

Zero-dependency Windows EDR utility that detects and mitigates unauthorized LSASS memory access, handle duplication, and LOLBin credential dumping in…

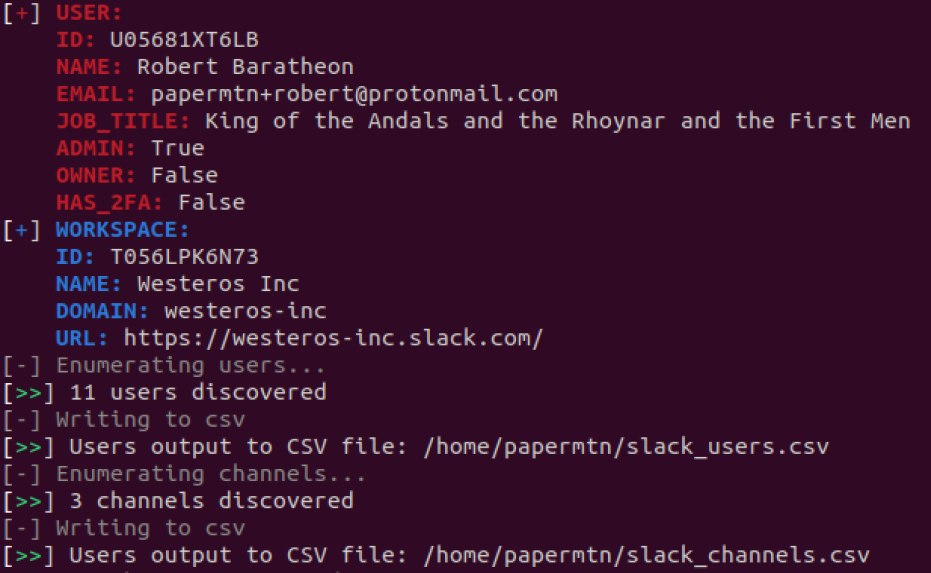
Slack enumeration and exposed secrets detection tool

Blue Team detection lab created with Terraform and Ansible in Azure.

Windows service that creates fake SMB sessions to simulate high-privilege user logons, luring attackers into honeypot machines for early detection…