
msteams
 whispergate/msteams
Mythic C2 profile that tunnels agent traffic through Microsoft Teams channels using the Microsoft Graph API, with AES256 encryption, jitter, kill…
command-and-controldefensive-toolsencryption-decryption-tools+5
39
whispergate/msteamsMythic C2 profile that tunnels agent traffic through Microsoft Teams channels using the Microsoft Graph API, with AES256 encryption, jitter, kill…
 alphasoc/flightsim
A utility to safely generate malicious network traffic patterns and evaluate controls.
 onyks-os/transparenttorproxy
A Linux CLI utility that transparently routes all system traffic through the Tor network using nftables. It enables rapid IP rotation and easy…
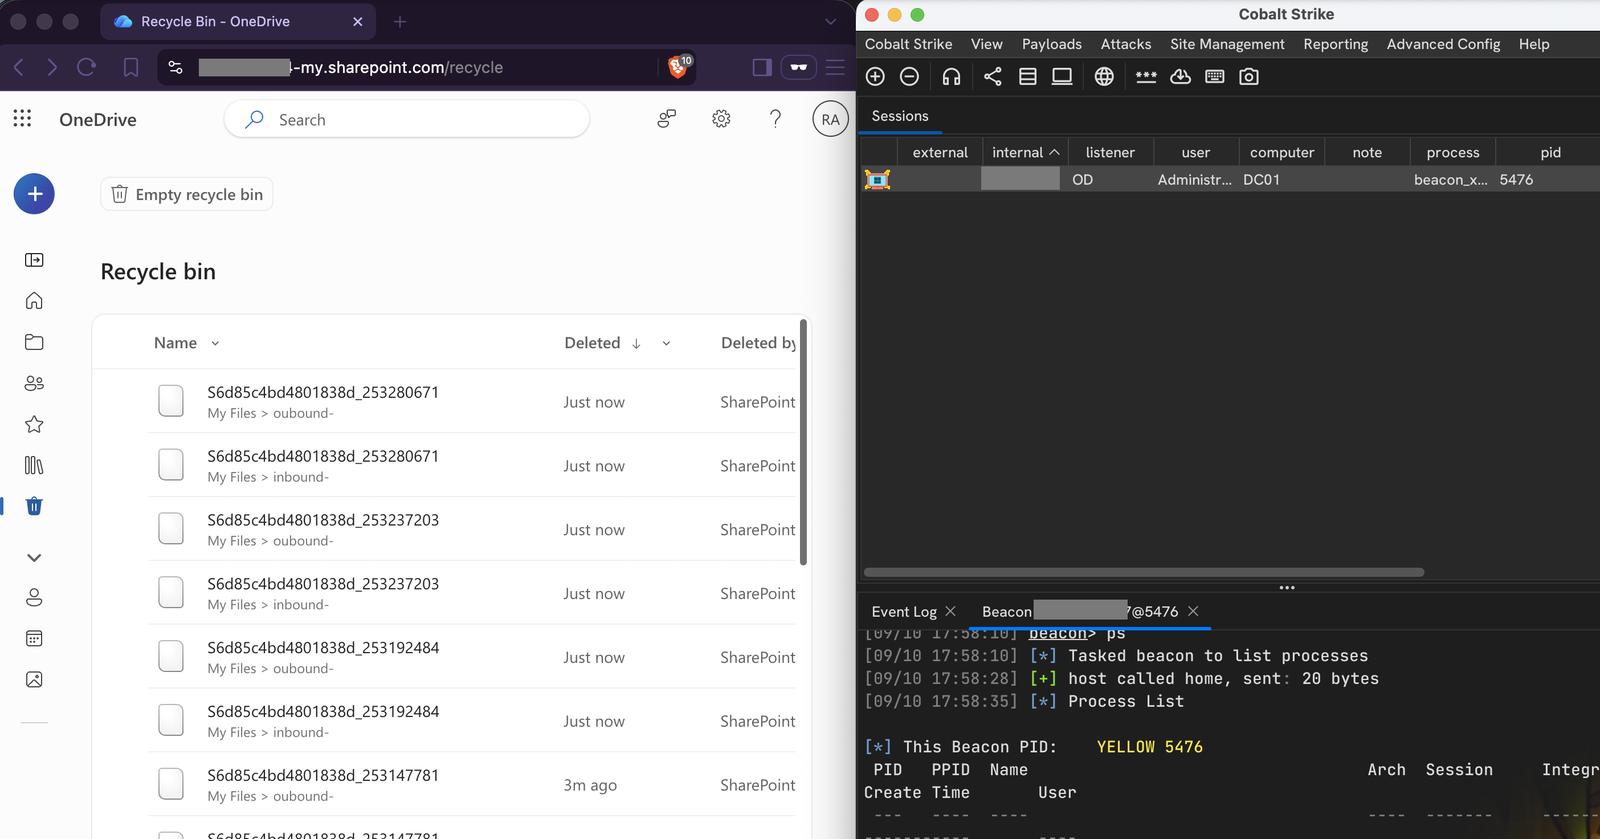 nmht3t/onedrive-udc2
OneDrive as a covert C2 transport for Cobalt Strike
 galoryber/fawkes
Fawkes is a golang Mythic C2 Agent exclusively written by AI.
 kaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis
Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
 audibleblink/bothan
Is this IP a C2 server?
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
 sastraadiwiguna-purpleeliteteaming/ddos-purple-teaming-offensive-multi-vector-7-tier-defensive-holistic-blueprint-
Replicable Blueprint for advanced DDoS Purple Teaming, engineered for the threat landscape. It integrates a Red Elite Teaming offensive…
 mythicc2profiles/httpx
Configurable, Community driven, HTTP C2 Profile
 watchtowrlabs/citrix-netscaler-cve-2026-88771-iocs
Indicators of Compromise and hunting guidance for CVE-2026-88771, an unauthenticated command injection in Citrix NetScaler ADC and Gateway, covering…
 tyeurada/edrevasionworkshop
Workshop materials for “Step-by-Step Malware Development: Evading EDR from Loaders to the Kernel” presented at DEF CON 34 and BSidesLV 2026. Covers…
 theflink/hunt-sleeping-beacons
Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
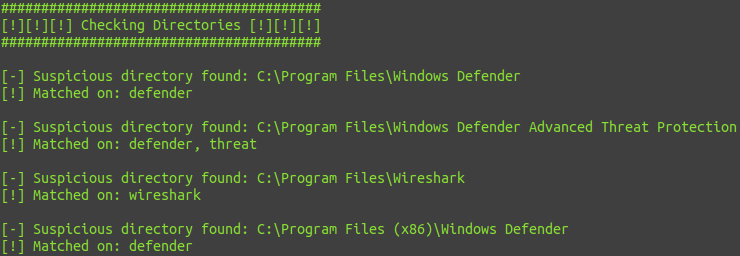 pwndexter/sharpedrchecker
C# tool that enumerates running processes, loaded DLLs, installed services, and drivers to detect the presence of AV, EDR, and logging products,…
 corelight/redxor
Detection of Linux Malware C2 RedXOR - demonstration
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.
 embee-research/yara-detection-rules
Yara Rules for Modern Malware
 ldpreload/blacklotus
BlackLotus UEFI Windows Bootkit