
EDRHunt
 fourcorelabs/edrhunt
Scan installed EDRs and AVs on Windows
defensive-toolsinformation-gatheringreconnaissance+1
fourcorelabs/edrhuntScan installed EDRs and AVs on Windows
 trustedsec/spoonmap
Python wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…
 spaceraccoon/manuka
A modular OSINT honeypot for blue teamers
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.
 r00t-3xp10it/redpill
Assist reverse tcp shells in post-exploration tasks
 gbrindisi/wordpot
A Wordpress Honeypot
 pwndexter/invoke-edrchecker
PowerShell script that enumerates running processes, loaded DLLs, services, registry, and drivers to detect the presence of AV, EDR, and logging…
 patrowl/patrowlhears
PatrowlHears - Vulnerability Intelligence Center / Exploits
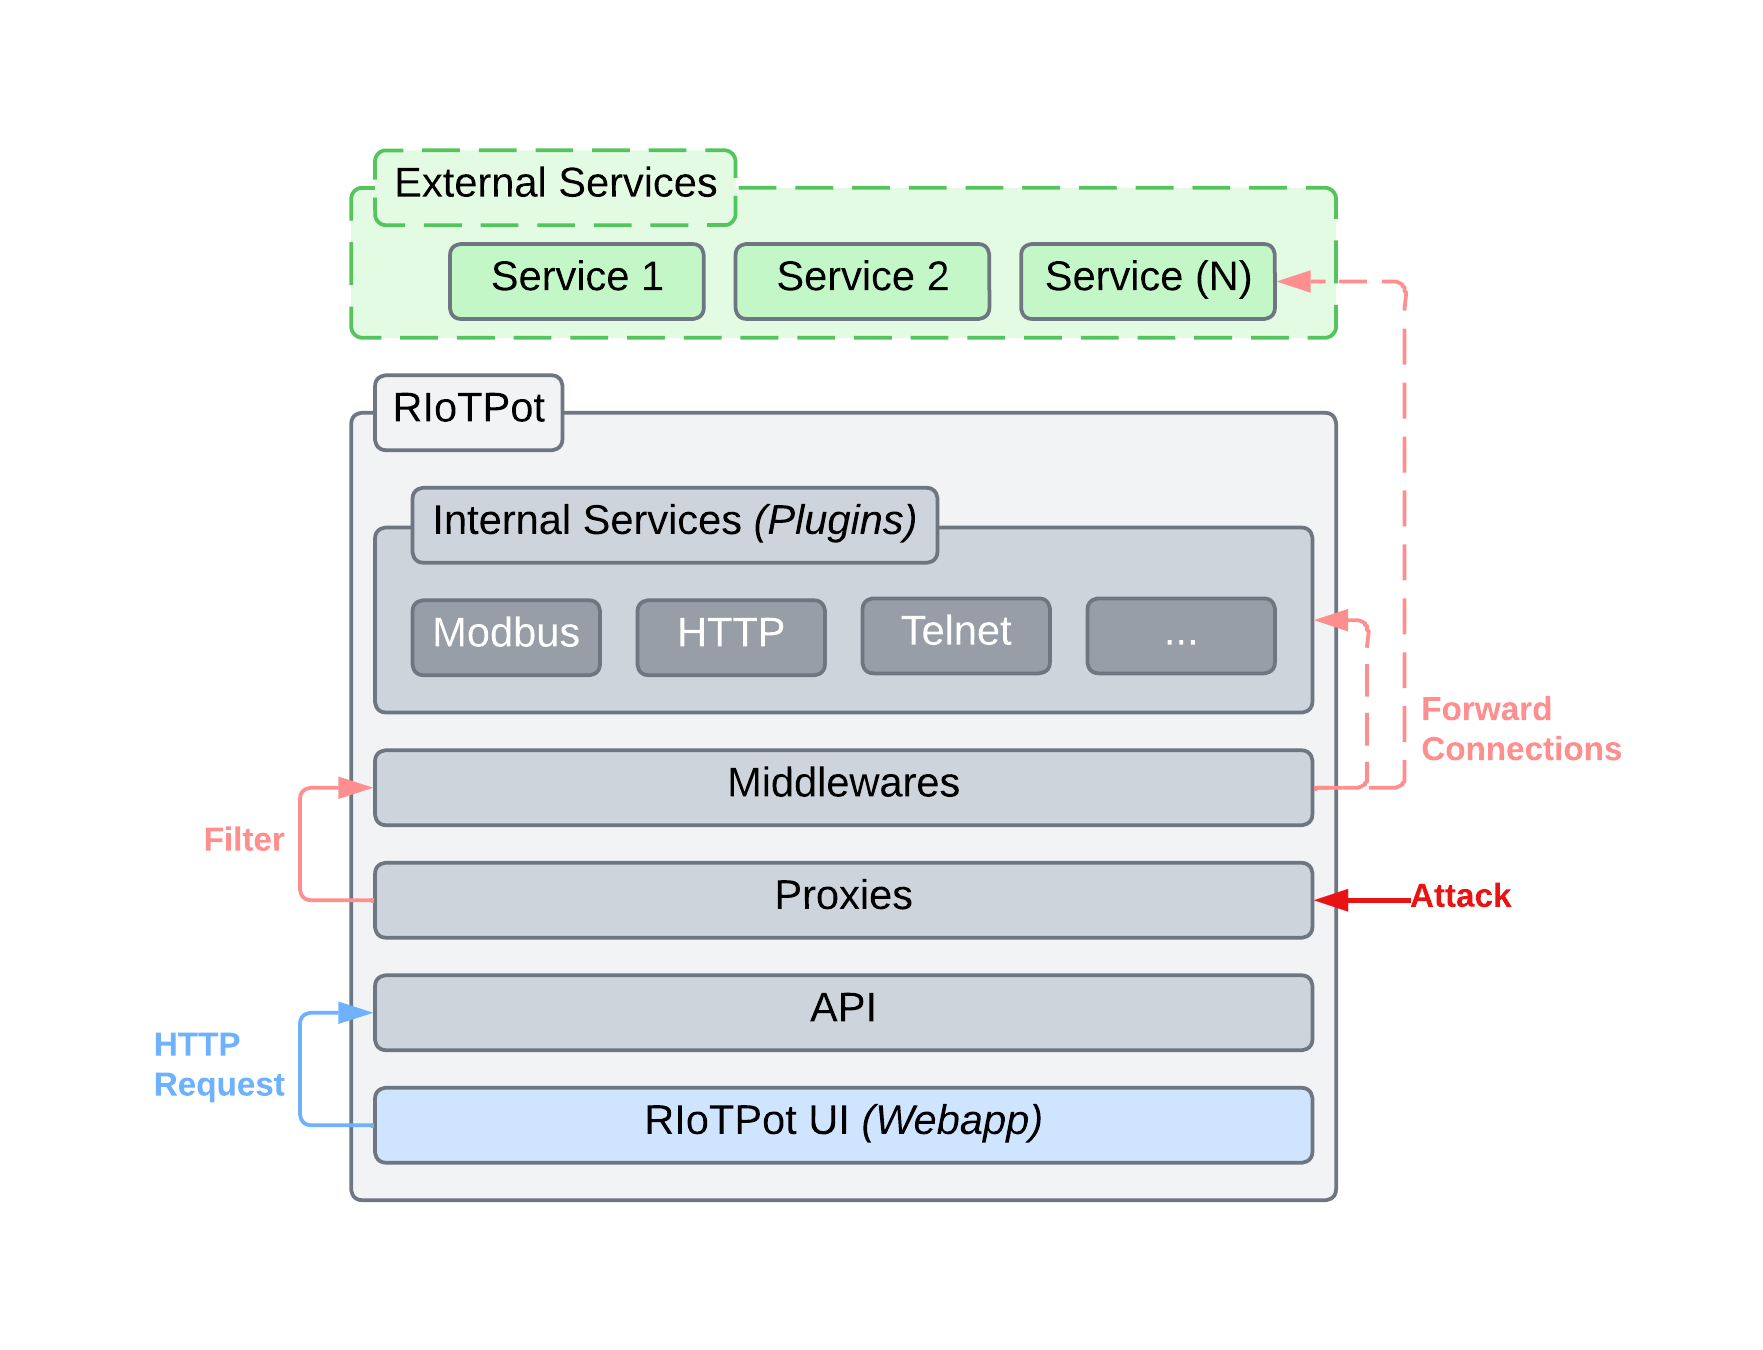 aau-network-security/riotpot
IoT and Operational Technology Honeypot
 randomuserid/tylium
Primary data pipelines for intrusion detection, security analytics and threat hunting
 ammarion/waf-detector
🛡️ High-performance WAF & CDN detection tool. Identify protection layers (Cloudflare, Akamai, AWS, Fastly, and more), run effectiveness and…
 ssteelfactor-oss/kestrel
Low-observability Active Directory security enumeration tool using native ADSI/COM interfaces. Enumerates ACLs, delegation, trusts, ADCS, Kerberoast…
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 crypt0p3g/adnullenum
One-pass anonymous Active Directory enumeration over SAMR and LSARPC — null session, no credentials, with structured reusable output.
 reloading01/certstream-server-rust
High-performance Certificate Transparency (CT) monitoring tool written in Rust. Real-time stream of newly issued SSL/TLS certificates from CT logs.…
 ivancabrera02/hashsiphon
Extracts the current user's NetNTLMv2 hash via HTTP authentication proxying, avoiding direct SSPI calls; v2 delegates auth to the BITS service to…
 iamagarre/badexclusionsnwbo
BadExclusionsNWBO is an evolution from BadExclusions to identify folder custom or undocumented exclusions on AV/EDR
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…