

OpenHunterAI
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
ai-securityapi-securityapi-security-testing+9
338
lumoslab-innovation/openhunteraiLocal-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 portswigger/active-scan-plus-plus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, code injection, and known CVEs like…
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 datadog/threatest
CLI and Go framework for end-to-end testing of threat detection rules. Detonates attack techniques and verifies alerts in security platforms like…
 cyberark/evasor
A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies
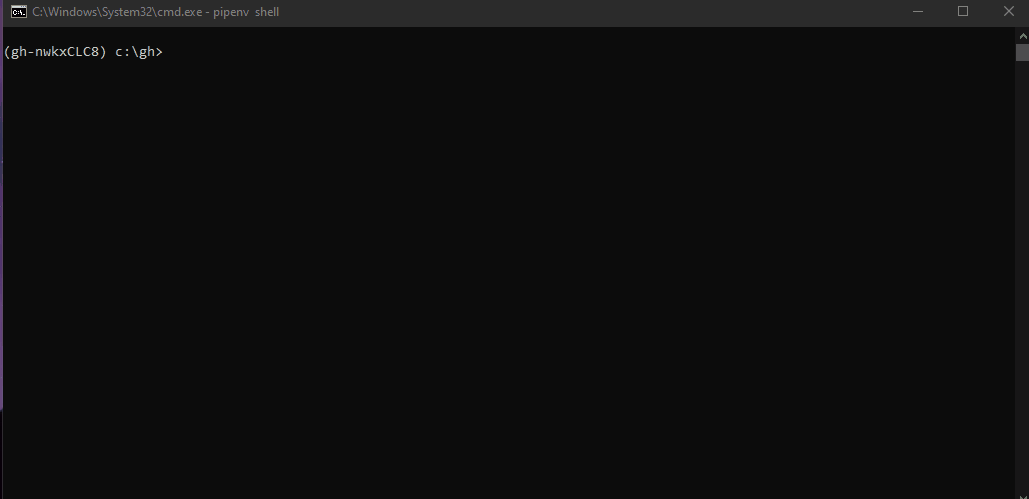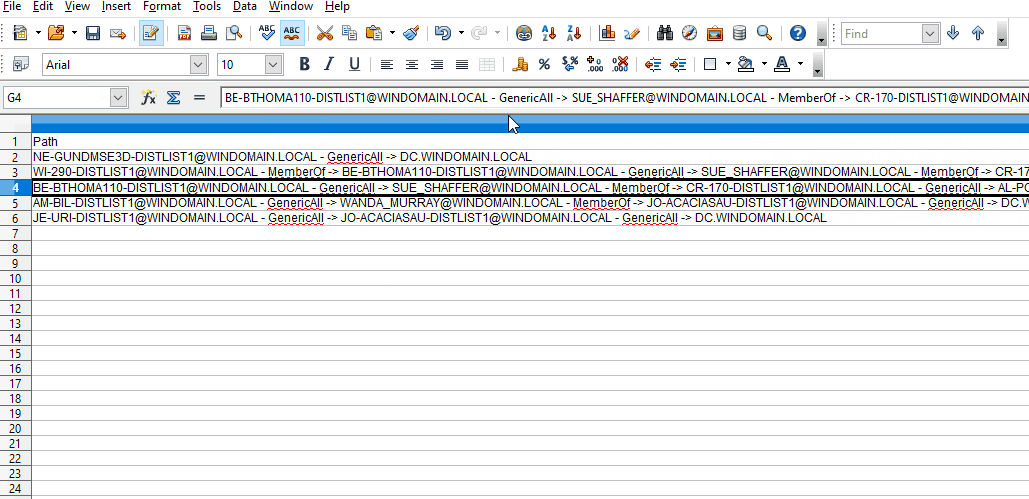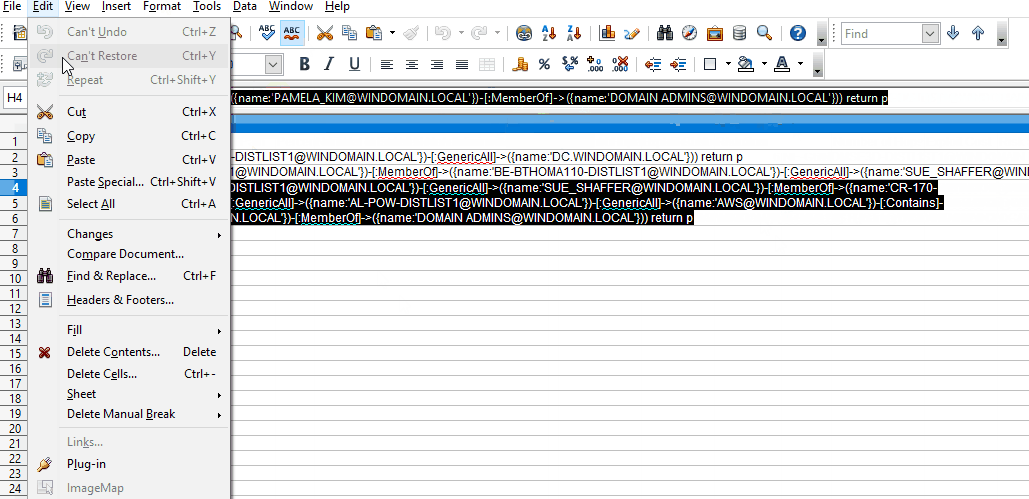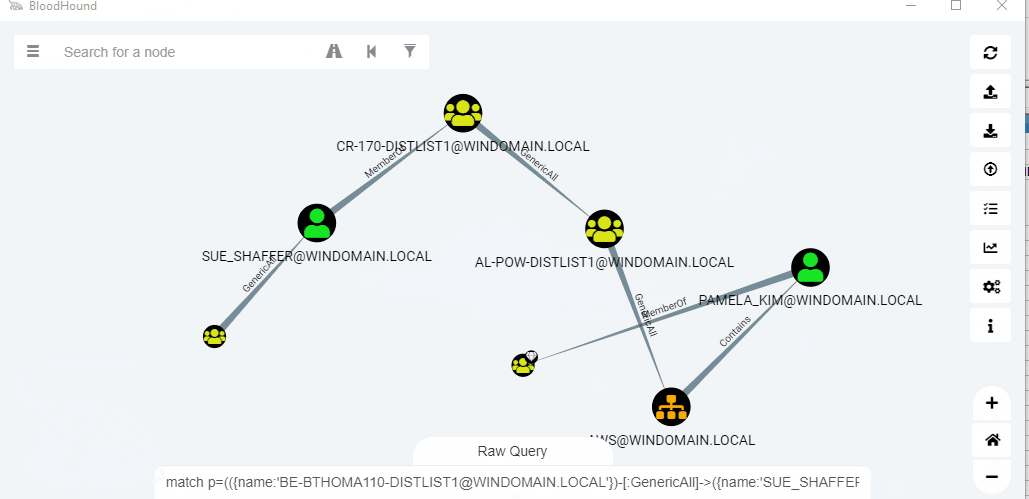 idnahacks/goodhound
Uses Sharphound, Bloodhound and Neo4j to produce an actionable list of attack paths for targeted remediation.
 ge0rg/memorizingtrustmanager
A "plugin" for Android Java to allow asking the user about SSL certificates
 a-d-team/sharpmemshell
.NET in-memory webshell (memshell) payloads implemented via HttpListener and VirtualPath, compatible with the Godzilla 4.01 post-exploitation…
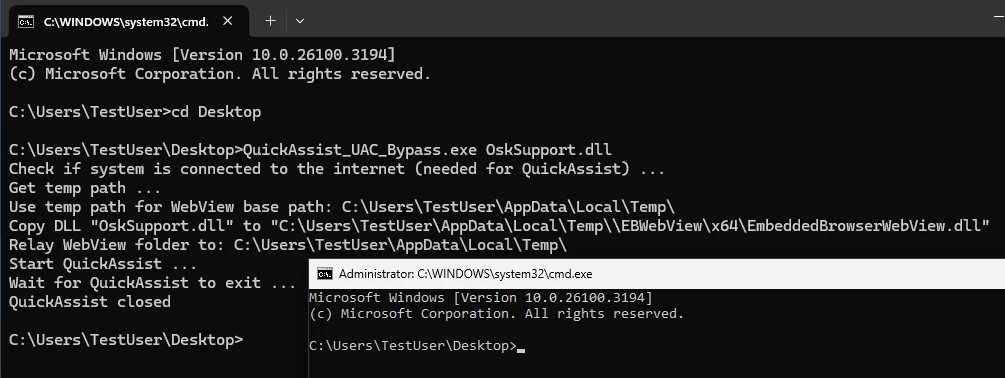 r41n3rzuf477/quickassist_uac_bypass
UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…
 redcanaryco/atomictestharnesses
Public Repo for Atomic Test Harness
 magisterquis/sshhipot
High-interaction MitM SSH honeypot
 olafhartong/bamboozledr
A comprehensive ETW (Event Tracing for Windows) event generation tool designed for testing and research purposes.
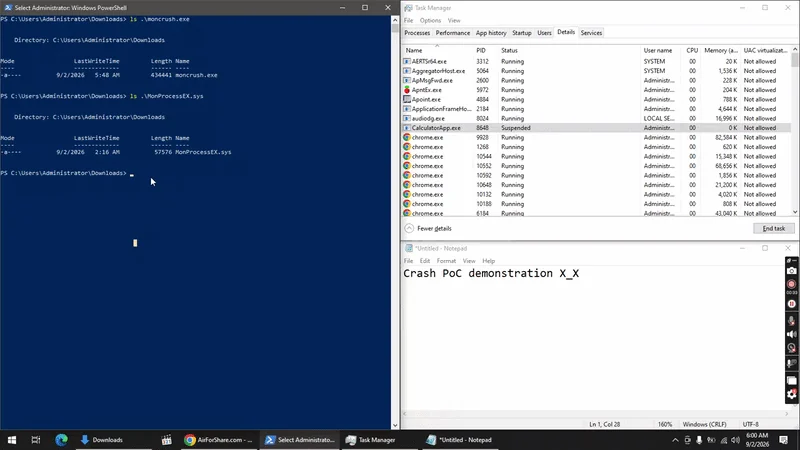 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
 hwbp/clr-unhook
Modern security products (CrowdStrike, Bitdefender, SentinelOne, etc.) hook the nLoadImage function inside clr.dll to intercept and scan in-memory…
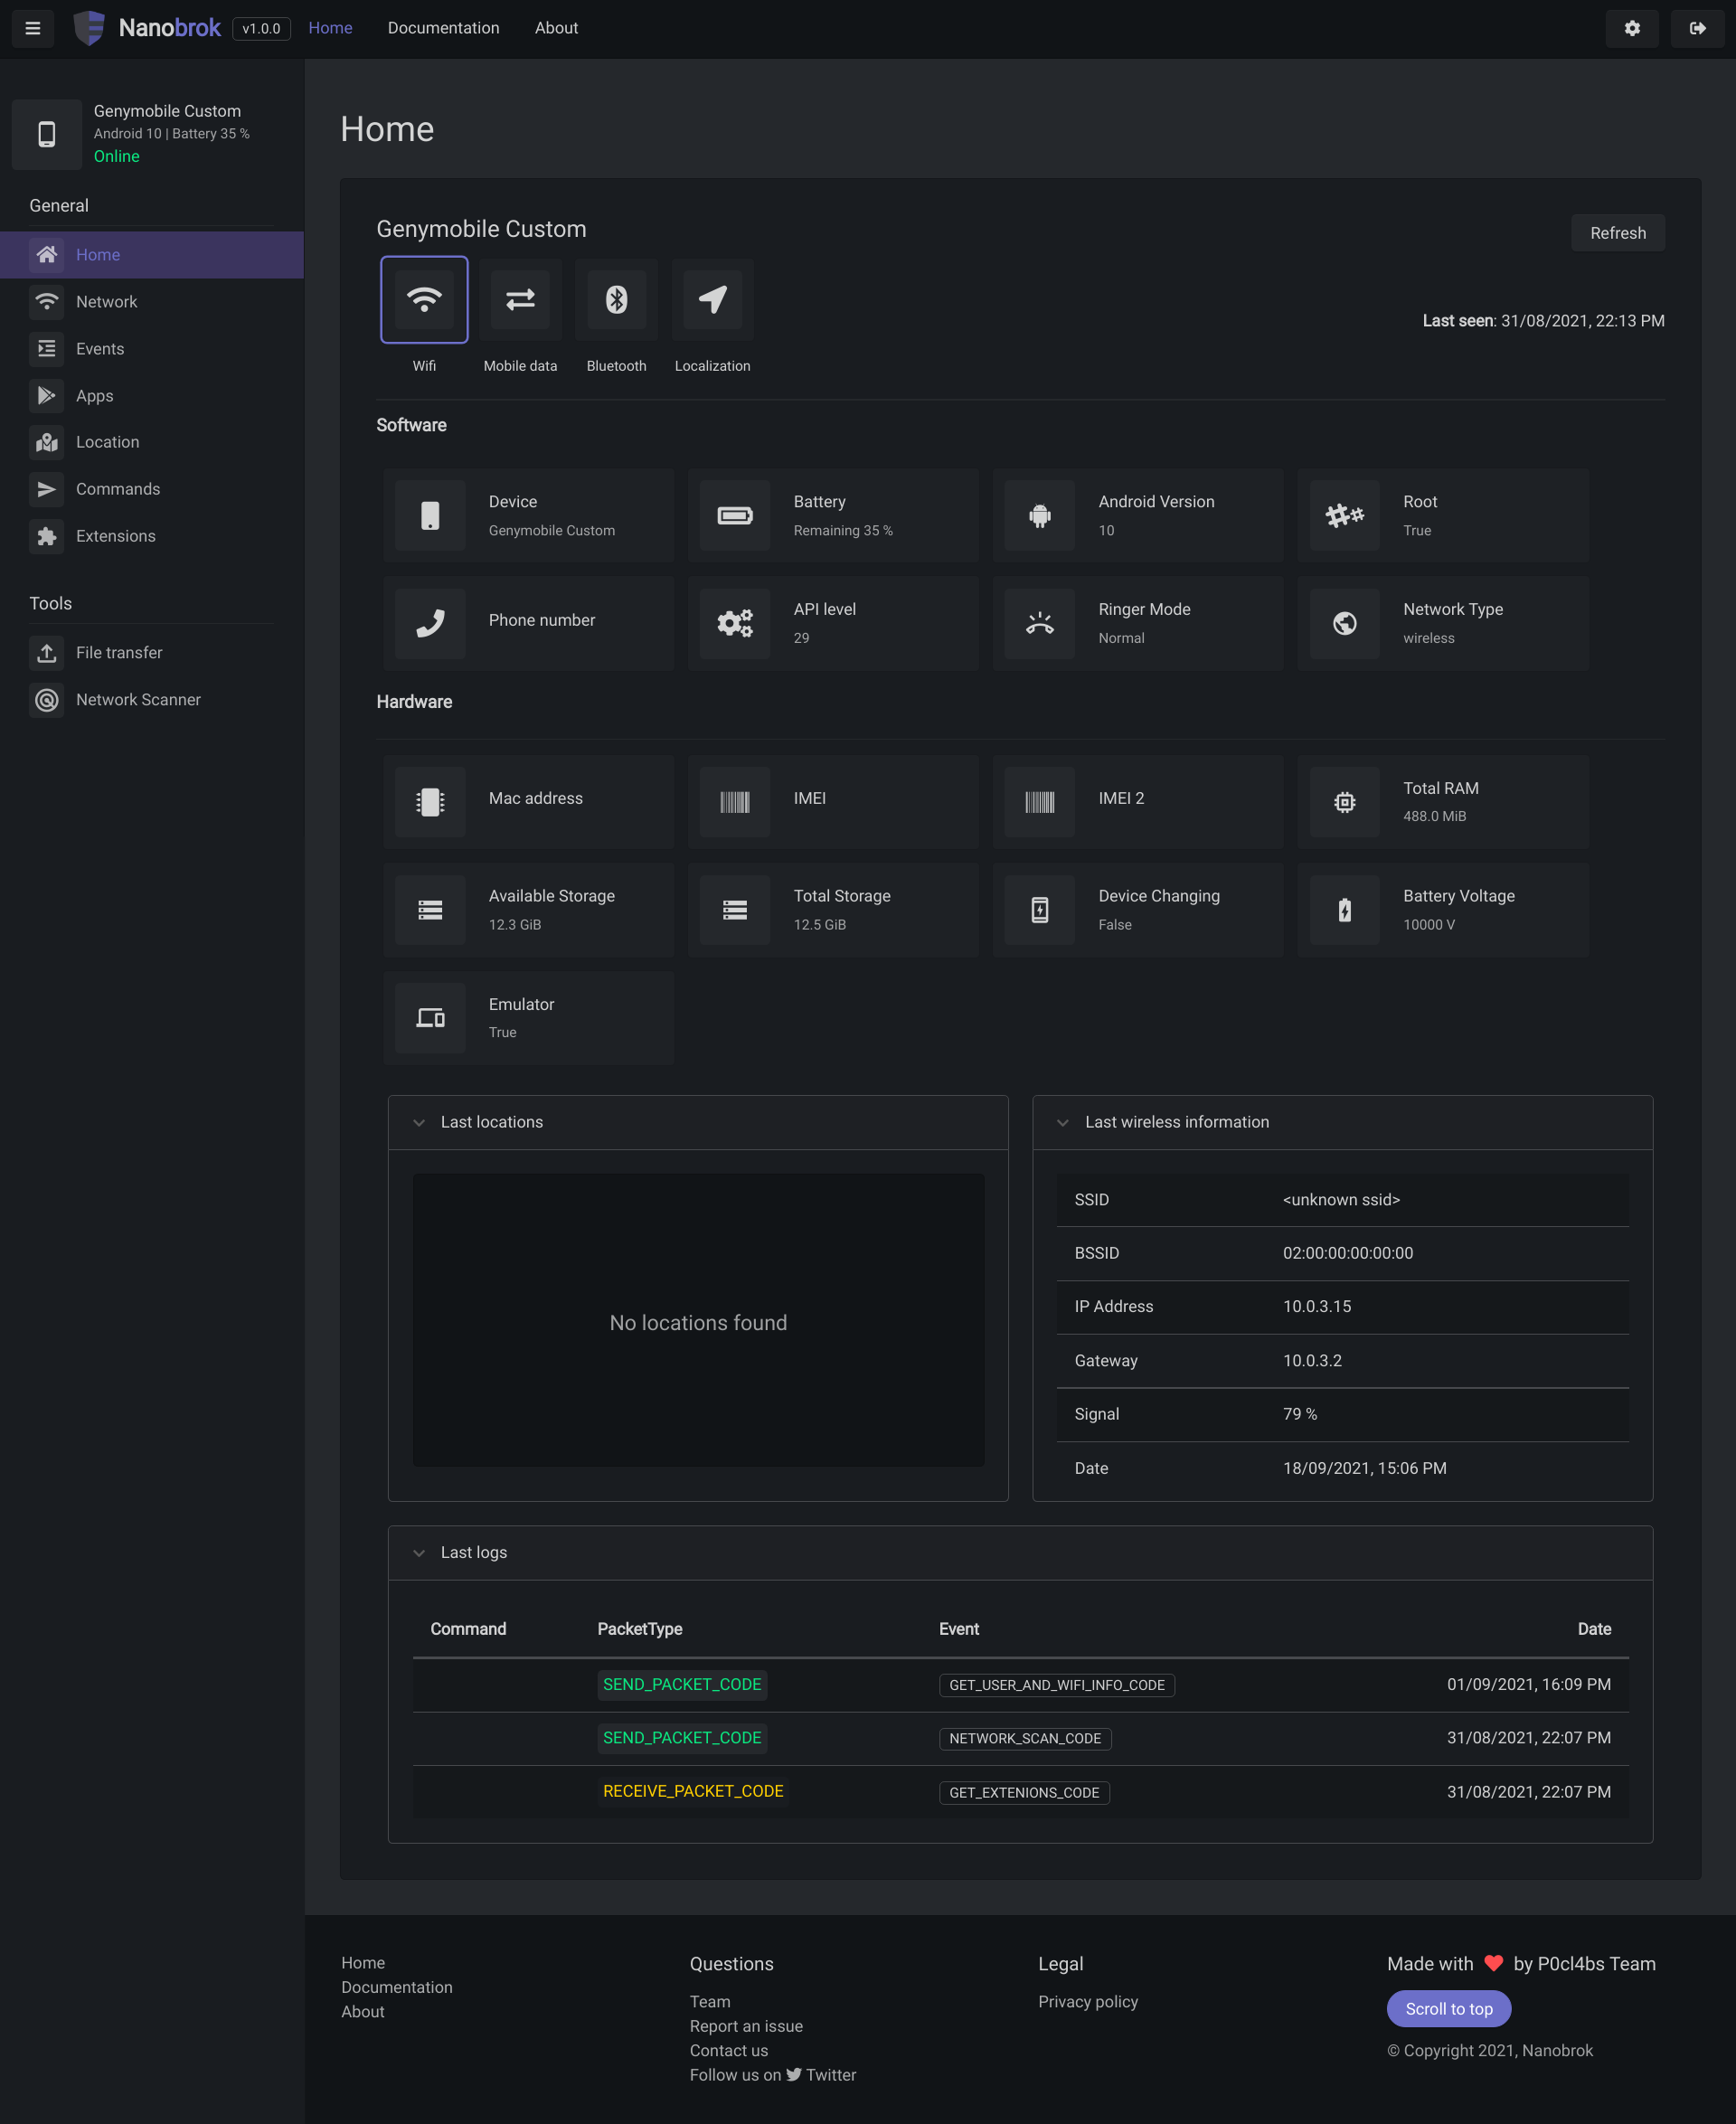 p0cl4bs/nanobrok
Web Service write in Python for control and protect your android device remotely.
 thannikudam/topazterminator
C-based tool exploiting the vulnerable wsftprm.sys kernel driver to terminate protected EDR/AV processes on Windows, including PPL processes, via…
 shutdownrepo/dcshadow
Python alternative to Mimikatz lsadump::dcshadow
 cedowens/macshellswift
Proof of concept MacOS post exploitation tool written in Swift. Designed as a POC for blue teams to build macOS detections. Author: Cedric Owens