
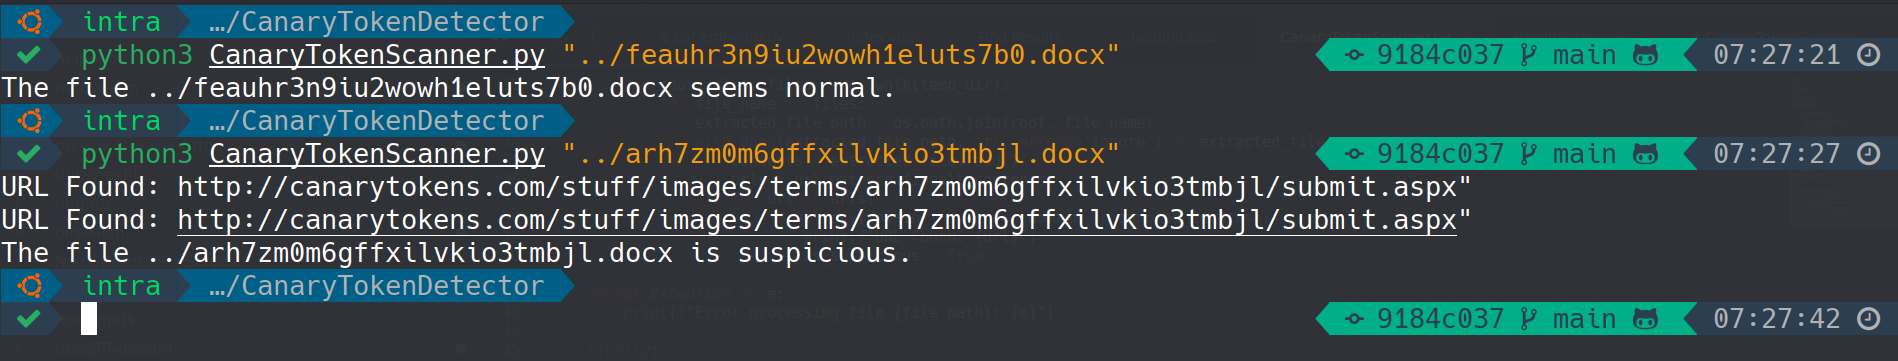
CanaryTokenScanner
 0xnslabs/canarytokenscanner
Detects CanaryTokens in Office docs and PDFs (docx, xlsx, pptx, pdf) without triggering alerts
defensive-toolseducationforensics+2
149
0xnslabs/canarytokenscannerDetects CanaryTokens in Office docs and PDFs (docx, xlsx, pptx, pdf) without triggering alerts
 malwaretech/appcontainersandbox
An example sandbox using AppContainer (Windows 8+)
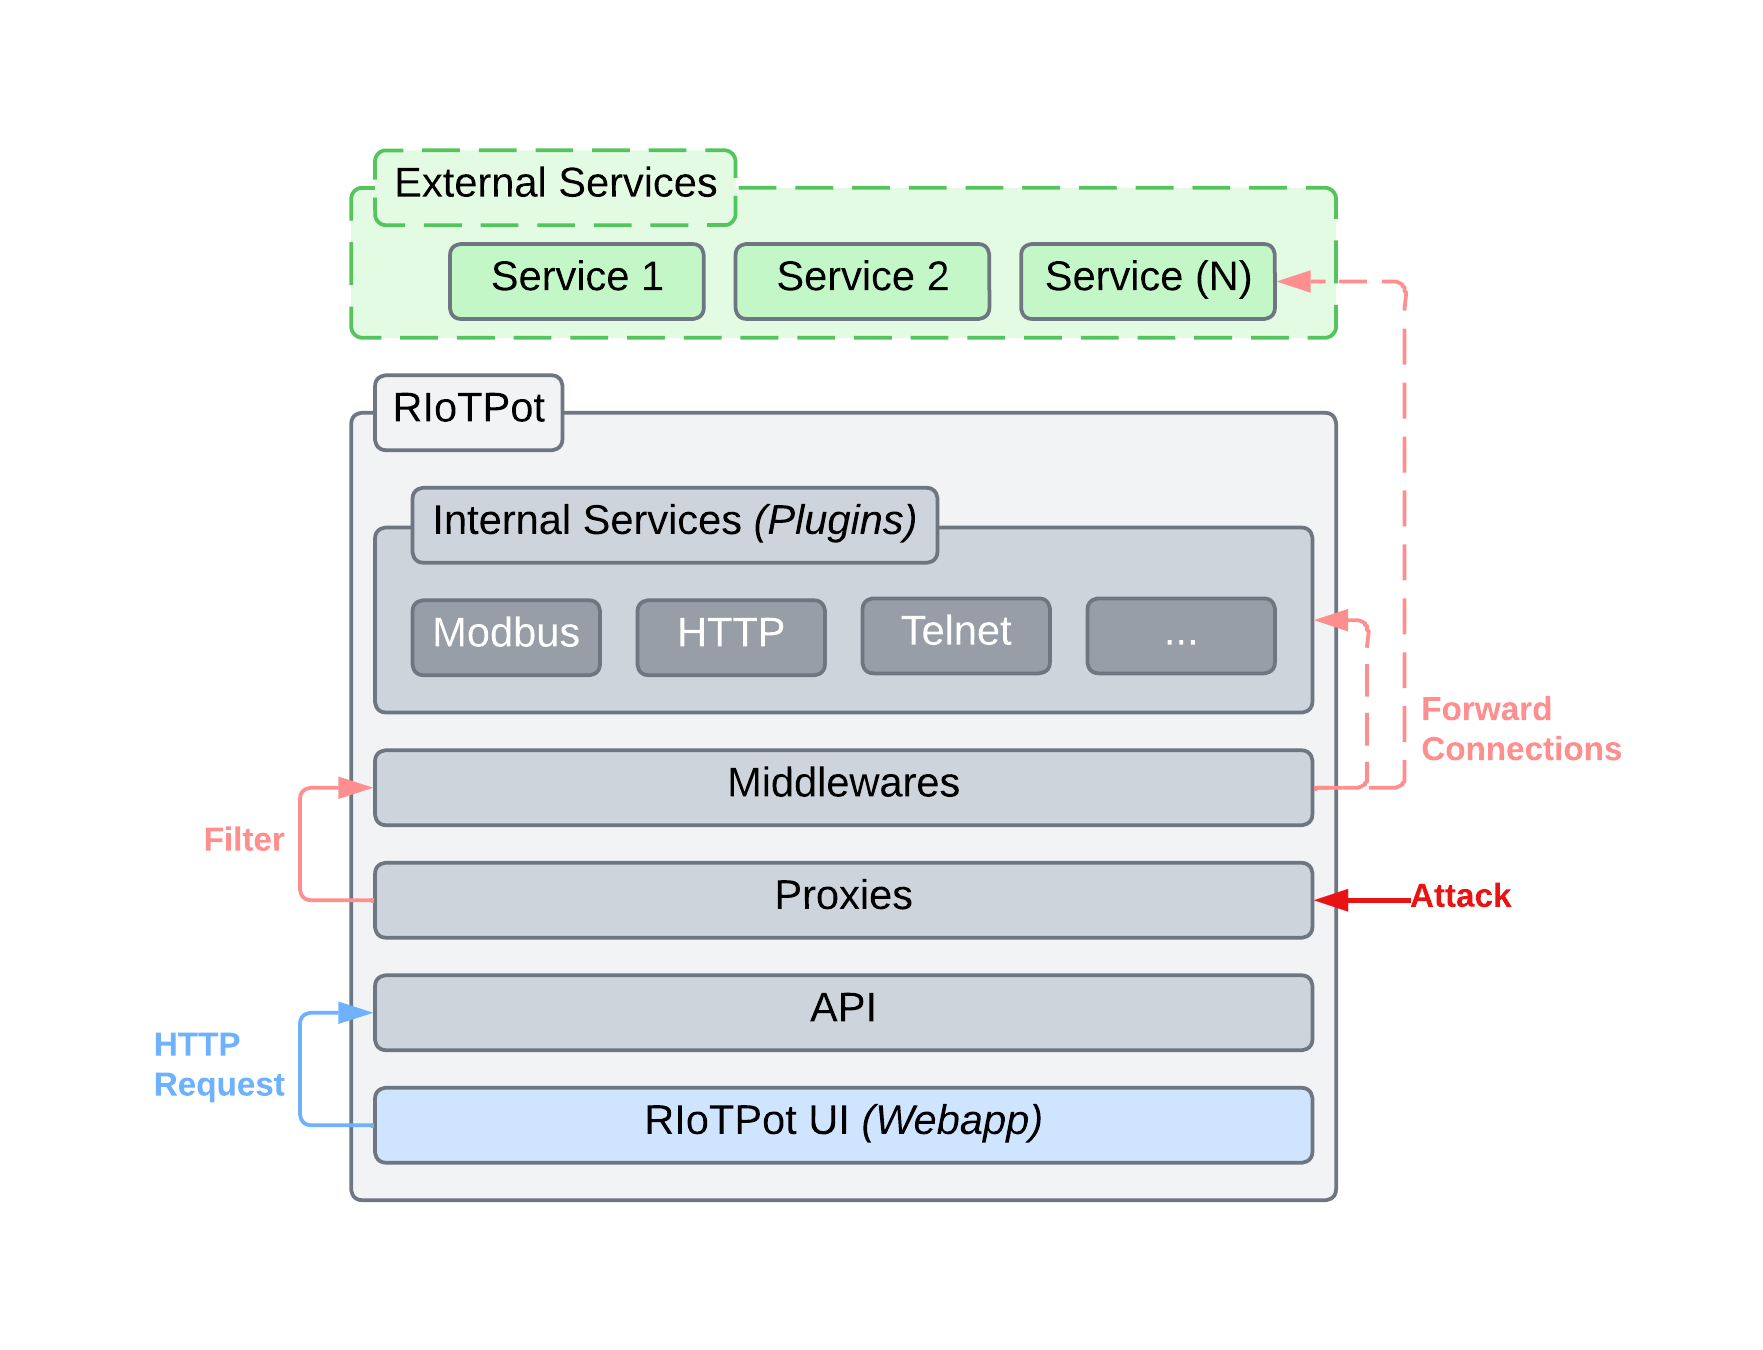 aau-network-security/riotpot
IoT and Operational Technology Honeypot
 neo23x0/process-watcher
A process monitoring tool that tries to detect exploitation
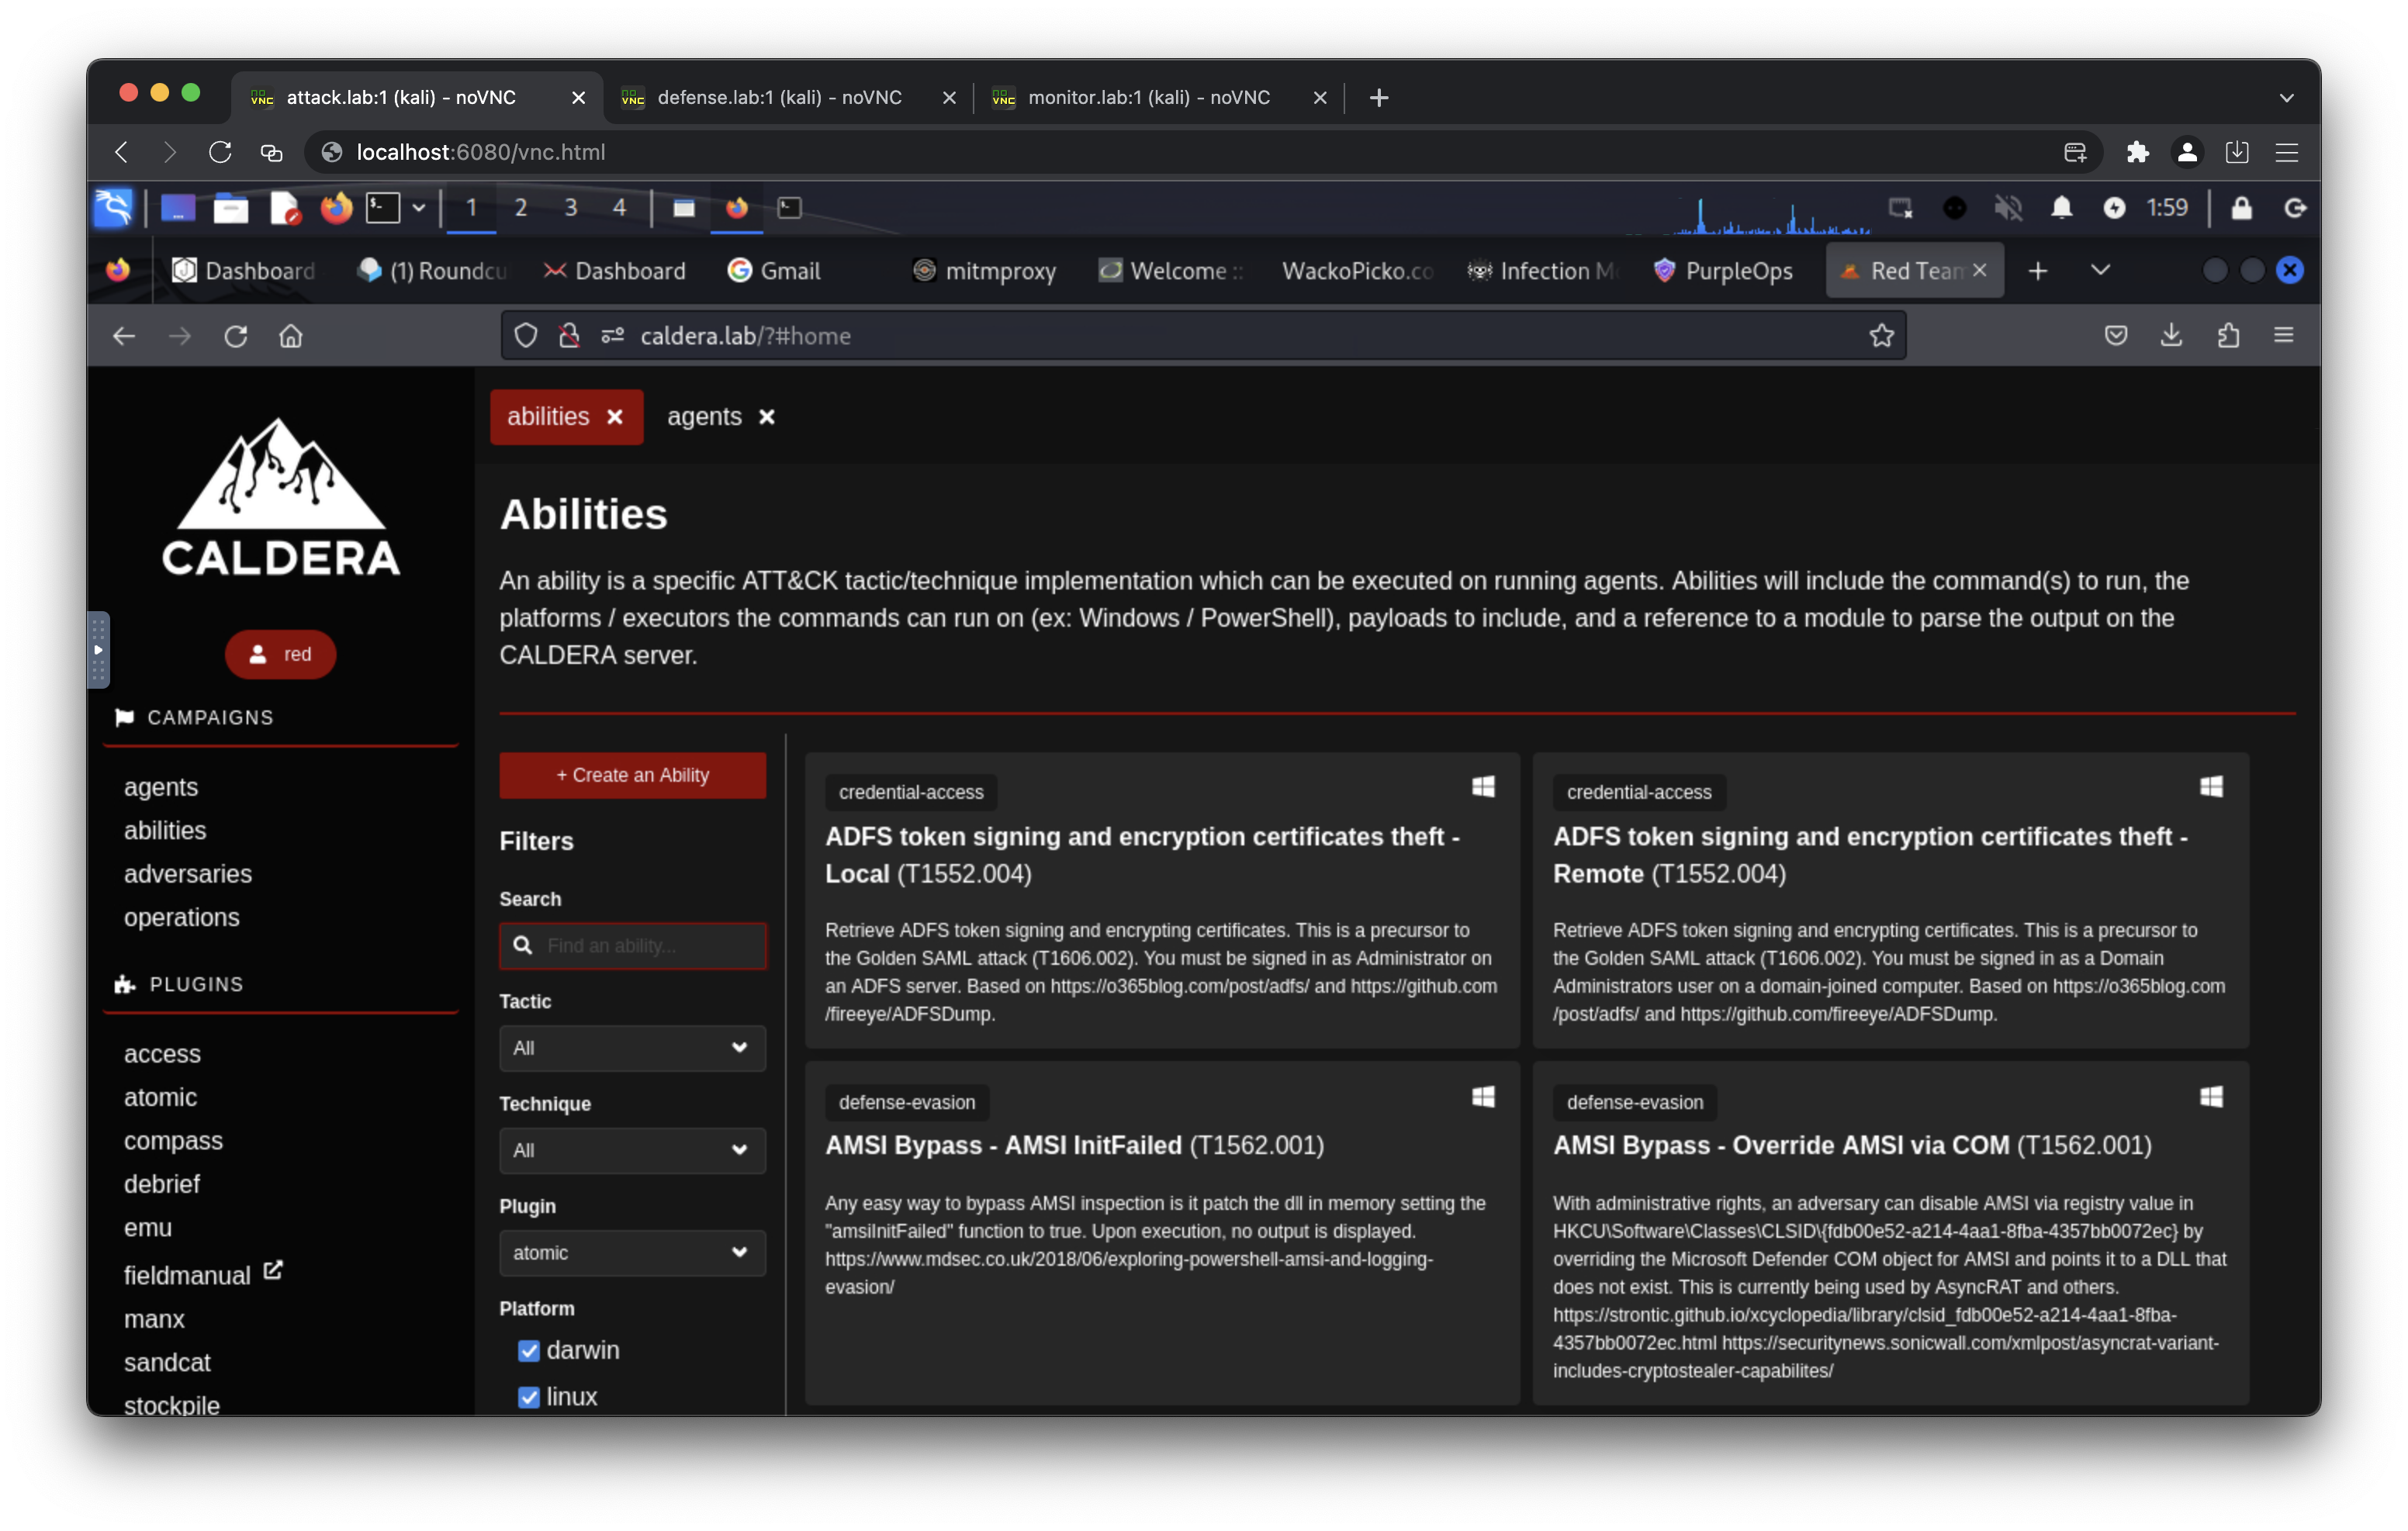
 haidang-infosec/phantom-grid
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
 nccgroup/windowsjoblock
Windows Process Lockdown Tool using Job Objects
 falconforceteam/falcondash
Azure workbook dashboard that visualizes and explores detection performance metrics, helping security teams measure and proactively maintain their…
 abraxas/signal-server-dropwizard-admin
Signal-Server v20261007.0.0 - High - Remote - Privilege leftover - unauth Dropwizard admin :8081
 stillbigjosh/kube-reaper
Scans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
 abraxas/tomcat-rewrite-ns-loop
Apache Tomcat 11.0.27 - High - Remote - DoS - RewriteValve [NS] worker pin
 crussella0129/tricorne
a Fedora remix focused on pentesting and purple hat tooling
 top-celestial-company-ltd/dros-vep-lite
Open reference implementation of the VEP protocol (RFC-010): a deterministic sandbox and benchmark suite evaluating AI agent runtime containment…
 yandex-cloud-examples/yc-mk8s-sctphantom-mitigation
DaemonSet для митигации уязвимости CVE-2026-64564 (SCTPhantom)
 webhosting4u/copy-fail_detect_and_mitigate_cve-2026-31431
Detects exposure to CVE-2026-31431 (Copy Fail) and optionally mitigates by disabling the vulnerable algif_aead kernel module, providing verdicts and…
 digicred-oss/caos-os
Customer Assurance Operating System. Answer the security questionnaires your customers send you, once.