
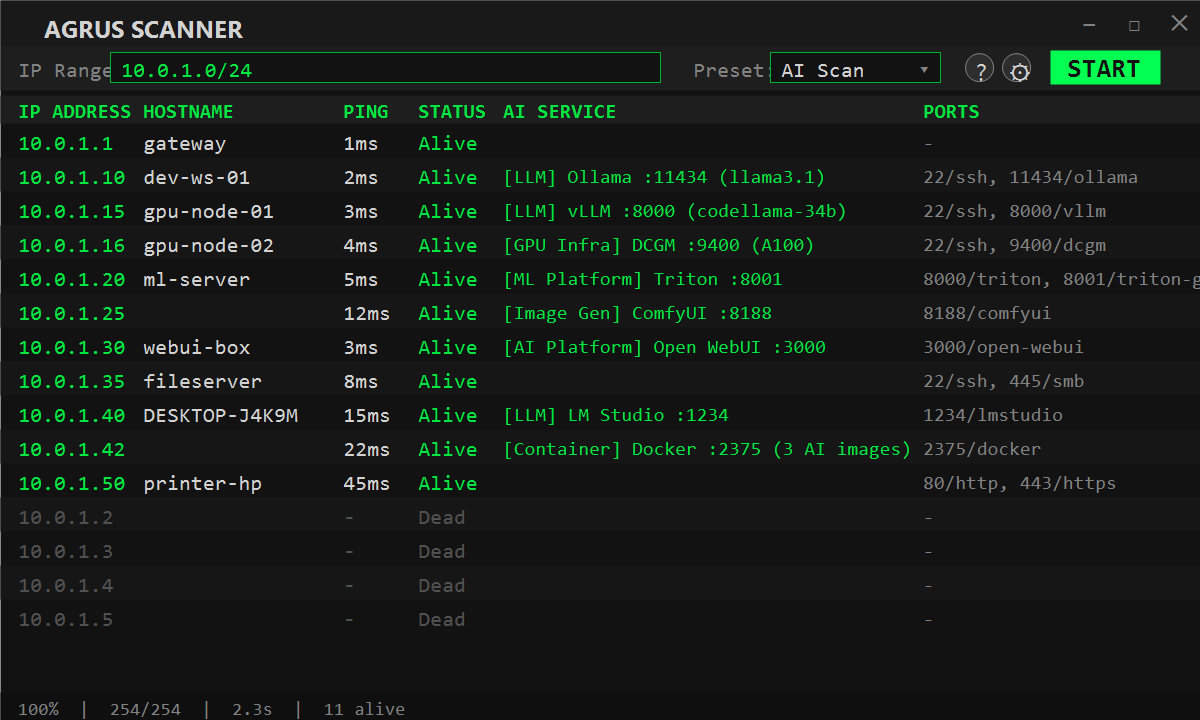
AgrusScanner
 nybaywatch/agrusscanner
Windows network reconnaissance scanner with ping sweeps, TCP port scanning, and deep AI/ML service detection for finding shadow AI, rogue LLM…
ai-securitydefensive-toolsinformation-gathering+6
26
nybaywatch/agrusscannerWindows network reconnaissance scanner with ping sweeps, TCP port scanning, and deep AI/ML service detection for finding shadow AI, rogue LLM…
 ssteelfactor-oss/kestrel
Low-observability Active Directory security enumeration tool using native ADSI/COM interfaces. Enumerates ACLs, delegation, trusts, ADCS, Kerberoast…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 runzeroinc/sshamble
Research tool that scans SSH services for authentication bypasses, timing leaks, weak keys, and post-session exposures, with JSON output and analysis.
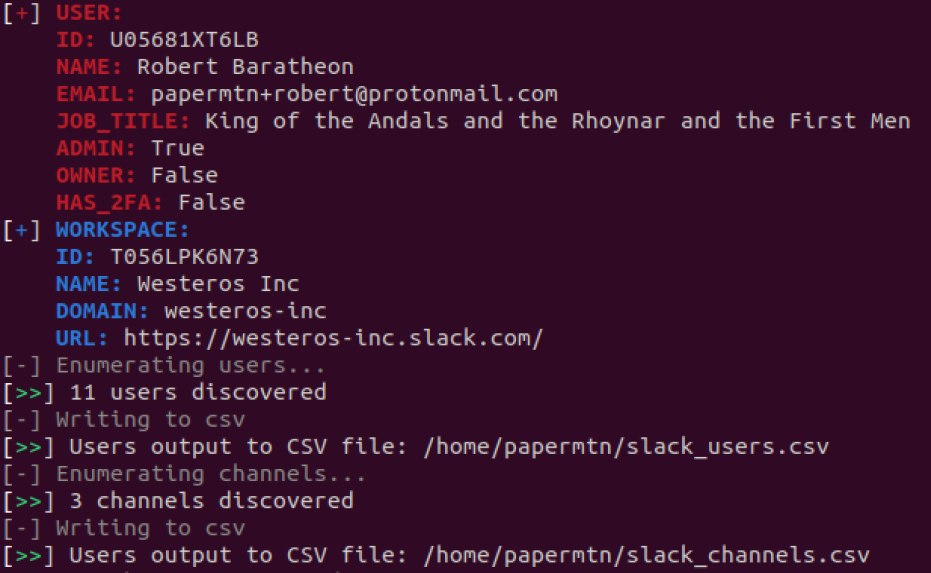 papermtn/slack-watchman
Slack enumeration and exposed secrets detection tool
 virologi-info/mssharepoint-scanner
A scanner for CVE-2026-55040 and CVE-2026-63520, designed to determine whether the server is affected by these two CVEs.
 spinfosecurity/rail-ot-protector
Rail-OT-Protector (ROP) — free, open-source cybersecurity scanning tool for rail and transit OT/SCADA networks. PowerShell + Bash scanners for…
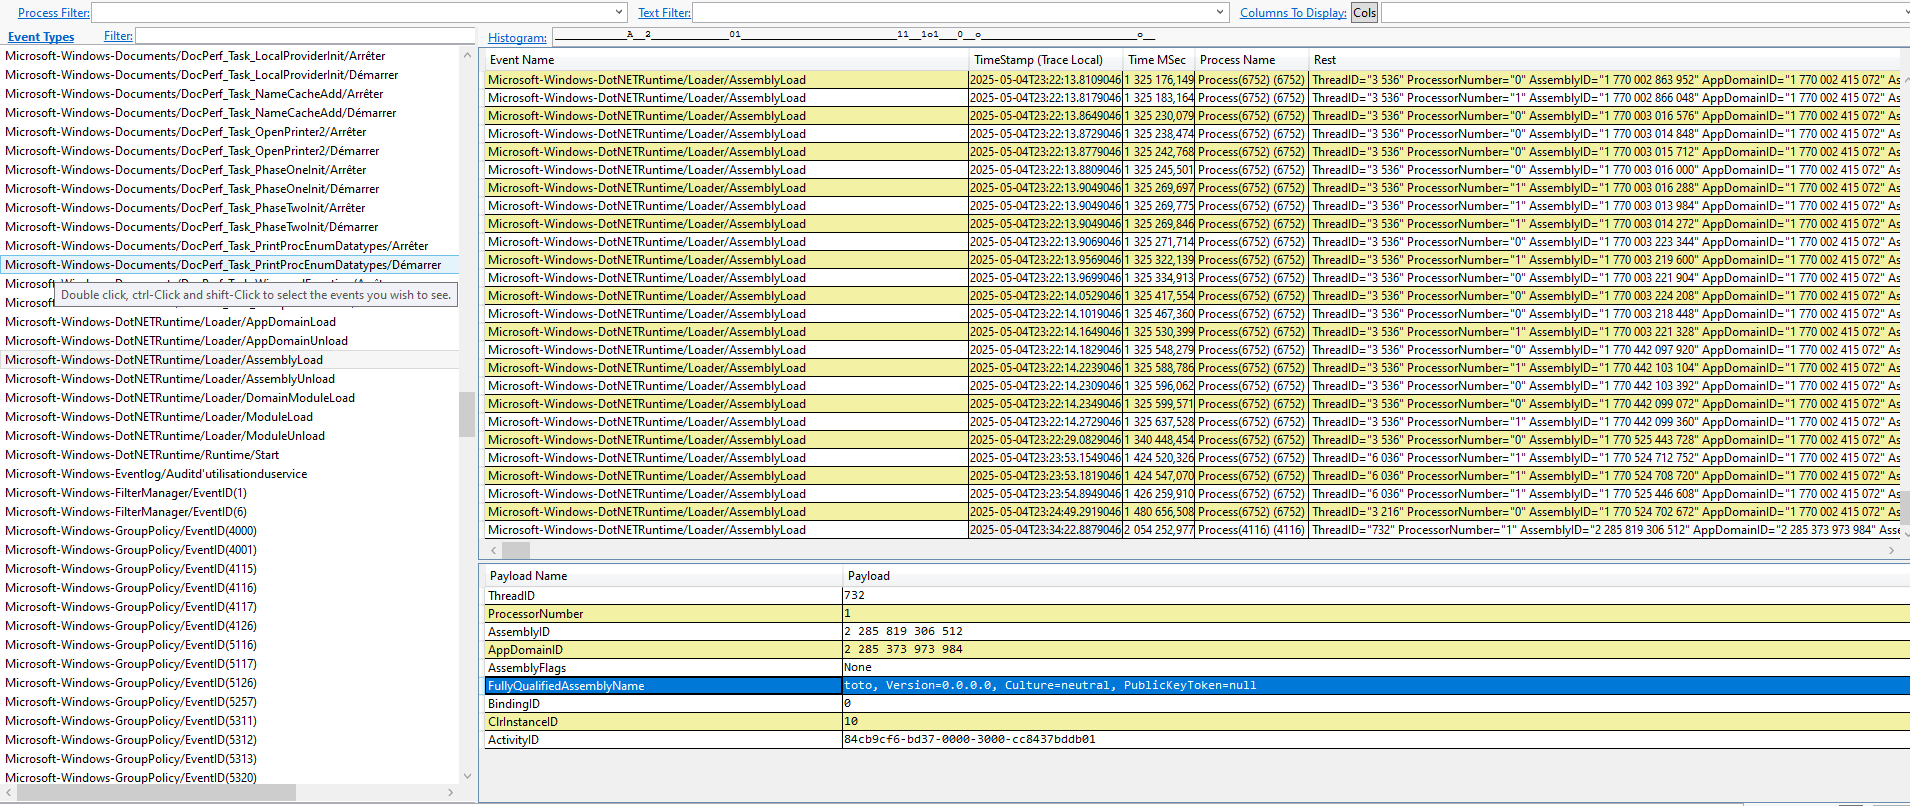 synacktiv/metamorph
A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.
 shizuku198411/cve-2026-0300
Non-destructive exposure survey tool for assessing PAN-OS User-ID Authentication Portal surfaces related to CVE-2026-0300, performing safe HTTP(S)…
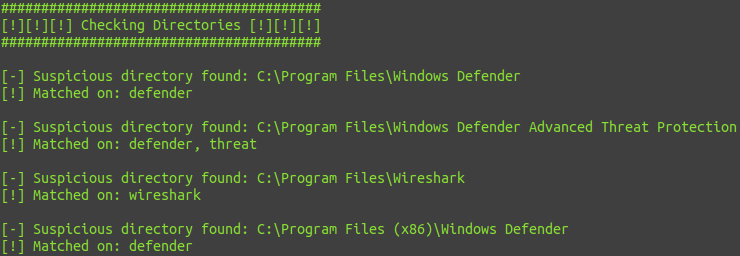 pwndexter/sharpedrchecker
C# tool that enumerates running processes, loaded DLLs, installed services, and drivers to detect the presence of AV, EDR, and logging products,…
 cisagov/untitledgoosetool
Untitled Goose Tool is a robust and flexible hunt and incident response tool that adds novel authentication and data gathering methods in order to…
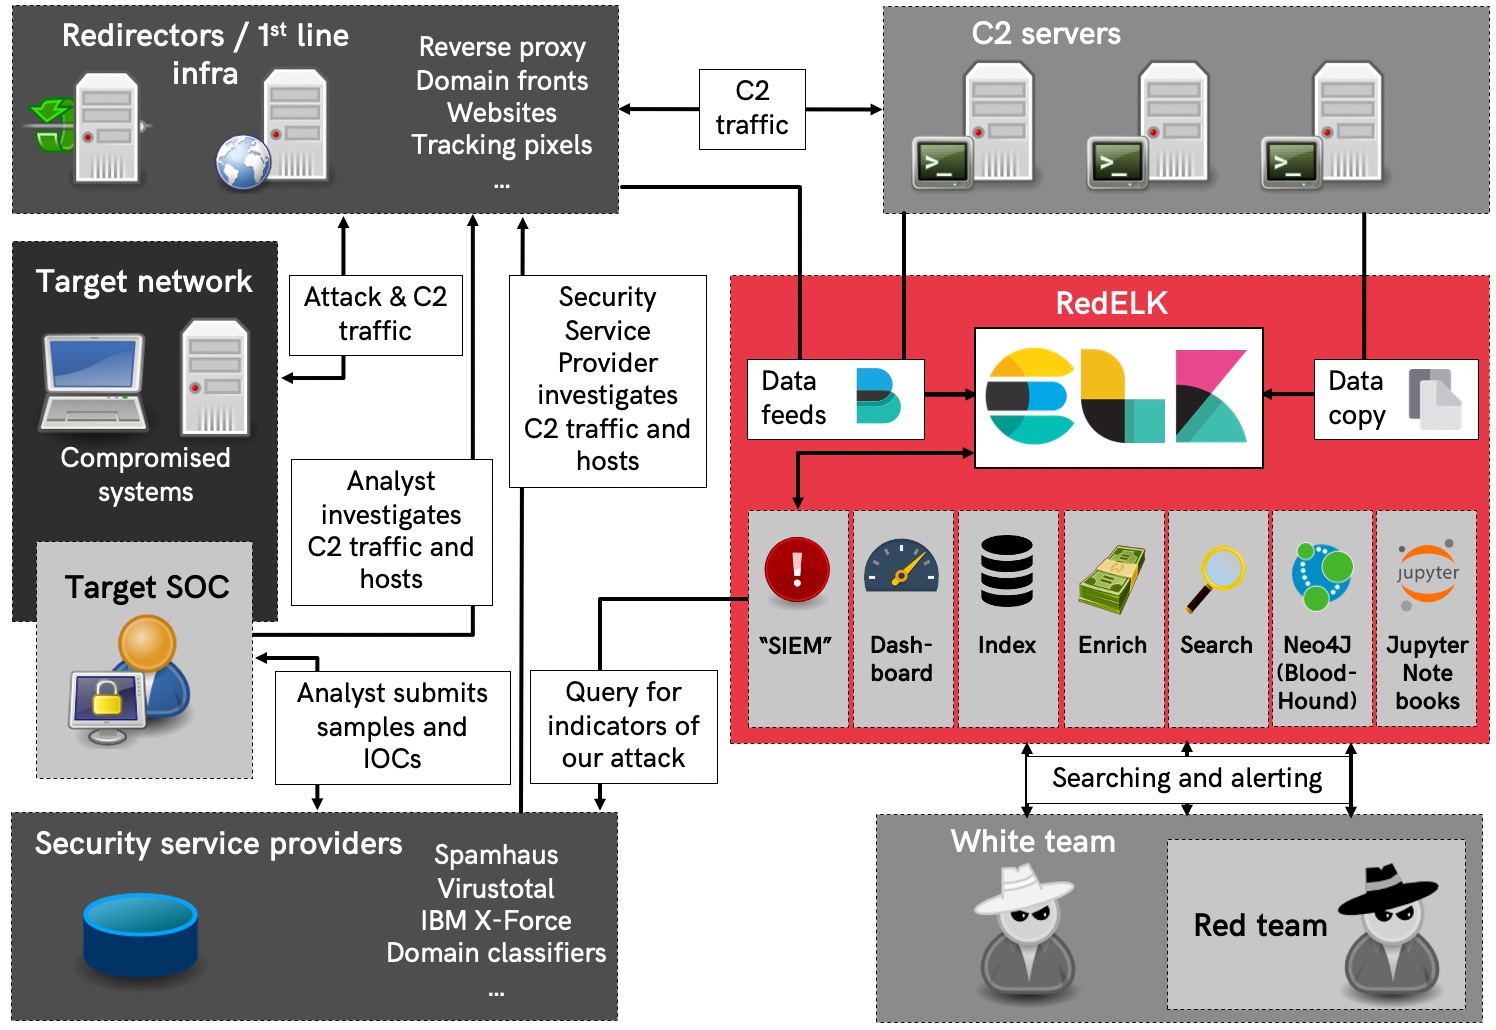 outflanknl/redelk
Red Team's SIEM - tool for Red Teams used for tracking and alarming about Blue Team activities as well as better usability in long term operations.
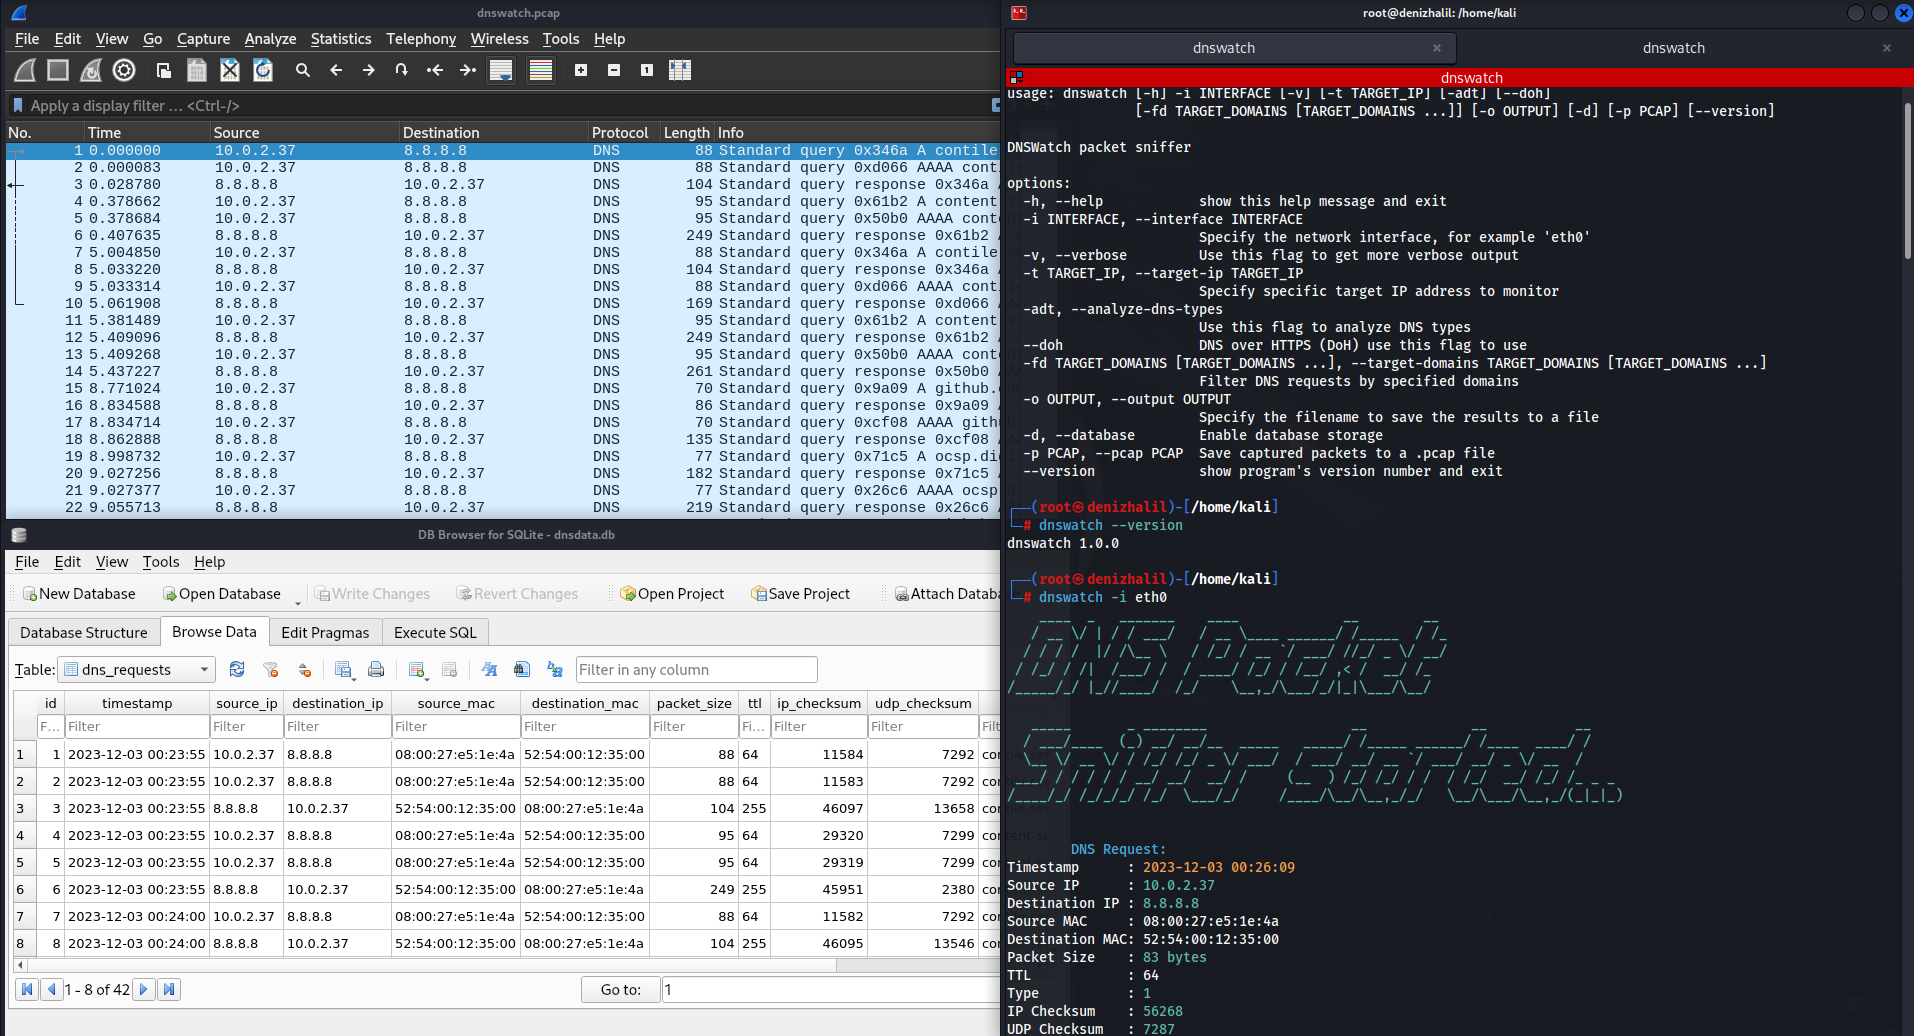 halildeniz/dnswatch
DNS traffic sniffer and analyzer for monitoring, filtering, and detecting anomalies in DNS queries. Features include PCAP export, DoH support, and a…
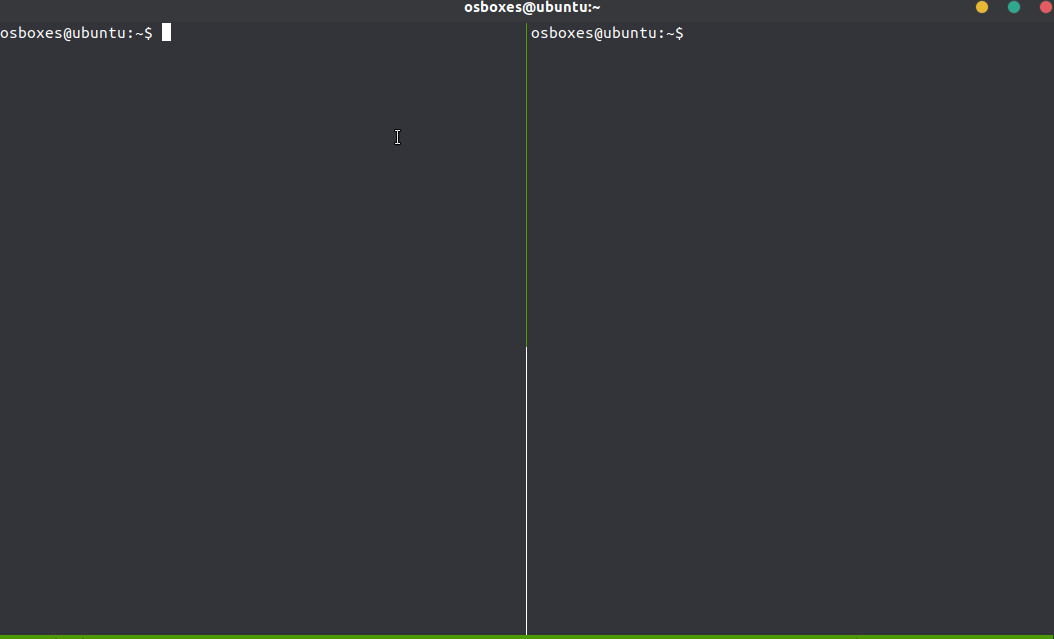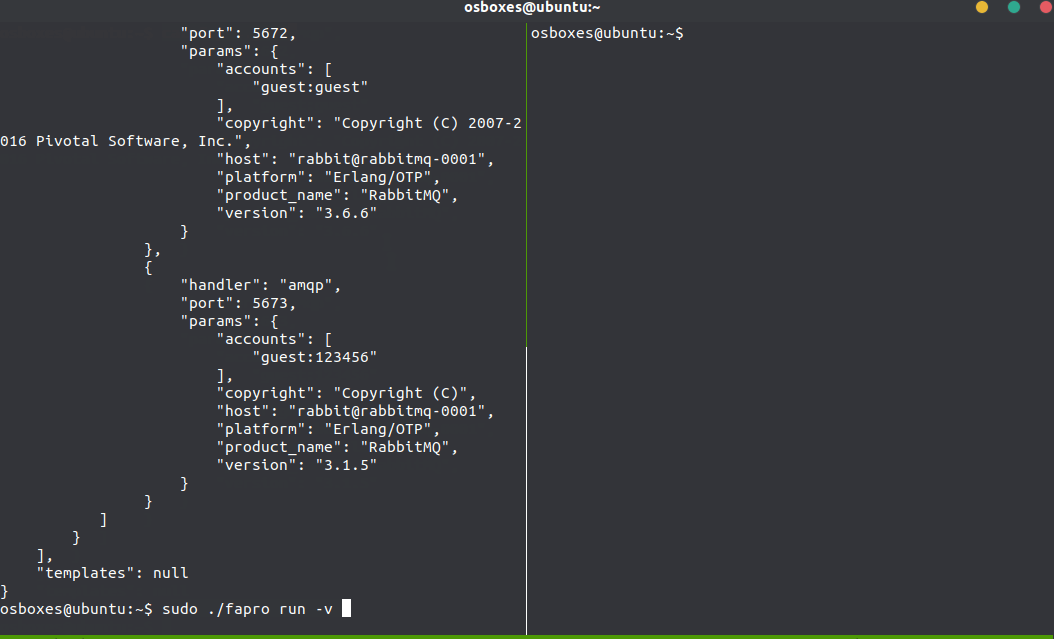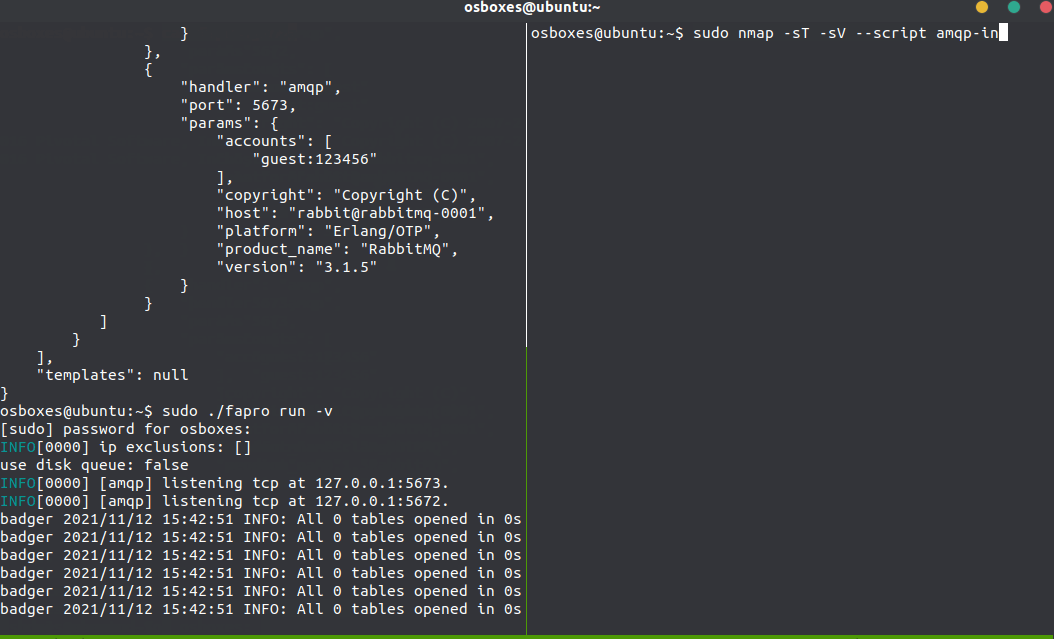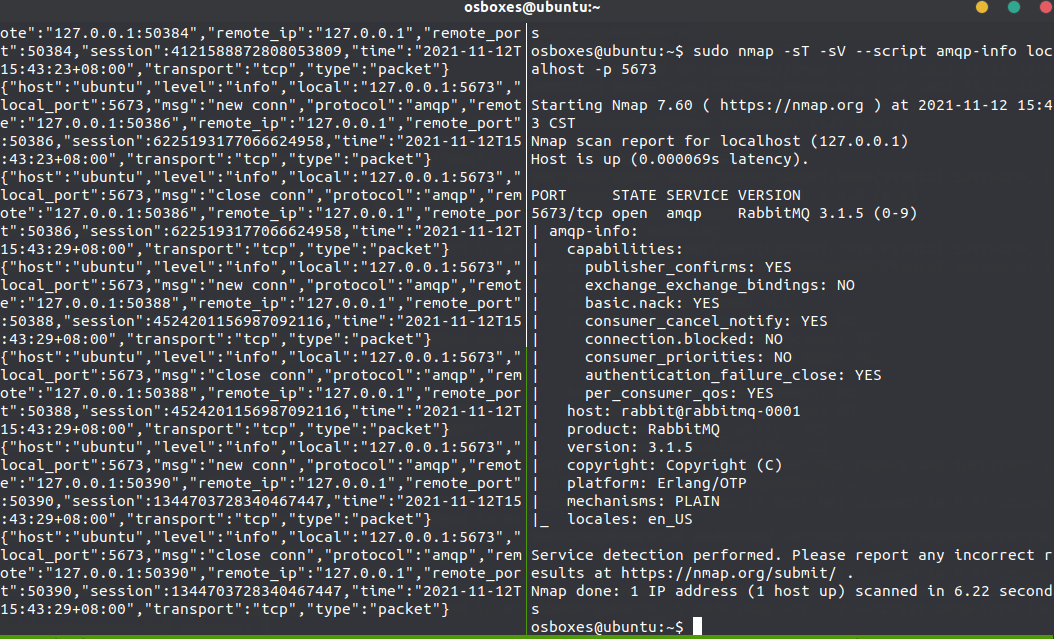 fofapro/fapro
Multi-protocol honeypot simulator supporting 50+ network services with deep interaction, TCP/UDP/ICMP logging, JA3 fingerprinting, and virtual…
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
 gmh5225/disclosure-check
Tool to identify the best mechanisms for privately disclosing a security vulnerability for a package/project.
 gmh5225/github-gato
GitHub Self-Hosted Runner Enumeration and Attack Tool
 assurancemaladiesec/ad-description-password-finder
Retrieve AD accounts description and search for password in it