
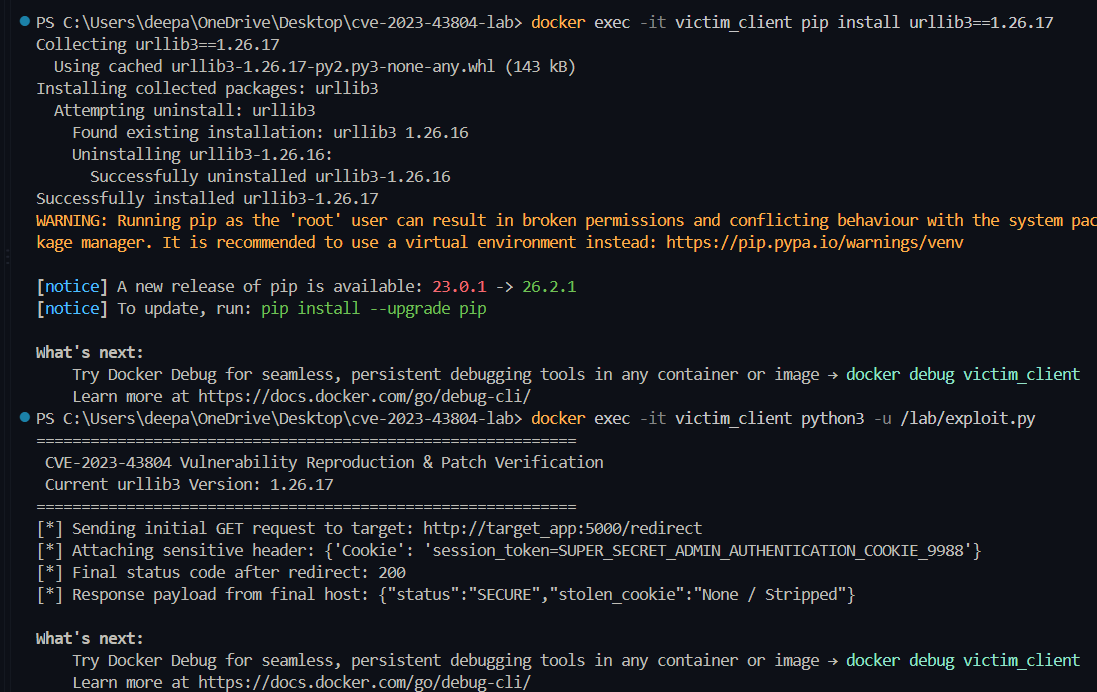
CVE-2023-43804
 deepanshu-khurana/cve-2023-43804
Containerized three-tier lab reproducing CVE-2023-43804 urllib3 cookie leak via cross-origin redirects, with exploit script and patch verification.
container-securitydefensive-toolseducation+5
deepanshu-khurana/cve-2023-43804Containerized three-tier lab reproducing CVE-2023-43804 urllib3 cookie leak via cross-origin redirects, with exploit script and patch verification.
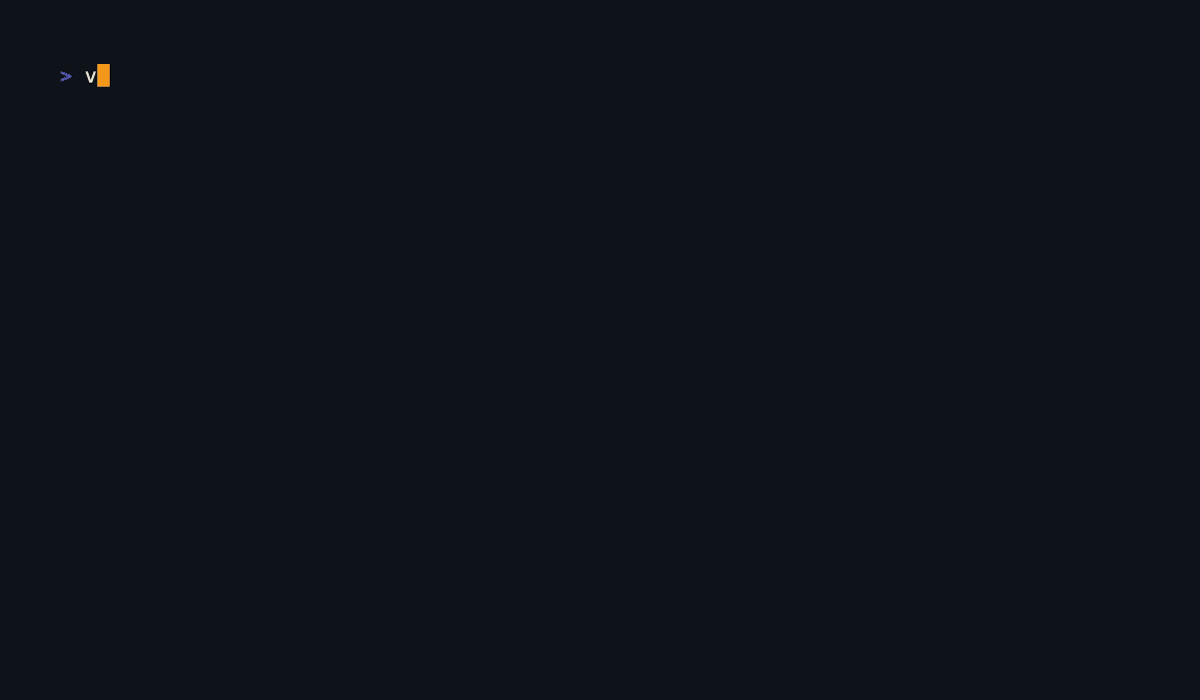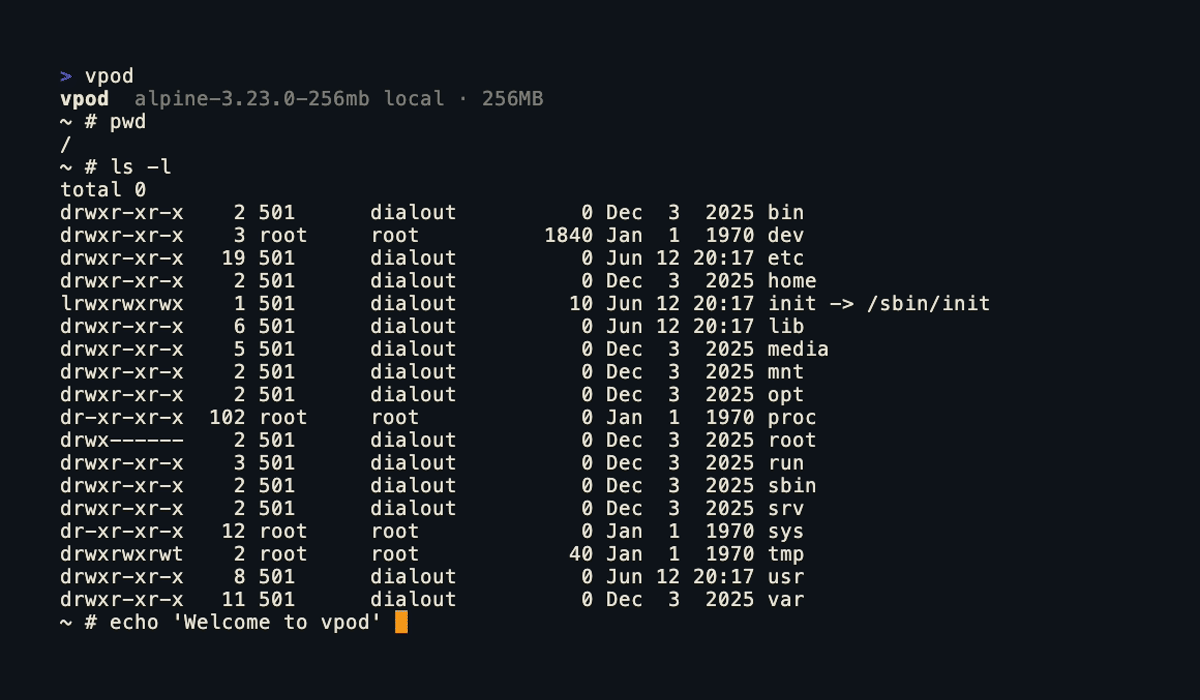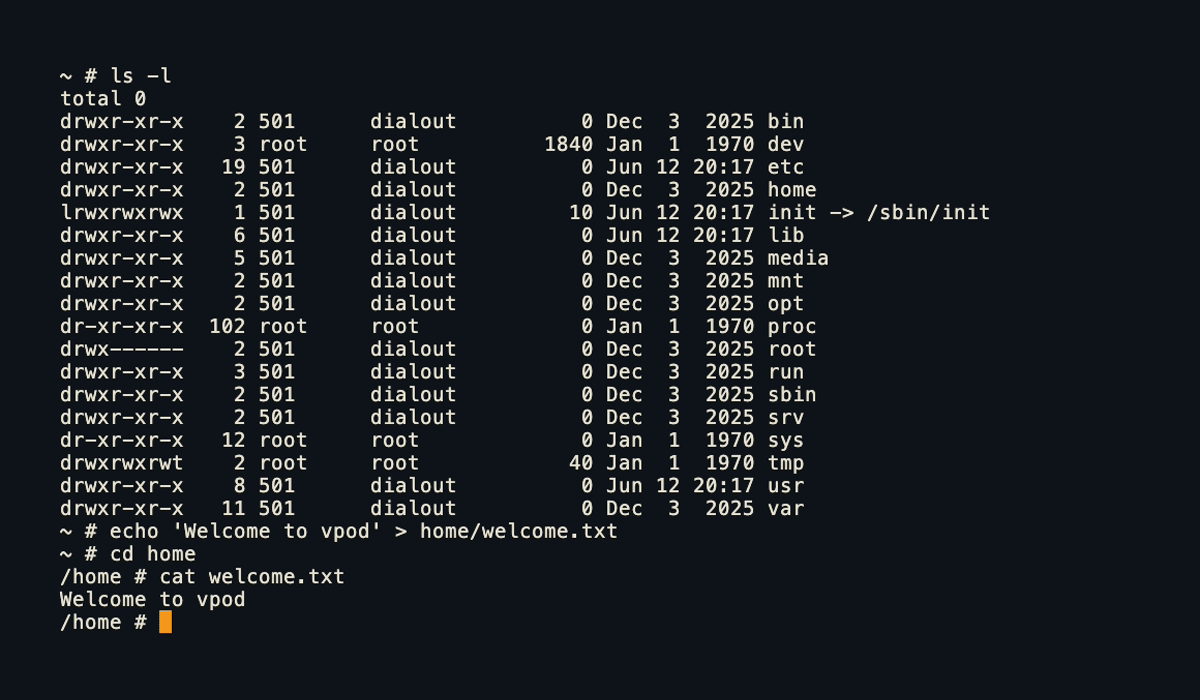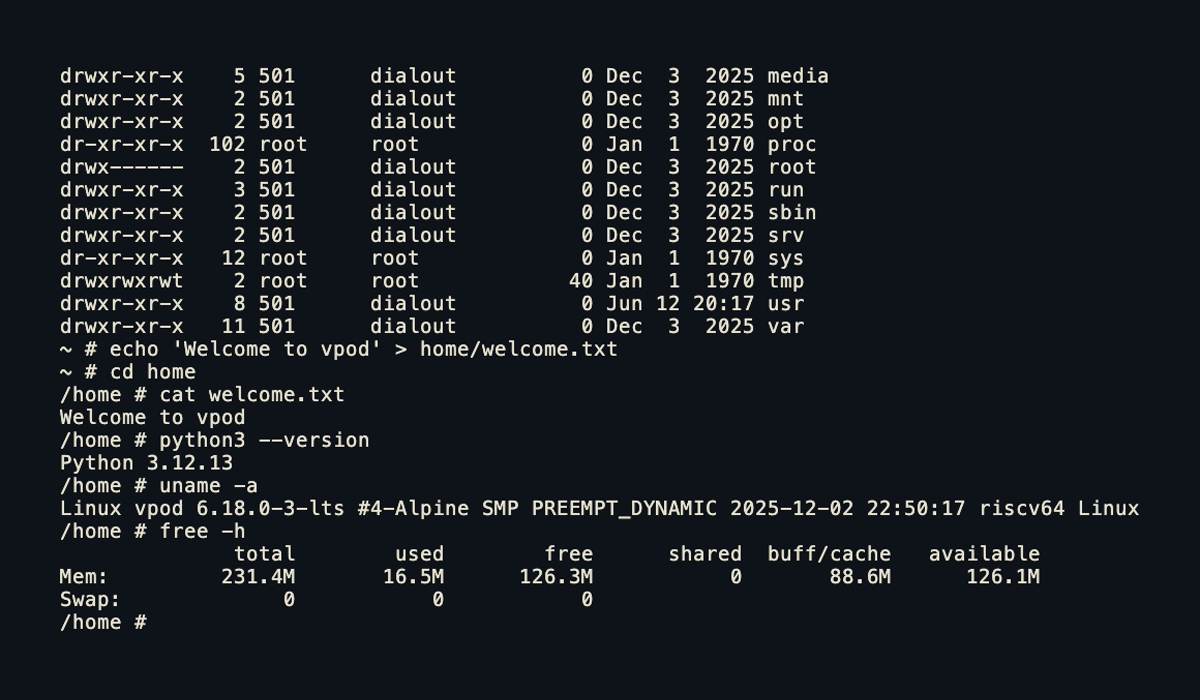 capsulerun/vpod
Lightweight, secure Linux sandboxes for untrusted processes. Runs in the browser and on the server.
 amulyakaushik/cve-2023-27163-lab
Docker-based lab reproducing CVE-2023-27163 SSRF in Request-Baskets, with exploitation verification, detection script, and network-isolation…
 shambhavim18/cve-2019-15107-lab
Docker-based lab demonstrating CVE-2019-15107, the Webmin unauthenticated RCE, covering deployment, exploitation, detection, and remediation.
 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
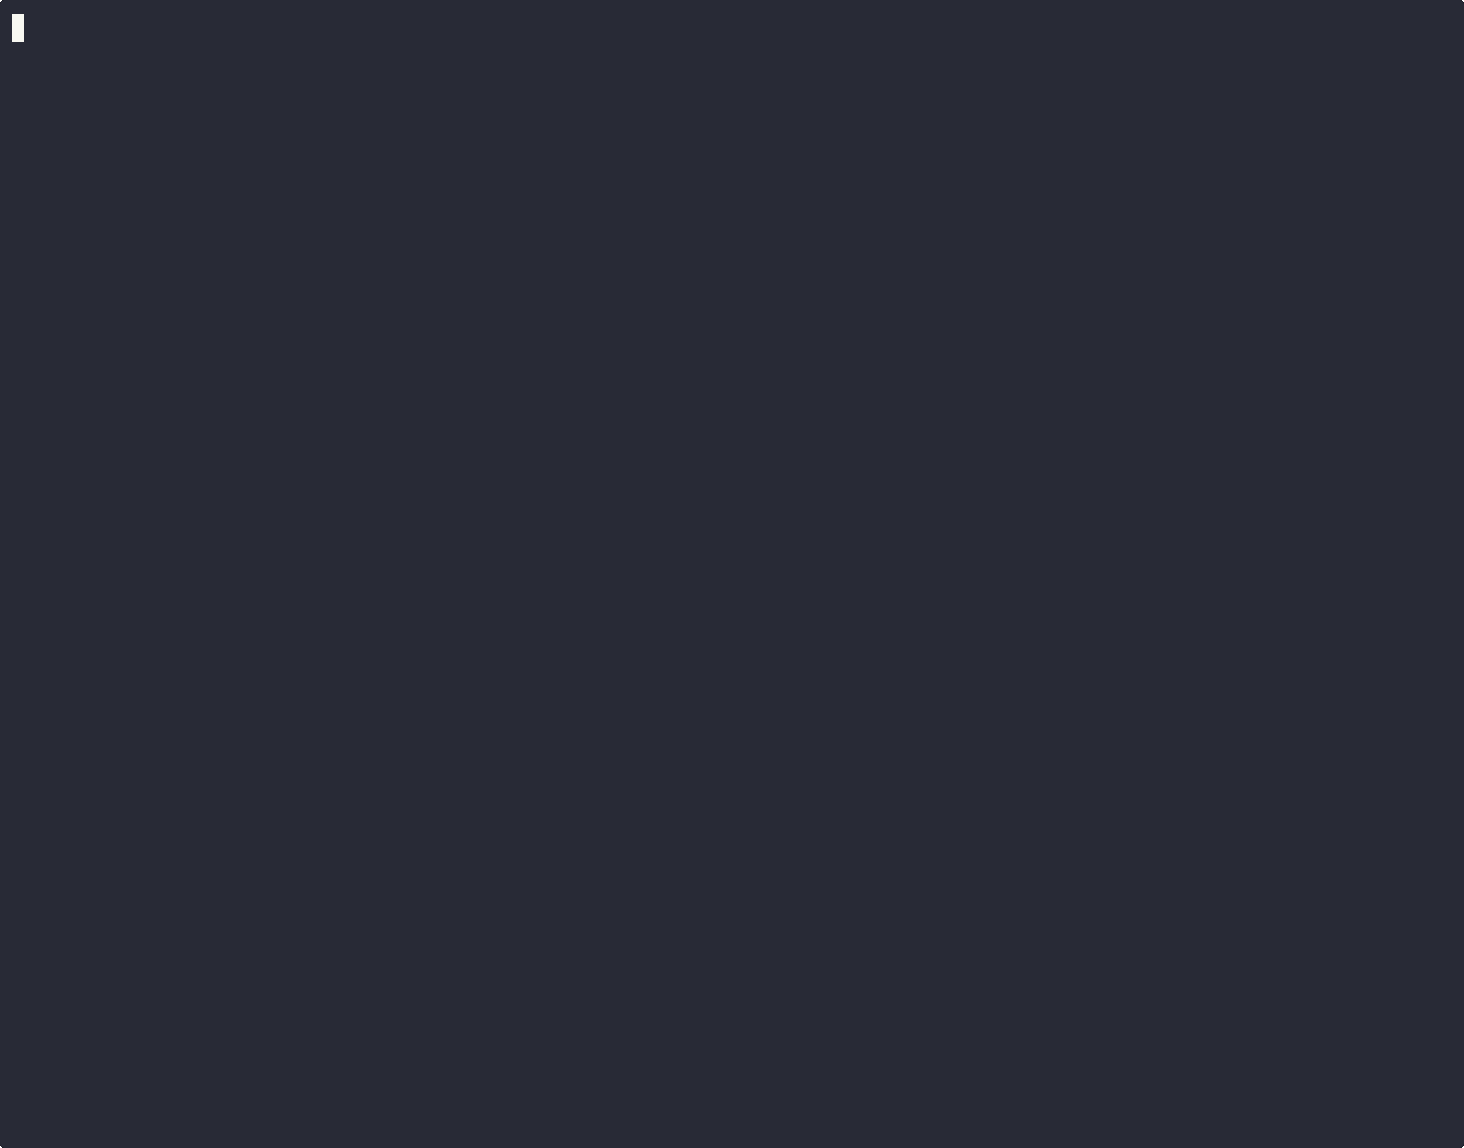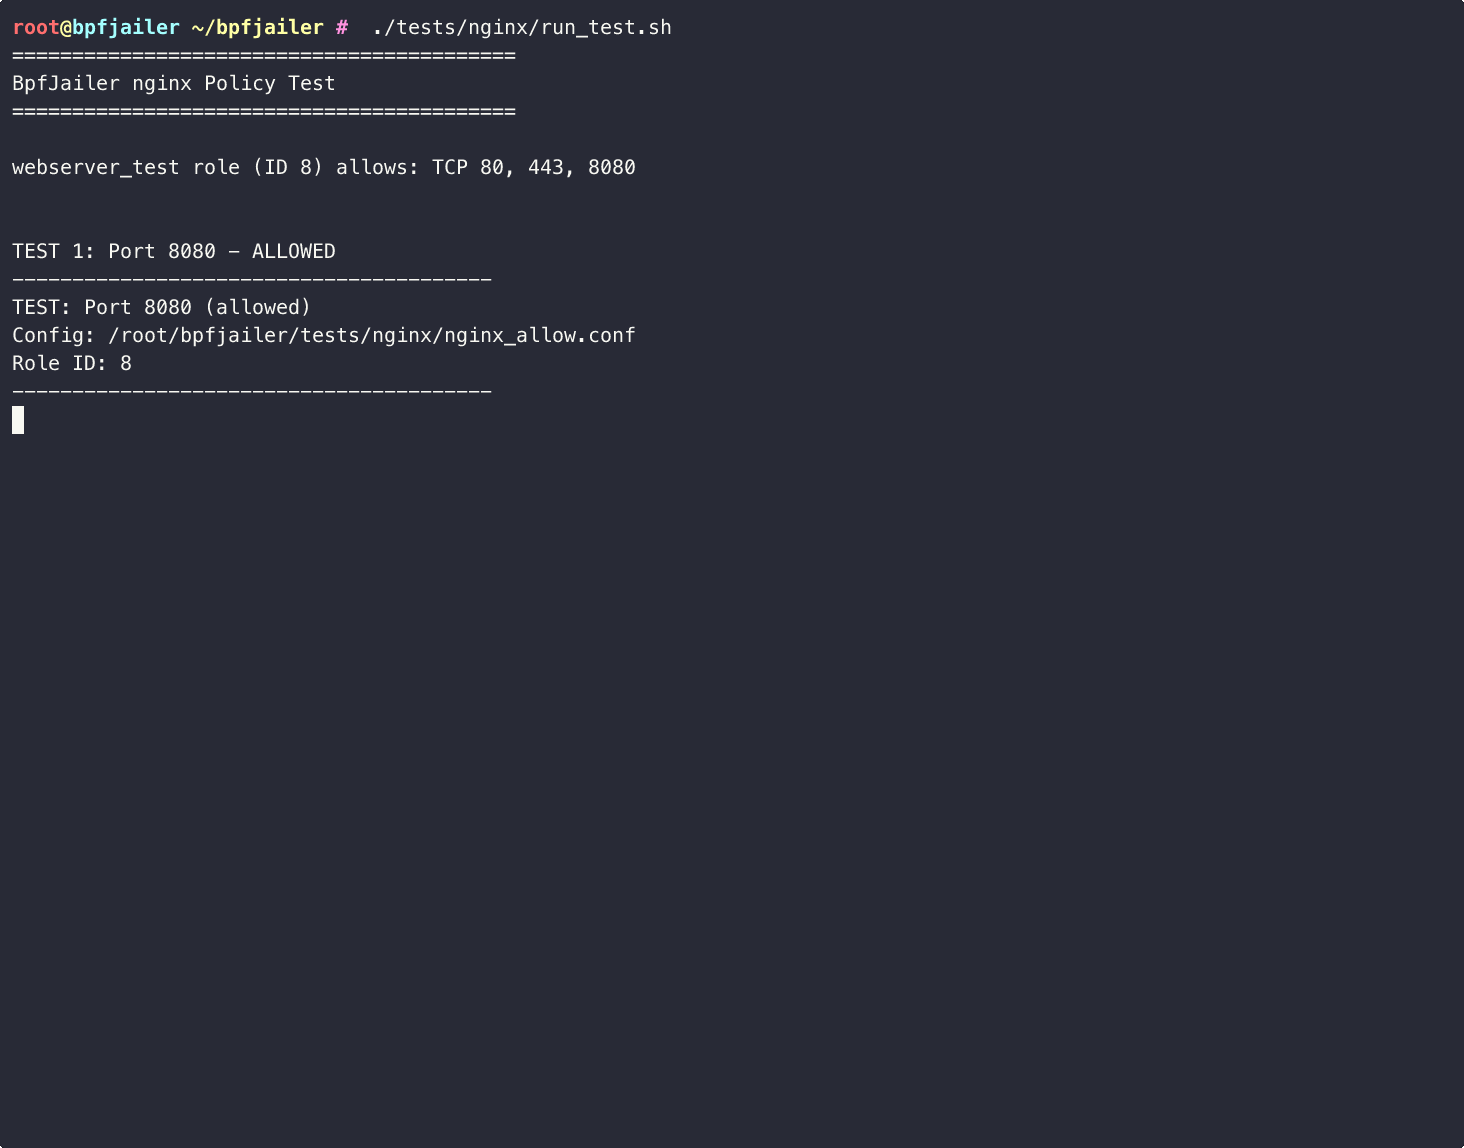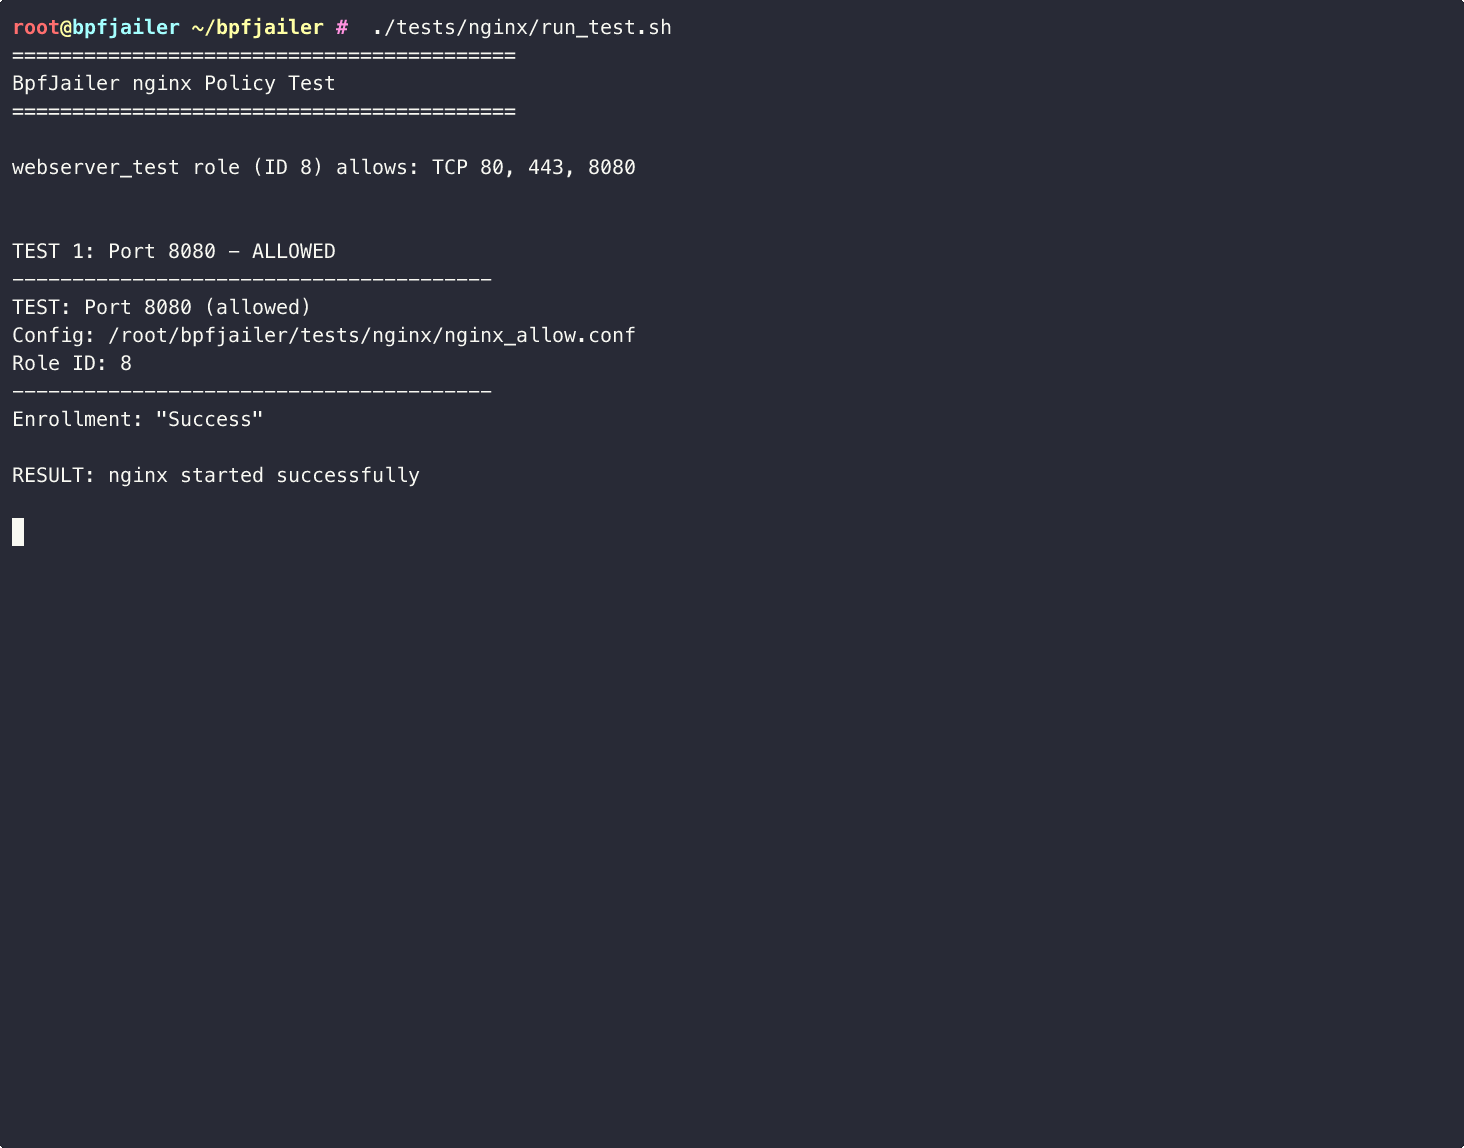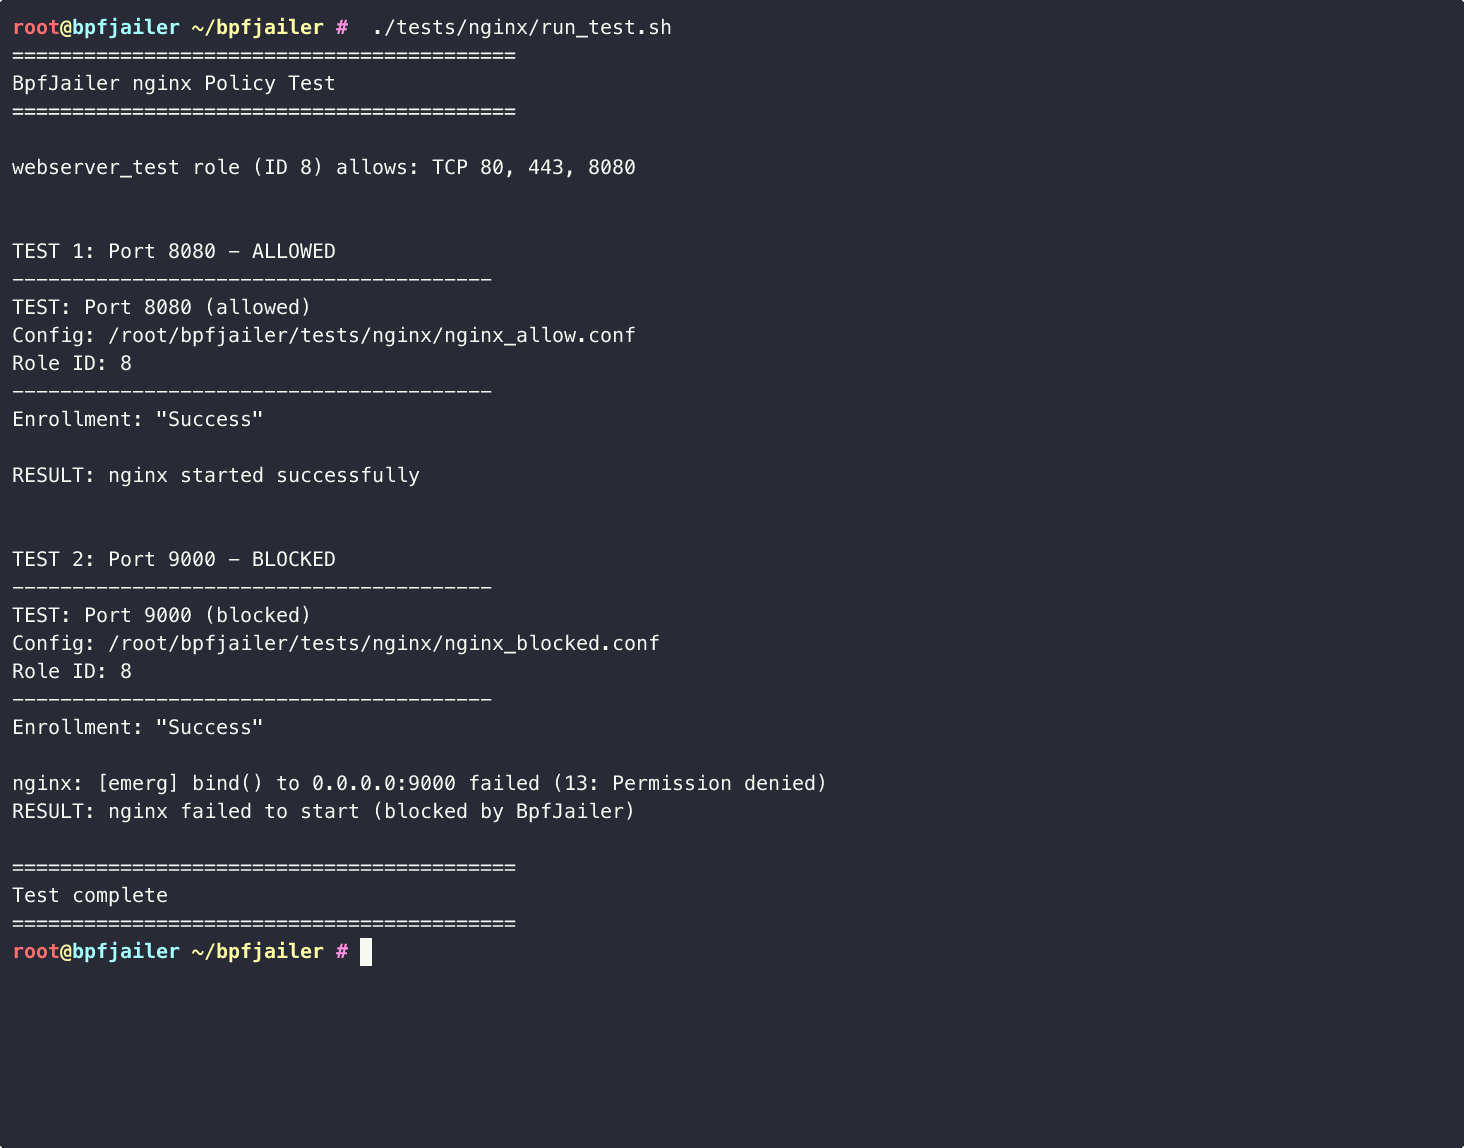 gen0sec/jailer
Jailer is an eBPF-based process jailing system that provides mandatory access control (MAC) for Linux. It tracks processes using BPF task_storage…
 kubearmor/kubearmor
Runtime Security Enforcement System. Workload hardening/sandboxing and implementing least-permissive policies made easy leveraging LSMs (LSM-BPF,…
 aquasecurity/tracee
Linux Runtime Security and Forensics using eBPF
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
 facebook/threatexchange
Trust & Safety tools for working together to fight digital harms.
 fencesandbox/fence
Lightweight, container-free sandbox for running commands with network and filesystem restrictions
 xtuc/airgap
Security for the modern age of AI: defend against bad AI agents and malicious npm packages
 trailofbits/claude-code-devcontainer
Sandboxed devcontainer for running Claude Code in bypass mode safely. Built for security audits and untrusted code review.
 grepular/foxcage
Run Firefox in a rootless Podman container with dropped capabilities, isolated networking, and ephemeral storage to contain sandbox escapes and…
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
 wattocyber/detection-defense-library
Detection-engineering reference mapping Windows, cloud, container, identity, and ICS attack classes to Sigma rules, trust-boundary models, BYOVD…
 kunai-project/kunai
eBPF-based Linux security monitor and threat hunter providing chronologically ordered, container-aware events with on-host correlation for incident…
 ahndrewalters/projectsecurity-homelab
Hands-on homelab simulating the Log4Shell (CVE-2021-44228) vulnerability. Deploy Docker containers to build a vulnerable target and attacker machine,…