
HashSiphon
 ivancabrera02/hashsiphon
Extracts the current user's NetNTLMv2 hash via HTTP authentication proxying, avoiding direct SSPI calls; v2 delegates auth to the BITS service to…
defensive-toolsinformation-gatheringpassword-attacks+3
32
ivancabrera02/hashsiphonExtracts the current user's NetNTLMv2 hash via HTTP authentication proxying, avoiding direct SSPI calls; v2 delegates auth to the BITS service to…
 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
 apache/spamassassin
Open-source email filtering framework that detects spam and phishing using content analysis, header checks, Bayesian scoring, and DNS blocklists.
 gmh5225/anti_suspend
Protect process by shellcode
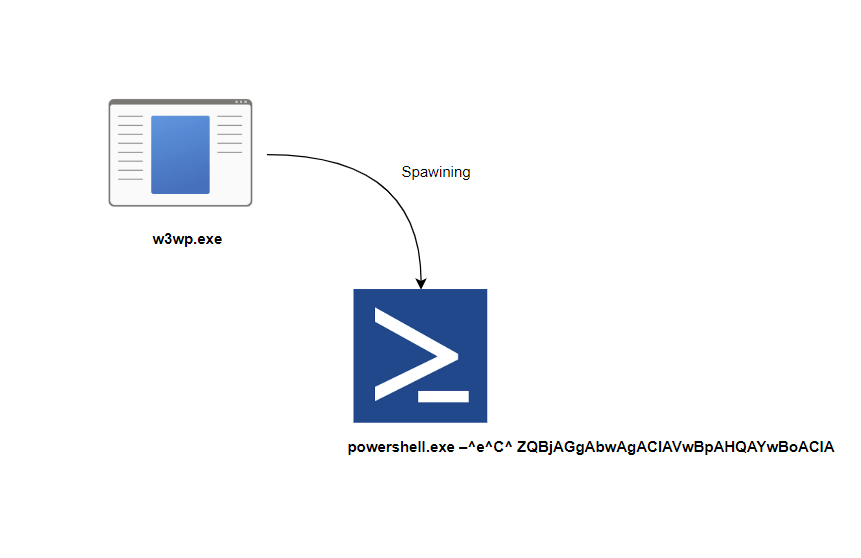 alwashali/detection-validation
Detection rule validation
 hotcakex/harden-windows-security
Harden Windows Safely, Securely using Official Supported Microsoft methods and proper explanation | Always up-to-date and works with the latest build…
 1-bit-wonder/kestrel
Single-host runtime-security dashboard on eBPF — Go agent + SvelteKit. Live process tree, network map, and rule-based alerts for plain Linux hosts.
 scoubi/bloodsocer
Aggregates MITRE ATT&CK, Sigma, and Atomic Red Team data into BloodHound graphs so SOC analysts can map detection coverage, identify gaps, and…
 nccgroup/detectwindowscopyonwriteforapi
Enumerate various traits from Windows processes as an aid to threat hunting
 mr-un1k0d3r/redteamccode
Red Team C code repo
 joe-desimone/patriot
In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
 mrezqi/cve-2021-1675_carbonblack_huntingquery
CarbonBlack hunting queries to detect PrintNightmare (CVE-2021-1675) exploitation via file, module load, and process events, based on Sigma rules.
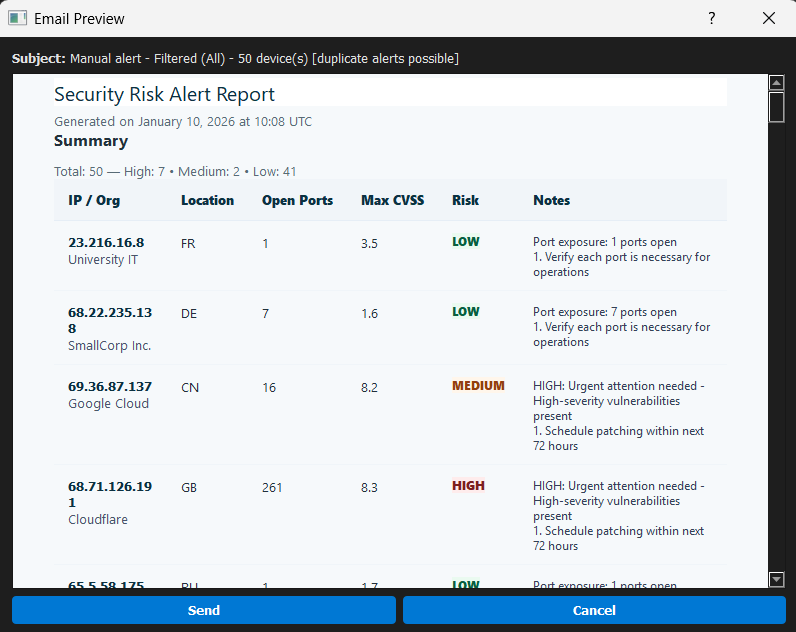 eclipsemanic/threatsentry-ai
ThreatSentry AI is an intelligent threat hunting dashboard that leverages machine learning to proactively identify and prioritize risks in your…
 torque59/nosqlpot
The NoSQL Honeypot Framework
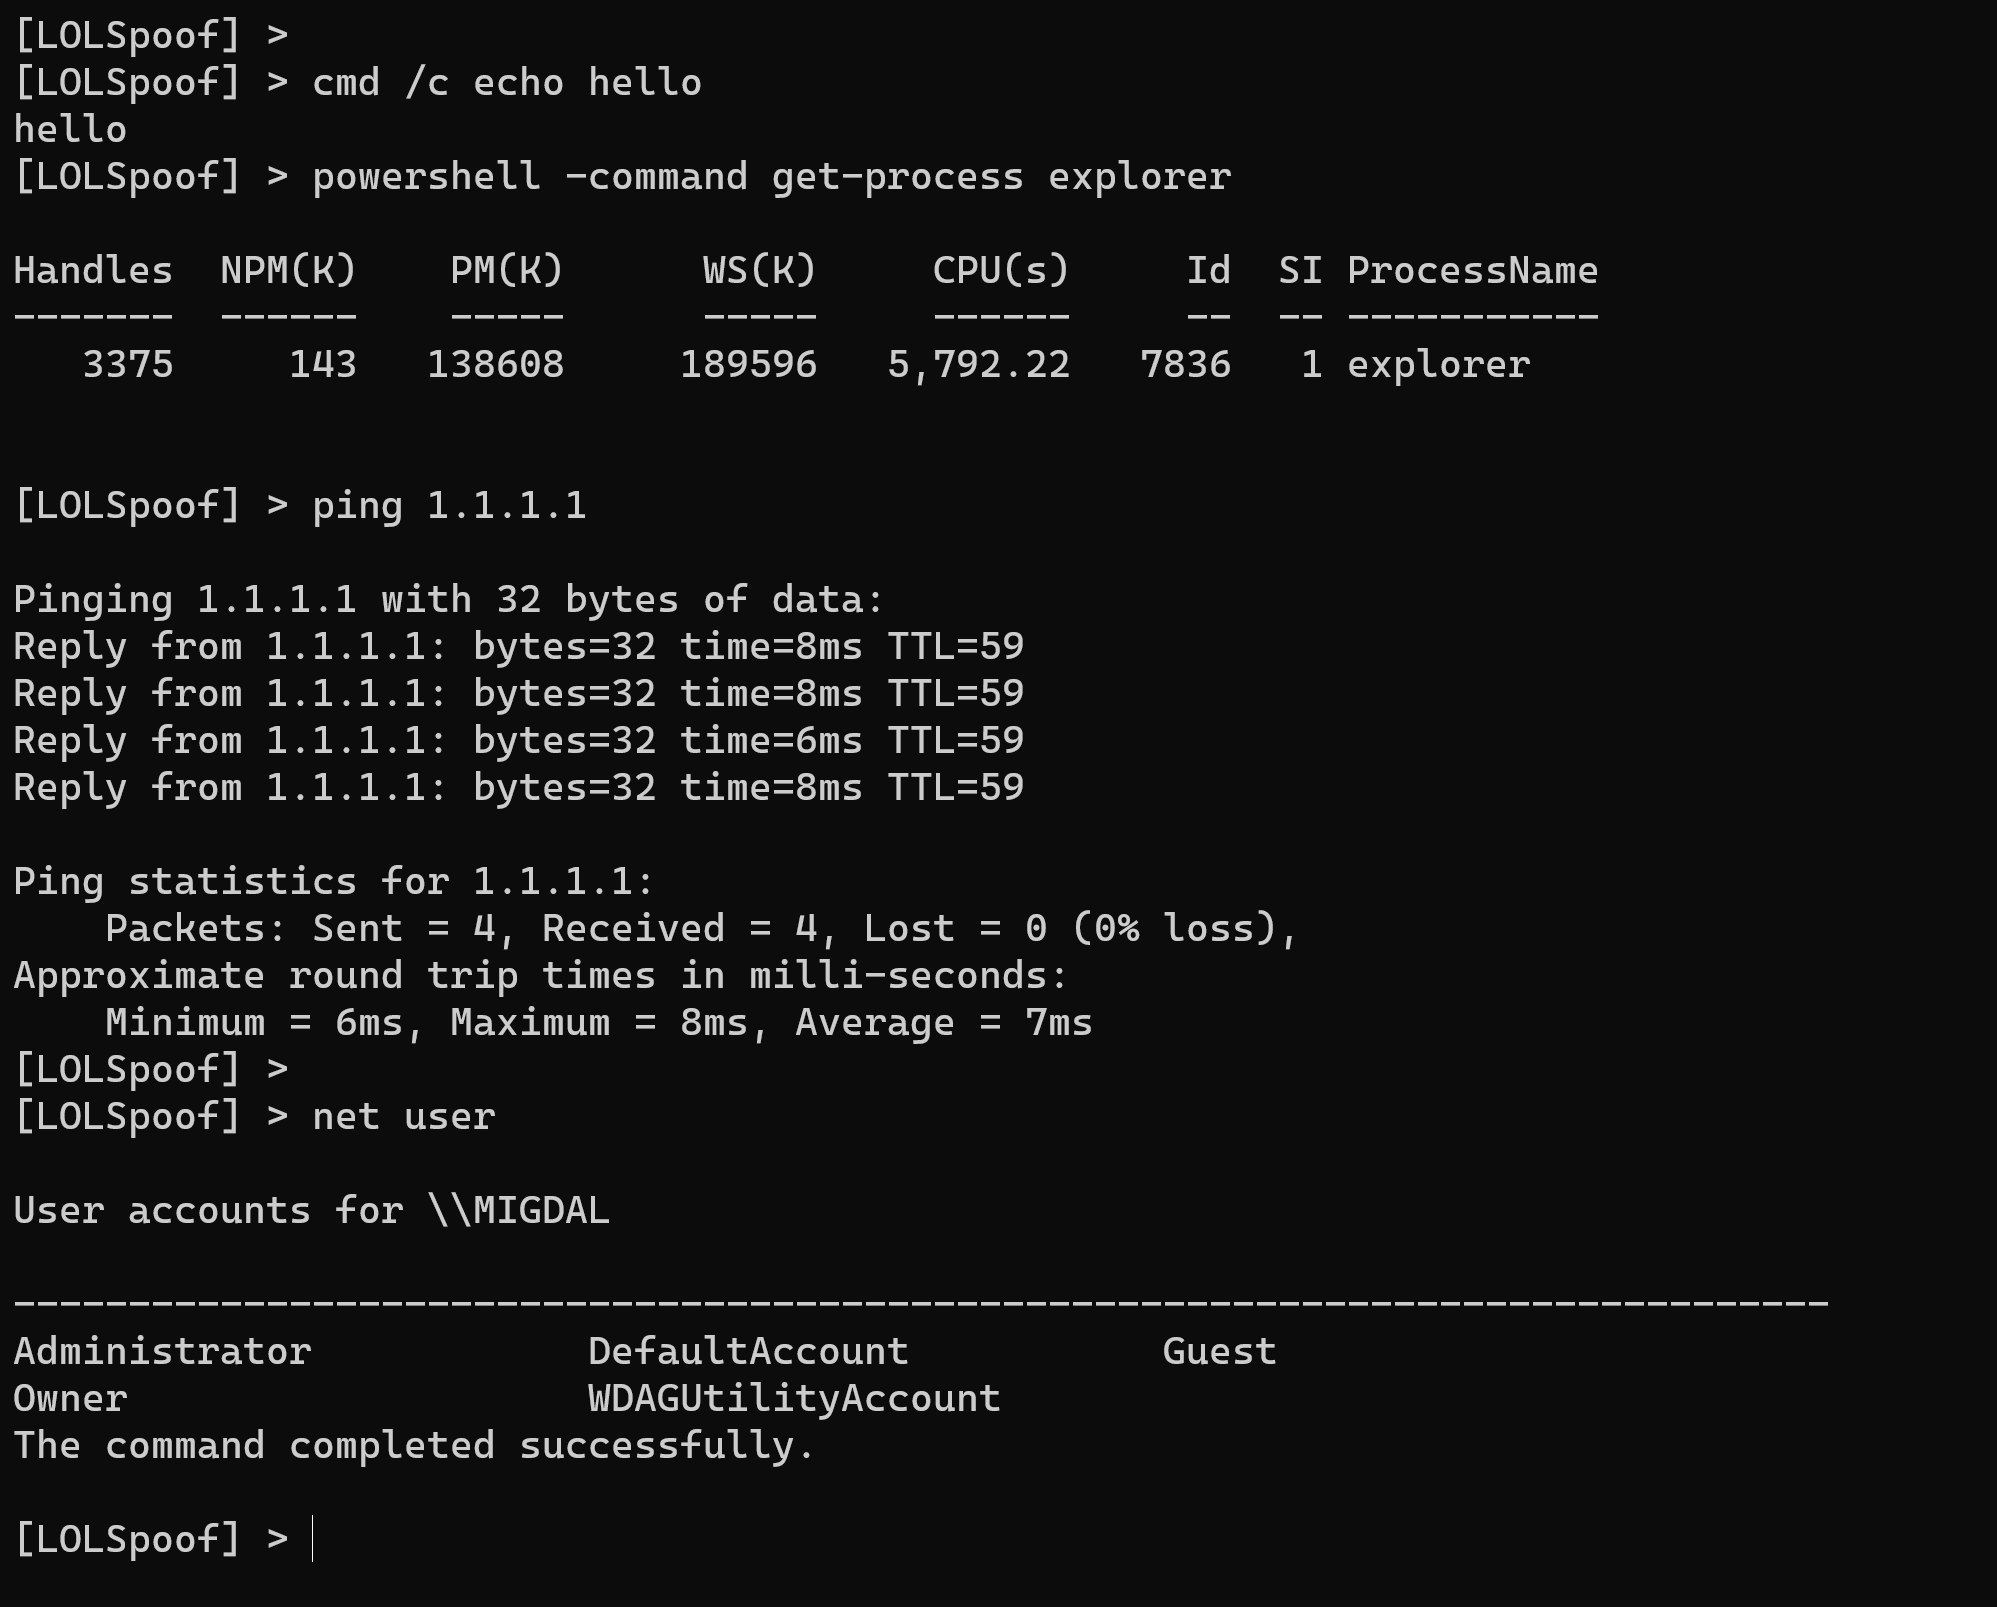 itaymigdal/lolspoof
An interactive shell to spoof some LOLBins command line
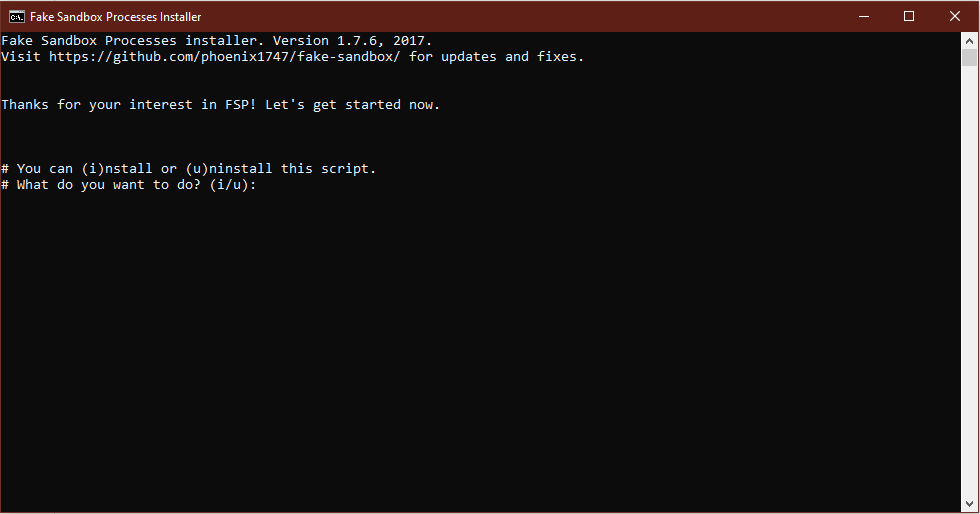 nuclearphoenixx/fake-sandbox
👁🗨 This script will simulate fake processes of analysis sandbox/VM software that some malware will try to avoid.
 rotemreiss/robusto
Robust Subdomain Takeover Tool
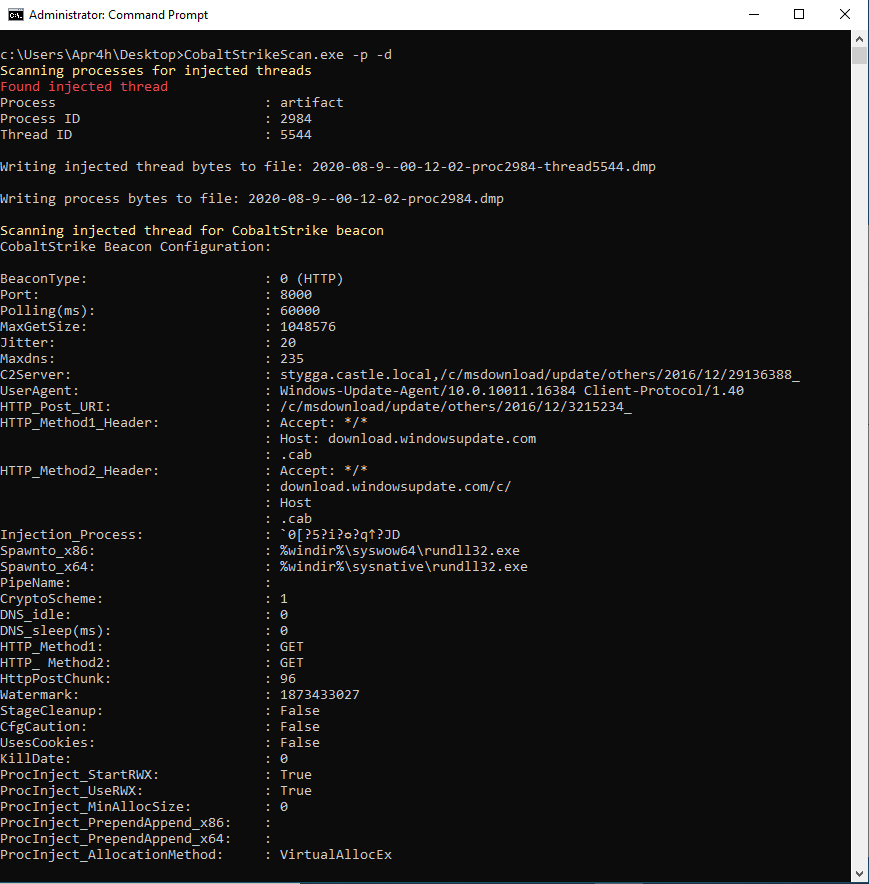 apr4h/cobaltstrikescan
Scan files or process memory for CobaltStrike beacons and parse their configuration