

LogsTotal
 wagga40/logstotal
Self-hosted multi-engine Sigma detection for event logs
defensive-toolsdigital-forensicsincident-response+5
wagga40/logstotalSelf-hosted multi-engine Sigma detection for event logs
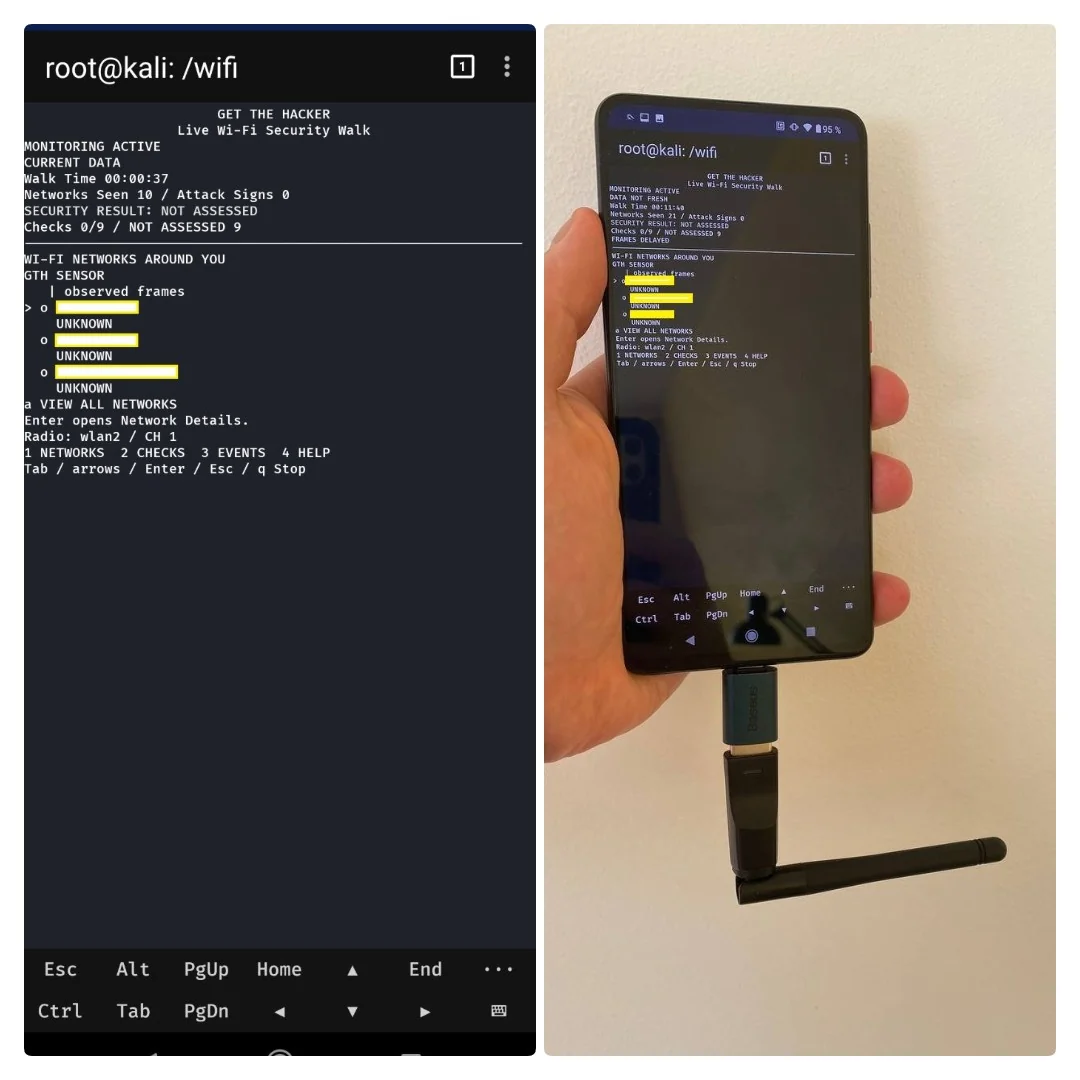 buybitart/get-the-hacker
Hunt WiFi threats silently. Catch the hackers.
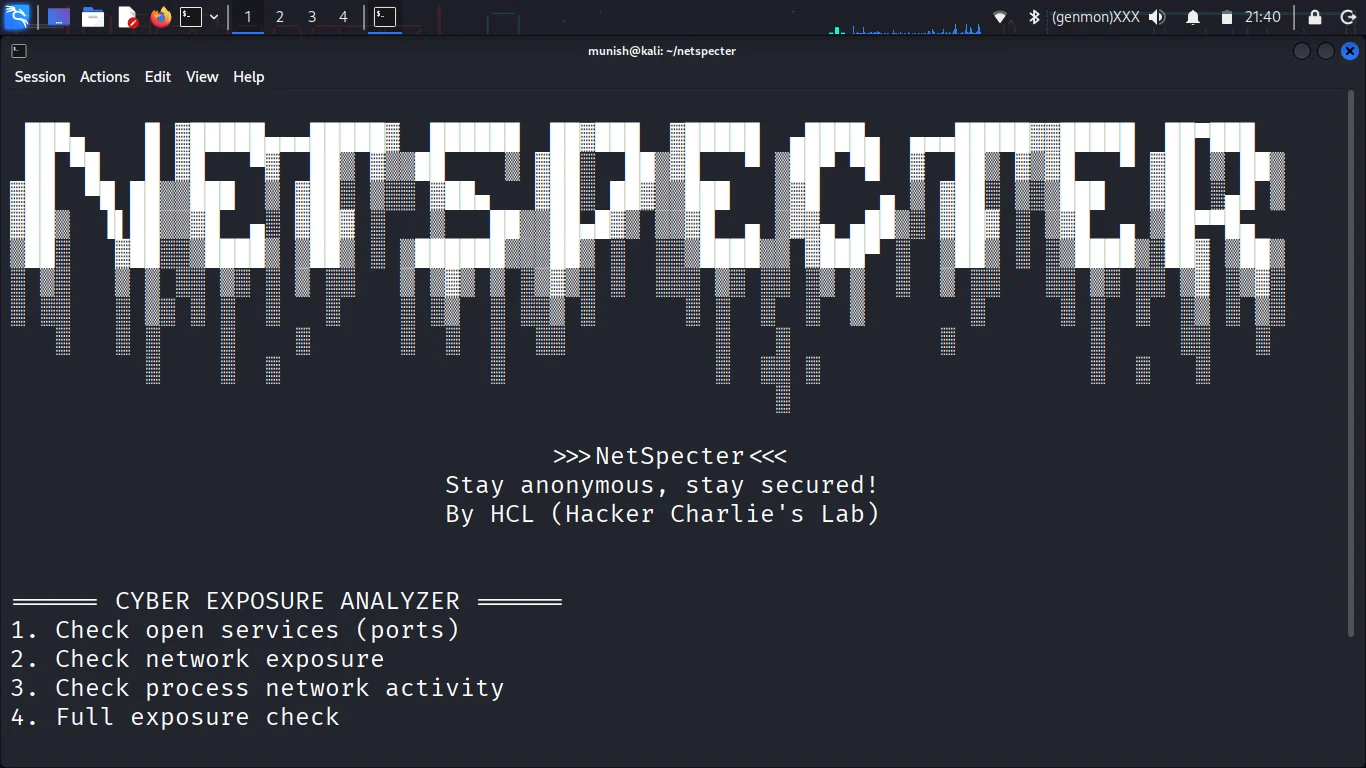 mrhackercharlie/netspecter
Real-time system monitoring tool for detecting process activity and network exposure!
 reloading01/certstream-server-rust
High-performance Certificate Transparency (CT) monitoring tool written in Rust. Real-time stream of newly issued SSL/TLS certificates from CT logs.…
 trustedsec/artillery
Open-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.
 foxboron/attezt
An open-source TPM device-attest-01 CA server
 msuhanov/easy_triage
Scripts to triage compromised systems (Linux, ESXi, FreeBSD/NetScaler)
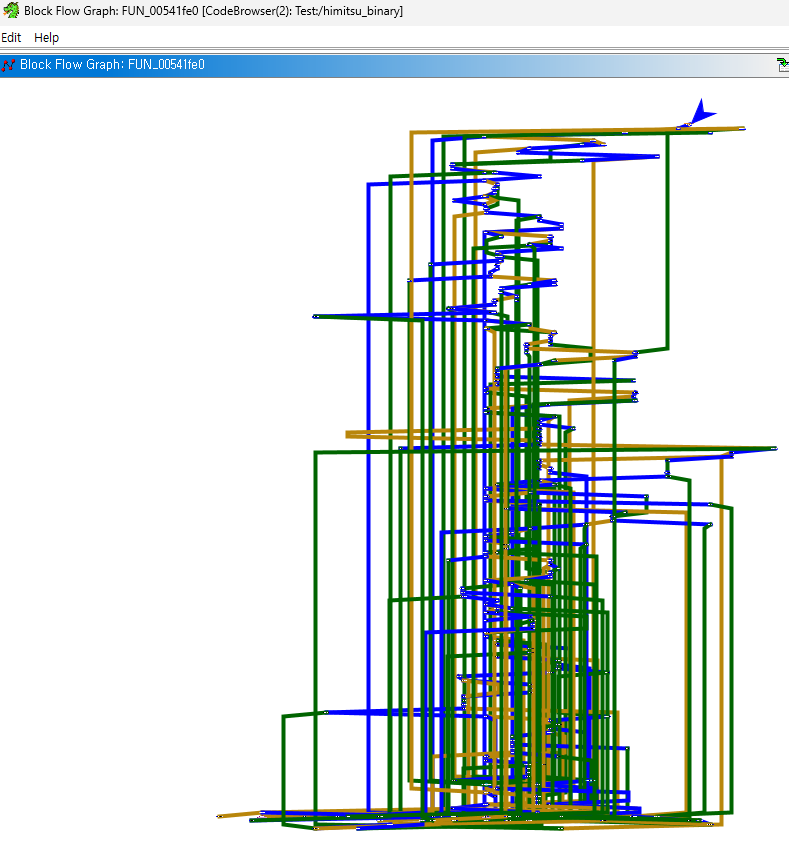 himitsushell/himitsushell
shell script protector (obfuscation, embedded interpreter, DRM) - invisible to kernel tracing
 gmh5225/f31
Tool for hiding Kali Linux on the network
 yolkfull/cve-2026-52910-poc
Race reproducer and stress toolkit for CVE-2026-52910, a Linux kernel use-after-free in reuseport cBPF selector programs, with dmesg and leak checks.
 gmh5225/crowarmor
Linux kernel security driver using LSM to harden the system, monitor and restore syscall table integrity, and protect CPU control registers against…
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
 spensercai/copy_fail
Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…
 webhosting4u/copy-fail_detect_and_mitigate_cve-2026-31431
Detects exposure to CVE-2026-31431 (Copy Fail) and optionally mitigates by disabling the vulnerable algif_aead kernel module, providing verdicts and…
 professional-slacker/alg_check
Audits and hardens Linux systems against AF_ALG local privilege escalation (CVE-2026-31431) by checking kernel crypto API exposure, restricting…
 ctzisme/copyfail-guard
Detect and mitigate CVE-2026-31431 (Copy Fail) on Linux systems.
 silent0x0/copy-fail---cve-2026-31431
CVE-2026-31431 "Copy Fail" - Analysis and defensive research for the Linux kernel AF_ALG privilege escalation vulnerability affecting all major…
 wgnet/wg.copyfail.patch
eBPF-based workaround for CVE-2026-31431 (Copy.Fail) that filters or kills AF_ALG socket creation to prevent local privilege escalation and container…