
CVE-2026-77771
 pervinzahidli/cve-2026-77771
Advisory for CVE-2026-77771, a 2FA bypass in the miniOrange WordPress plugin via session-scoped OTP lockout, with impact analysis and remediation…
authenticationdefensive-toolseducation+2
pervinzahidli/cve-2026-77771Advisory for CVE-2026-77771, a 2FA bypass in the miniOrange WordPress plugin via session-scoped OTP lockout, with impact analysis and remediation…
 facebook/threatexchange
Trust & Safety tools for working together to fight digital harms.
 immersive-labs-sec/bruteratel-detectiontools
A collection of Tools and Rules for decoding Brute Ratel C4 badgers
 embee-research/yara-detection-rules
Yara Rules for Modern Malware
 sarjanpatel22/siem-threat-detection-lab
Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…
 dave_m/clamtk
An easy to use, light-weight, on-demand virus scanner for Linux systems. For additional help, see the <a…
 taisa456/network-security-snort
Snort 3 IDS → IPS lab on Kali. Custom detection rules + iptables enforcement against ICMP recon, Nmap SYN scans, Hydra FTP brute force, and vsftpd…
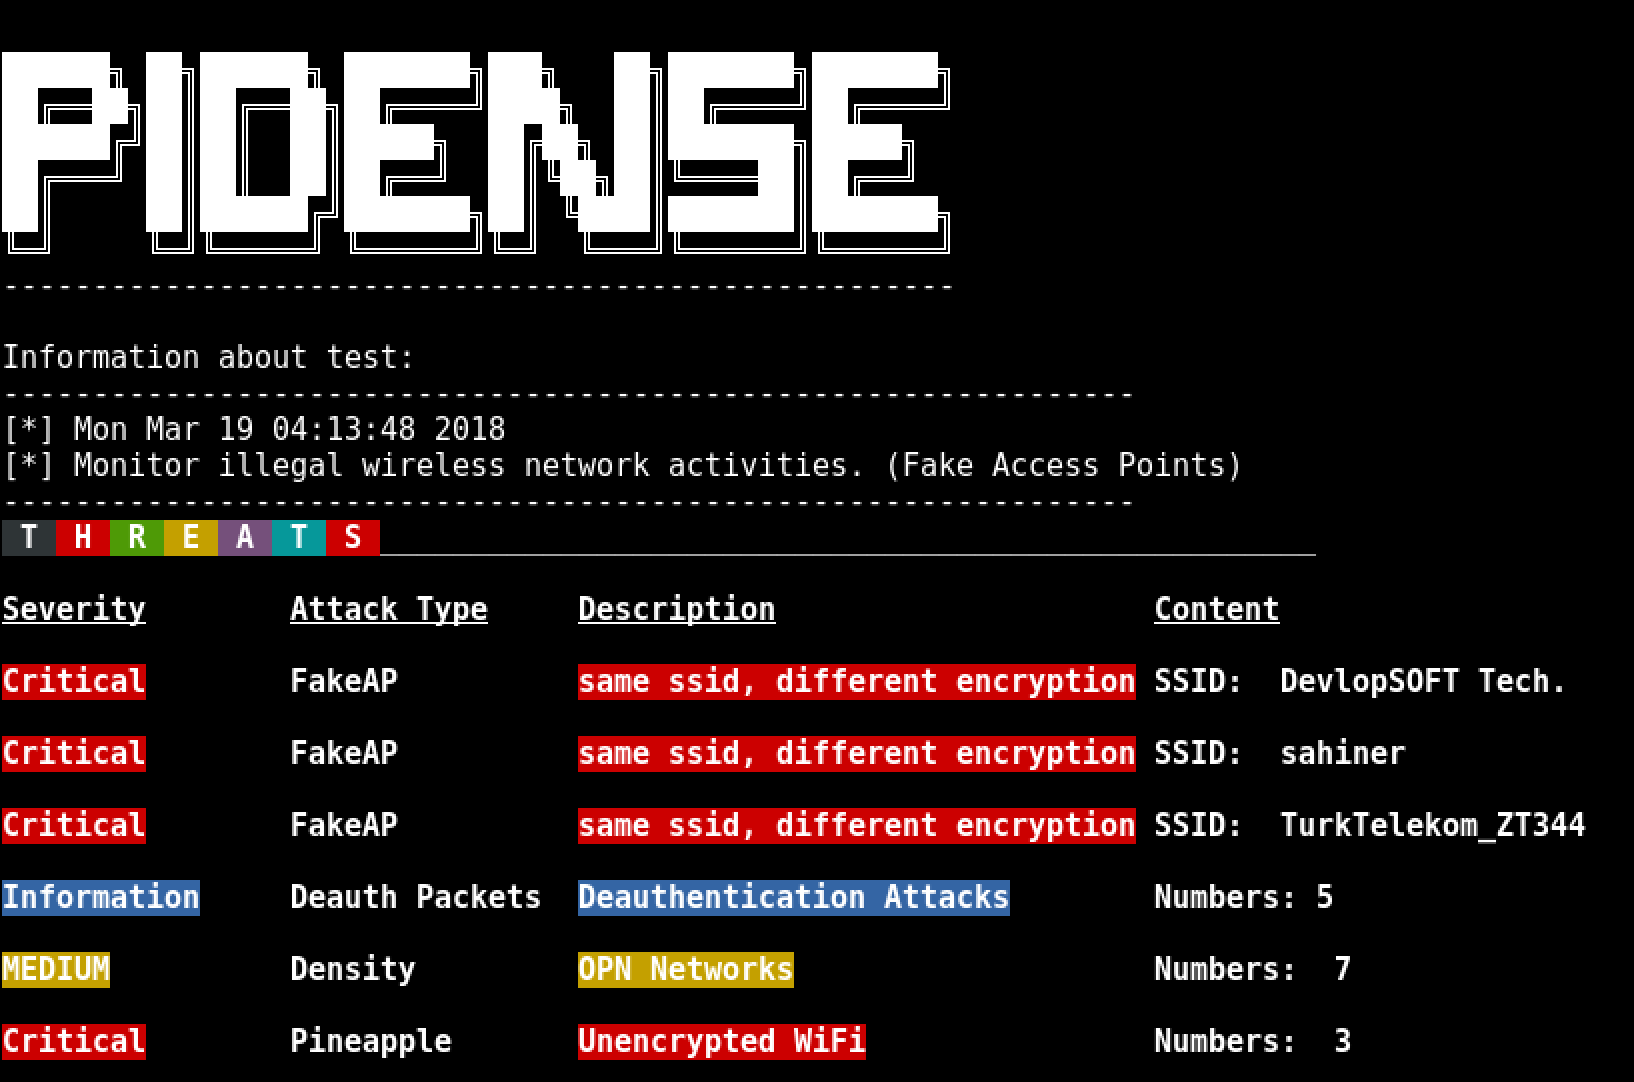 wipi-hunter/pidense
🍓📡🍍Monitor illegal wireless network activities. (Fake Access Points), (WiFi Threats: KARMA Attacks, WiFi Pineapple, Similar SSID, OPN Network…
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/
 jazzband/django-defender
A simple super fast django reusable app that blocks people from brute forcing login attempts
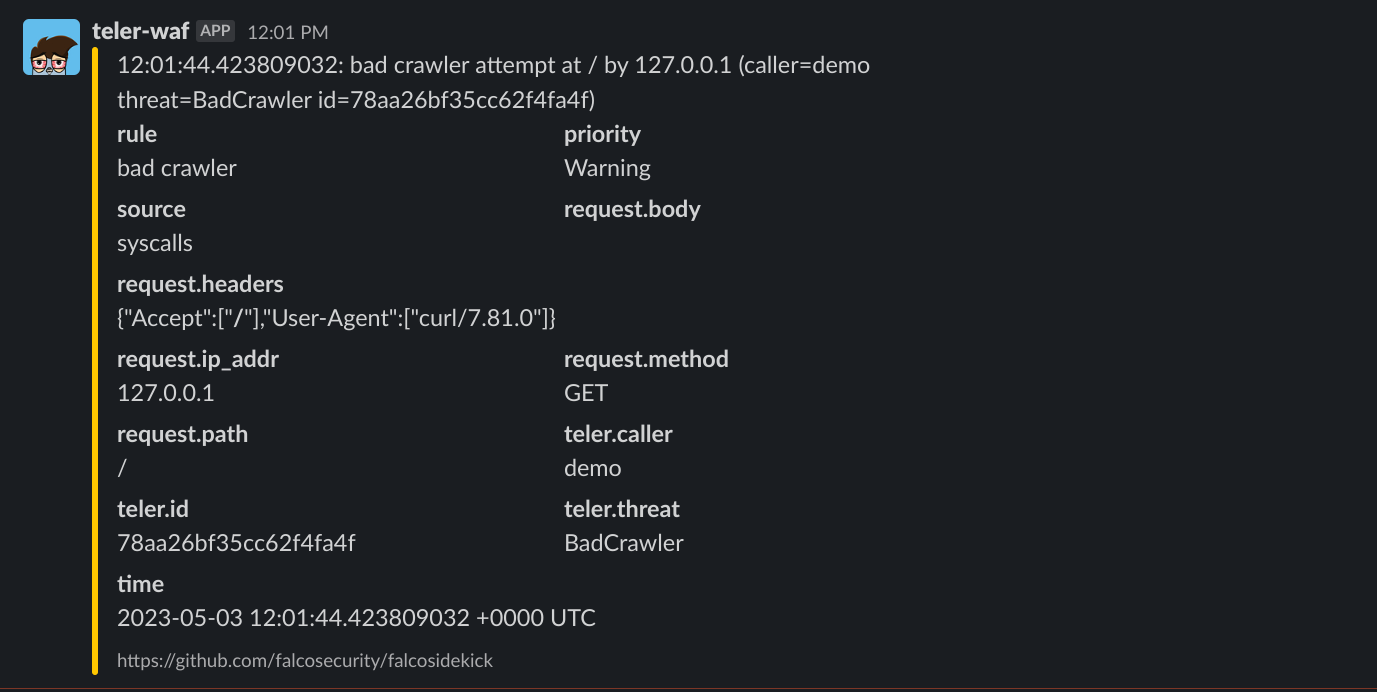 teler-sh/teler-waf
teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…

 ranguli/ioccheck
A tool for simplifying the process of researching IOCs.
 g0tmi1k/kippo-g0tmi1k
Medium-interaction SSH honeypot that logs brute force attacks and full attacker shell interactions, with customization options to reduce…