

fad-checker
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
code-analysisconfiguration-auditingdefensive-tools+6
9pings/fad-checkerBuildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 disley15-collab/bigint-buffer-js
Pure-JS drop-in for [email protected] without the vulnerable native binding (CVE-2025-3194)
 darabium/cve-2026-24733
Dependency-free Python verifier that detects CVE-2026-24733, an Apache Tomcat HTTP/0.9 HEAD security-constraint bypass, with JSON output and CI/CD…
 virologi-info/mssharepoint-scanner
A scanner for CVE-2026-55040 and CVE-2026-63520, designed to determine whether the server is affected by these two CVEs.
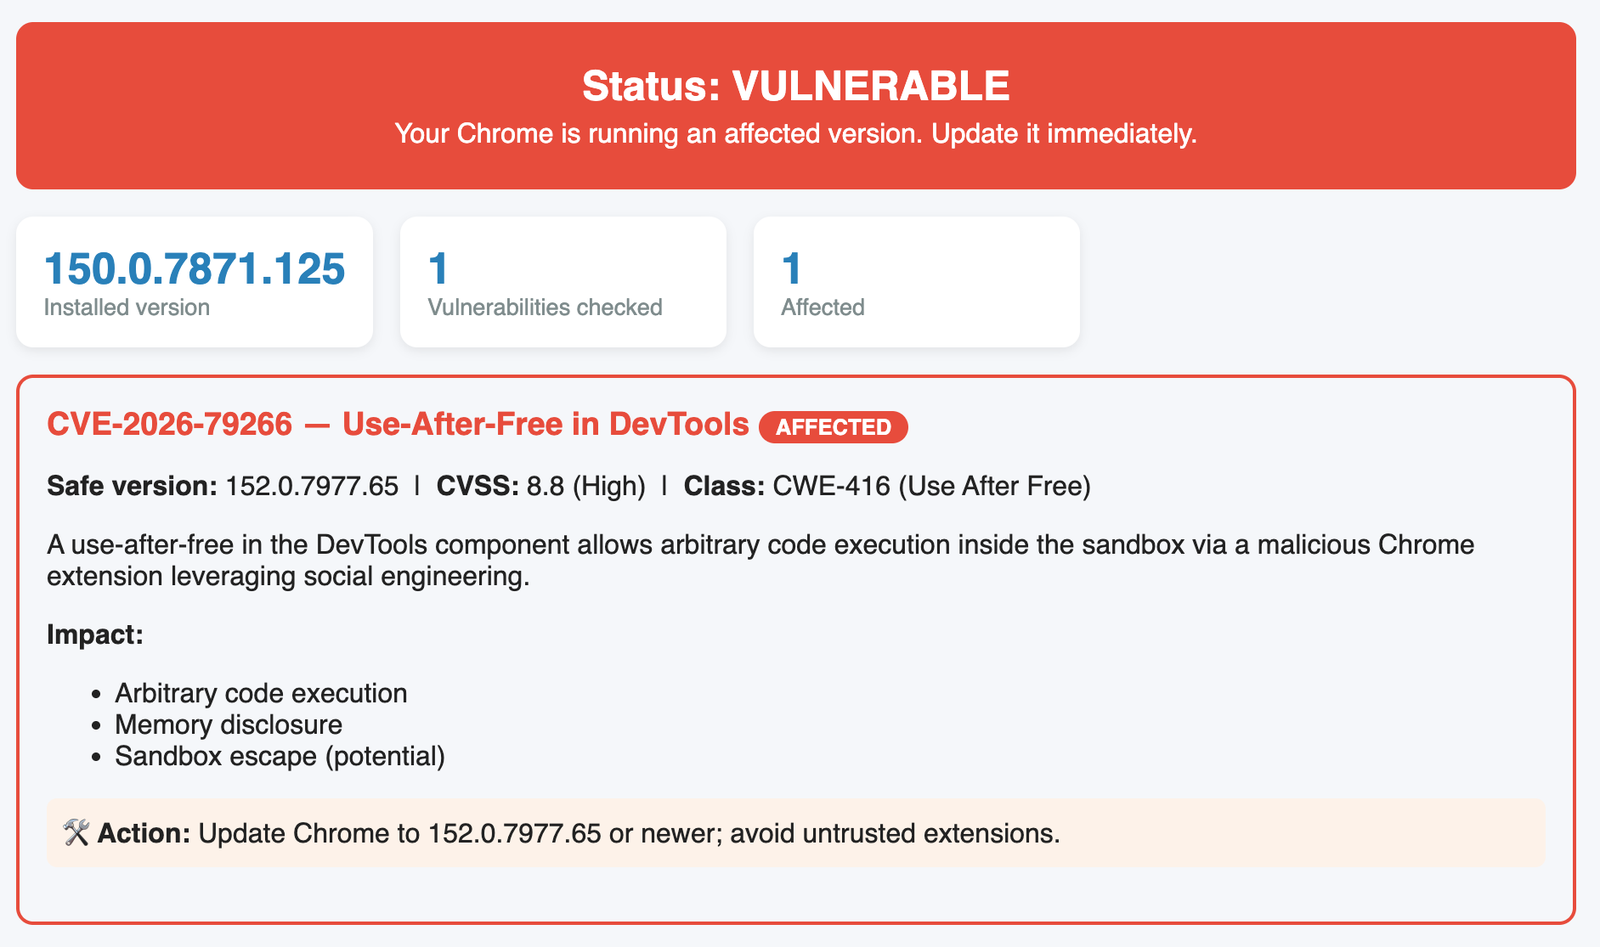 virologi-info/chrome-vuln-scanner
Check for CVE-2026-79266. A use-after-free in the DevTools component allows arbitrary code execution inside the sandbox via a malicious Chrome…
 ctzisme/copyfail-guard
Detect and mitigate CVE-2026-31431 (Copy Fail) on Linux systems.
 cyclonedx/cyclonedx-cli
CLI for generating, analyzing, merging, diffing, validating, signing, and converting CycloneDX SBOMs across JSON, XML, Protobuf, CSV, and SPDX…
 sanaullahamanullah/xss2shell-check
Non-destructive detector for CVE-2026-64638 (XSS2Shell) — WordPress pre-auth XSS reflection primitive
 dissectmalware/yaradbg-frontend
Web-based Yara rule debugger with an editor, live match evaluation, matched-string details, and rule dependency visualization for detection…
 vladimir-tokarev-cyera/llama-cpp-security-patches
Security patches for unpatched llama.cpp vulnerabilities (CVE-2026-43626 through CVE-2026-43632) — Cyera Research
 scitotec/log4j-recognizer
A Java helper to identify log4j in the current classpath
 amavis/amavis
amavis is a high-performance email content filter framework written in Perl.
 arpitgupta369/log4shell-scanner
Lightweight scanner that detects vulnerable Log4j versions and Log4Shell (CVE-2021-44228) indicators in a filesystem tree.
 winnpixie/log4noshell
A Java Agent that disables Apache Log4J's JNDI Lookup to mitigate CVE-2021-44228 ("Log4Shell").
 nccgroup/log4j-jndi-be-gone
A Byte Buddy Java agent-based fix for CVE-2021-44228, the log4j 2.x "JNDI LDAP" vulnerability.
 rails-lts/json_cve_2020_10663
Workaround for CVE-2020-10663 (vulnerability in json gem)
 rashedhasan090/cve-2025-55182-mitigator
CLI scanner that detects likely vulnerable React/Next.js dependencies for CVE-2025-55182 and provides mitigation targets. Supports JSON output and…
 aikidosec/safe-chain
Protect against malicious code installed via npm, yarn, pnpm, npx, pnpx, pip, uv and poetry with Aikido Safe Chain. Free to use, no tokens required.