
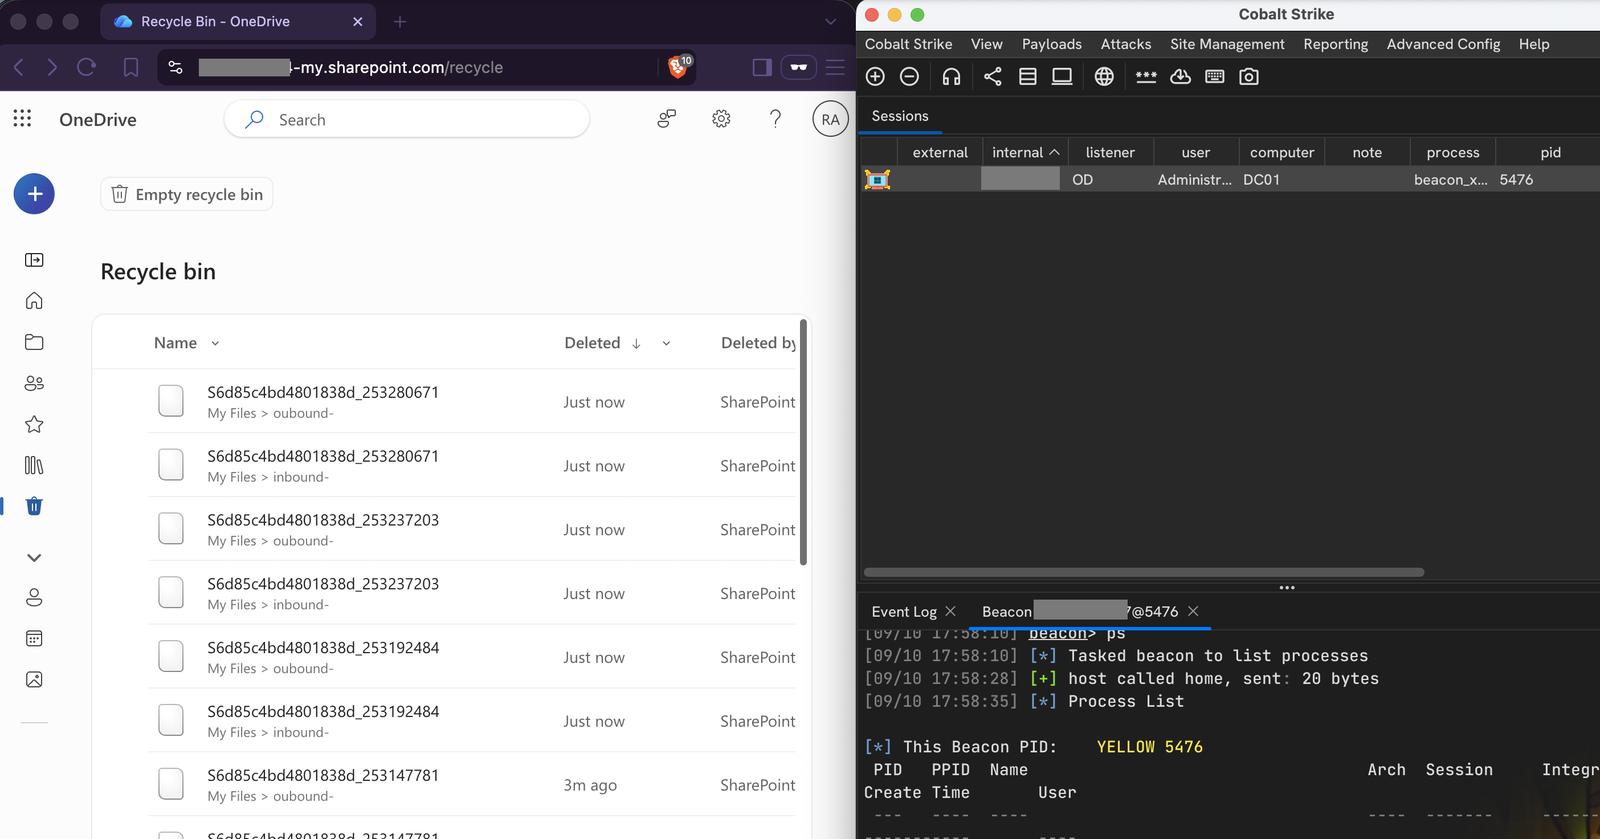
OneDrive-UDC2
 nmht3t/onedrive-udc2
OneDrive as a covert C2 transport for Cobalt Strike
cloud-securitycommand-and-controldefensive-tools+4
345 days ago
nmht3t/onedrive-udc2OneDrive as a covert C2 transport for Cobalt Strike
 gmh5225/dsark64
BYOVD proof-of-concept abusing the WHQL-signed DsArk64.sys driver for ring-0 process termination and kernel read/write via encrypted IOCTLs and…
 withsecureopensource/chainsaw
Rapidly Search and Hunt through Windows Forensic Artefacts
 gmh5225/dropper
Tool for embedding payloads into JPG/PNG format images, allowing to perform certain actions when opening them.
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
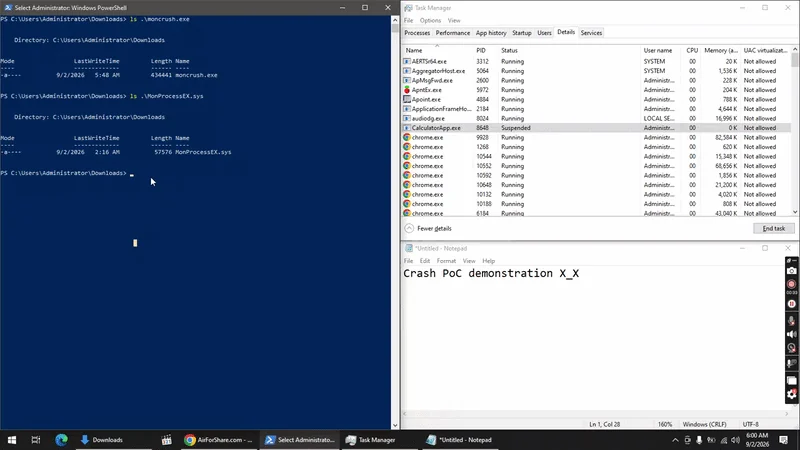 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
 javascript-obfuscator/javascript-obfuscator
Obfuscates JavaScript and Node.js code with variable renaming, string encryption, control flow flattening, and anti-debugging to protect source code…
 fireeye/pywintrace
Python ctypes wrapper for Event Tracing for Windows (ETW) enabling session control, event capture, and custom callbacks for security monitoring and…
 rspamd/rspamd
Spam filtering and email processing framework with regex rules, statistical analysis, custom Lua plugins, and external blocklists for MTA integration.
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 0xlipon/xss2shell
🔥 XSS2Shell — CVE-2026-64638 Scanner & PoC Toolkit
 michenriksen/drawio-threatmodeling
Draw.io libraries for threat modeling diagrams
 google/safetext
Go library for safe YAML and shell generation, using syntax-aware templates to detect and block injection attacks via annotations for trusted data.
 zephrfish/autohoneypoc
AutoPoC Generator HoneyPoC
 olafhartong/sysmon-parser
Automatically generated Sysmon parser for Azure Sentinel
 sigmahq/pysigma
Python library to parse and convert Sigma rules into queries (and whatever else you could imagine)
 nccgroup/reactor
Runs custom filters on Elasticsearch and alerts on matches
