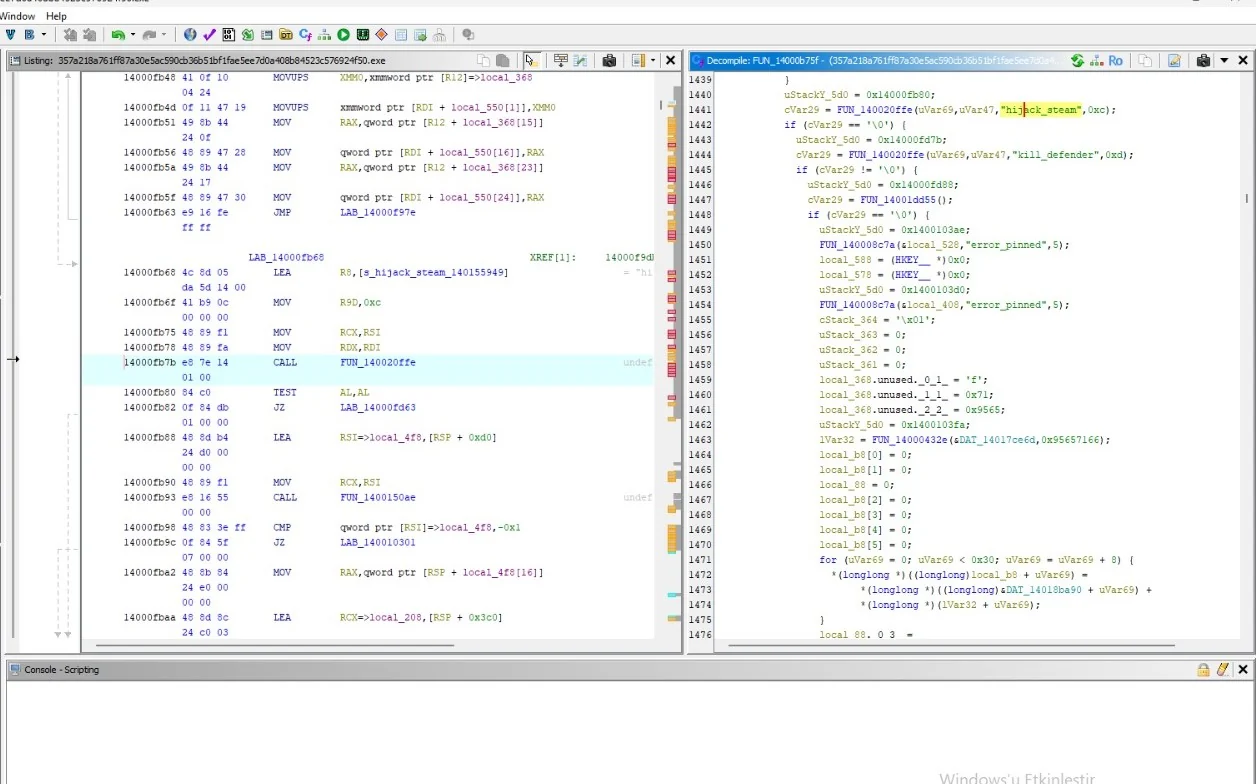
Rusty-Stealer-Keylogger-Screen-Streaming-Service-Persistence-Defender-Evasion-Analysis

Reverse engineering Rusty Stealer: A Rust-based RAT featuring advanced keylogging, live screen streaming, and aggressive defense evasion (killing…

Reverse engineering Rusty Stealer: A Rust-based RAT featuring advanced keylogging, live screen streaming, and aggressive defense evasion (killing…

NetExec module: run every stock Windows vuln-check in one pass (check-only, no exploit)

An AD CS toolkit for AD Admins, Defensive Security Professionals, and Filthy Red Teamers

Runnable proof-of-concept reproducer for CVE-2026-85315, demonstrating camel-grpc consumer exception message disclosure (CWE-209) in Camel Spring…

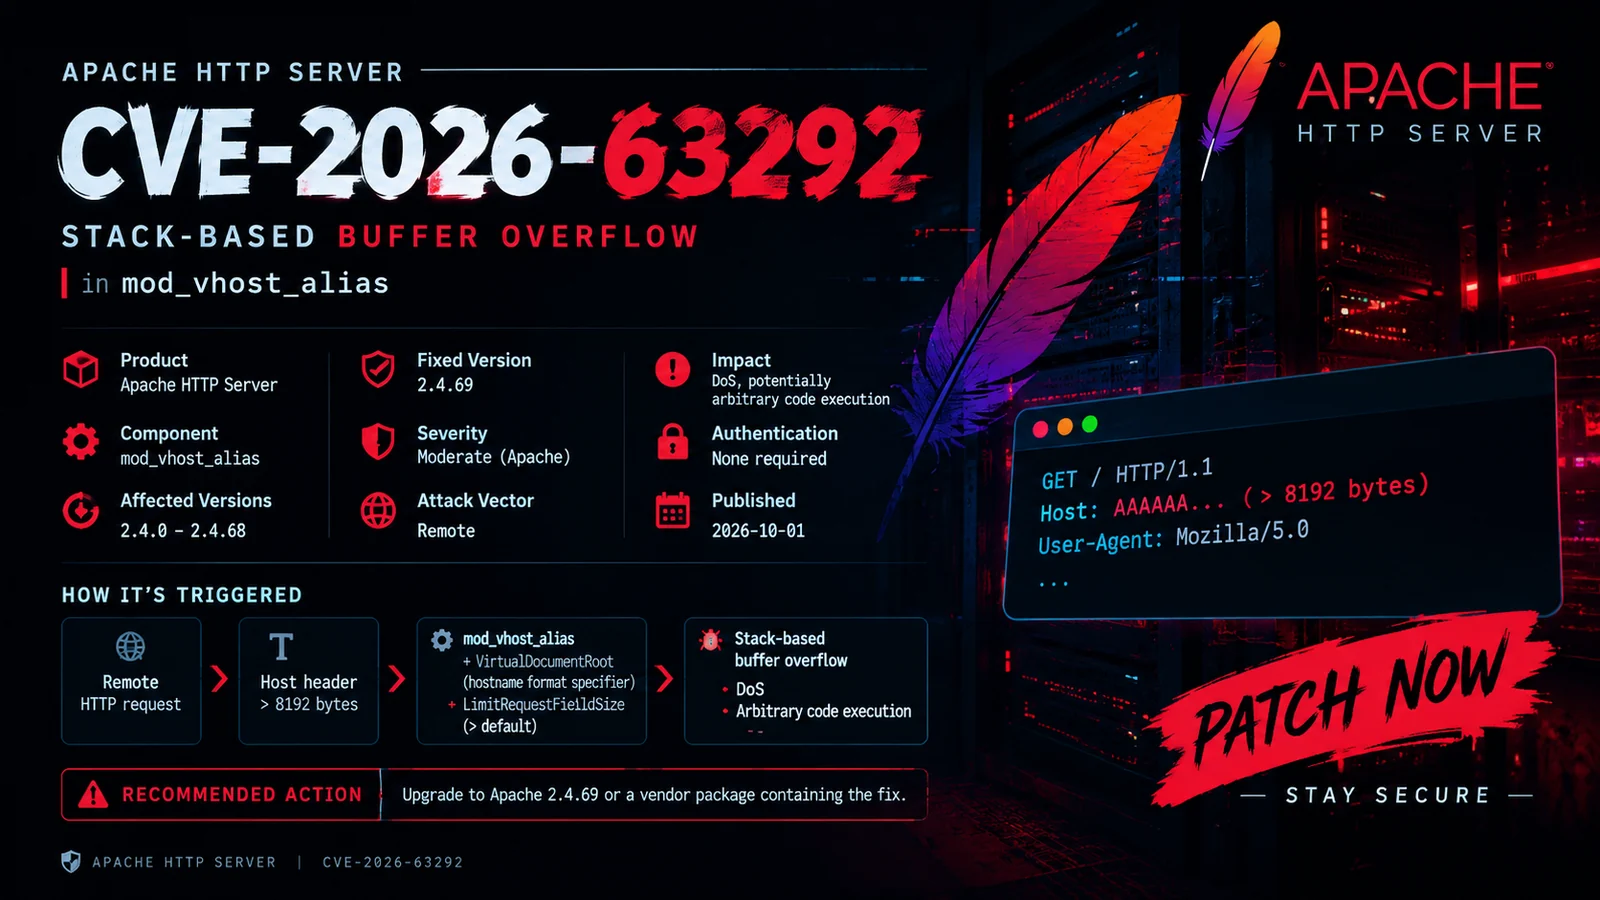
Documents CVE-2026-63292, a stack-based buffer overflow in Apache mod_vhost_alias, with affected versions, safe version and configuration checks, and…

Minimal Windows x64 reflective PE mapper that loads DLLs from memory without LoadLibrary, resolves exports, and dispatches calls through a…

Exploit and analyze CVE-2026-42978 with a Windows Push Notifications module for AI security, multi-protocol terminal, and autonomous agent suite.

eBPF Security Monitoring and Sandboxing Agent Based on Aya

Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…

CVE-2026-42978 Windows Push Notifications (WpnService) Use-After-Free & Race Condition PoC research, diagnostic scanner, and security audit module…

🛡️ Official AI Security Tool diagnostic module for CVE-2026-41089 (Windows Netlogon Stack Buffer Overflow RCE). Features technical writeup, attack…

Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…

Detects exposure to CVE-2026-31431 (Copy Fail) and optionally mitigates by disabling the vulnerable algif_aead kernel module, providing verdicts and…

Copy Fail (CVE-2026-31431) is a logic flaw in the Linux kernel's algif_aead module — part of the AF_ALG userspace crypto API. It was disclosed on…

Kubernetes DaemonSet to detect and remediate CVE-2026-31431 (GHSA-2274-3hgr-wxv6) — algif_aead LPE via modprobe blacklist

Kernel module using ftrace to block AF_ALG/AEAD requests, mitigating CVE-2026-31431 without requiring LSM BPF. Provides logging and easy compilation…

No-reboot mitigation script for the Copy Fail kernel bug (CVE-2026-31431). Disables the vulnerable algif_aead module and evicts page cache for setuid…

Permanent mitigation scripts for CVE-2026-31431 (Copy Fail) on Ubuntu 24.04, blacklisting the vulnerable algif_aead kernel module and updating…