

DFIR-Companion
 hasamba/dfir-companion
DFIR forensics companion server + capture extension
ai-securitydefensive-toolsdigital-forensics+9
3515h 37m ago
hasamba/dfir-companionDFIR forensics companion server + capture extension
 withsecureopensource/chainsaw
Rapidly Search and Hunt through Windows Forensic Artefacts
 karim852/kage-dfir-toolkit
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
 last-byte/persistencesniper
Powershell module that can be used by Blue Teams, Incident Responders and System Administrators to hunt persistences implanted in Windows machines.…
 seekbytes/ipa
GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 mindcrypt/powerglot
Powerglot encodes offensive powershell scripts using polyglots . Offensive security tool useful for stego-malware, privilege escalation, lateral…
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
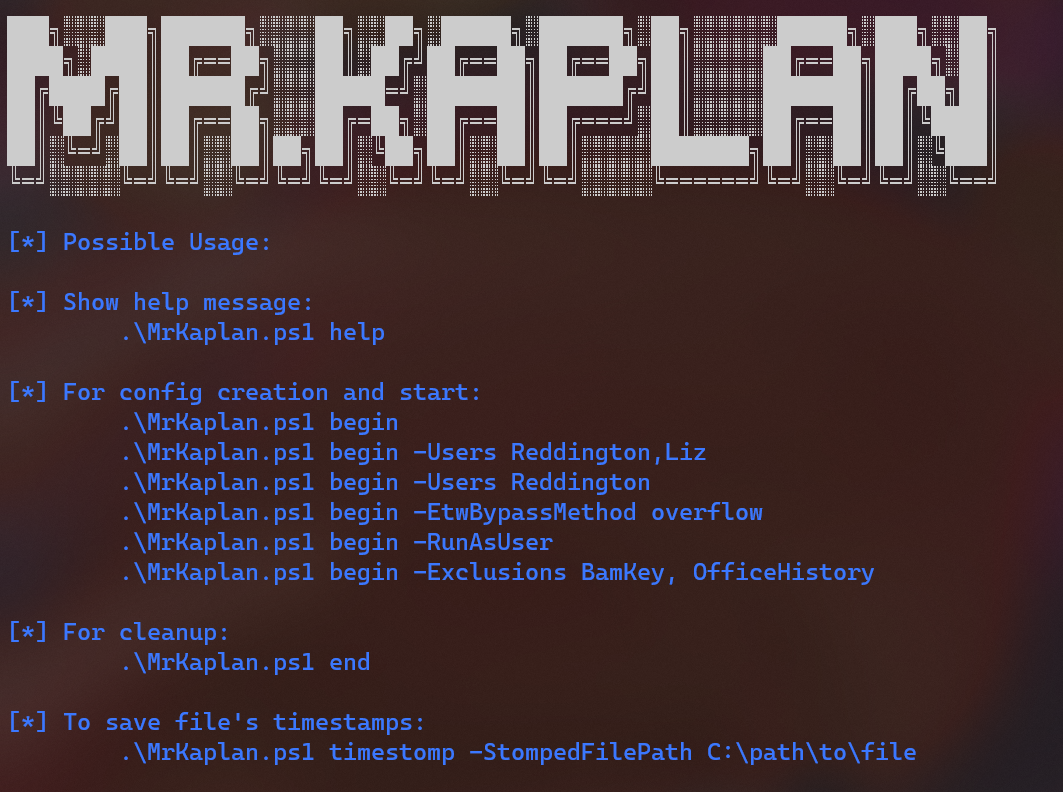 idov31/mrkaplan
PowerShell tool for red teamers that clears execution evidence by stopping event logging, removing file and registry artifacts, and saving timestamps…
 rorywag/hayabusa-bulk-runner
Bulk-run Hayabusa across a folder of triage collections, one run per host, with per-host reports and a cross-host triage dashboard
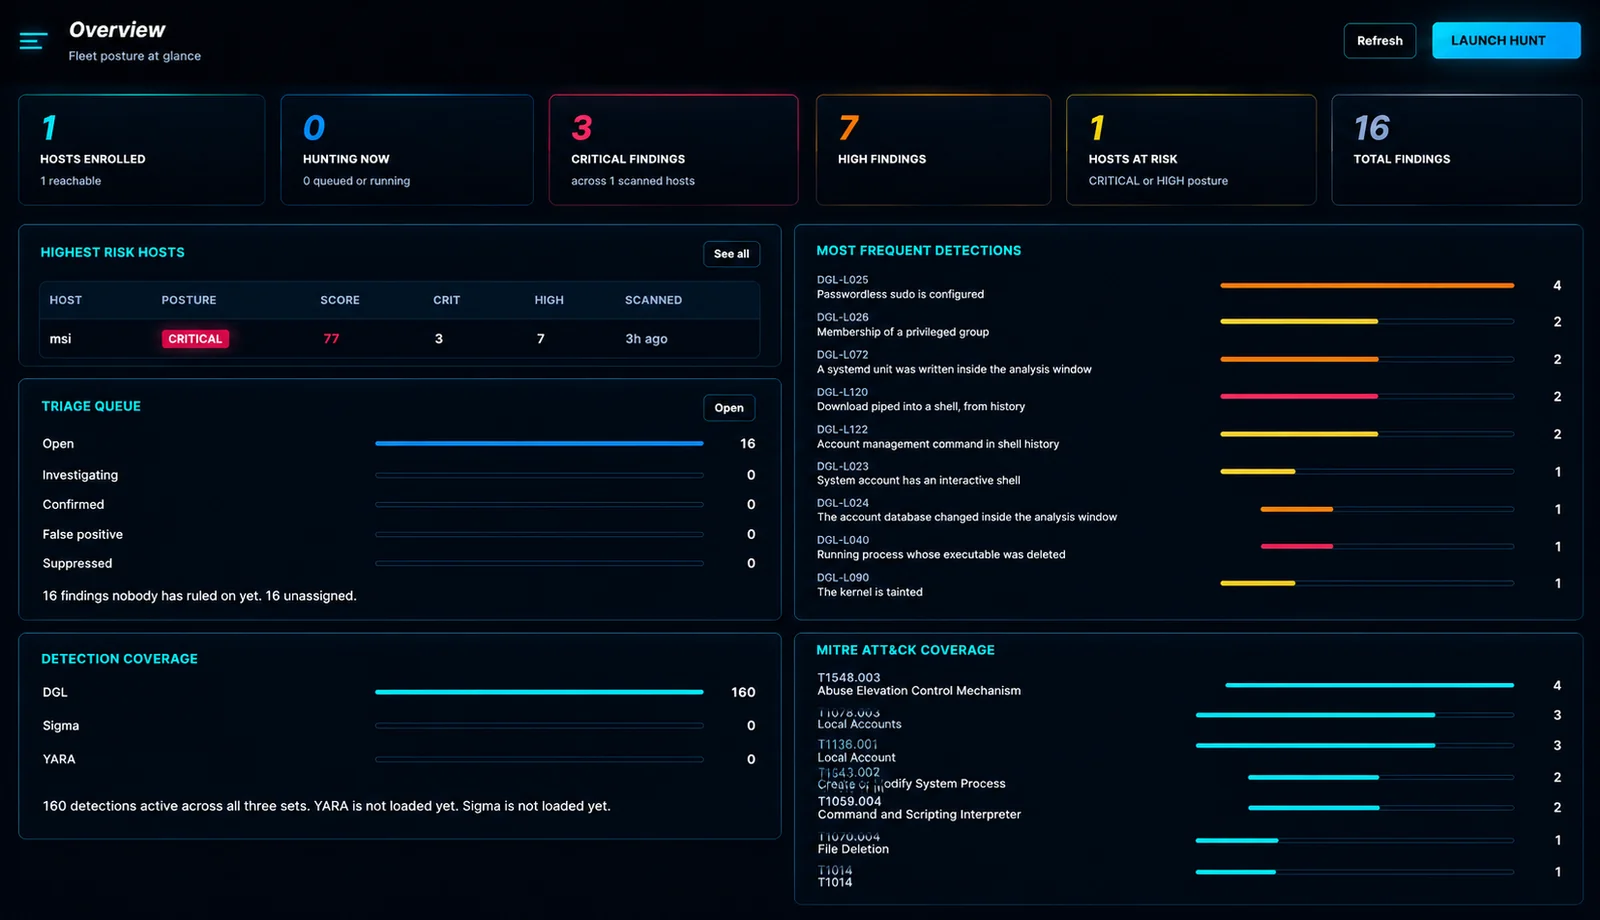 douglas-042/douglas-042-hq
Central console for Douglas-042 HEADQUARTERS collectors. Sweeps a fleet, correlates results across hosts, and manages IOC feeds and SIEM delivery…
 threathunters-io/qlog
ETW-based Windows process creation logger that enriches events with file hashes, signatures, and parent process details, outputting to Windows…
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
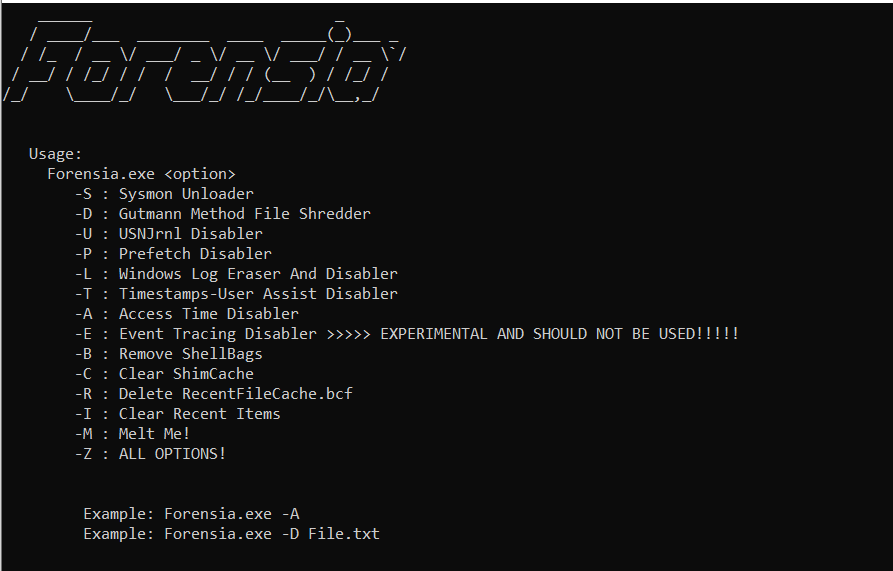 paulnorman01/forensia
Anti Forensics Tool For Red Teamers, Used For Erasing Footprints In The Post Exploitation Phase.
 instawp/wp2shell-scan
Detect & clean up wp2shell (CVE-2026-63030) WordPress compromise — bulk-runnable, read-only by default
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
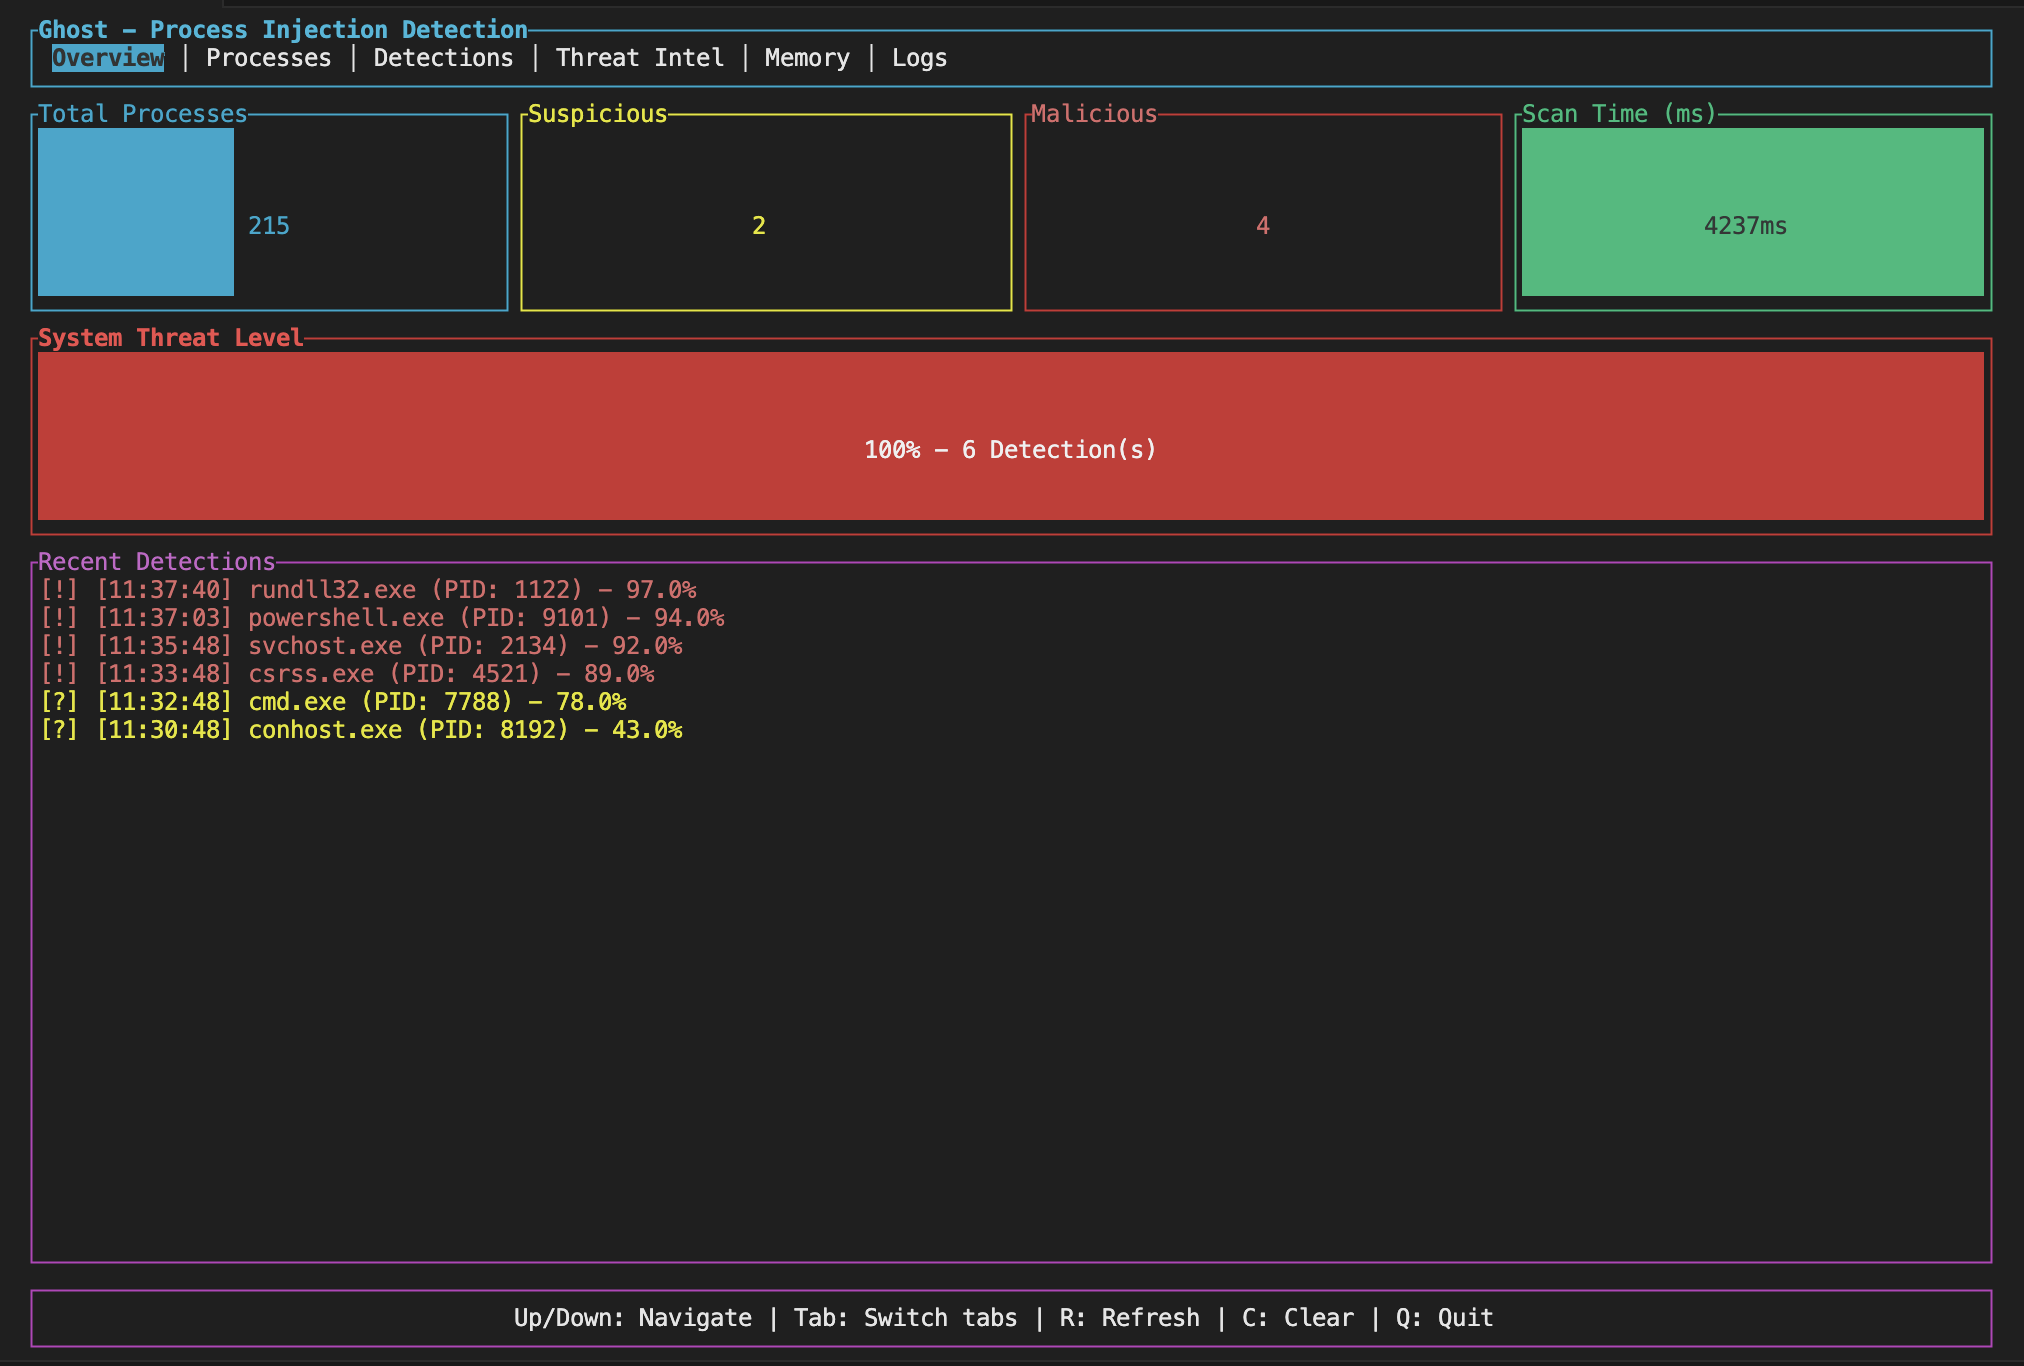 pandaadir05/ghost
Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
 tjnel/certgraveyard_yara
Automated YARA rule generation from the Cert Central compromised certificate database.