
SmuggleMyPayload
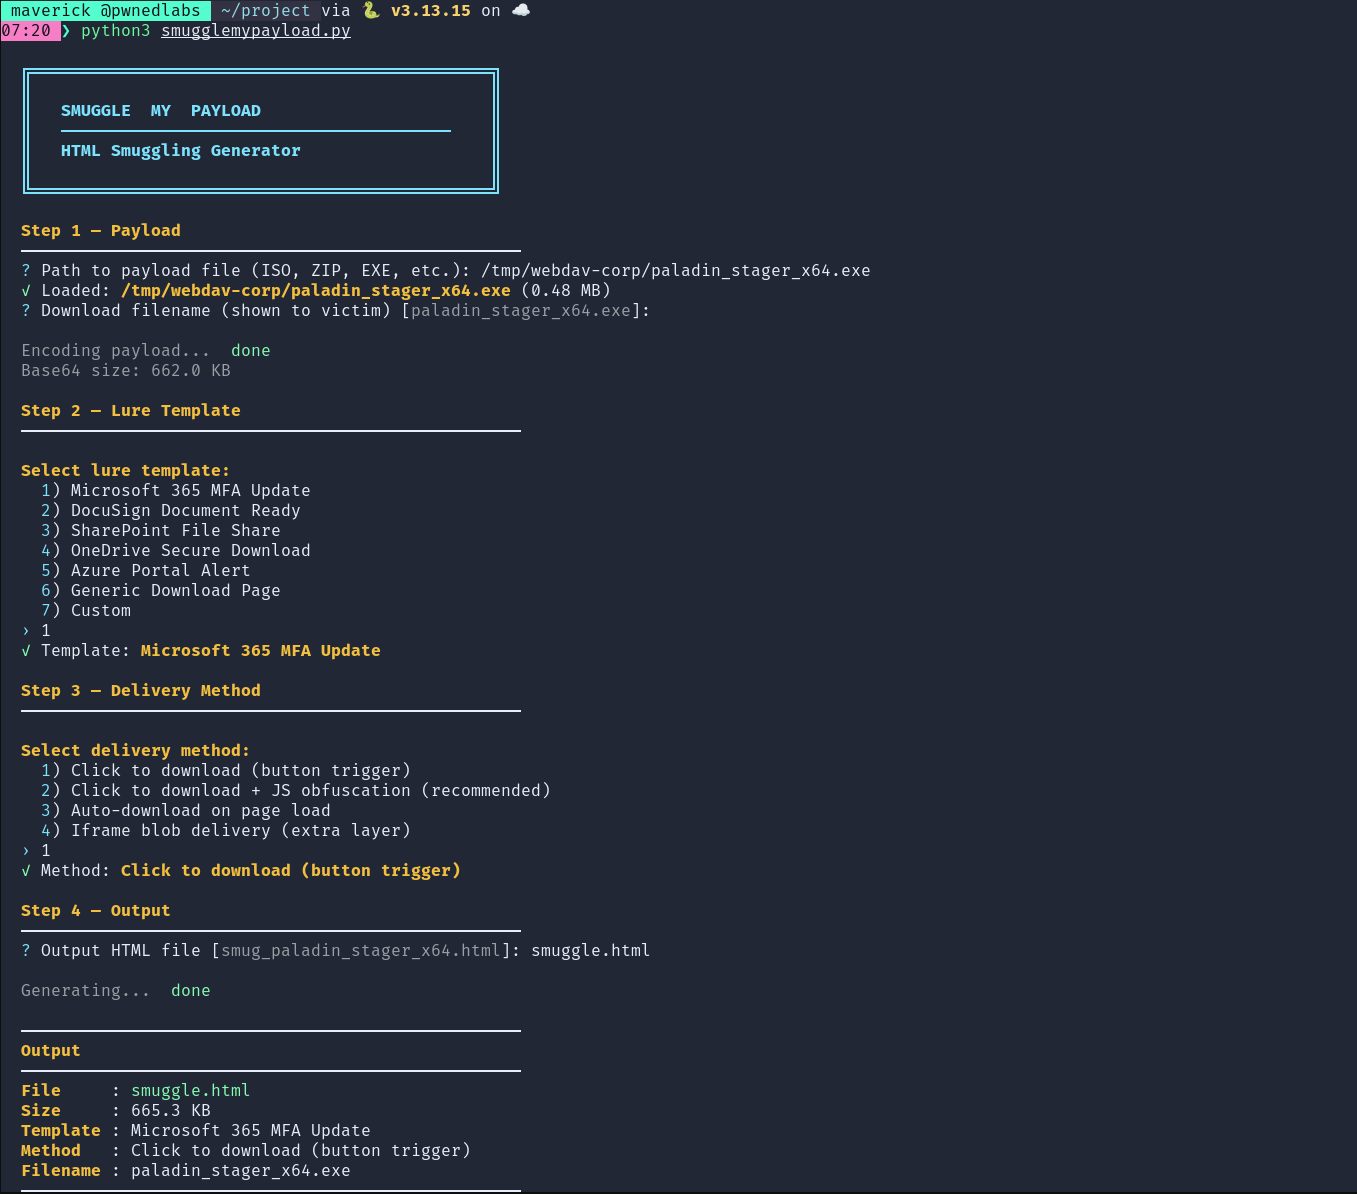
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Obfuscates JavaScript and Node.js code with variable renaming, string encryption, control flow flattening, and anti-debugging to protect source code…

POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution

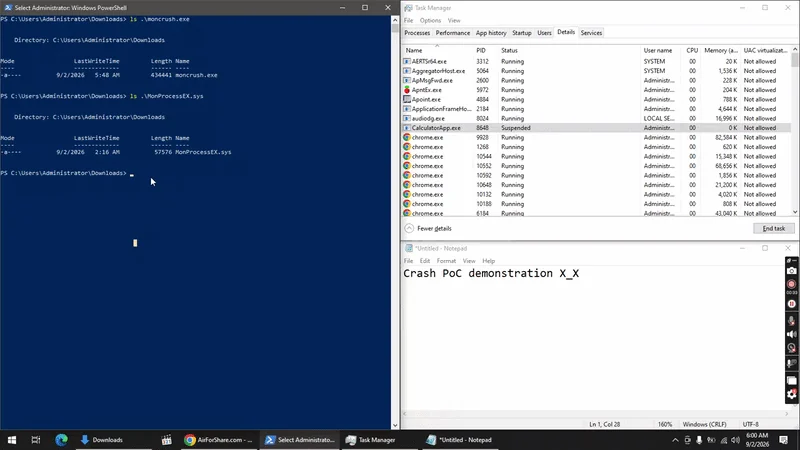
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.

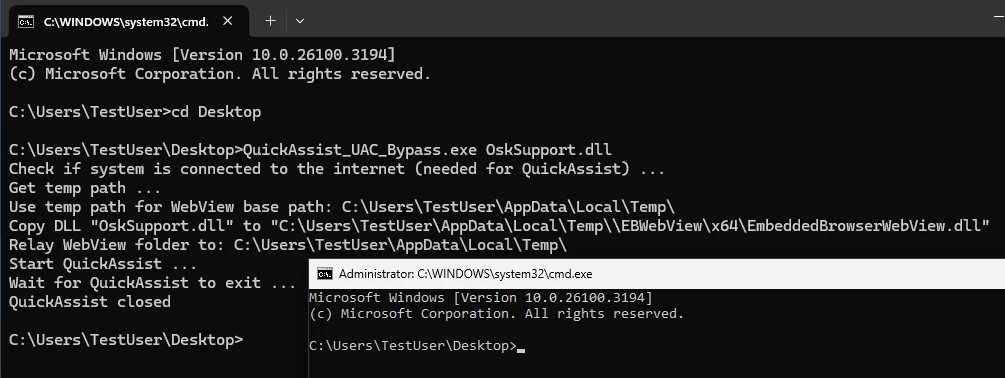
UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…

Tool for embedding payloads into JPG/PNG format images, allowing to perform certain actions when opening them.

OneDrive as a covert C2 transport for Cobalt Strike

A PoC on how to use a Compute Shader as Payload

Process Explorer vulnerable driver PPL Bypass

Header-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.

🔥 XSS2Shell — CVE-2026-64638 Scanner & PoC Toolkit

A BYOSI (Bring-Your-Own-Script-Interpreter) Rapid Payload Deployment Toolkit

BYOVD proof-of-concept abusing the WHQL-signed DsArk64.sys driver for ring-0 process termination and kernel read/write via encrypted IOCTLs and…

Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs

A unique technique to execute binaries from a password protected zip

#PaperCut CVE-2026-81578 + CVE-2026-82078 Defense Toolkit 2 3 A **defensive** toolkit to check and understand exposure to the chained

Python PoC for Apache OFBiz CVE-2023-49070: auth-bypass on /webtools/control/xmlrpc plus ysoserial gadget chain to achieve pre-auth deserialization…

XLL Phishing Tradecraft