SmuggleMyPayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…

Proof-of-concept exploiting a Fortinet fortimon3_74.sys kernel driver flaw to bypass PPL and terminate protected processes like lsass.exe via an…

Extracts LSA secrets and DPAPI keys from Windows registry hives via existing or newly created VSS shadow copies, with an inline regf parser and…

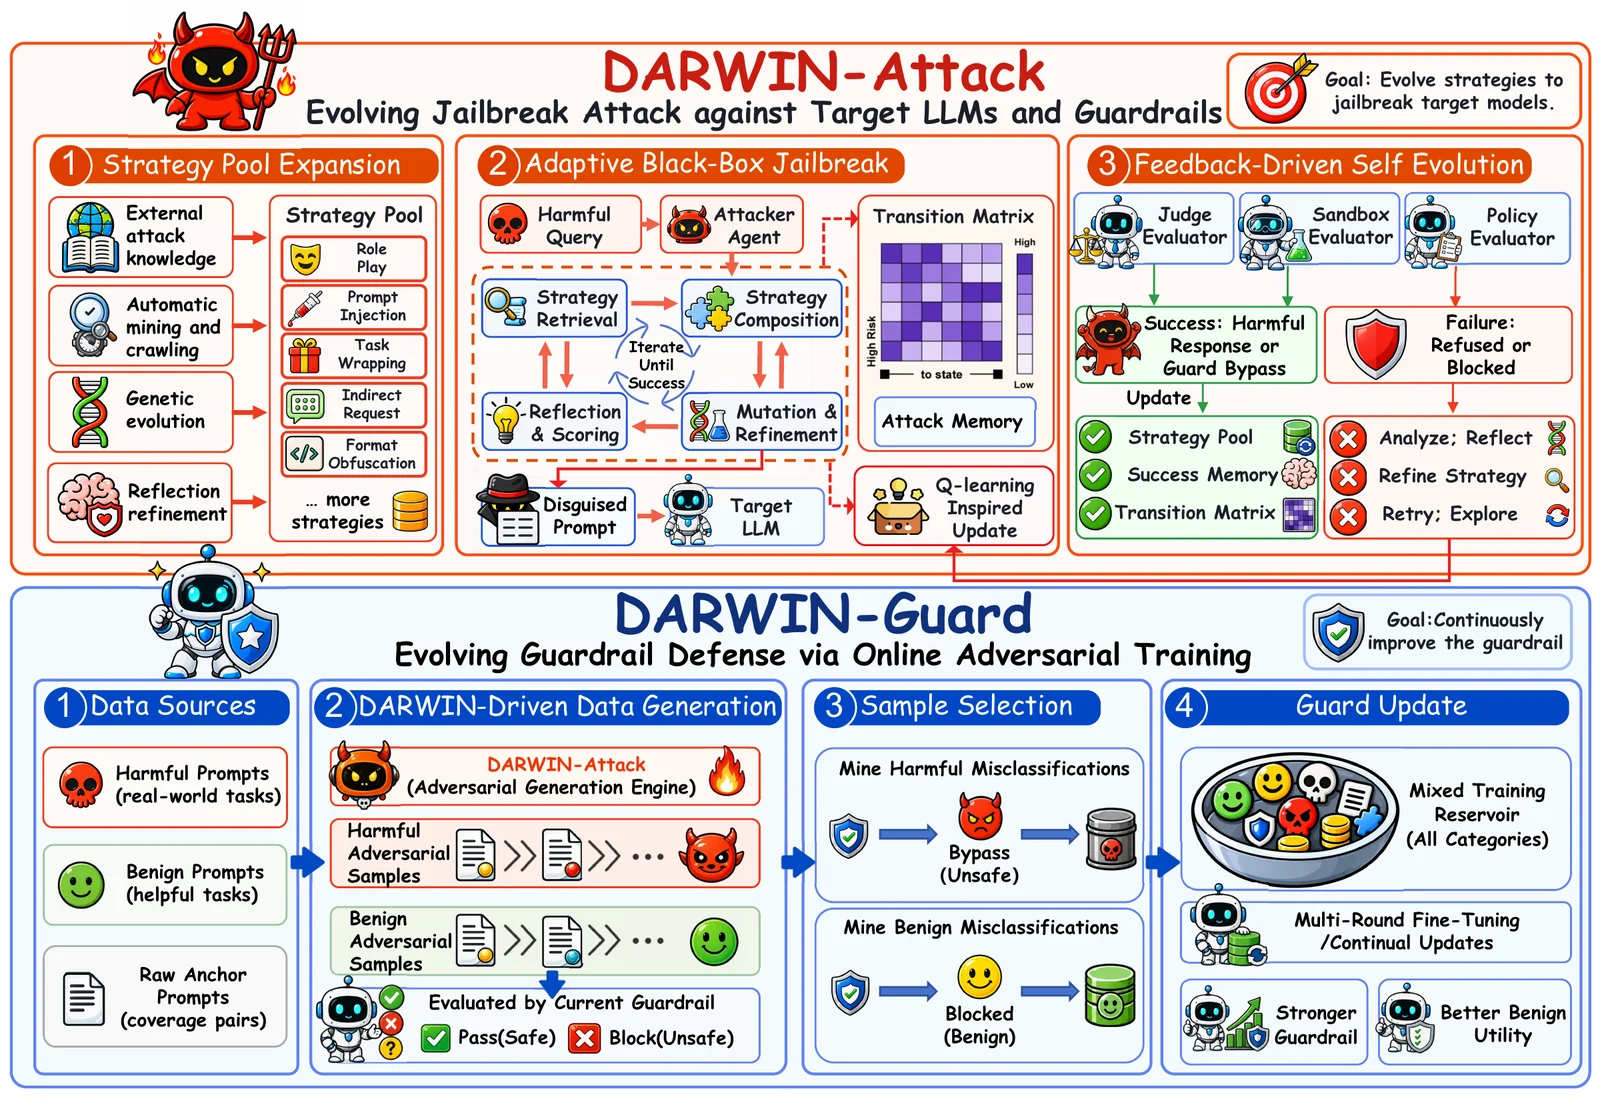
Evolutionary LLM jailbreak and guardrail framework that grows a reusable strategy pool via genetic mutation, Markov selection, and online adversarial…

UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…

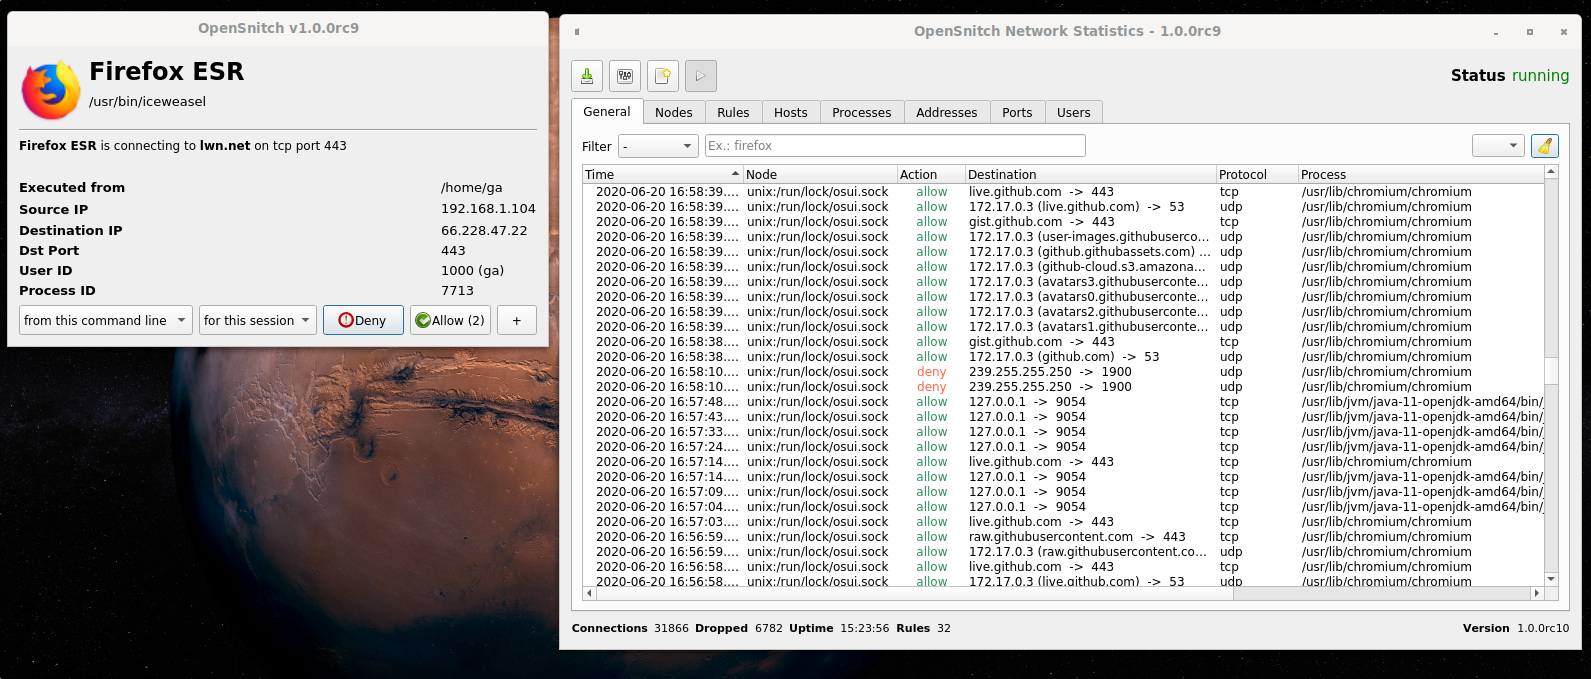
Interactive GNU/Linux application firewall that filters outbound connections, blocks ads and malware domains, manages system firewall rules via GUI,…

Python PoC reproducing the CUPS 2.4.16 local-printer flaw: captures the Local auth token via a rogue IPP endpoint, creates a file:// printer, and…

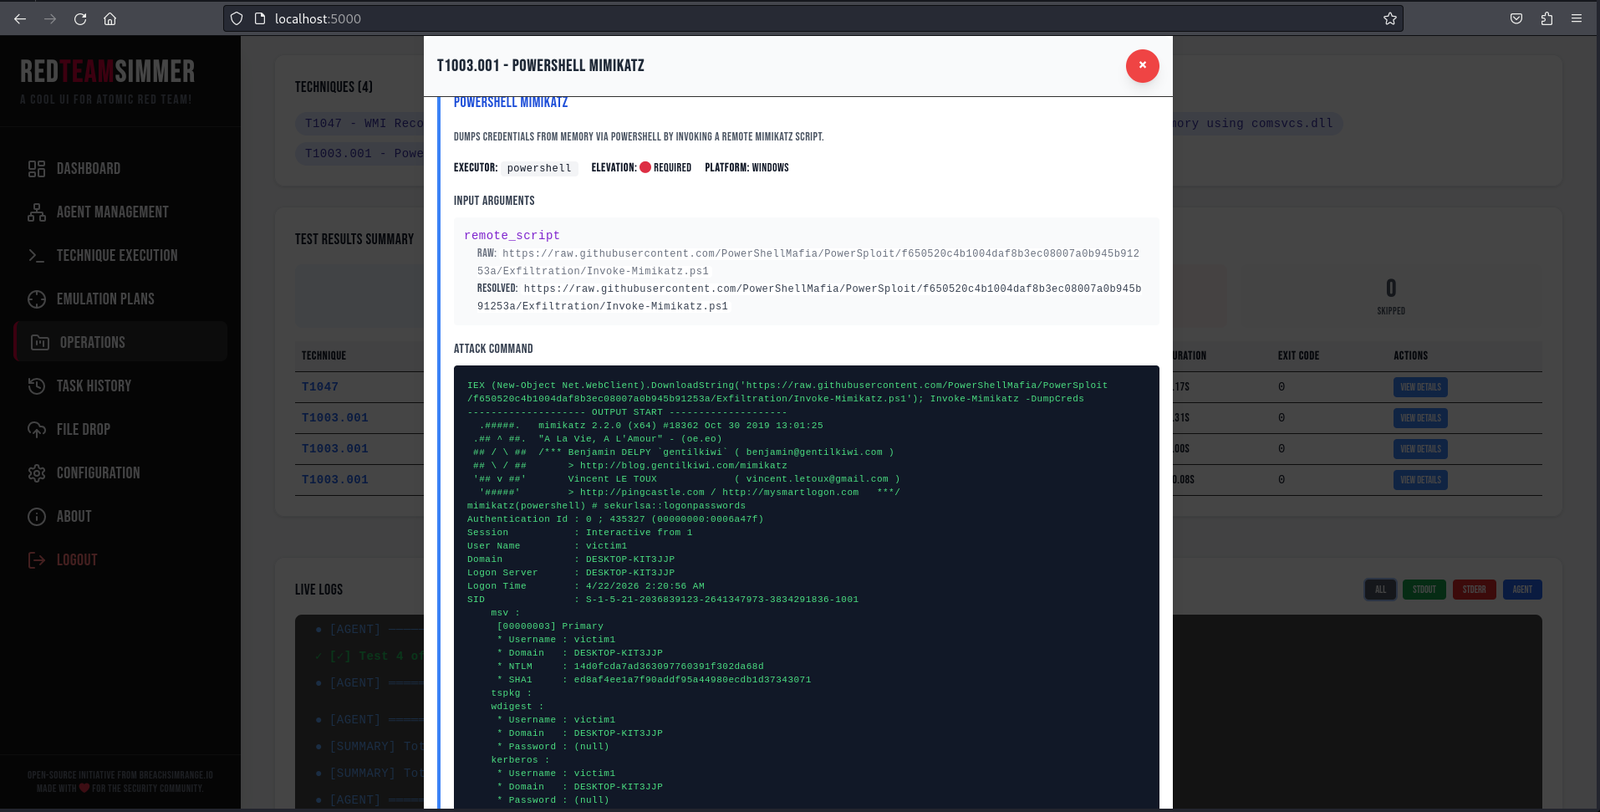
Web-based adversary emulation platform that orchestrates Atomic Red Team tests across Windows endpoints via Go agents, with MITRE ATT&CK mapping, APT…

Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…

Manages the core lifecycle of Qubes OS domains via a Python admin API, handling secure compartmentalization with Xen and exposing an event system for…

Obfuscates Go source code via AES-256 string encryption with runtime decryption, identifier renaming, and comment removal to hinder reverse…

PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…

Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…

SysWhispers on Steroids - AV/EDR evasion via direct system calls.

Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…

Defender framework for LLM agent security that compiles task contracts, validates capability manifests, and checks effects via PLANT/WRAP proof…

Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…