awesome-exploit-development

A curated list of resources (books, tutorials, courses, tools and vulnerable applications) for learning about Exploit Development

A curated list of resources (books, tutorials, courses, tools and vulnerable applications) for learning about Exploit Development

A curated list of IDA x64DBG, Ghidra and OllyDBG plugins.

List of awesome reverse engineering resources

Frida-based tracer for easier reverse-engineering on Android, iOS, Linux, Windows and most related architectures.

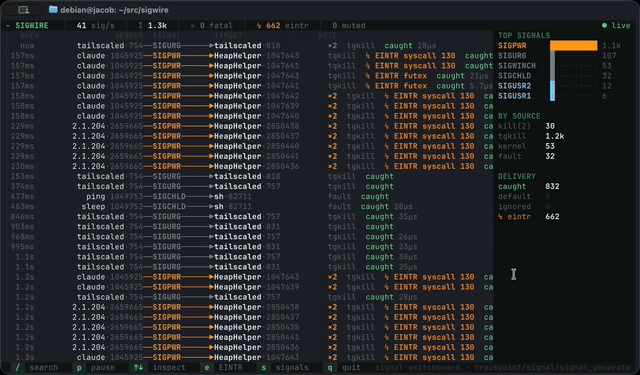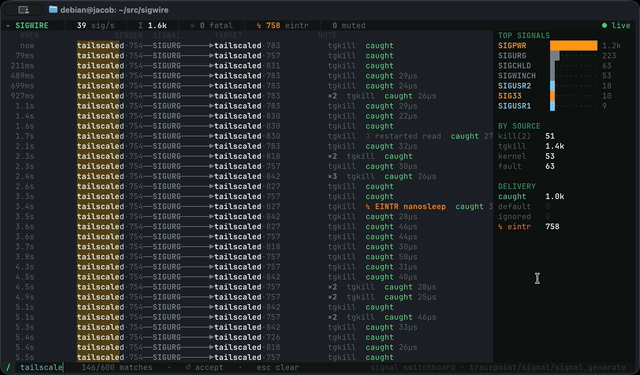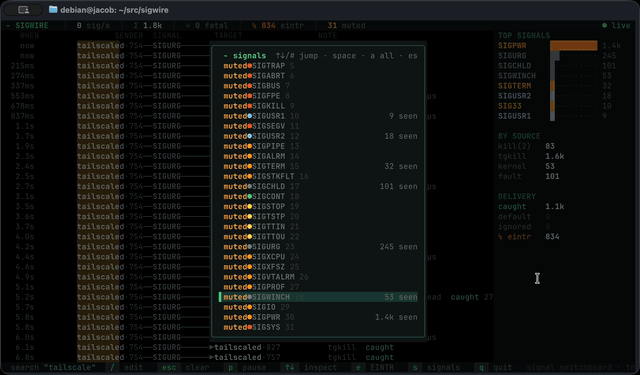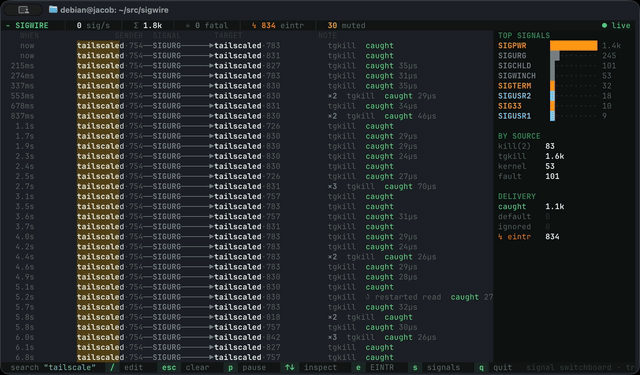
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…

TRANSFORMERS: Forged to Fight is a 3D combat game where you take over some of the most charismatic troopers straight out of the Transformers…

SEH-based buffer overflow in Easy File Sharing Web Server 7.2 demonstrating how an authenticated HTTP POST parameter can corrupt the exception…

MCP Server for Ghidra

My musings with PowerShell

More than a ReClass port to the .NET platform.

Unofficial frida extension for VSCode

MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…

BPF-based Linux IPC tracer for pipes, signals, Unix sockets, loopback, and pseudoterminals with metadata and content capture, filtering, and JSON…

IDA plugins and scripts for analyzing register usage frame

Burp Suite JS Beautifier

WinDbg plugin for automated malware dynamic analysis and IOC extraction. Executes within the debugger to collect predefined indicators and writes…

Extract labels from IDA, Ghidra, Binary Ninja, and Relyze files and export x64dbg database. Including radare2 main address.

Executes at the silicon boundary