

miasm
 cea-sec/miasm
Reverse engineering framework in Python
binary-analysisdebuggersdynamic-analysis-sandboxing+3
cea-sec/miasmReverse engineering framework in Python
 cs01/gdbgui
Browser-based frontend to gdb (gnu debugger). Add breakpoints, view the stack, visualize data structures, and more in C, C++, Go, Rust, and Fortran.…
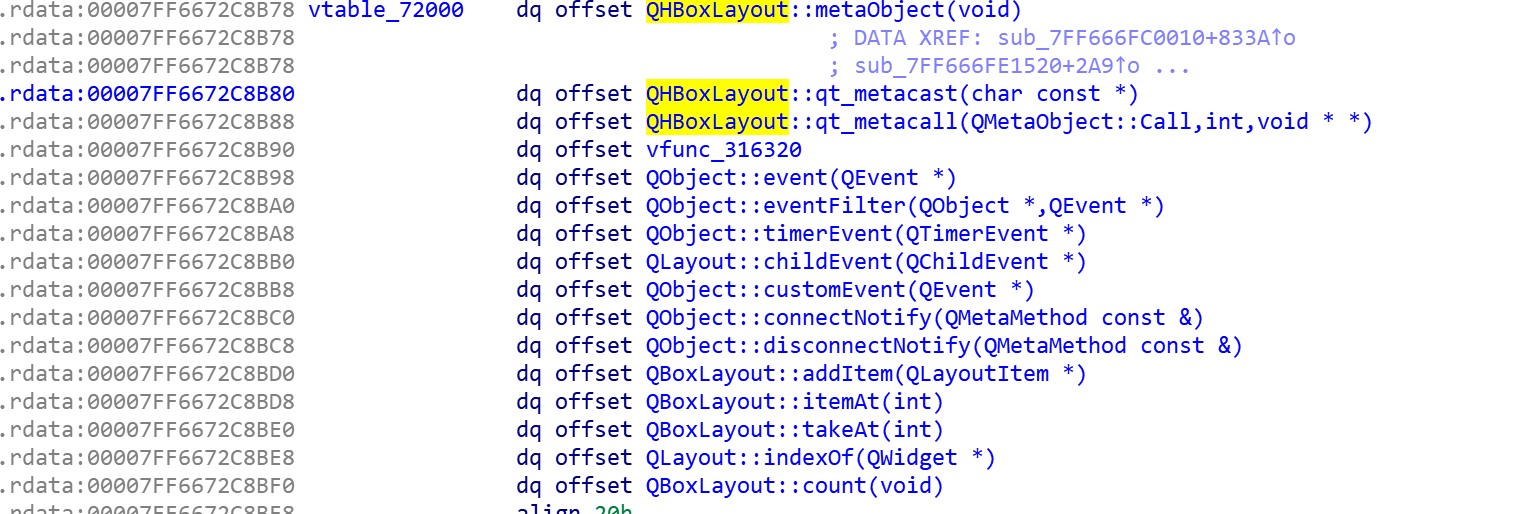 0xgalz/virtuailor
IDAPython tool for creating automatic C++ virtual tables in IDA Pro
 symgraph/ghidrassist
An LLM extension for Ghidra to enable AI assistance in RE.
 openrce/paimei
A reverse engineering framework written in Python.
 nickcano/xenoscan
Open source memory scanner written in C++
 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy that shows every real tool call between your AI client and your MCP servers, live in your terminal.
 skylined/bugid
Detect, analyze and uniquely identify crashes in Windows applications
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby
 allthingsida/idasql
Vibe Reverse Engineer with IDA SQL: An interface for IDA in SQL via live virtual tables
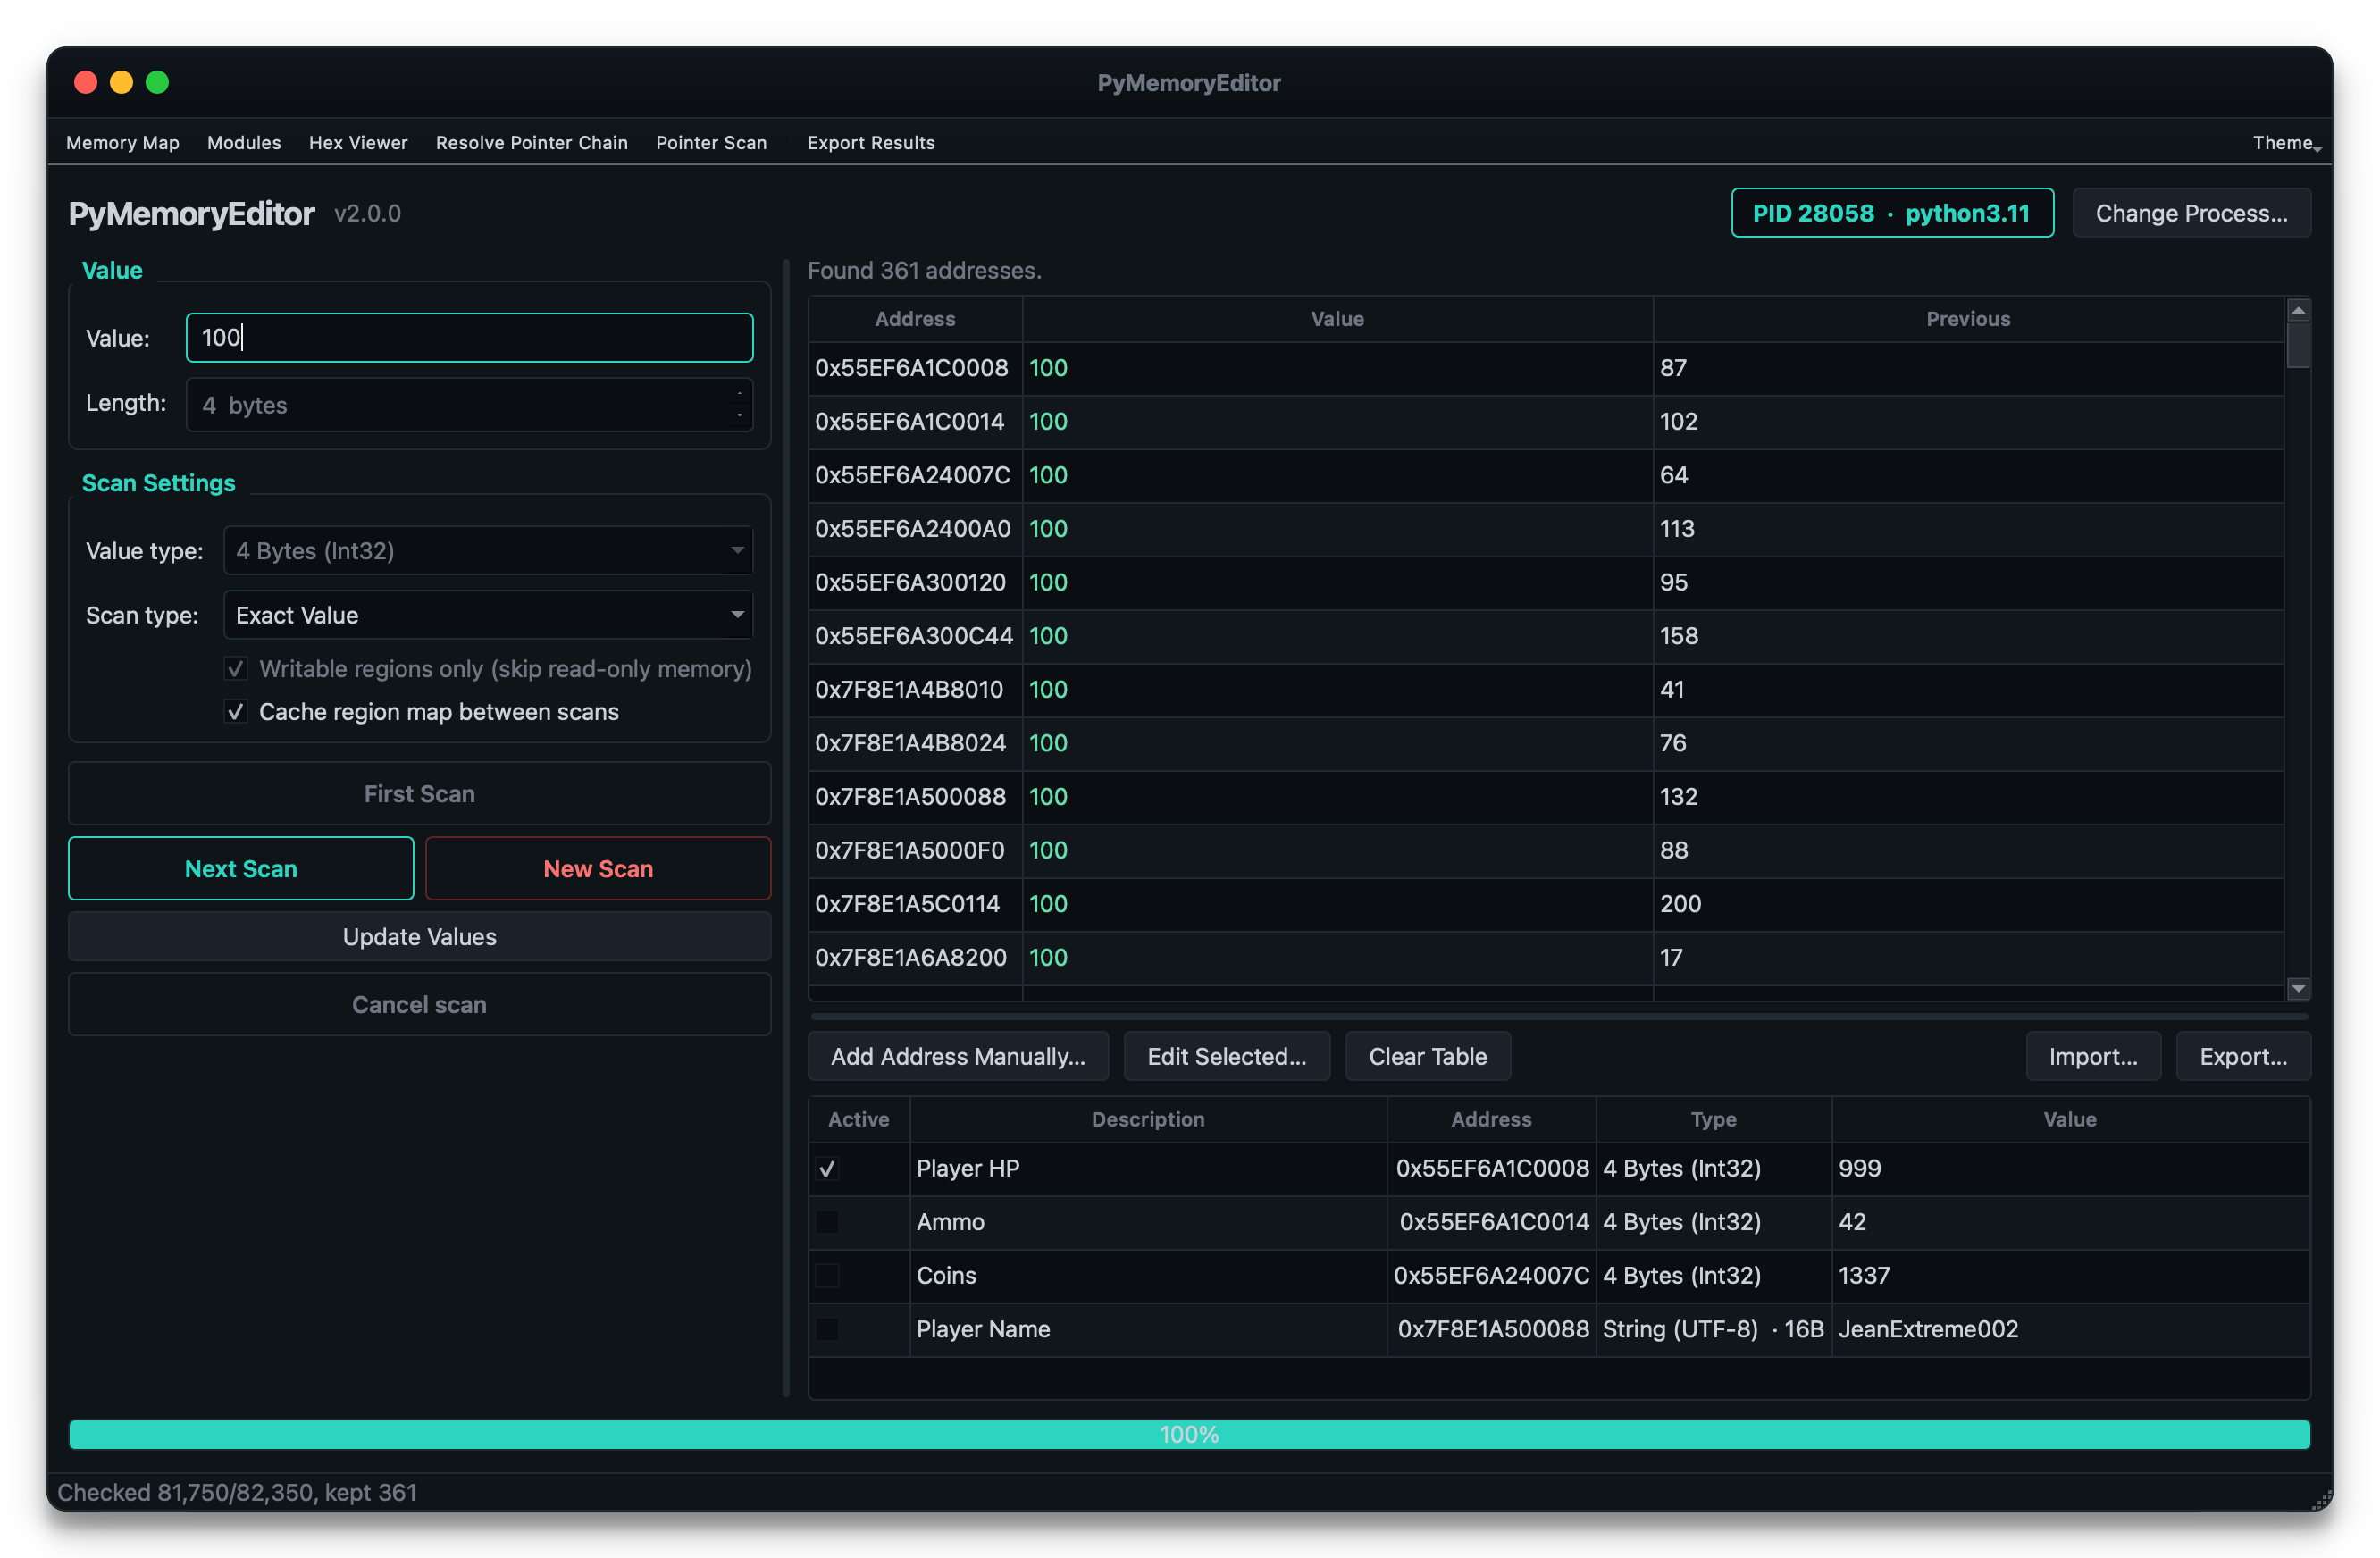 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 amossys/memitm
Tool to make in memory man in the middle
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
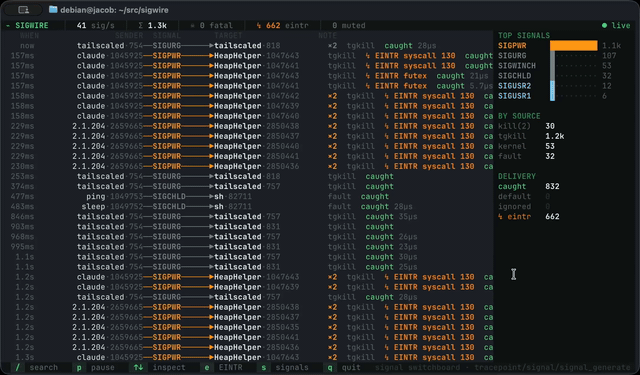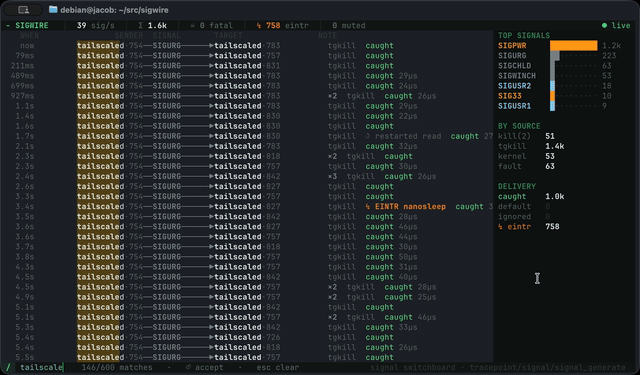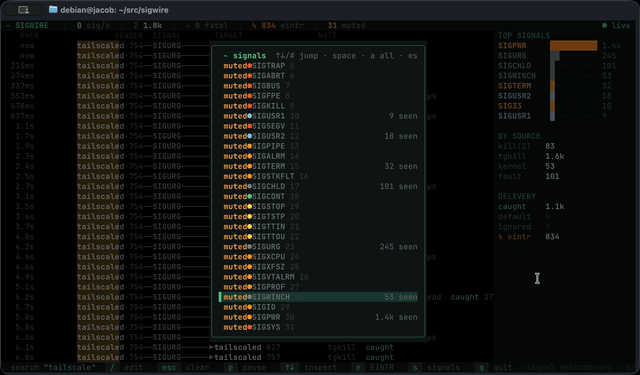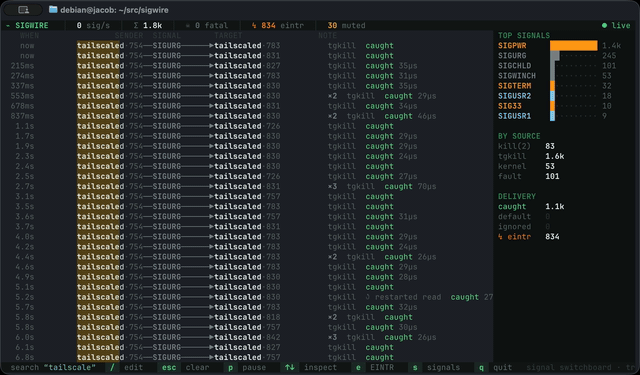 yeet-src/sigwire
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
 fortra/cve-2023-28252
Technical analysis and proof-of-concept exploit for CVE-2023-28252, a Windows Common Log File System (CLFS) driver privilege escalation vulnerability…
 ngwg/ceasta
disassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
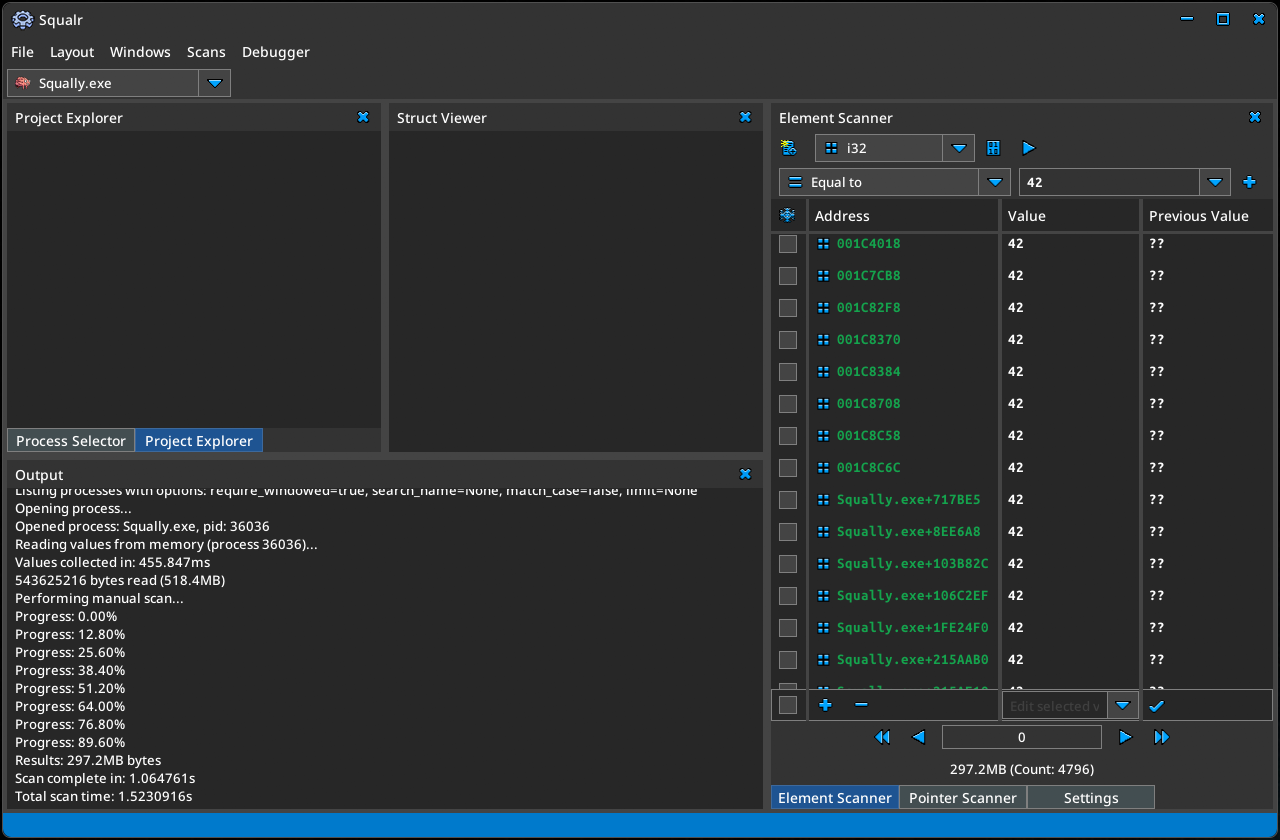 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…