
salt
 paolomonti42/salt
SALT - SLUB ALlocator Tracer for the Linux kernel
binary-analysisdebuggerseducation+2
paolomonti42/saltSALT - SLUB ALlocator Tracer for the Linux kernel
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
 gmh5225/asm-obfuscator
Obfuscates x86-64 assembly with instruction injection, junk code, constant obfuscation, and runtime decryption to hinder reverse engineering and…
 t00sh/rop-tool
A tool to help you write binary exploits
 amossys/memitm
Tool to make in memory man in the middle
 jhftss/ida2obj
Static binary instrumentation tool that dumps COFF object files from executables, enabling code/data insertion at any location for black-box fuzzing…
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
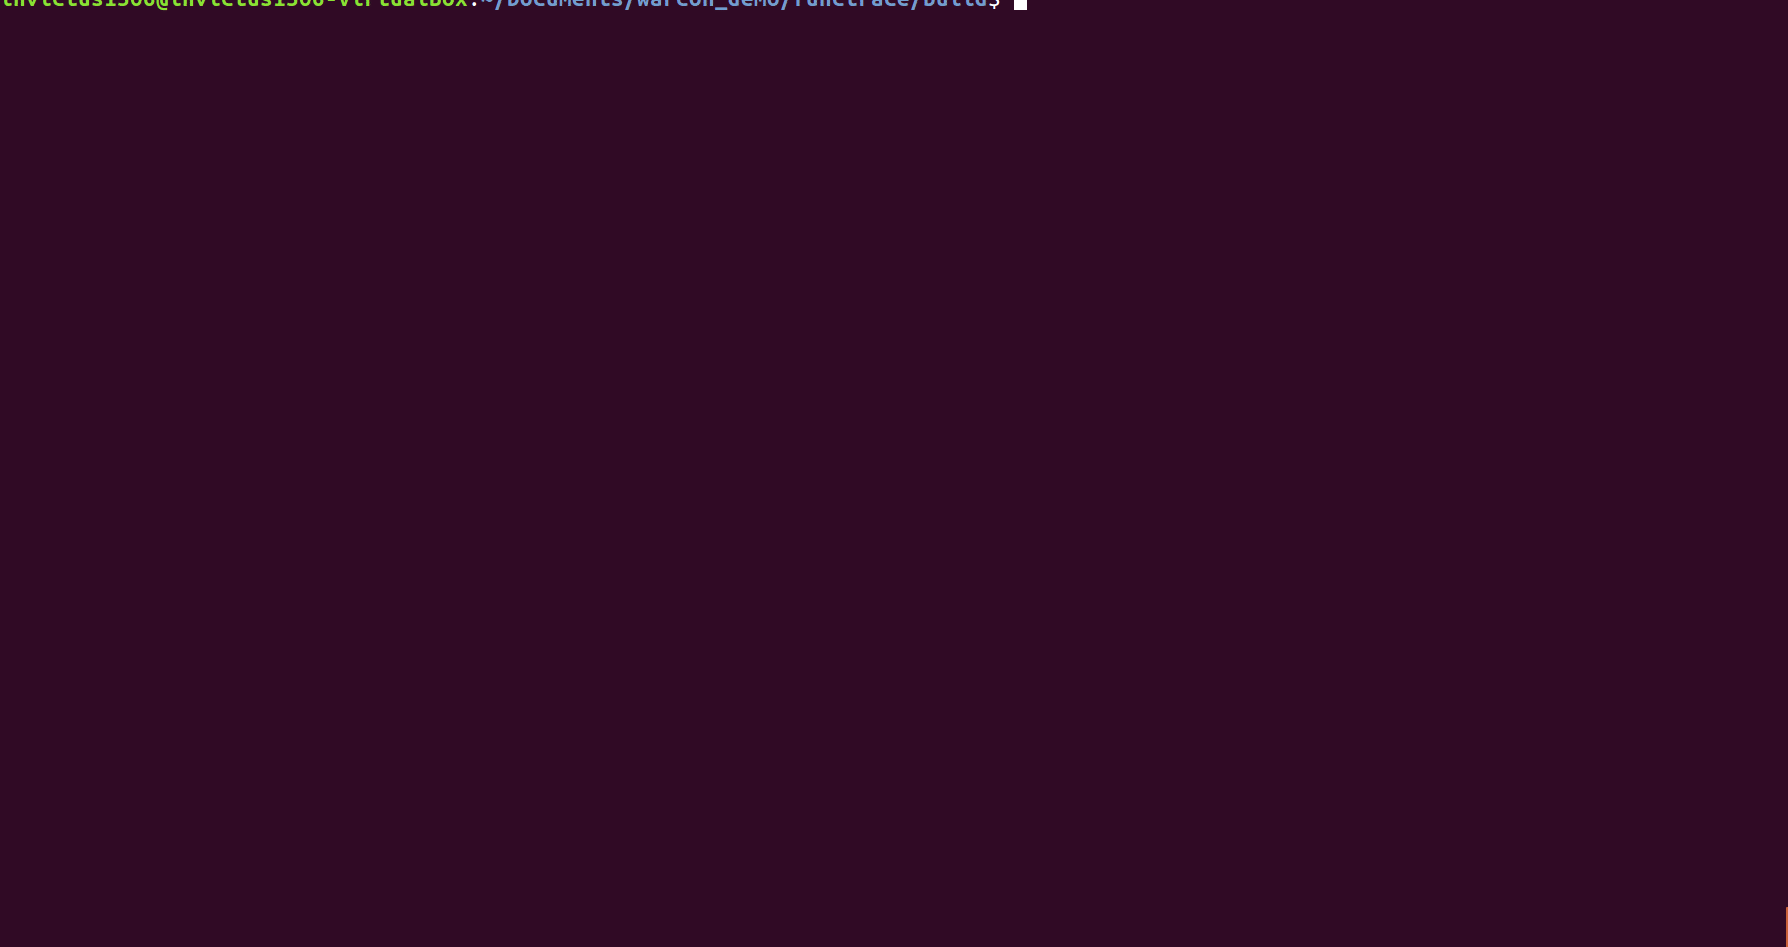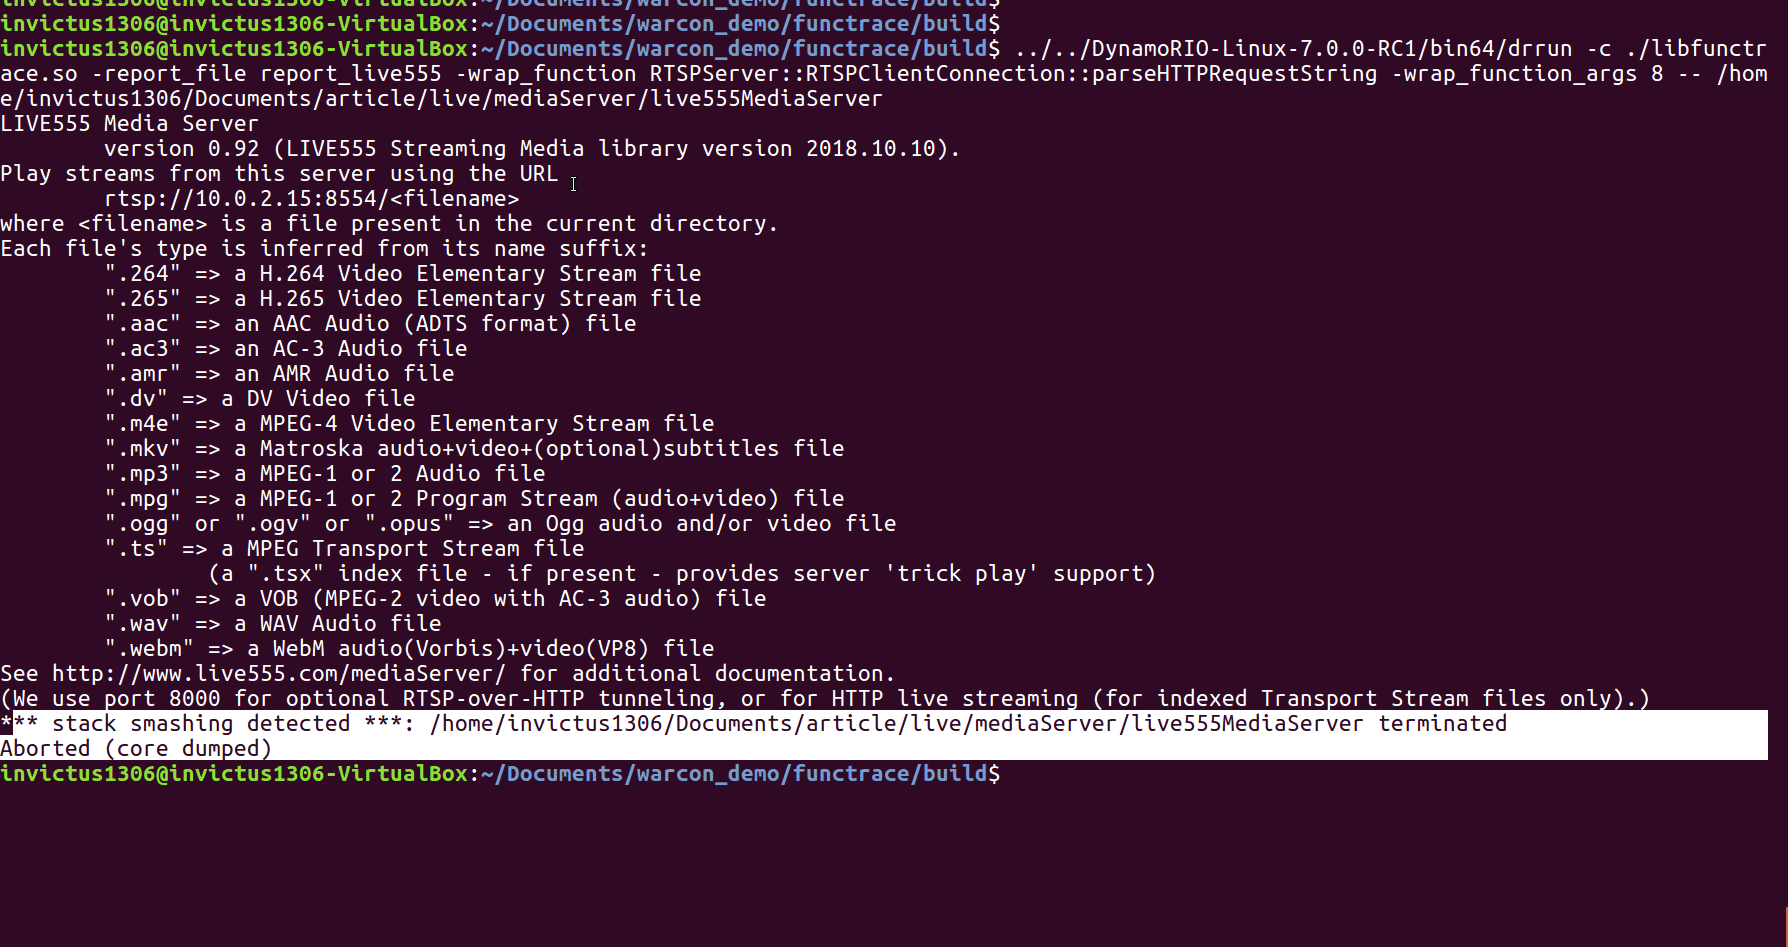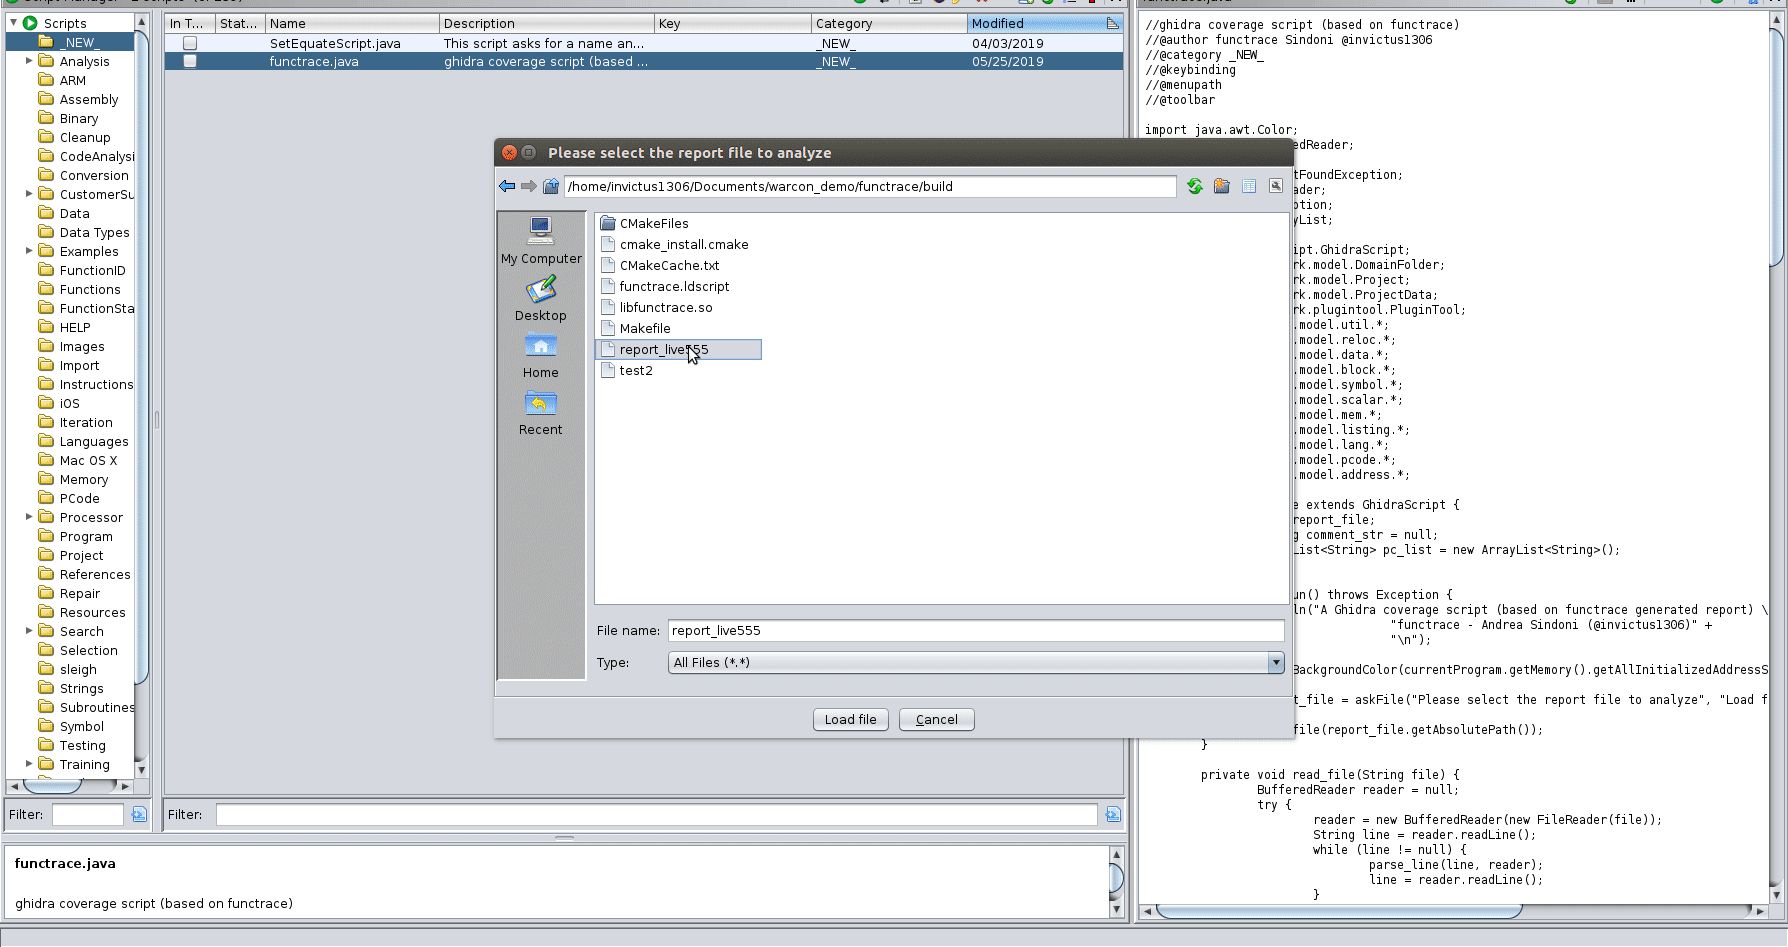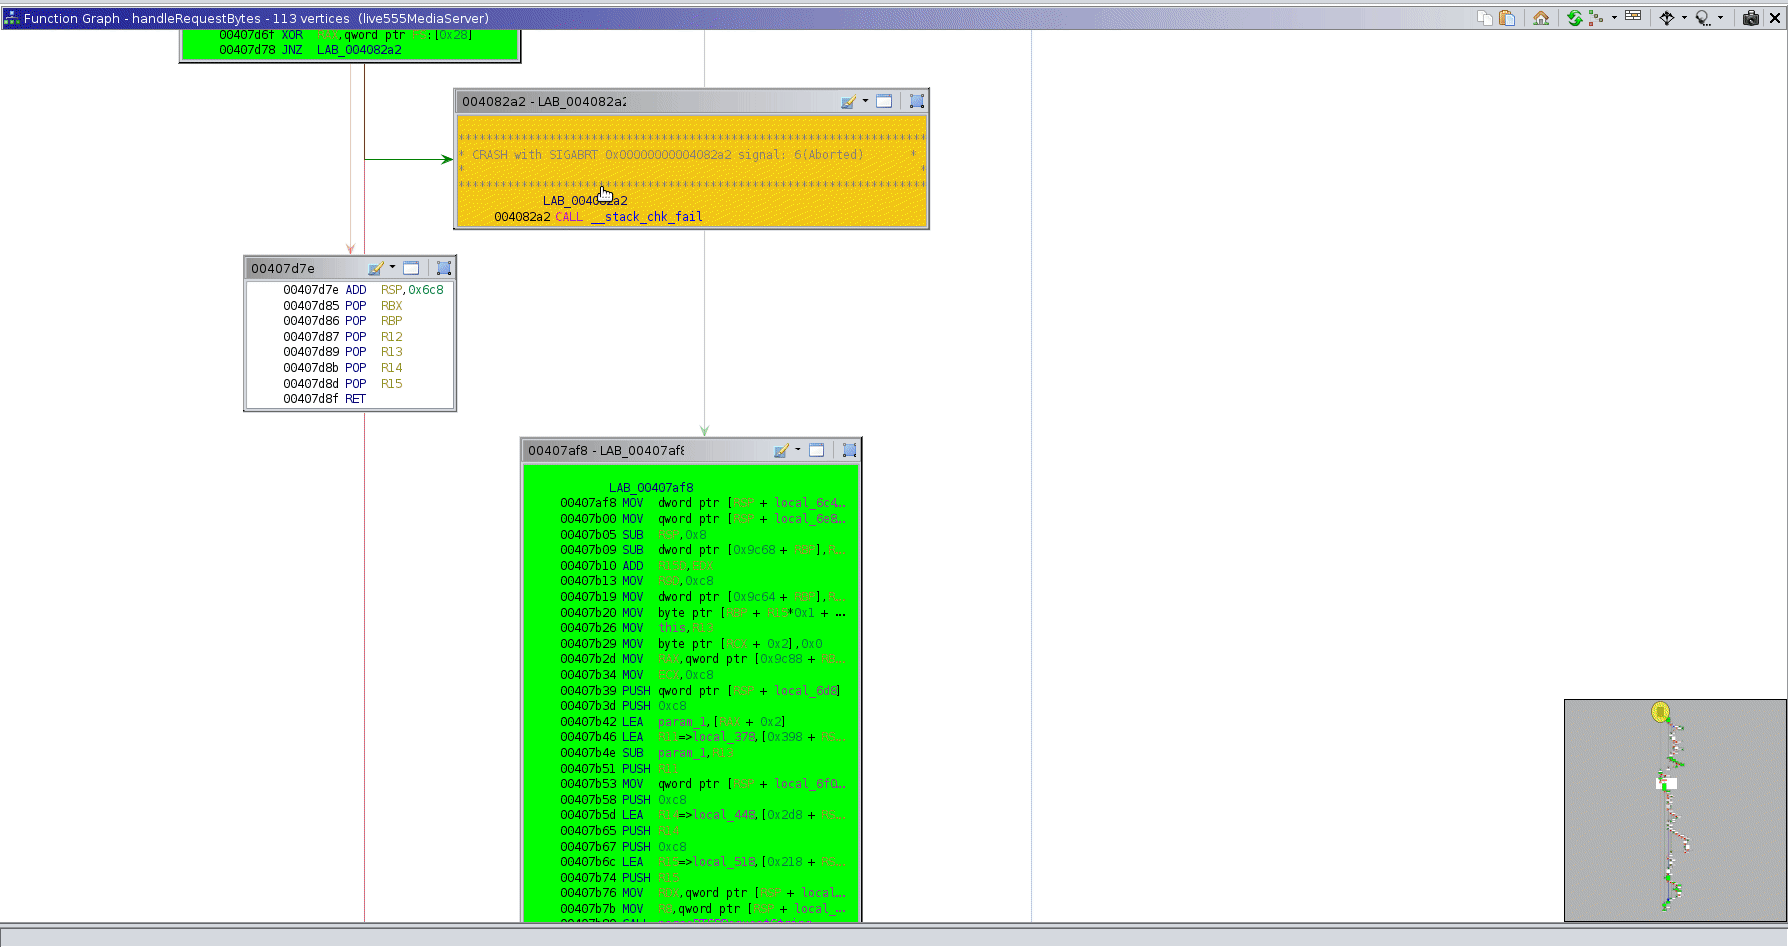 invictus1306/functrace
A function tracer
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 nccgroup/asatools
Main repository to pull all NCC Group Cisco ASA-related tool projects.
 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
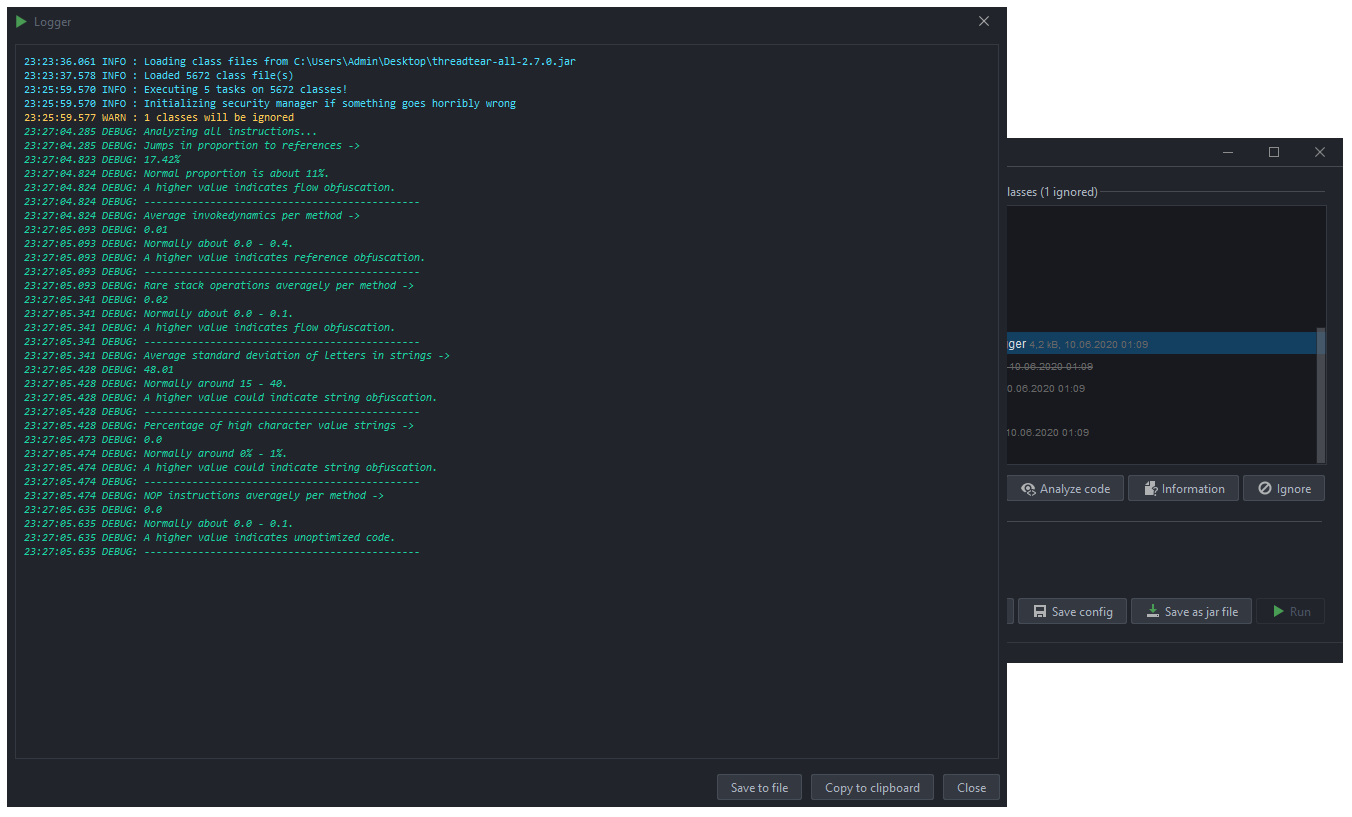 loerting/threadtear
Multifunctional java deobfuscation tool suite
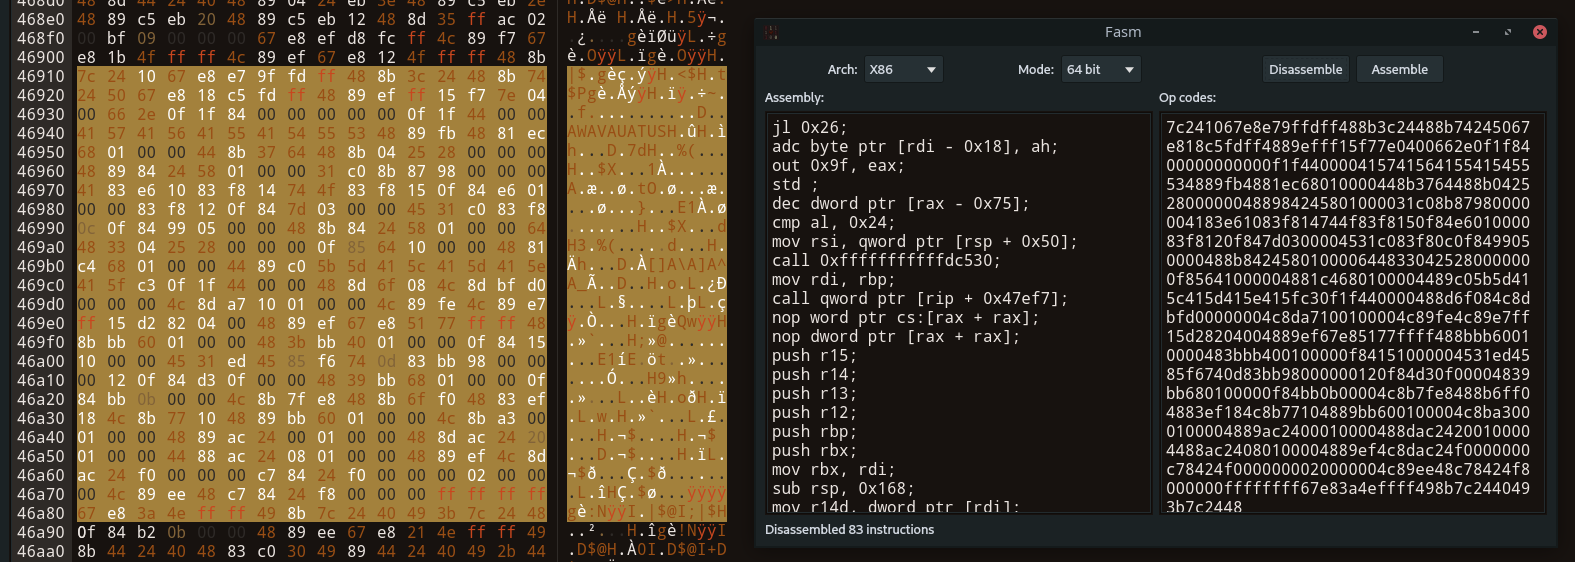 echo-devim/fhex
A Full-Featured HexEditor compatible with Linux/Windows/MacOS

 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 k2/ehtrace
ATrace is a tool for tracing execution of binaries on Windows.