
strace
 strace/strace
Linux syscall tracer using ptrace to monitor, debug, and analyze system calls, signal deliveries, and process state changes for diagnostics and…
debuggersdynamic-analysis-sandboxinggeneral-purpose-utilities
strace/straceLinux syscall tracer using ptrace to monitor, debug, and analyze system calls, signal deliveries, and process state changes for diagnostics and…
 amossys/memitm
Tool to make in memory man in the middle
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
 davidcarliez/cve-2026-62737-lab
Elevates a low-privilege Windows process to SYSTEM via a gdb-assisted ROP token-swap chain, demonstrating CVE-2026-62737 in a lab-only QEMU…
 googleprojectzero/tinyinst
A lightweight dynamic instrumentation library
 structio-labs/n0xis
AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).
 swdunlop/andbug
Scriptable debugger for Android Dalvik VM using JDWP/DDM interfaces to hook methods, inspect process state, and modify runtime behavior without…
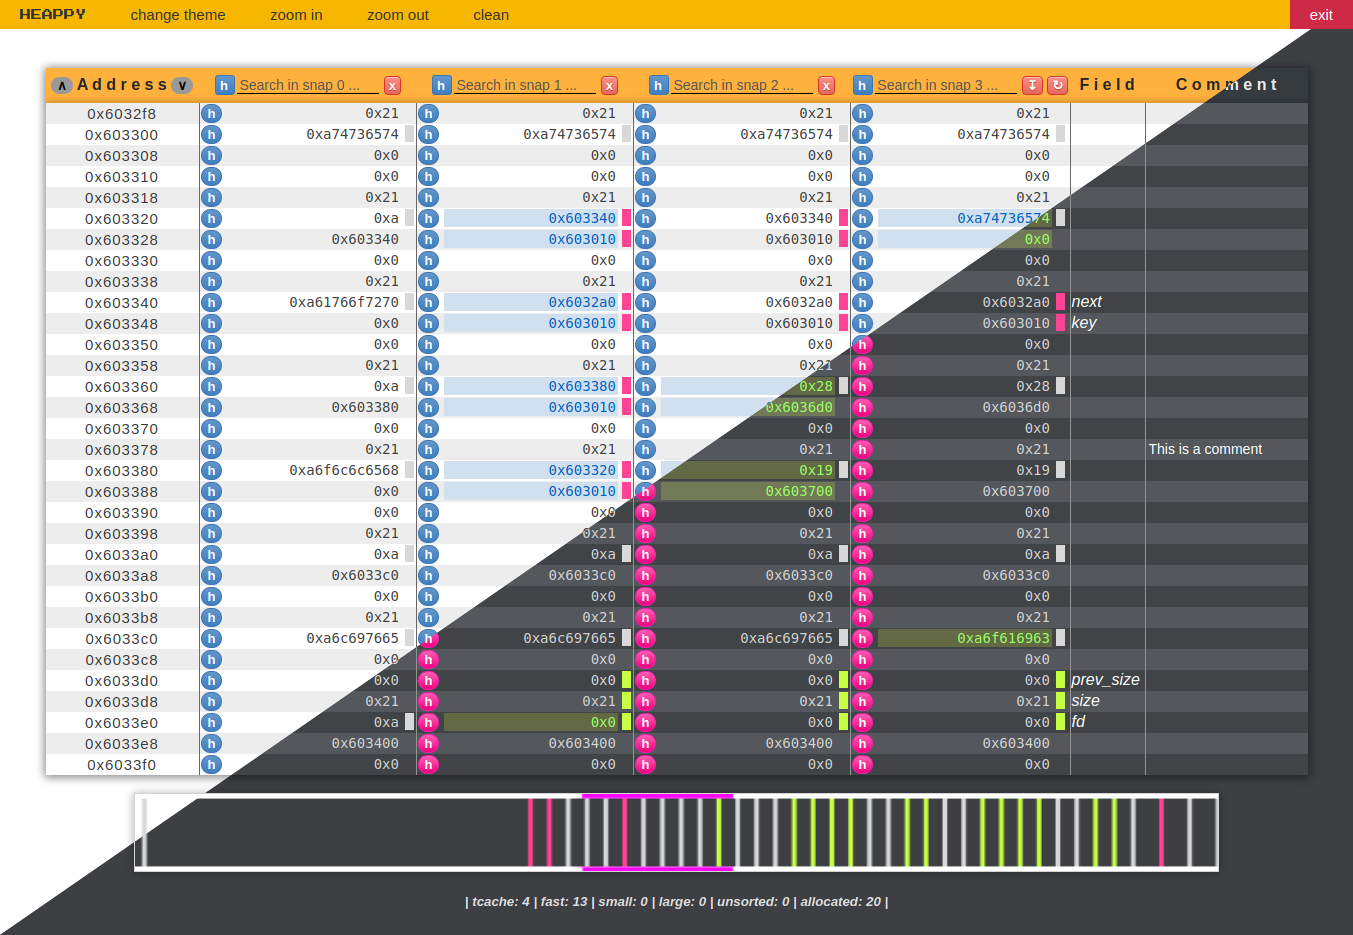 gand3lf/heappy
A happy heap editor to support your exploitation process :slightly_smiling_face:
 enkomio/thematrix
a PE Loader and Windows API tracer. Useful in malware analysis.
 thalium/icebox
Virtual Machine Introspection, Tracing & Debugging
 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 sadopc/machscope
All-in-one macOS binary analysis: Mach-O parsing, ARM64 disassembly, code signatures, and debugging.
 mfthomps/resim
Reverse engineering software using a full system simulator
 zodiacon/alltools
All reasonably stable tools
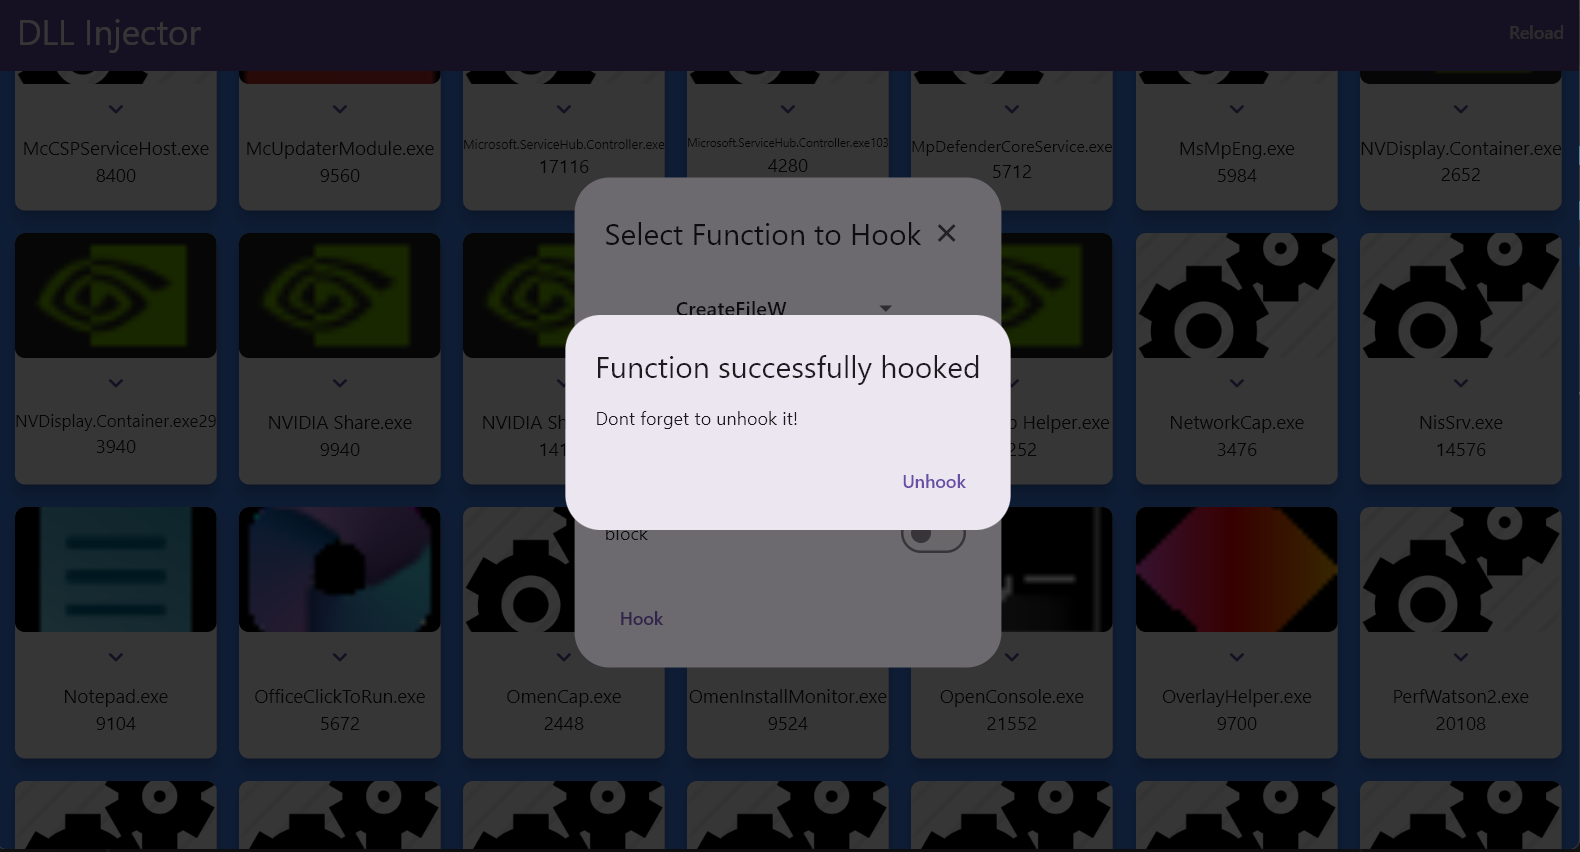 yasharote/dll-injector
A desktop tool that allows injecting DLLs, hooking WinAPI functions like CreateFileW, and modifying process behavior at runtime — designed for…
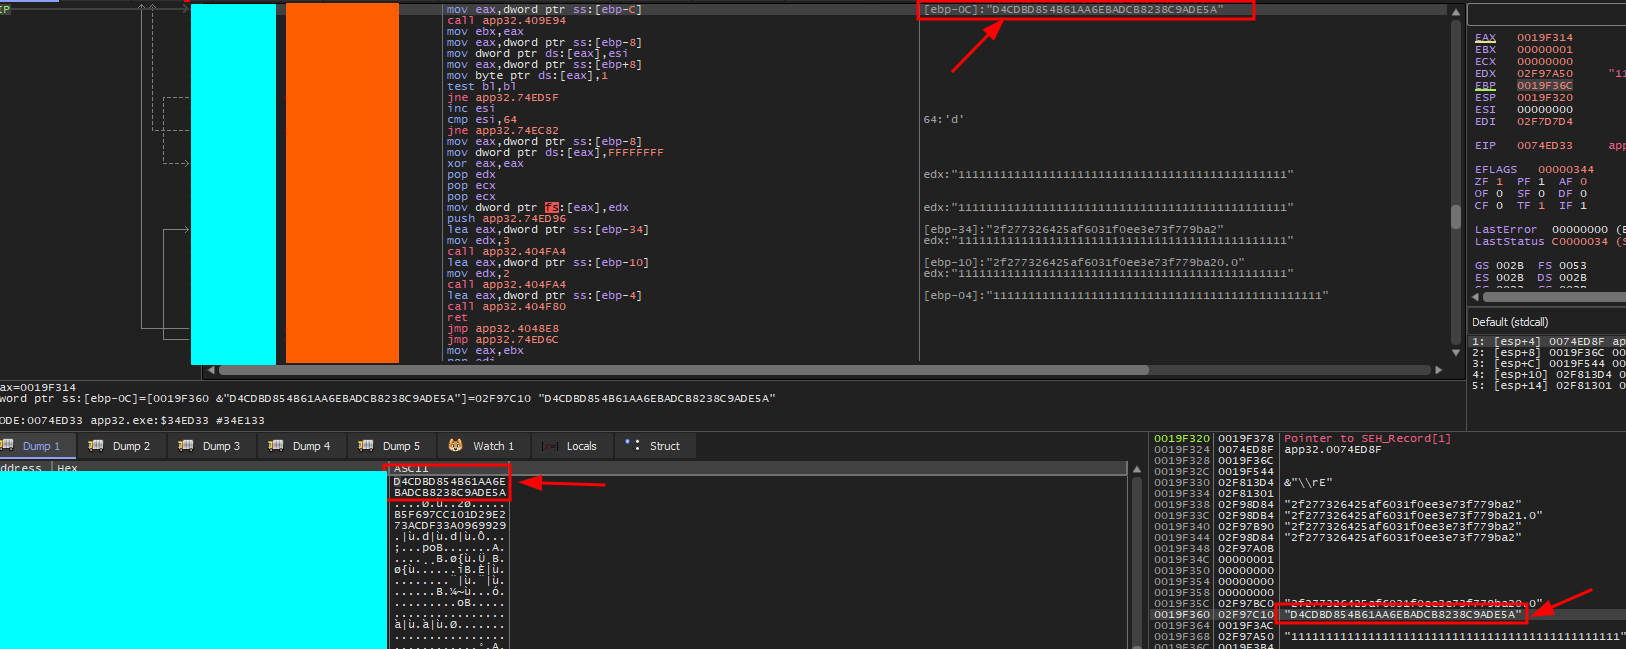 smarttfoxx/cve-2025-60791
Easywork Enterprise 2.1.3.354 is vulnerable to Cleartext Storage of Sensitive Information in Memory. The application leaves valid device-bound…
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 sneakynachos/cve-2026-85048-the-gpu-died
Reproducer and technical analysis for CVE-2026-85048, a Chrome viz surface use-after-free in the GPU process, with ASAN unit tests and browser…