

TangledWinExec
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
adversarial-attackdebuggersids-ips-evasion+6
957
daem0nc0re/tangledwinexecPoCs and tools for investigation of Windows process execution techniques
 rad9800/hwbp4mw
Hardware breakpoint hooking engine for Windows that uses debug registers to hook functions, bypass ETW/AMSI, and evade user-land EDR monitoring.
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 gallopsled/pwntools
CTF framework and exploit development library
 angr/angr
A powerful and user-friendly binary analysis platform!
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 darthton/blackbone
Windows memory hacking library
 longld/peda
PEDA - Python Exploit Development Assistance for GDB
 fuzzysecurity/powershell-suite
My musings with PowerShell
 fabiobaroni/awesome-exploit-development
A curated list of resources (books, tutorials, courses, tools and vulnerable applications) for learning about Exploit Development
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
 meckazin/chromekatz
Dump cookies and credentials directly from Chrome/Edge process memory
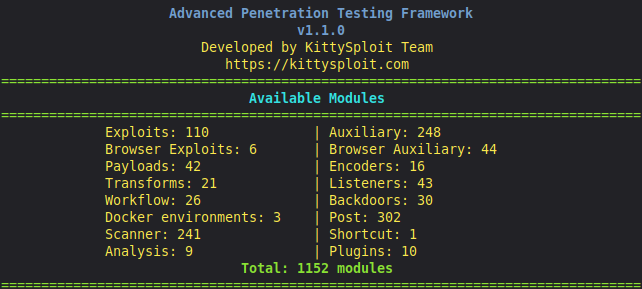 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 openrce/paimei
A reverse engineering framework written in Python.
 0xm3r/cgpwn
A lightweight VM for hardware hacking, RE (fuzzing, symEx, exploiting etc) and wargaming tasks
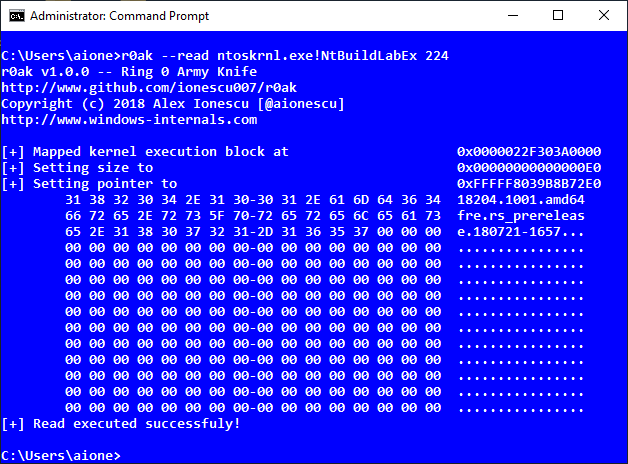 harryanon/r0ak
Windows command-line utility for reading, writing, and executing kernel-mode code from Administrator context using a font validation execution…
 kangtastic/cve-2019-2215
Temproot for Pixel 2 and Pixel 2 XL via CVE-2019-2215