

 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
 icsharpcode/ilspy
.NET Decompiler with support for PDB generation, ReadyToRun, Metadata (&more) - cross-platform!
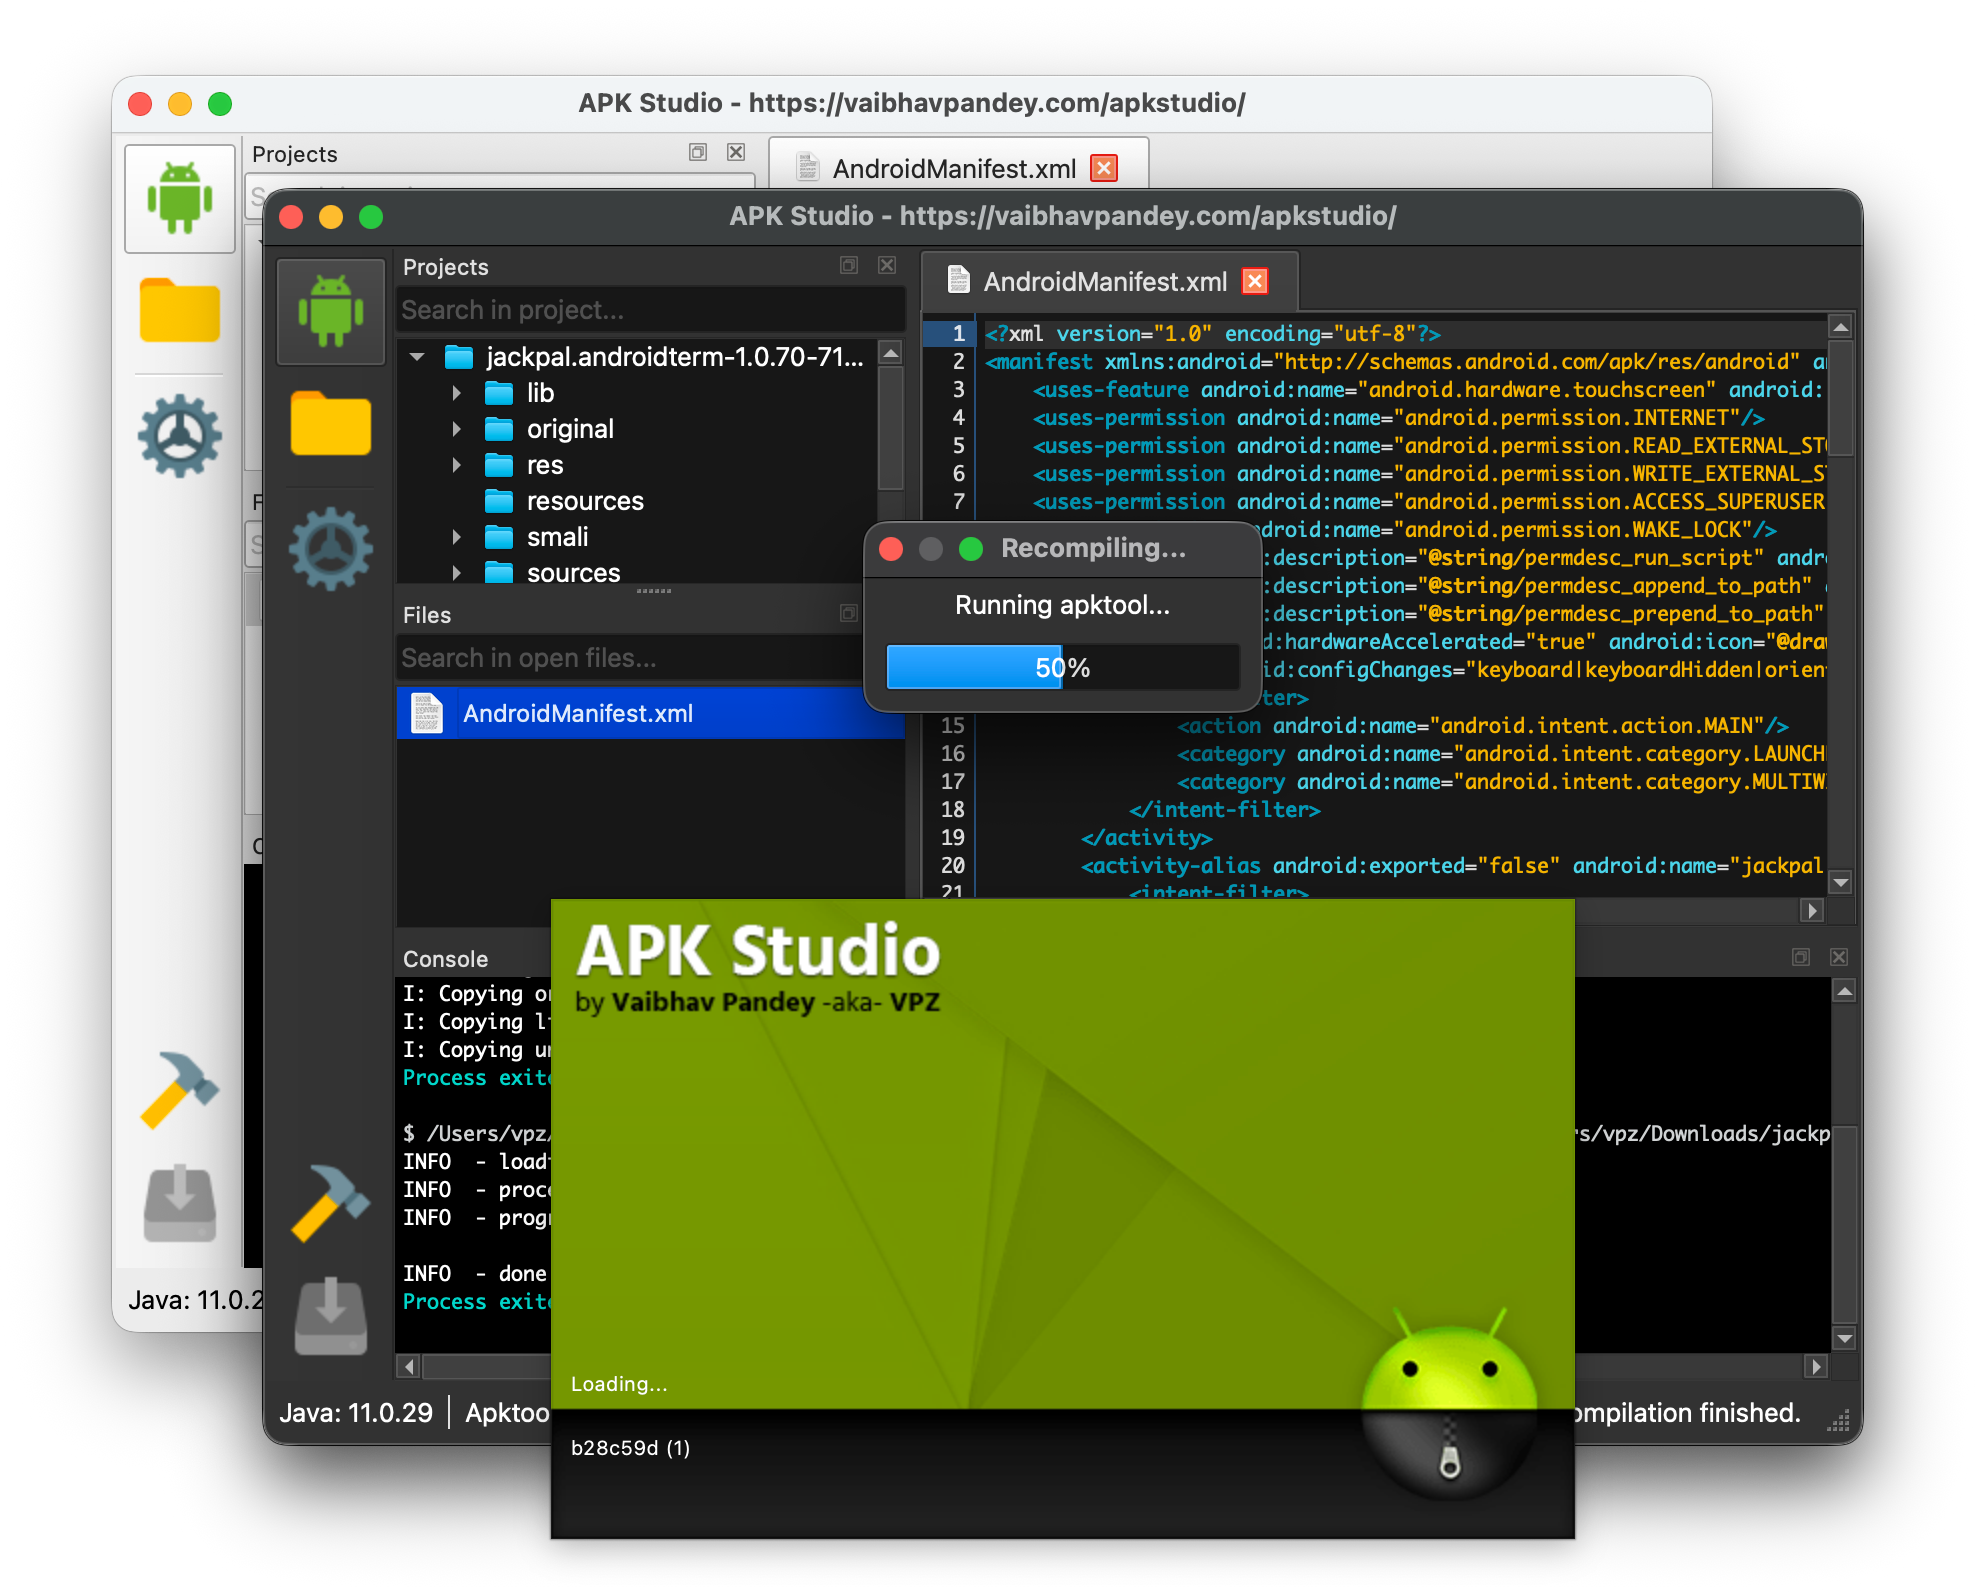 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 shaikusaf/linux-4.19.72_cve-2020-14356
Linux kernel source tree modified for CVE-2020-14356, providing a reference for vulnerability analysis and exploitation research.
 shaikusaf/linux-4.19.72_cve-2020-10757
Linux kernel source tree modified to demonstrate CVE-2020-10757, a use-after-free vulnerability in the AF_PACKET socket, for educational and research…
 satheesh575555/linux-4.1.15_cve-2022-45934
Linux kernel 4.1.15 source code with a focus on CVE-2022-45934, providing a reference for vulnerability analysis and exploitation research.
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
 momo5502/sogen
🪅 Windows & Linux userspace emulator
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 0xricksanchez/like-dbg
Fully dockerized Linux kernel debugging environment for Linux and MacOS
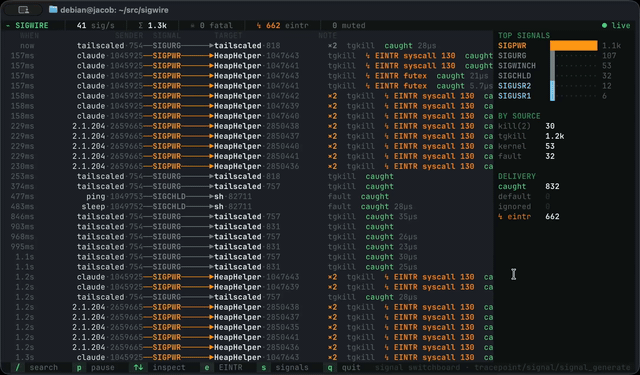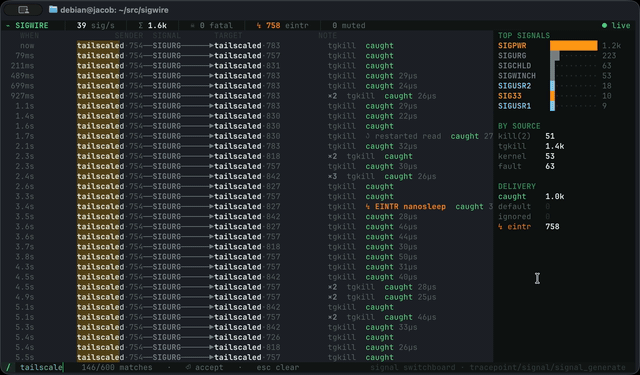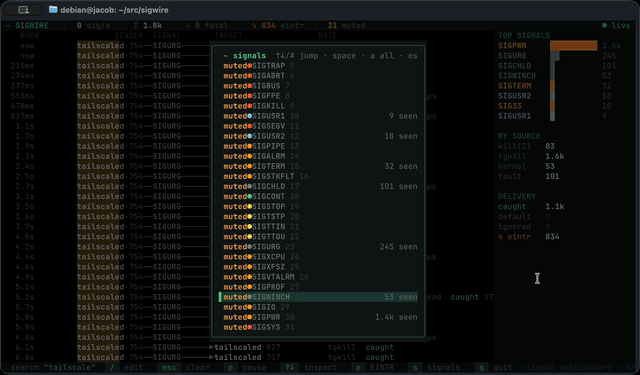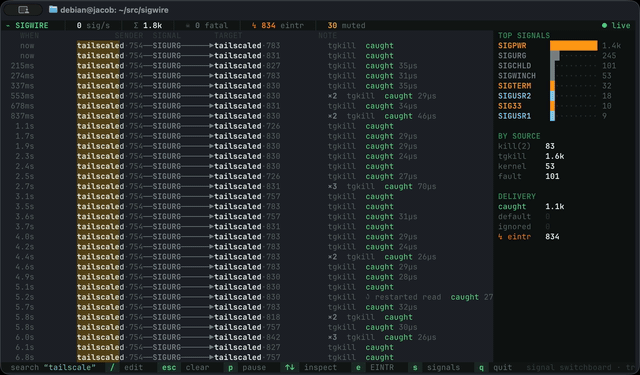 yeet-src/sigwire
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
 wkoszek/emuko
RISC-V emulator in Rust that boots Linux with JIT on ARM64/x86_64 and Sv39 virtual memory
 catern/rsyscall
Process-independent interface to Linux system calls
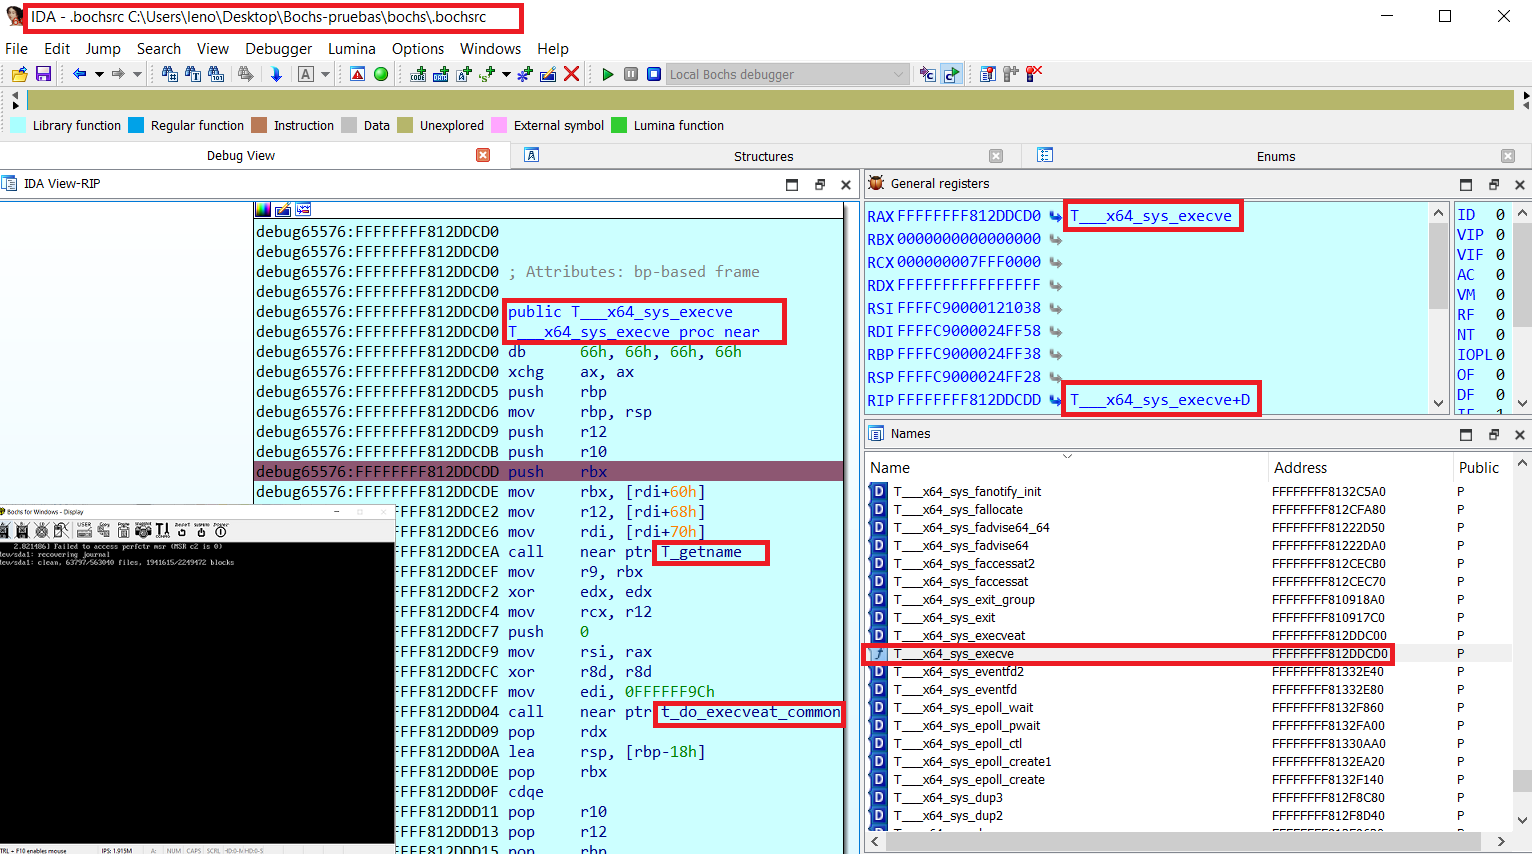 therealdreg/bochs_linux_kernel_debugging
Tools for Linux kernel debugging on Bochs (including symbols, native Bochs debugger and IDA PRO)
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool