
CVE-2018-1000199
 dsfau/cve-2018-1000199
Proof-of-concept exploit for Linux kernel ptrace debug register corruption (CVE-2018-1000199), demonstrating incorrect error handling in breakpoint…
binary-exploitationdebuggersexploitation+1
dsfau/cve-2018-1000199Proof-of-concept exploit for Linux kernel ptrace debug register corruption (CVE-2018-1000199), demonstrating incorrect error handling in breakpoint…
 ngtuonghung/cve-2022-27666
Heap buffer overflow exploit for CVE-2022-27666 in Linux kernel IPsec ESP6 implementation. Includes kernel build, debug setup with GDB stub, and…
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 nidhihcl/linux-4.19.72_cve-2022-29581
Linux kernel 4.19.72 with a targeted patch or exploit for CVE-2022-29581, demonstrating a specific kernel vulnerability for security research and…
 nccgroup/libslub
Python library for examining Linux kernel SLUB heap allocations and structures within GDB, enabling deeper understanding of kernel heap internals for…
 momo5502/sogen
🪅 Windows & Linux userspace emulator
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
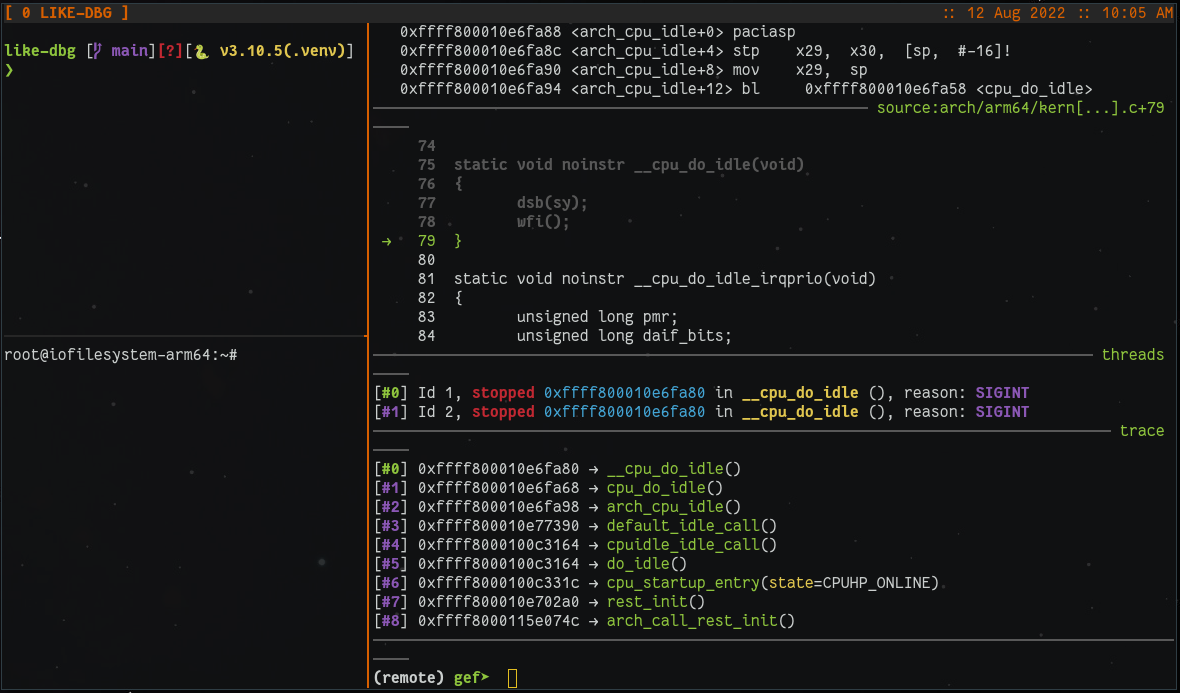 0xricksanchez/like-dbg
Fully dockerized Linux kernel debugging environment
 wkoszek/emuko
RISC-V emulator in Rust that boots Linux with JIT on ARM64/x86_64 and Sv39 virtual memory
 catern/rsyscall
Process-independent interface to Linux system calls
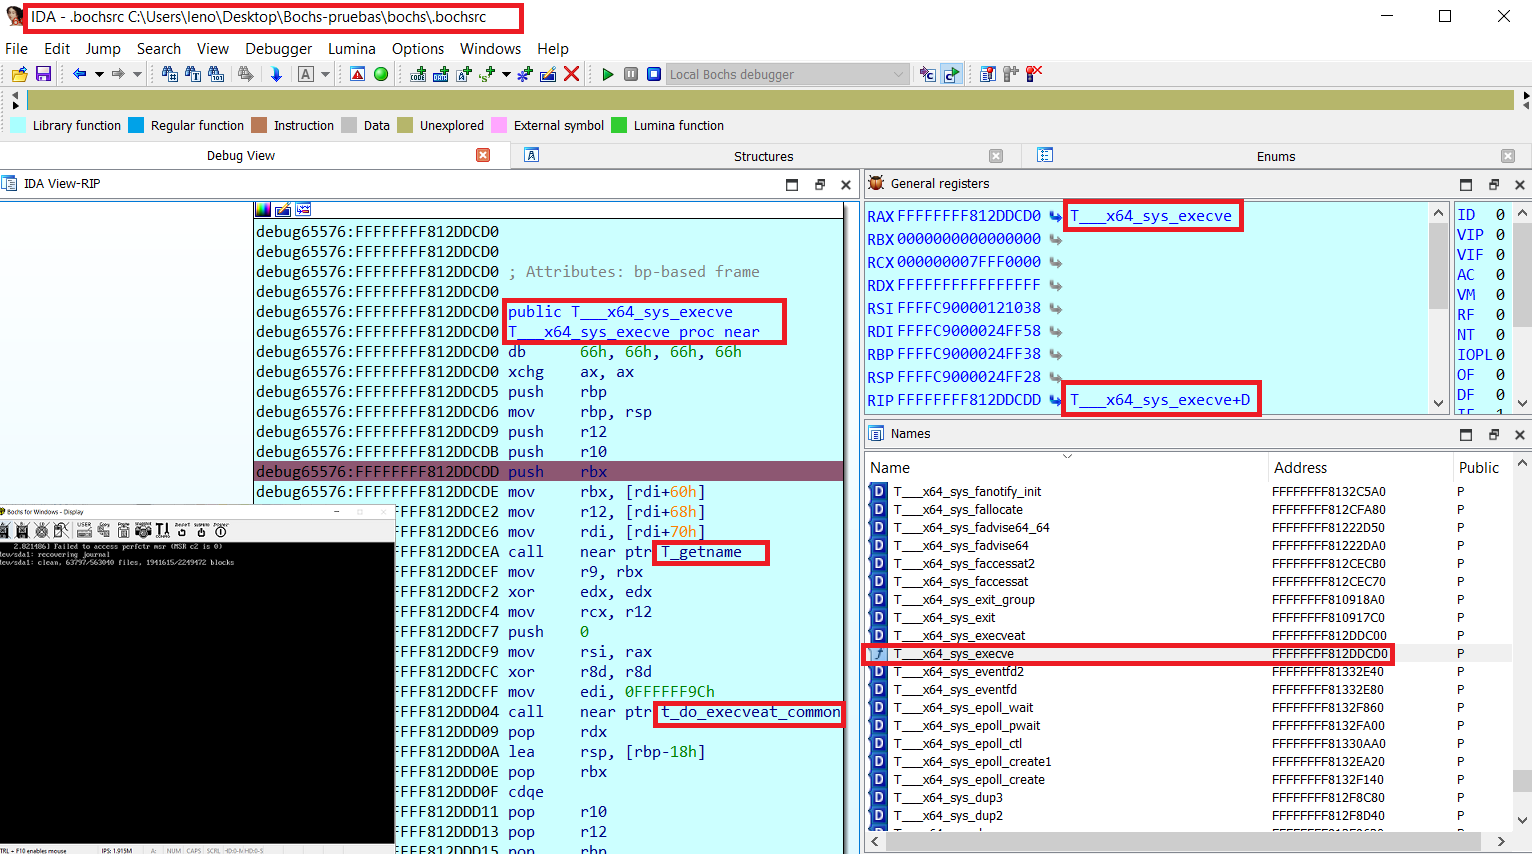 therealdreg/bochs_linux_kernel_debugging
Tools for Linux kernel debugging on Bochs (including symbols, native Bochs debugger and IDA PRO)
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
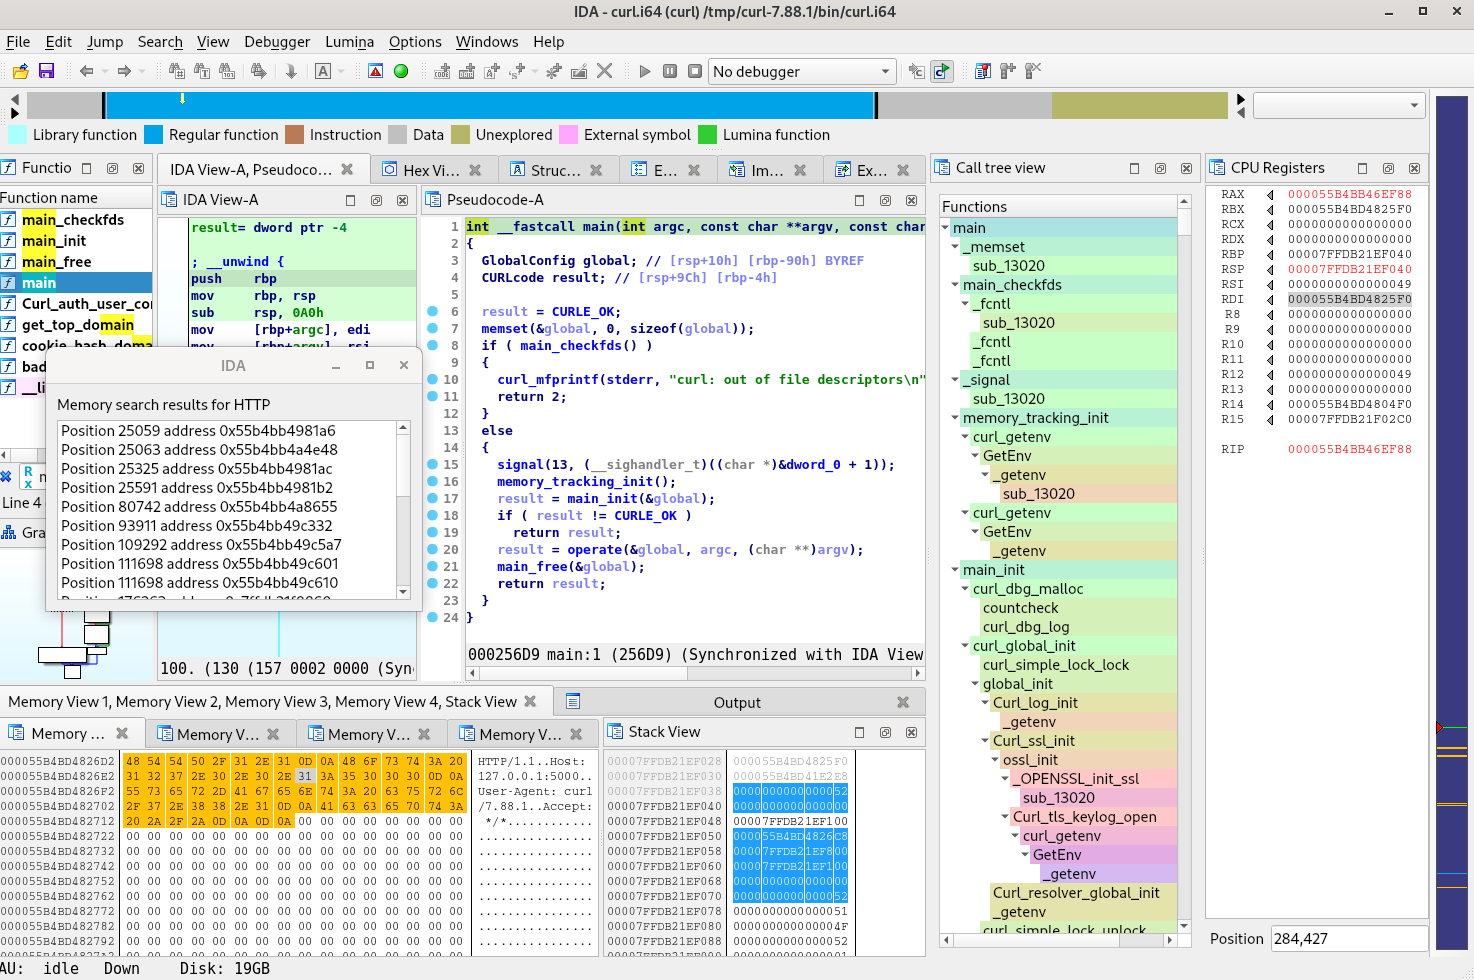 synacktiv/frinet
Frida-based tracer for easier reverse-engineering on Android, iOS, Linux, Windows and most related architectures.
 yhs0602/android-disassembler
Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
 paolomonti42/salt
SALT - SLUB ALlocator Tracer for the Linux kernel
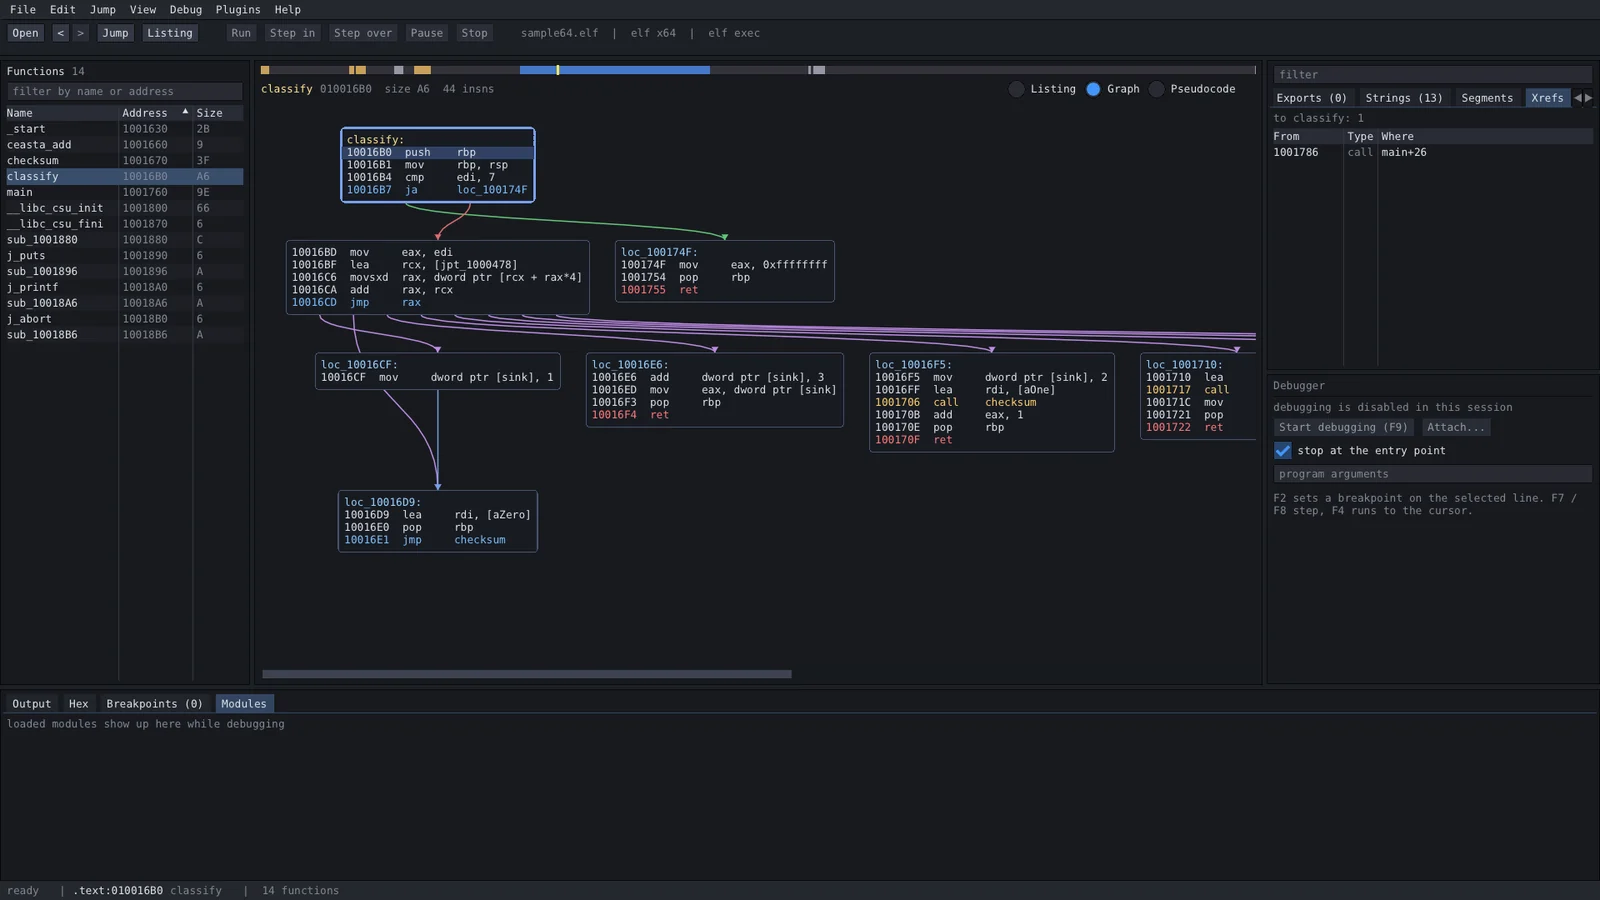 ngwg/ceasta
disassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
 packtpublishing/learning-linux-binary-analysis
Learning Linux Binary Analysis, published by Packt