MemITM
 amossys/memitm
Tool to make in memory man in the middle
binary-analysisdebuggersdynamic-analysis-sandboxing+4
amossys/memitmTool to make in memory man in the middle
 gmh5225/hooktools
Basic injectable for analyzing the behavior of evasive malware
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 isecpartners/introspy-ios
Security profiling for blackbox iOS
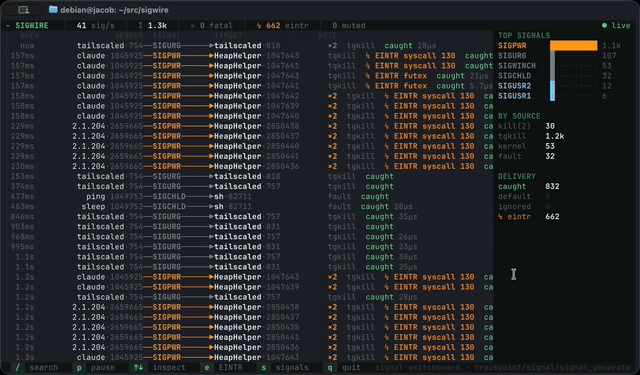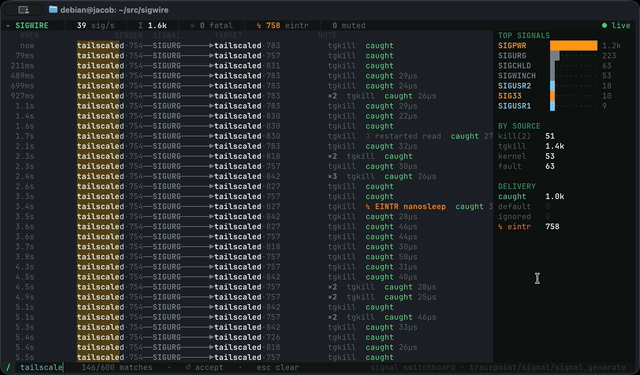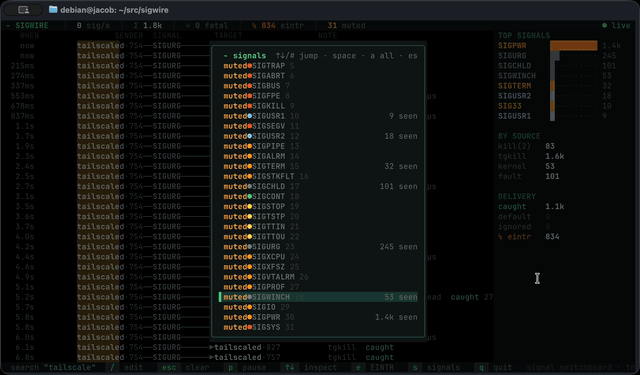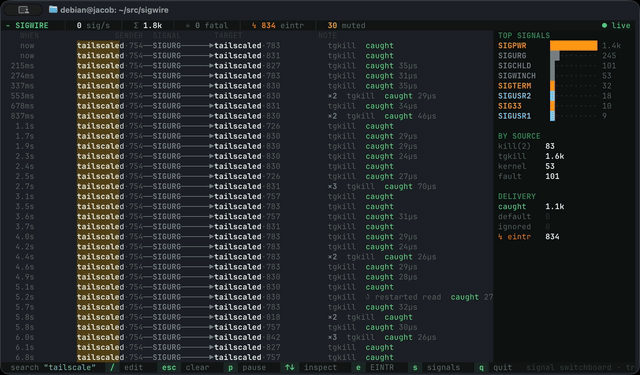 yeet-src/sigwire
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
 skylined/bugid
Detect, analyze and uniquely identify crashes in Windows applications
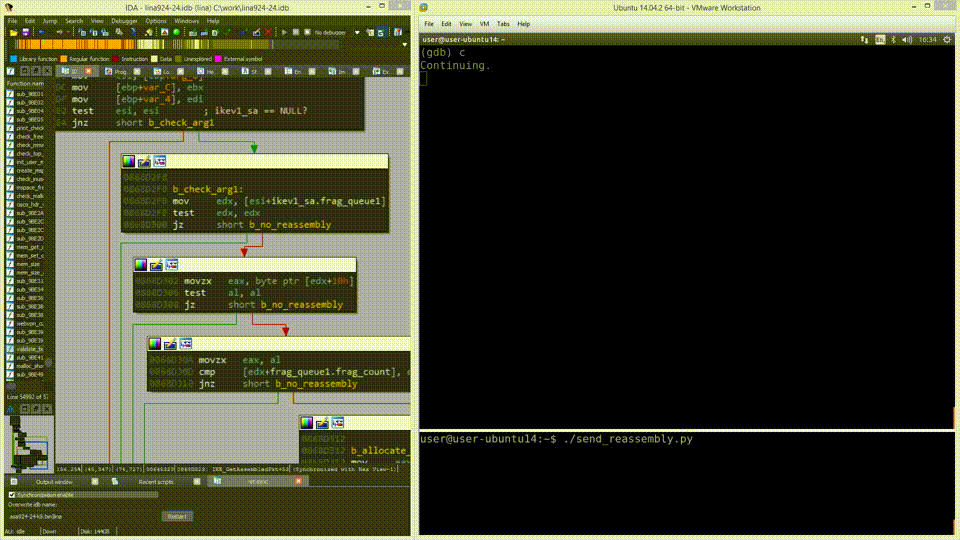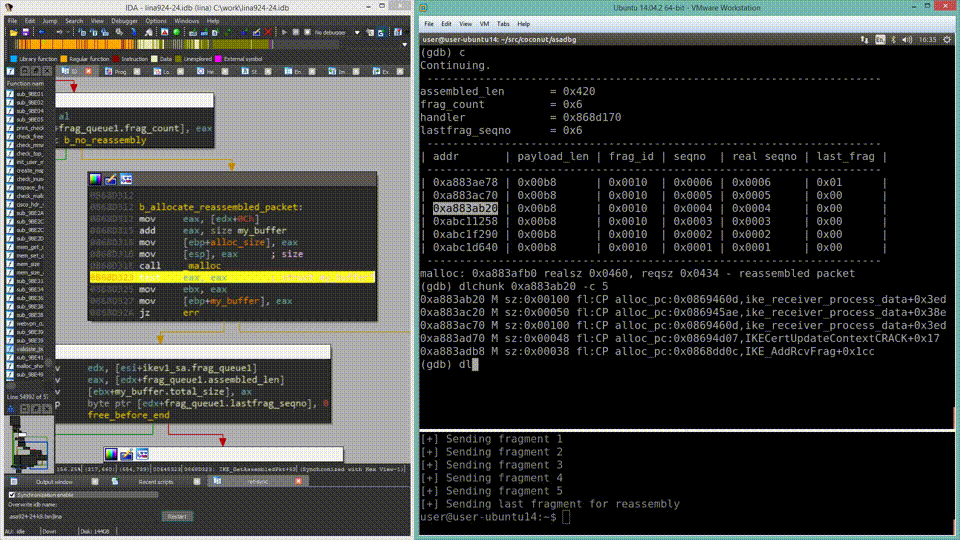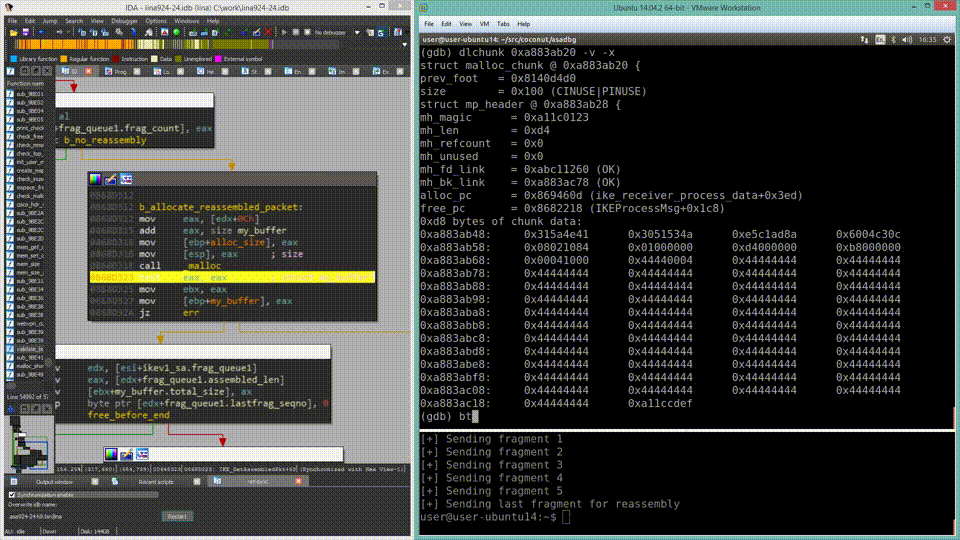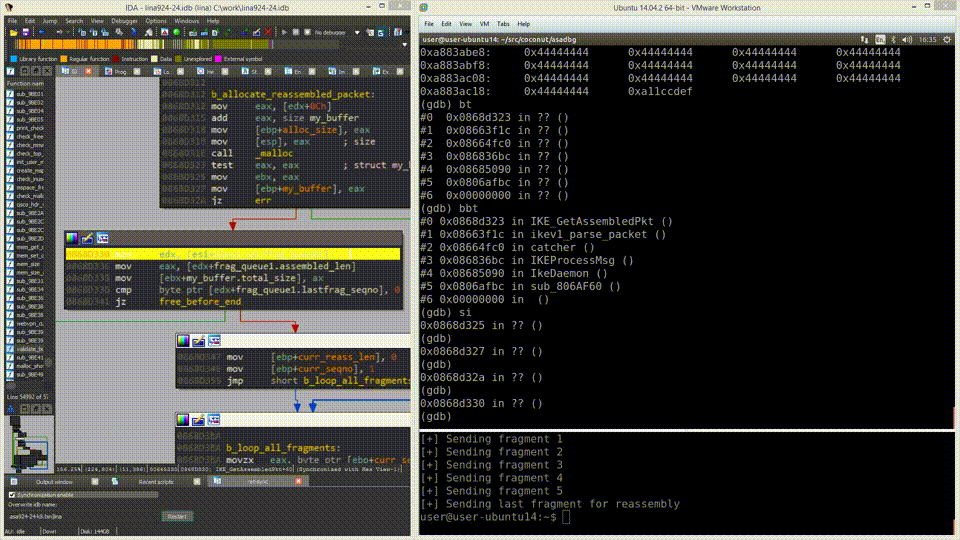 nccgroup/asadbg
asadbg is a framework of tools to aid in automating live debugging of Cisco ASA devices
 ioactive/jdwp-shellifier
Exploitation script for exposed Java Debug Wire Protocol (JDWP) services, enabling pentesters to inject Java code and execute arbitrary OS commands…
 jaf0rk/cve-2026-5281
Proof-of-concept exploit for CVE-2026-5281, a heap-use-after-free vulnerability in Chromium's Dawn WebGPU implementation, with ASAN log and build…
 vrikodar/cve-2003-0264_exploit
Buffer Overflow in Seattle Lab Mail (SLmail) 5.5 - POP3
 irsdl/burpsuitejsbeautifier
Burp Suite JS Beautifier
 atlas0fd00m/vivisection
Analysis Plugin and Tools for Vivisect
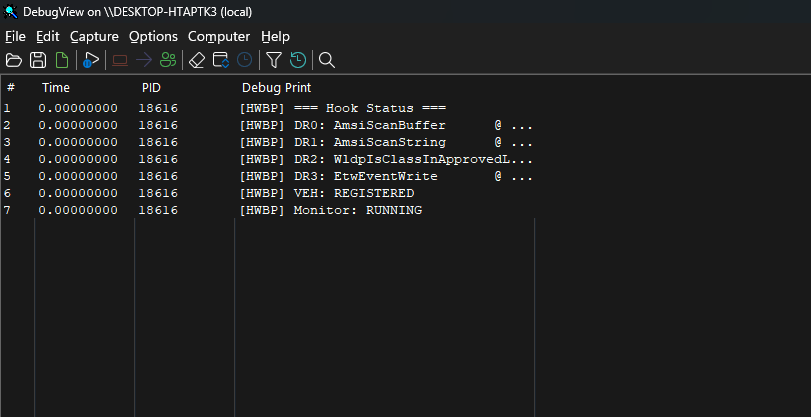 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
 phantomn/virtualbox_cve-2019-2525-cve-2019-2548
Proof-of-concept exploits for VirtualBox guest-to-host escape vulnerabilities CVE-2019-2525 and CVE-2019-2548, with a Python library for HGCM…
 tnot123/cve-2017-9822
In-depth technical analysis and proof-of-concept for CVE-2017-9822, an insecure deserialization vulnerability in DotNetNuke leading to remote code…