

dexcalibur
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
android-securitybinary-analysisdebuggers+5
1.2k
reversenseorg/dexcalibur[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 kevoreilly/capev2
Malware Configuration And Payload Extraction
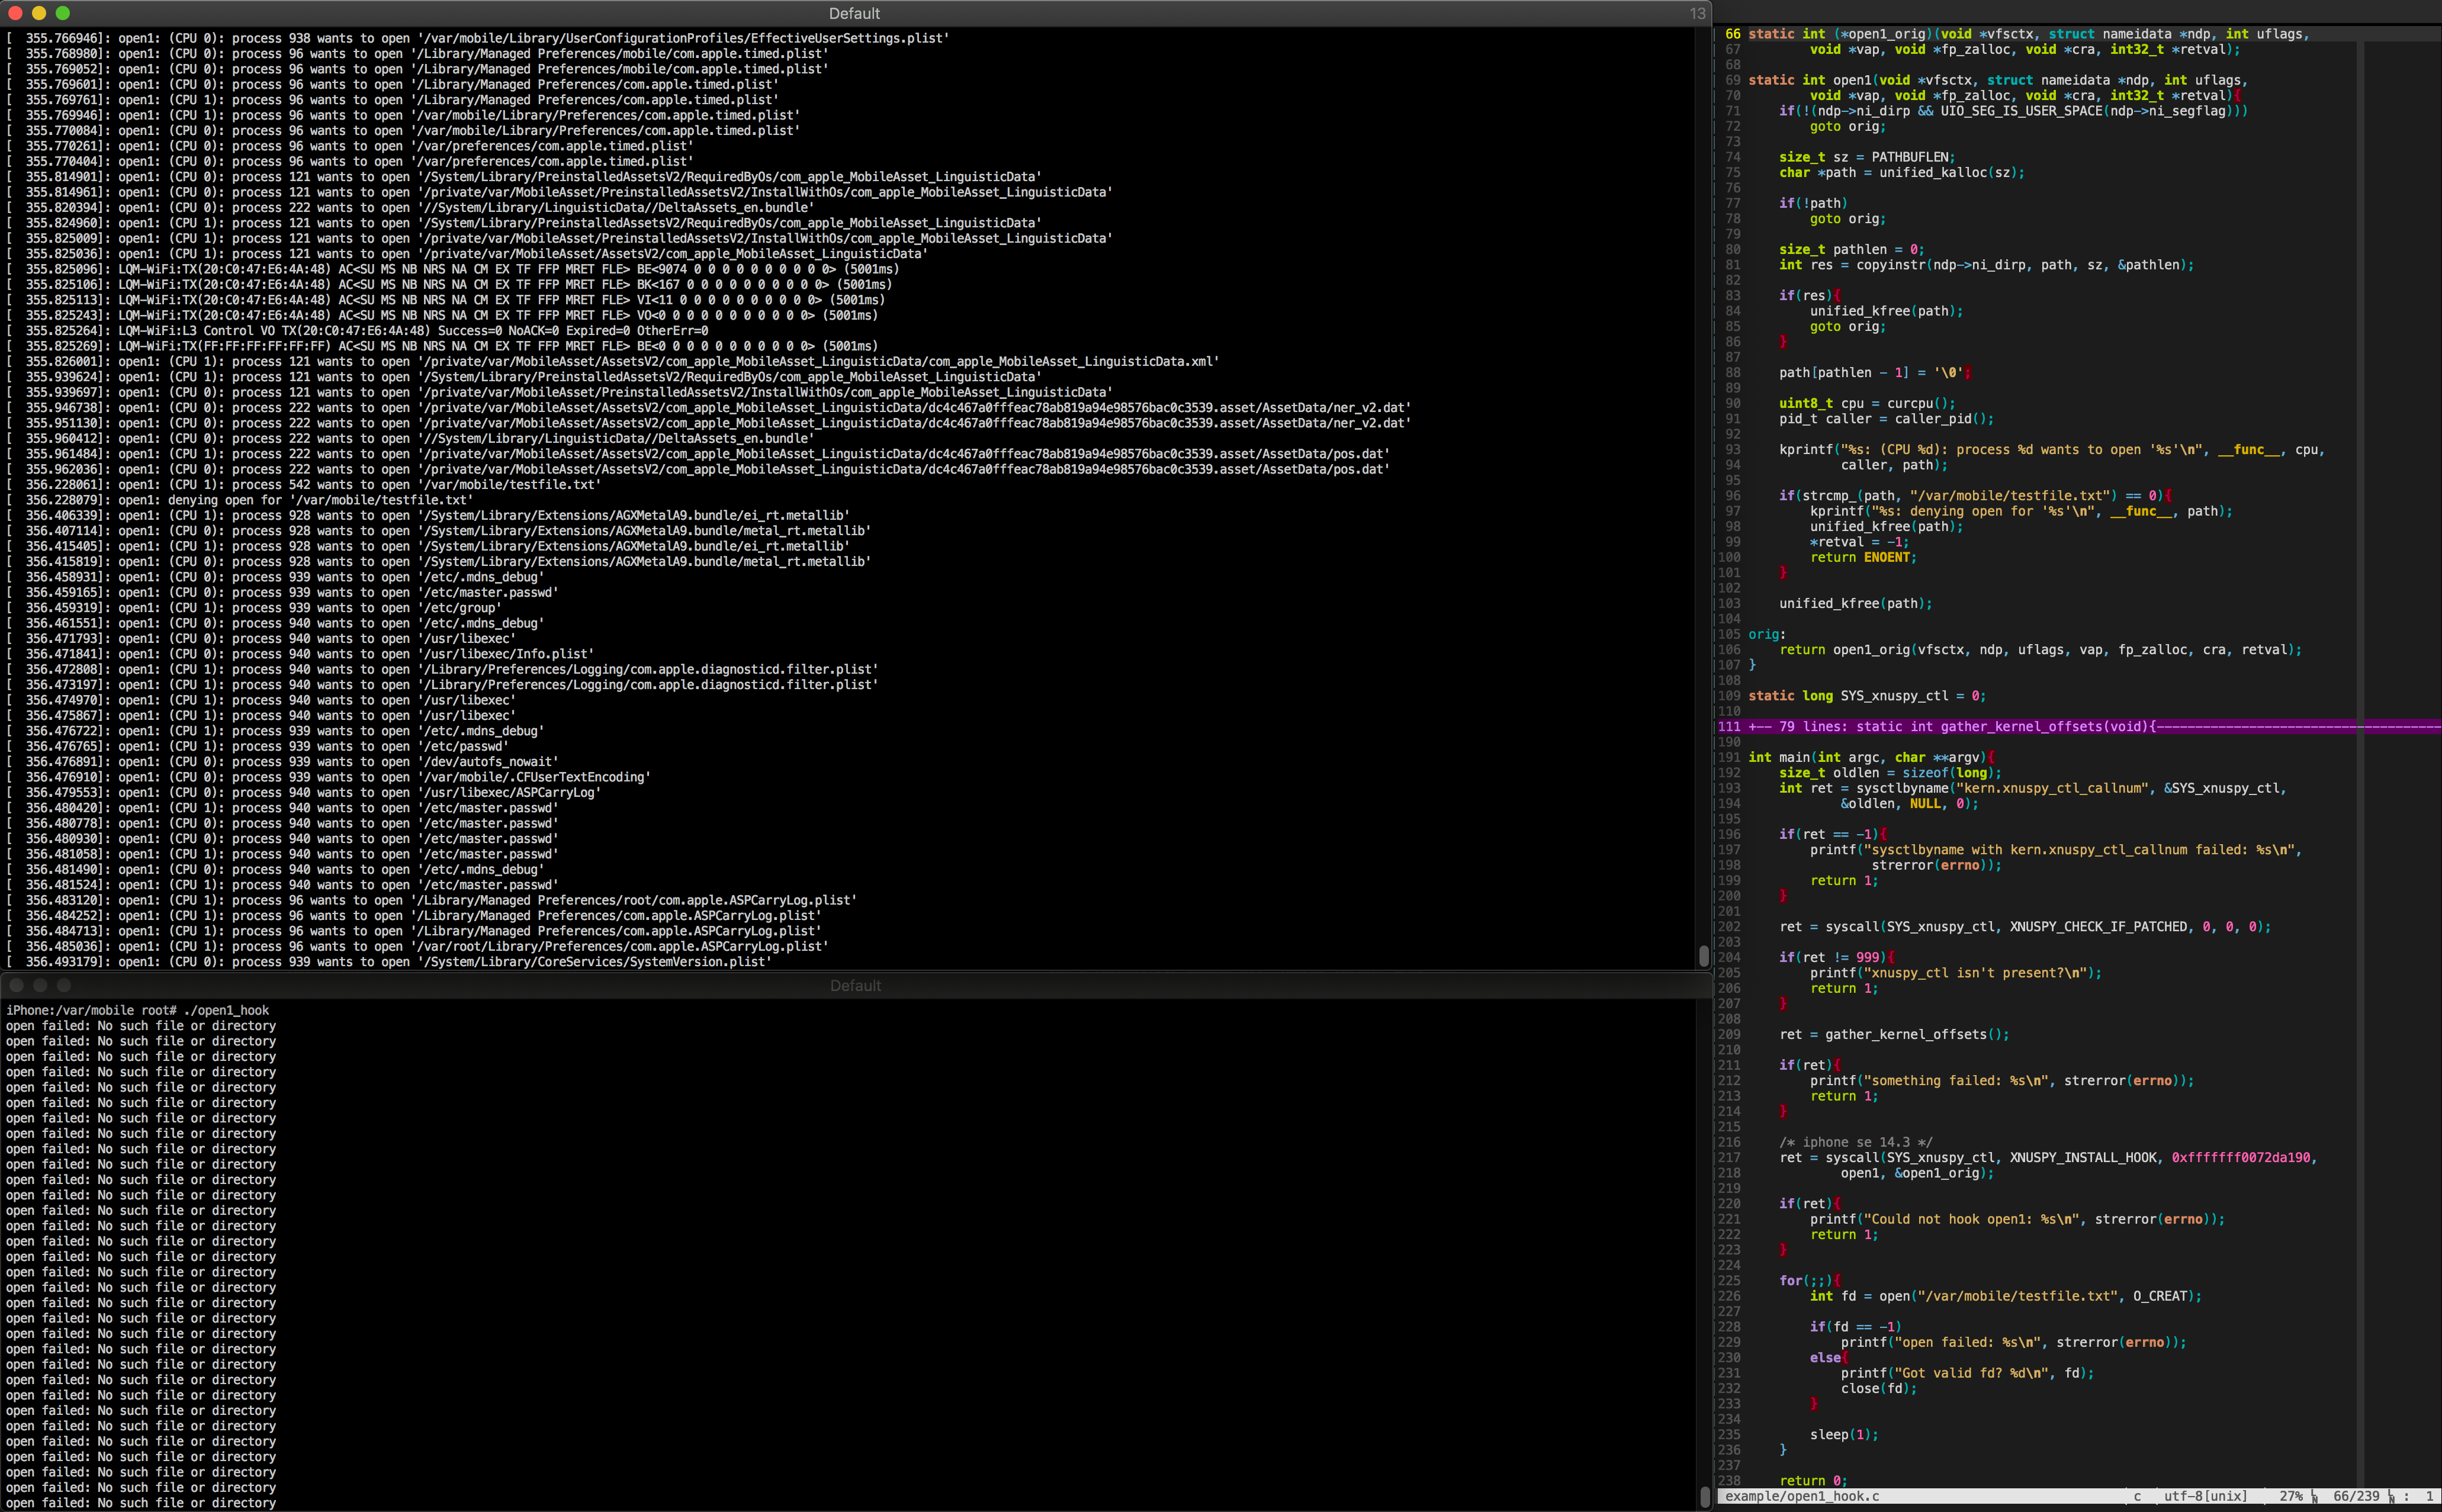 jsherman212/xnuspy
an iOS kernel function hooking framework for checkra1n'able devices
 swdunlop/andbug
Scriptable debugger for Android Dalvik VM using JDWP/DDM interfaces to hook methods, inspect process state, and modify runtime behavior without…
 vichhka-git/renef-skills
Agent Skill for operating renef.io — Android ARM64 dynamic instrumentation: hook native/Java, patch memory, trace syscalls, bypass SSL pinning/root…
 mandiant/strace
A DTrace on Windows Reimplementation
 humoud/hooketh
A set of scripts that ease working with frida
 rad9800/hwbp4mw
Hardware breakpoint hooking engine for Windows that uses debug registers to hook functions, bypass ETW/AMSI, and evade user-land EDR monitoring.