
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
162 results
c0ntextomy preview

c0ntextomy

GitHubc0ntextomy/c0ntextomy

CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…

data-exfiltrationdebuggersexploitation+9
73
6 years ago
systeminformer preview

systeminformer

GitHubwinsiderss/systeminformer

Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…

debuggersdigital-forensicsforensics+6
16.3k8h 33m ago
TangledWinExec preview

TangledWinExec

GitHubdaem0nc0re/tangledwinexec

PoCs and tools for investigation of Windows process execution techniques

adversarial-attackdebuggersids-ips-evasion+6
9608 months ago
radare2 preview

radare2

GitHubradareorg/radare2

UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
25.1k5h 41m ago
PowerShell-Suite preview

PowerShell-Suite

GitHubfuzzysecurity/powershell-suite

My musings with PowerShell

binary-analysisdebuggersforensics+5
2.7k4 years ago
x64dbg preview

x64dbg

GitHubx64dbg/x64dbg

An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.

ai-assisted-reversingbinary-analysisbinary-exploitation+7
50k5 days ago
pwndbg preview

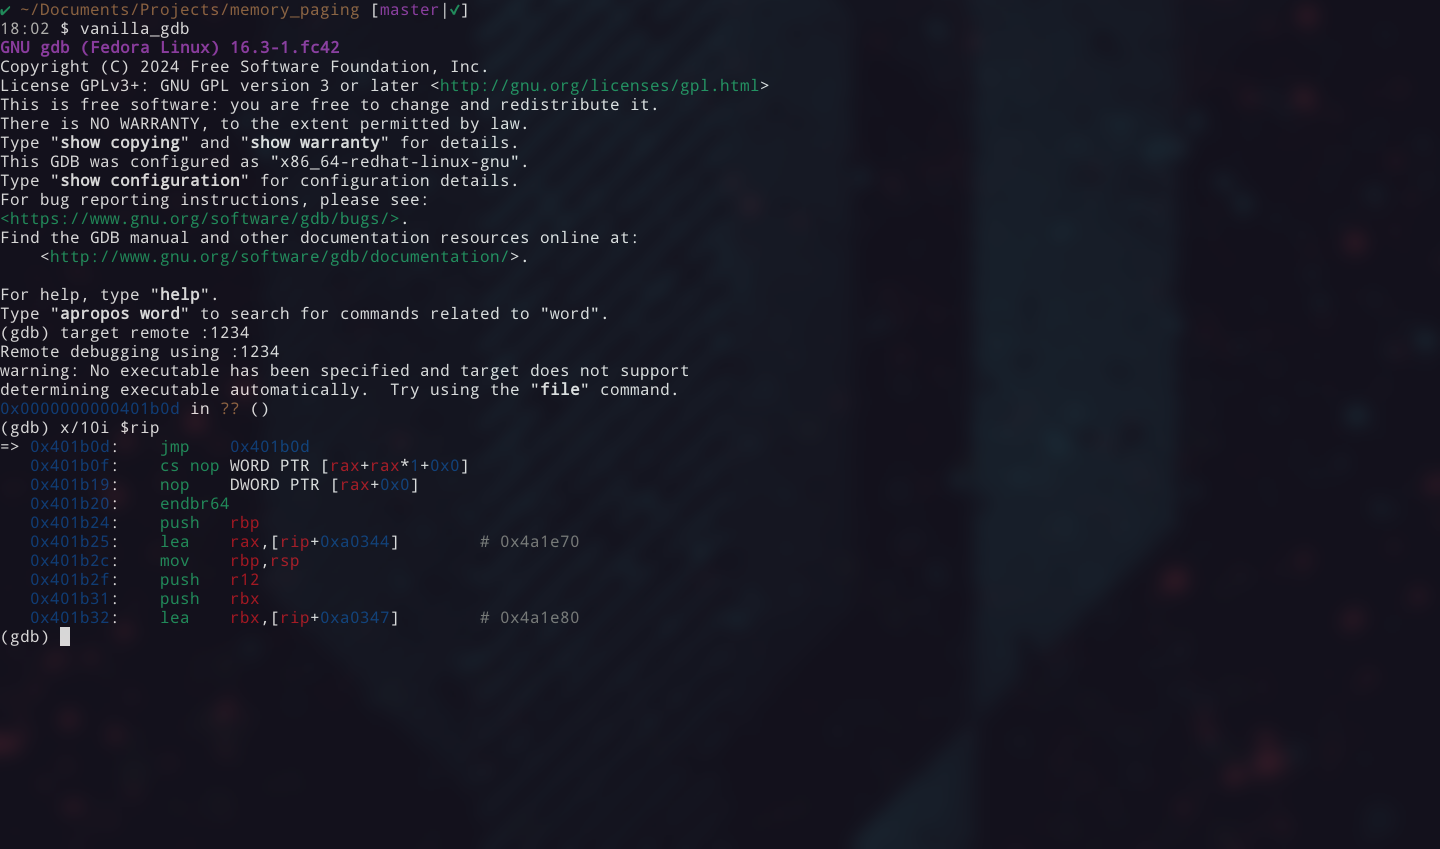
pwndbg

GitHubpwndbg/pwndbg

Exploit Development and Reverse Engineering with GDB & LLDB Made Easy

ai-assisted-reversingbinary-analysisbinary-exploitation+12
11.1k2 days ago
angr preview

angr

GitHubangr/angr

A powerful and user-friendly binary analysis platform!

ai-assisted-reversingbinary-analysisbinary-exploitation+12
9.2k1 day ago
Malware-analysis-and-Reverse-engineering preview

Malware-analysis-and-Reverse-engineering

GitHubdump-guy/malware-analysis-and-reverse-engineering

Some of my publicly available Malware analysis and Reverse engineering.
binary-analysisctfcurated-resources+8
9682 years ago
heaptrace preview

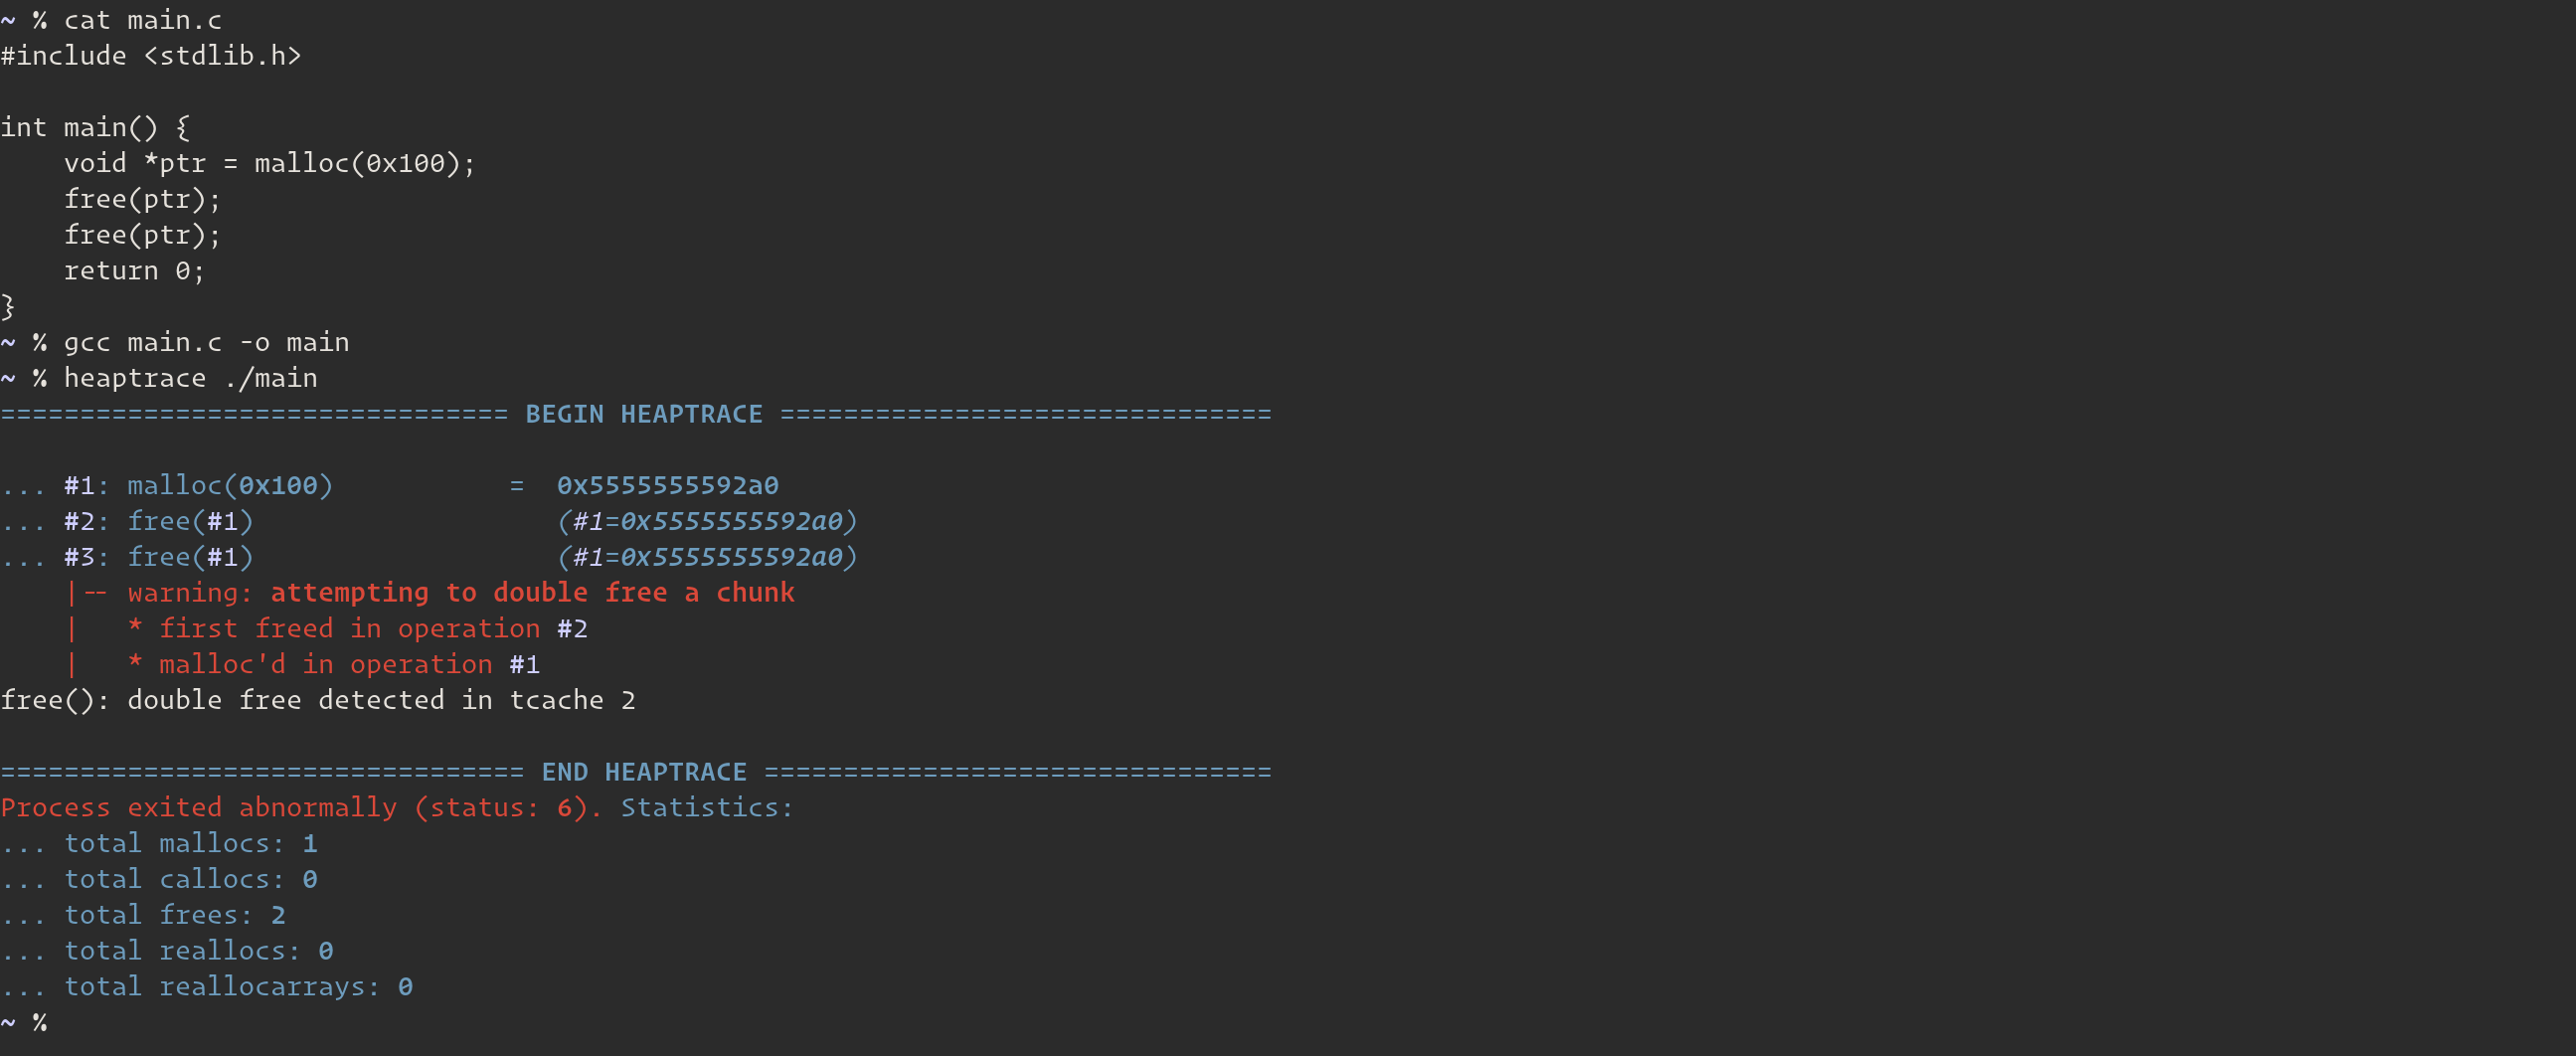
heaptrace

GitHubarinerron/heaptrace

helps visualize heap operations for pwn and debugging
binary-analysisctfdebuggers+1
3303 years ago
page_table_walk preview

page_table_walk

GitHubjazho76/page_table_walk

Walk x86-64 page tables by hand in qemu and gdb. Decompose a virtual address, follow cr3 through all levels of physical memory, and extract a flag…
binary-analysisctfdebuggers+4
287 months ago
CheatSheetHost preview

CheatSheetHost

GitHubjimmyader/cheatsheethost

A locally hosted page for cheat sheets. Currently being used for reverse engineering and hosted in labs so I can limit or forgo (lock down firewall)…

ctfcurated-resourcesdebuggers+3
147 months ago
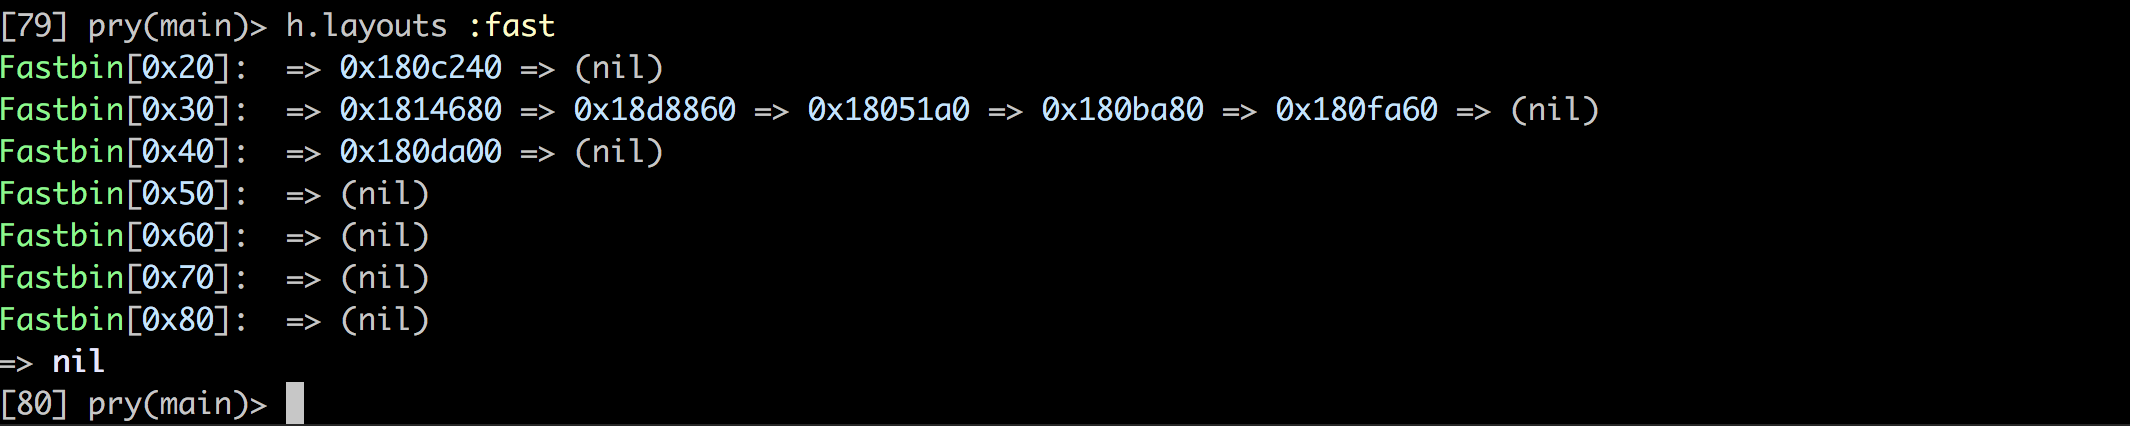
gef preview

gef

GitHubhugsy/gef

GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
ai-assisted-reversingbinary-analysisbinary-exploitation+10
8.4k2 months ago
heapinfo preview

heapinfo

GitHubdavid942j/heapinfo

An interactive memory info for pwning / exploiting
binary-analysisbinary-exploitationctf+3
983 years ago
fatal_core_dump preview

fatal_core_dump

GitHubaxlan/fatal_core_dump

A core dump debugging murder mystery.

binary-exploitationctfdebuggers+5
137 months ago
secbox preview

secbox

GitHubyv1ing/secbox

Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.
binary-exploitationctfdebuggers+9
4 days ago
Rainfall preview

Rainfall

GitLabqduarte-42/rainfall

Introduction to the exploitation of ELF binaries.

binary-exploitationctfdebuggers+5
1 year ago
Brovan preview

Brovan

GitHubadvdebug/brovan

User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…

binary-analysisdebuggersdynamic-analysis-sandboxing+3
1678h 22m ago
Previous12…9Next
